NIST IR 5495 日本語訳
英語タイトル : Computer Security Training & Awareness Course Compendium日本語タイトル : コンピュータセキュリティトレーニング・意識向上コース集
公開日 : 1994-09-01
原文URL : https://csrc.nist.gov/pubs/ir/5495/final
翻訳編集 : 自動生成(有志による非公式の日本語訳), 原文取得日 : 2026-10-31, 訳文 : 27 / 30 ブロック
[要約] NIST IR 5495 は、NISTIR 4846 を置き換える、コンピュータセキュリティのトレーニングおよび意識向上のコースを集めた報告書です。本書の目的は、連邦機関がコンピュータセキュリティのトレーニング資源を探す手助けをすることで、1987 年コンピュータセキュリティ法に基づく NIST の権限に沿って連邦機関を支援する継続的な取り組みの一環とされています。掲載したコースは、1993 暦年中に実施した公開データ募集によって得られたもので、NIST Special Publication 500-172 のトレーニングマトリクスに対応付けられています。コースの一覧に加え、主要な区分、ベンダー、製品、製品固有のコース、トレーニングマトリクスを示す付録があります。
NISTIR 5495
(Supersedes NISTIR 4846)
NISTIR 5495
(NISTIR 4846 を置き換え)
Computer Security Training & Awareness Course Compendium
コンピュータセキュリティトレーニング・意識向上コース集
Kathie Everhart
Editor
Kathie Everhart
編集者
U.S. DEPARTMENT OF COMMERCE
Technology Administration
National Institute of Standards and Technology
Gaithersburg, MD 20899
米国商務省
技術管理局(Technology Administration)
米国国立標準技術研究所(NIST)
Gaithersburg, MD 20899
NISTIR 5495
NISTIR 5495
(Supersedes NISTIR 4846)
(NISTIR 4846 を置き換え)
Computer Security Training & Awareness Course Compendium
コンピュータセキュリティトレーニング・意識向上コース集
Kathie Everhart
Editor
Kathie Everhart
編集者
U.S. DEPARTMENT OF COMMERCE
Technology Administration
National Institute of Standards and Technology
Gaithersburg, MD 20899
米国商務省
技術管理局(Technology Administration)
米国国立標準技術研究所(NIST)
Gaithersburg, MD 20899
September 1994
1994 年 9 月
U.S. DEPARTMENT OF COMMERCE
Ronald H. Brown, Secretary
TECHNOLOGY ADMINISTRATION
Mary L. Good, Under Secretary for Technology
米国商務省
Ronald H. Brown, 長官
技術管理局(TECHNOLOGY ADMINISTRATION)
Mary L. Good, 技術担当次官
NATIONAL INSTITUTE OF STANDARDS AND TECHNOLOGY
Arati Prabhakar, Director
米国国立標準技術研究所
Arati Prabhakar, 長官
Preface
序文
This National Institute of Standards and Technology (NIST) Interagency Report (NISTIR) is a compendium of computer security training and awareness courses. The purpose of this publication is to assist federal agencies locate computer security training resources. This publication is part of a continuing NIST effort to support federal agencies in accordance with NIST’s mandate under the Computer Security Act of 1987. In addition to the table of contents, which lists the courses, there are four appendices: A) lists the courses by training areas within audience categories as defined in NIST Special Publication 500-172, Computer Security Training Guidelines; B) lists the vendors that participated in this effort; C) lists the specific products for which training is available; and D) lists the product specific courses.
この米国国立標準技術研究所(NIST)省庁間報告書(NISTIR)は、コンピュータセキュリティのトレーニングおよび意識向上のコースを集めたものです。本書の目的は、連邦機関がコンピュータセキュリティのトレーニング資源を見つけるのを支援することです。本書は、1987 年コンピュータセキュリティ法(Computer Security Act of 1987)に基づく NIST の権限に沿って連邦機関を支援する、NIST の継続的な取り組みの一環です。コースを一覧にした目次に加えて、4 つの付録があります。A) NIST Special Publication 500-172, Computer Security Training Guidelines で定義された対象者区分ごとに、トレーニング分野別にコースを一覧にしたもの、B) この取り組みに参加したベンダーを一覧にしたもの、C) トレーニングが提供されている個々の製品を一覧にしたもの、D) 製品固有のコースを一覧にしたものです。
NIST Special Publication 500-172 was developed to provide a framework for identifying computer security training requirements for diverse audiences. It focuses on learning objectives based upon the extent to which computer security knowledge is required by individuals as it applies to their job function.
NIST Special Publication 500-172 は、多様な対象者のコンピュータセキュリティトレーニング要件を特定するための枠組みを提供するために策定されました。同書は、個人の職務に適用されるコンピュータセキュリティ知識の必要度に基づく学習目標に焦点を当てています。
A training matrix was introduced in Special Publication 500-172 to assist agencies in designing training that meets the learning objectives for a particular group. The training and awareness courses in this compendium have been mapped to the matrix (see appendix E) by the training organization/vendor.
Special Publication 500-172 では、特定のグループの学習目標を満たすトレーニングを機関が設計する手助けとして、トレーニングマトリクスが導入されました。本コース集のトレーニングおよび意識向上コースは、トレーニング組織/ベンダーによって、そのマトリクスに対応付けられています(付録 E を参照)。
NIST makes no claim or endorsement of the computer security courses or their currency in this compendium. Courses listed in this compendium were obtained from a public data call during the 1993 calendar year. The data call consisted of a letter of invitation to known sources of trainers as provided by the Federal Computer Security Program Managers’ Forum; and the Federal Information Systems Security Educators’ Association (FISSEA). In addition, a NIST CSL Newsletter was disseminated nationwide inviting vendors to participate in this effort. Therefore, this listing is not a complete source of all available security related courses.
NIST は、本コース集に掲載したコンピュータセキュリティコースやその最新性について、いかなる主張も推奨も行いません。本コース集に掲載したコースは、1993 暦年中に実施した公開データ募集によって得られたものです。データ募集では、Federal Computer Security Program Managers’ Forum および Federal Information Systems Security Educators’ Association(FISSEA)が提供した既知のトレーナー情報に基づき、トレーナーに招待状を送りました。加えて、ベンダーに参加を呼びかける NIST の CSL Newsletter を全国に配布しました。したがって、この一覧は、入手可能なセキュリティ関連コースをすべて網羅した情報源ではありません。
Vendors already listed are encouraged to continue to send in changes/updates and new vendors are invited to send in their computer security courses (See address below.) NIST expresses its appreciation to the many federal, academic, and vendor organizations that participated in this effort for their time and interest in mapping their courses to the matrix in NIST Special Publication 500-172. A special thanks to those members of FISSEA who participated in the organization of this compendium.
すでに掲載されているベンダーには、変更や更新を引き続き送っていただくよう推奨します。また、新規ベンダーには、コンピュータセキュリティコースを送っていただくようお願いします(下記の住所を参照)。NIST は、時間と関心を割いて、自らのコースを NIST Special Publication 500-172 のマトリクスに対応付けてくださった、多くの連邦機関、学術機関およびベンダー組織の参加に感謝します。本コース集の編成に参加した FISSEA の会員の皆さまには、特に感謝します。
Questions or comments regarding this publication should be addressed to Kathie Everhart, Office of the Associate Director for Computer Security, Computer Systems Laboratory, Building 225, Room B154, National Institute of Standards and Technology, Gaithersburg, MD, 20899.
本書に関する質問やコメントは、Kathie Everhart, Office of the Associate Director for Computer Security, Computer Systems Laboratory, Building 225, Room B154, National Institute of Standards and Technology, Gaithersburg, MD, 20899 宛にお寄せください。
Additional copies of this NISTIR may be purchased through the National Technical Information Service, Springfield, VA. 22161, telephone: (703) 487-3238.
この NISTIR の追加部数は、National Technical Information Service, Springfield, VA. 22161(電話: (703) 487-3238)から購入できます。
TABLE OF CONTENTS
目次
[Excerpt from 各提供者のコース一覧(目次), © 各コースの提供者 — not reproduced on this unofficial site]
[各提供者のコース一覧(目次) からの引用。第三者(各コースの提供者)の著作物のため、この非公式サイトには掲載していません。原本 PDF を参照してください。]
LIST OF APPENDICES
付録一覧
A - Major Categories
B - Vendor List
C - Product List
D - Product Specific Courses
E - Training Matrix
A - 主要な区分
B - ベンダー一覧
C - 製品一覧
D - 製品固有のコース
E - トレーニングマトリクス
[Excerpt from Courses listed in this compendium were obtained from a public data call, © 外部の著者(原本の記載による) — not reproduced on this unofficial site]
[Courses listed in this compendium were obtained from a public data call からの引用。第三者(外部の著者(原本の記載による))の著作物のため、この非公式サイトには掲載していません。原本 PDF を参照してください。]
It is our intention to update this document as the need arises and we welcome any comments and corrections that will yield a better product. Please contact Kathie Everhart (301) 975-3868.
本書は、必要に応じて更新する予定です。より良い成果物につながるコメントや訂正を歓迎します。Kathie Everhart (301) 975-3868 までご連絡ください。
APPENDIX A
付録 A
[Excerpt from コースの索引(付録 A〜D), © 各コースの提供者 — not reproduced on this unofficial site]
[コースの索引(付録 A〜D) からの引用。第三者(各コースの提供者)の著作物のため、この非公式サイトには掲載していません。原本 PDF を参照してください。]
APPENDIX E
付録 E
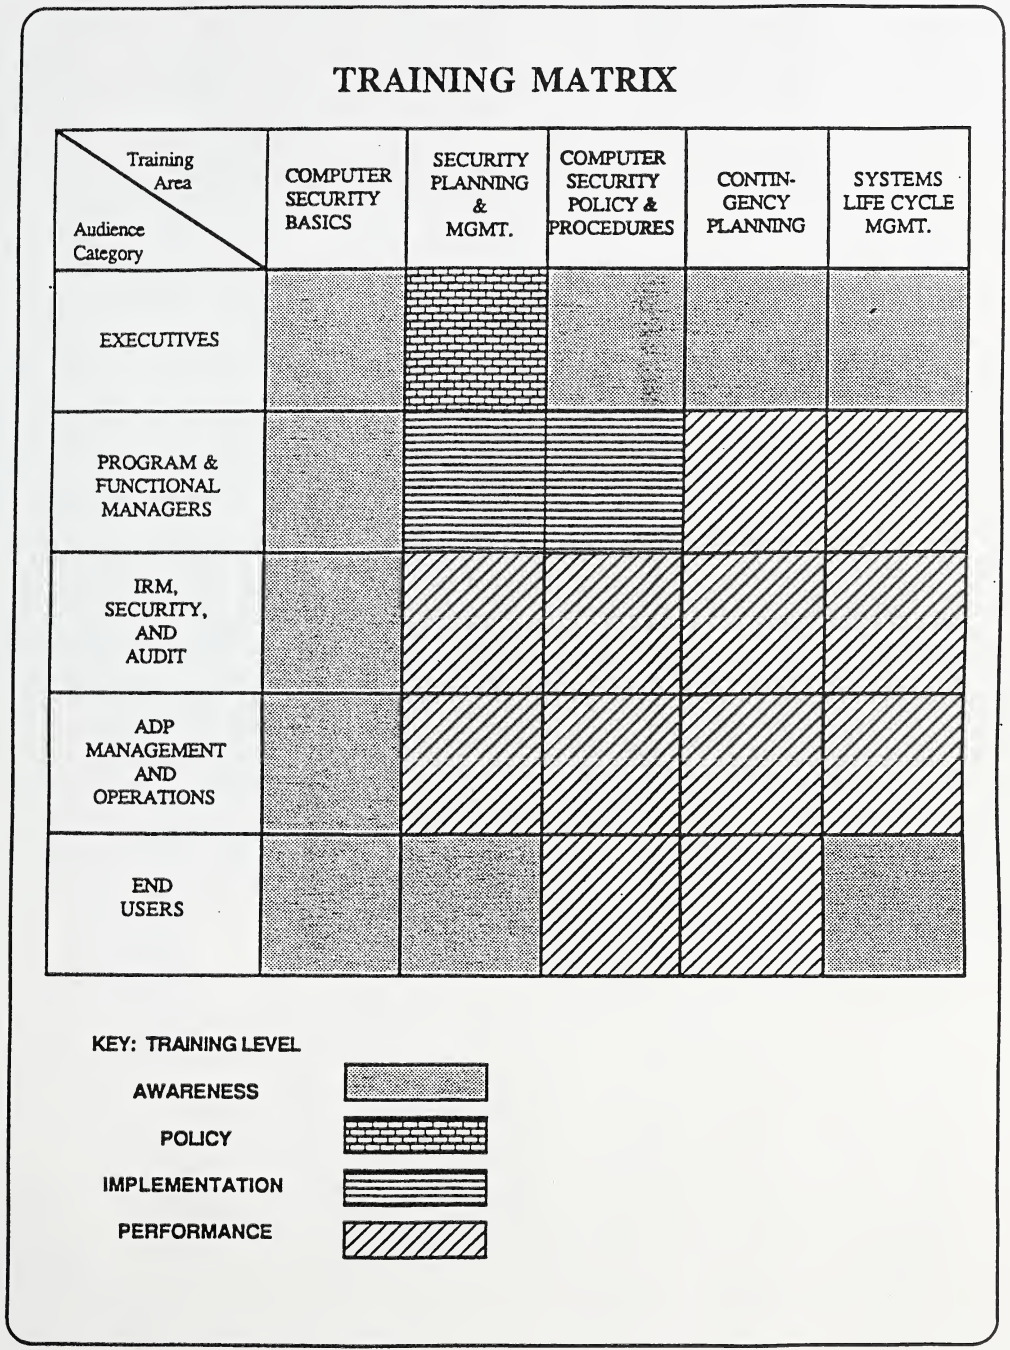
「TRAINING MATRIX」(訓練マトリクス)と題した表です。左上の欄は列が「Training Area」(訓練分野)、行が「Audience Category」(対象者区分)であることを示します。列は「COMPUTER SECURITY BASICS」(コンピュータセキュリティの基礎)、「SECURITY PLANNING & MGMT.」(セキュリティ計画・管理)、「COMPUTER SECURITY POLICY & PROCEDURES」(コンピュータセキュリティのポリシー・手順)、「CONTINGENCY PLANNING」(コンティンジェンシー計画)、「SYSTEMS LIFE CYCLE MGMT.」(システムライフサイクル管理)です。行は「EXECUTIVES」(幹部)、「PROGRAM & FUNCTIONAL MANAGERS」(プログラム・機能管理者)、「IRM, SECURITY, AND AUDIT」(IRM・セキュリティ・監査)、「ADP MANAGEMENT AND OPERATIONS」(ADP 管理・運用)、「END USERS」(エンドユーザー)です。各セルの模様が訓練レベルを表し、凡例「KEY: TRAINING LEVEL」は「AWARENESS」(意識向上、点描)、「POLICY」(ポリシー、れんが模様)、「IMPLEMENTATION」(実施、横線)、「PERFORMANCE」(実行、斜線)です。幹部は、意識向上、ポリシー、意識向上、意識向上、意識向上です。プログラム・機能管理者は、意識向上、実施、実施、実行、実行です。IRM・セキュリティ・監査は、基礎が意識向上で、残りの 4 列が実行です。ADP 管理・運用は、基礎が意識向上で、残りの 4 列が実行です。エンドユーザーは、意識向上、意識向上、実行、実行、意識向上です。