NIST IR 7870 日本語訳
英語タイトル : NIST Test Personal Identity Verification (PIV) Cards日本語タイトル : NIST テスト用個人識別検証(PIV)カード
公開日 : 2012-07-12
原文URL : https://csrc.nist.gov/pubs/ir/7870/final
翻訳編集 : 自動生成(有志による非公式の日本語訳), 原文取得日 : 2026-10-31, 訳文 : 77 / 79 ブロック
[要約] NIST IR 7870 は、NIST が開発したテスト用の個人識別検証(PIV)カード群と、それを支える公開鍵基盤の概要を示す報告書です。このテスト用カード群は、PIV カードに対応するアプリケーションおよびミドルウェアの開発を促進するために作られました。現在発行されているカードに似た例だけでなく、将来発行されるカードに現れると見込まれる機能を備えたカードの例も含まれています。本書は、テスト用の公開鍵基盤とテスト用 PIV カードの概要を説明し、付録で頭字語と参考文献を示します。
NISTIR 7870
NISTIR 7870
NIST Test Personal Identity Verification (PIV) Cards
NIST テスト用個人識別検証(PIV)カード
David A. Cooper
David A. Cooper
http://dx.doi.org/10.6028/NIST.IR.7870
http://dx.doi.org/10.6028/NIST.IR.7870
[NIST のロゴ。公的な標章のため、この非公式サイトには掲載していません。原本 PDF を参照してください。]
NISTIR 7870
NISTIR 7870
NIST Text Personal Identity Verification (PIV) Cards
NIST テスト用個人識別検証(PIV)カード
David A. Cooper
Computer Security Division
Information Technology Laboratory
David A. Cooper
コンピュータセキュリティ部門
情報技術研究所
http://dx.doi.org/10.6028/NIST.IR.7870
http://dx.doi.org/10.6028/NIST.IR.7870
July 2012
2012 年 7 月
U.S. Department of Commerce
Rebecca M. Blank, Acting Secretary
米国商務省
Rebecca M. Blank 長官代行
National Institute of Standards and Technology
Patrick D. Gallagher, Under Secretary of Commerce for Standards and Technology and Director
米国標準技術研究所
Patrick D. Gallagher、NIST 所長兼商務次官(標準・技術担当)
Reports on Computer Systems Technology
コンピュータシステム技術に関する報告書
The Information Technology Laboratory (ITL) at the National Institute of Standards and Technology (NIST) promotes the U.S. economy and public welfare by providing technical leadership for the Nation’s measurement and standards infrastructure. ITL develops tests, test methods, reference data, proof of concept implementations, and technical analysis to advance the development and productive use of information technology. ITL’s responsibilities include the development of technical, physical, administrative, and management standards and guidelines for the cost-effective security and privacy of sensitive unclassified information in Federal computer systems. This Interagency Report discusses ITL’s research, guidance, and outreach efforts in computer security, and its collaborative activities with industry, government, and academic organizations.
米国標準技術研究所(NIST)の情報技術研究所(ITL)は、国の計測・標準基盤に対する技術的なリーダーシップを提供することで、米国の経済と公共の福祉を促進しています。ITL は、情報技術の開発と生産的な利用を進めるために、試験、試験方法、参照データ、概念実証の実装、技術分析を開発しています。ITL の責務には、連邦コンピュータシステムにおける機微な非機密情報のセキュリティとプライバシーを費用対効果よく確保するための、技術的、物理的、管理的、運用管理上の標準およびガイドラインの策定が含まれます。この省庁間報告書では、コンピュータセキュリティに関する ITL の研究、ガイダンス、アウトリーチの取り組みと、産業界、政府、学術機関との共同活動を論じています。
National Institute of Standards and Technology Interagency Report
12 pages (2012)
米国標準技術研究所 省庁間報告書
12 ページ(2012 年)
Certain commercial entities, equipment, or materials may be identified in this document in order to describe an experimental procedure or concept adequately. Such identification is not intended to imply recommendation or endorsement by the National Institute of Standards and Technology, nor is it intended to imply that the entities, materials, or equipment are necessarily the best available for the purpose.
本書では、実験の手順や概念を適切に説明するために、特定の商業事業者、装置、または資材を挙げている場合があります。こうした記載は、米国標準技術研究所による推奨や支持を意味するものではなく、挙げられた事業者、資材、または装置がその目的に必ずしも最適であることを意味するものでもありません。
Abstract
概要
In order to facilitate the development of applications and middleware that support the Personal Identity Verification (PIV) Card, NIST has developed a set of test PIV Cards and a supporting public key infrastructure. This set of test cards includes not only examples that are similar to cards issued today, but also examples of cards with features that are expected to appear in cards that will be issued in the future. This document provides an overview of the test cards and the infrastructure that has been developed to support their use.
個人識別検証(PIV)カードに対応するアプリケーションおよびミドルウェアの開発を促進するため、NIST は、一組のテスト用 PIV カードと、それを支える公開鍵基盤を開発しました。このテスト用カード群には、現在発行されているカードに似た例だけでなく、将来発行されるカードに現れると見込まれる機能を備えたカードの例も含まれています。本書は、テスト用カードと、その利用を支えるために開発された基盤の概要を示します。
Disclaimer
免責事項
Statements made in this paper are the opinions of the author and should not be interpreted as standards, guidelines, best practices, or recommendations for specific changes to any other NIST publications.
本稿の記述は著者の見解であり、標準、ガイドライン、ベストプラクティス、または NIST のほかの刊行物に対する特定の変更の推奨として解釈すべきではありません。
Table of Contents
目次
1. Introduction
1. はじめに
In order to facilitate the development of applications and middleware that support the Personal Identity Verification (PIV) Card, NIST has developed a set of test PIV Cards and a supporting public key infrastructure. This set of test cards includes not only examples that are similar to cards issued today, but also examples of cards with features that are expected to appear in cards that will be issued in the future. For example, while the certificates and data objects on most, if not all, cards issued today are signed using RSA PKCS #1 v1.5, the set of test cards include examples of certificates and data objects that are signed using each of the algorithms and key sizes listed in Table 3-3 of SP 800-78-3, including RSASSA-PSS and ECDSA. Similarly, the infrastructure supporting the test cards provides examples of certificate revocation lists (CRLs) and Online Certificate Status Protocol (OCSP) responses that are signed using each of these signature algorithms. The set of test cards also includes certificates with ECC subject public keys in addition to RSA subject public keys, as is permitted by Table 3-1 of SP 800-78-3. The set of test cards, collectively, also include all of the mandatory and optional data objects listed in Section 3 of SP 800-73-3 Part 1, except for Cardholder Iris Images. Several of the cards include a Key History object along with retired key management keys.
個人識別検証(PIV)カードに対応するアプリケーションおよびミドルウェアの開発を促進するため、NIST は、一組のテスト用 PIV カードと、それを支える公開鍵基盤を開発しました。このテスト用カード群には、現在発行されているカードに似た例だけでなく、将来発行されるカードに現れると見込まれる機能を備えたカードの例も含まれています。たとえば、現在発行されているほとんどのカード(すべてではないにしても)の証明書とデータオブジェクトは RSA PKCS #1 v1.5 で署名されていますが、テスト用カード群には、SP 800-78-3 の表 3-3 に挙げられた各アルゴリズムと鍵長(RSASSA-PSS および ECDSA を含む)で署名された証明書とデータオブジェクトの例が含まれています。同様に、テスト用カードを支える基盤は、これらの署名アルゴリズムのそれぞれで署名された証明書失効リスト(CRL)とオンライン証明書状態プロトコル(OCSP)応答の例を提供します。また、SP 800-78-3 の表 3-1 で認められているとおり、テスト用カード群には、RSA のサブジェクト公開鍵に加えて ECC のサブジェクト公開鍵を持つ証明書も含まれています。テスト用カード群は全体として、SP 800-73-3 Part 1 の第 3 節に挙げられた必須およびオプションのデータオブジェクトのすべてを含んでいます(Cardholder Iris Images を除きます)。いくつかのカードには、失効した鍵管理用の鍵とともに Key History オブジェクトが含まれています。
2. Test Public Key Infrastructure
2. テスト用公開鍵基盤
The cardholders' certificates and the content signers' certificates of the test PIV Cards are issued from a simple two-level hierarchical public key infrastructure (PKI), as depicted in Figure 1. The root certification authority (CA) has issued certificates to several intermediate CAs, which in turn have issued the end-entity certificates. In order to be able to validate the certificates of the test cards, it will be necessary to install the root CA from the PKI as a trust anchor in the software that will be validating the certificates. A self-signed CA certificate for the root CA, which may be used to establish the root CA as a trust anchor, is available at http://csrc.nist.gov/groups/SNS/piv/testcards.html.
テスト用 PIV カードの所持者の証明書とコンテンツ署名者の証明書は、図 1 に示す単純な 2 階層の公開鍵基盤(PKI)から発行されます。ルート認証局(CA)が複数の中間 CA に証明書を発行し、それらの中間 CA がエンドエンティティ証明書を発行しています。テスト用カードの証明書を検証できるようにするには、証明書を検証するソフトウェアに、この PKI のルート CA をトラストアンカーとしてインストールする必要があります。ルート CA をトラストアンカーとして確立するために使える、ルート CA の自己署名 CA 証明書は、http://csrc.nist.gov/groups/SNS/piv/testcards.html で入手できます。
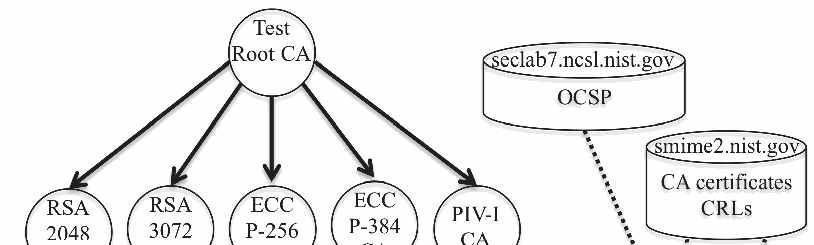
試験用 PKI の図の上半分です。「Test Root CA」の円から、「RSA 2048 CA」「RSA 3072 CA」「ECC P-256 CA」「ECC P-384 CA」「PIV-I CA」の 5 つの中間 CA の円へ矢印が出ています。右側には「OCSP」と書かれた円筒「seclab7.ncsl.nist.gov」と、「CA certificates CRLs」と書かれた円筒「smime2.nist.gov」があり、点線が下へ延びています(図の下半分に続きます)。
[米国の国章が写っている図。公的な標章のため、この非公式サイトには掲載していません。原本 PDF を参照してください。]
Figure 1 – PKI for Test PIV Cards
図 1 – テスト用 PIV カードの PKI
The test PKI includes a server that provides access to CA certificates and CRLs via both Lightweight Directory Access Protocol (LDAP) and Hypertext Transfer Protocol (HTTP). Each certificate issued by the PKI, except for the self-signed certificate issued by the root CA, includes a cRLDistributionPoints extension with both HTTP and LDAP URIs that point to the relevant CRL for that certificate. Each of these certificates also includes an authorityInfoAccess extension with both HTTP and LDAP URIs that point to the location where the CA certificates issued to the issuer of the certificate may be found. Each CA certificate issued by the PKI, including the self-signed certificate issued by the root CA, includes a subjectInfoAccess extension with both HTTP and LDAP URIs that point to the location where the CA certificates issued by the subject of the certificate may be found. While some certificate validation software will be able to use the URIs in the certificates to automatically retrieve the intermediate CA certificates needed to validate the end-entity certificates in the test PKI, some certificate validation software will only be able to validate the end-entity certificates if the intermediate CA certificates are installed manually. In order to support such software, the intermediate CA certificates have been made available at http://csrc.nist.gov/groups/SNS/piv/testcards.html.
テスト用 PKI には、Lightweight Directory Access Protocol(LDAP)と Hypertext Transfer Protocol(HTTP)の両方で CA 証明書と CRL へのアクセスを提供するサーバーが含まれています。ルート CA が発行した自己署名証明書を除き、PKI が発行する各証明書には、その証明書に対応する CRL を指す HTTP と LDAP の両方の URI を持つ cRLDistributionPoints 拡張が含まれています。これらの証明書にはそれぞれ、その証明書の発行者に対して発行された CA 証明書の所在を指す HTTP と LDAP の両方の URI を持つ authorityInfoAccess 拡張も含まれています。ルート CA が発行した自己署名証明書を含め、PKI が発行する各 CA 証明書には、その証明書のサブジェクトが発行した CA 証明書の所在を指す HTTP と LDAP の両方の URI を持つ subjectInfoAccess 拡張が含まれています。証明書検証ソフトウェアの中には、証明書内の URI を使って、テスト用 PKI のエンドエンティティ証明書の検証に必要な中間 CA 証明書を自動的に取得できるものもありますが、中間 CA 証明書を手動でインストールしなければエンドエンティティ証明書を検証できないものもあります。そのようなソフトウェアを支援するために、中間 CA 証明書は http://csrc.nist.gov/groups/SNS/piv/testcards.html で公開されています。
The test PKI also includes an OCSP responder that provides revocation status information for each of the unexpired end-entity certificates in the PKI. Each of the end-entity certificates includes an HTTP URI in its authorityInfoAccess extension that points to the OCSP responder. Each of the CAs issues CRLs once an hour, with the CRLs specifying a nextUpdate time that is 24 hours after the CRL was issued. The OCSP responder only provides pre-signed responses, which are also produced once an hour. The nextUpdate time indicated for each certificate in the OCSP responses is 2 hours after the OCSP response was produced.
テスト用 PKI には、PKI 内の有効期限が切れていない各エンドエンティティ証明書の失効状態情報を提供する OCSP レスポンダーも含まれています。各エンドエンティティ証明書には、その OCSP レスポンダーを指す HTTP URI が authorityInfoAccess 拡張に含まれています。各 CA は CRL を 1 時間に 1 回発行し、CRL の nextUpdate 時刻は CRL の発行から 24 時間後に設定されます。OCSP レスポンダーは事前に署名された応答のみを提供し、その応答も 1 時間に 1 回作成されます。OCSP 応答に示される各証明書の nextUpdate 時刻は、OCSP 応答の作成から 2 時間後です。
The server that provides access to the CA certificates and CRLs also provides access to the retired key management certificates for test cards that include a Key History object with an offCardCertURL. These certificates are available via HTTP, as specified in the offCardCertURL.
CA 証明書と CRL へのアクセスを提供するサーバーは、offCardCertURL を持つ Key History オブジェクトを含むテスト用カードについて、失効した鍵管理用証明書へのアクセスも提供します。これらの証明書は、offCardCertURL に指定されたとおり、HTTP で入手できます。
The URIs in many of the expired certificates refer to locations that do not exist. This was done to emphasize that there is no need to validate retired certificates for key management, and that repositories supporting CAs that are no longer operational may not be available.
有効期限が切れた証明書の多くに含まれる URI は、存在しない場所を指しています。これは、退役した証明書を鍵管理のために検証する必要はないこと、および運用を終えた CA を支えるリポジトリは利用できない場合があることを強調するために行われました。
3. Overview of Test PIV Cards
3. テスト用 PIV カードの概要
This section provides a brief overview of each of the test cards.
この節では、各テスト用カードの概要を簡単に示します。
Test PIV Card 1:
テスト用 PIV カード 1:
Test PIV Card 1 is based on the PIV Cards that are currently issued by the U.S. General Services Administration's USAccess program (http://www.fedidcard.gov), which issues PIV Cards for many federal agencies. Test PIV Card 1 contains many of the optional data objects specified in SP 800-73-2, but none of the data objects that were newly specified in SP 800-73-3. All of the certificates on Test PIV Card 1 contain 2048-bit RSA public keys and all of the certificates and data objects are signed using RSA PKCS #1 v1.5 with SHA-256. The PIV Authentication certificate on Test PIV Card 1 includes a User Principal Name (UPN) in the subjectAltName extension and has an extended key usage extension that asserts the client authentication and smart card logon object identifiers (OIDs) in addition to the anyExtendedKeyUsage OID.
テスト用 PIV カード 1 は、米国一般調達局(GSA)の USAccess プログラム(http://www.fedidcard.gov)が現在発行している PIV カードに基づいています。USAccess プログラムは、多くの連邦機関のために PIV カードを発行しています。テスト用 PIV カード 1 には、SP 800-73-2 で規定されたオプションのデータオブジェクトの多くが含まれていますが、SP 800-73-3 で新たに規定されたデータオブジェクトは含まれていません。テスト用 PIV カード 1 のすべての証明書には 2048 ビットの RSA 公開鍵が含まれ、すべての証明書とデータオブジェクトは、SHA-256 を用いた RSA PKCS #1 v1.5 で署名されています。テスト用 PIV カード 1 の PIV 認証証明書には、subjectAltName 拡張にユーザープリンシパル名(UPN)が含まれ、拡張鍵用途(extended key usage)拡張には、anyExtendedKeyUsage の OID に加えて、クライアント認証とスマートカードログオンのオブジェクト識別子(OID)が主張されています。
Test PIV Card 2:
テスト用 PIV カード 2:
Test PIV Card 2 is similar to Test PIV Card 1, except that certificates and data objects are signed using RSASSA-PSS rather than RSA PKCS #1 v1.5, and CAs, OCSP responders, and content signers use 3072-bit RSA keys rather than 2048-bit RSA keys. Other differences are that the cardholder is a contractor rather than an employee, and the PIV Authentication certificate does not include a user principal name (UPN) in the subjectAltName extension and does not include an extended key usage extension. The Card Authentication certificate on Test PIV Card 2 is the only certificate in the test set that has an empty subject name. The fingerprint data object does not contain any finger views, since none of the cardholder's fingerprints could be imaged. In addition, Test PIV Card 2 includes a Key History object, but the Key History object merely indicates that no retired keys are present on the card.
テスト用 PIV カード 2 はテスト用 PIV カード 1 に似ていますが、証明書とデータオブジェクトが RSA PKCS #1 v1.5 ではなく RSASSA-PSS で署名されており、CA、OCSP レスポンダー、コンテンツ署名者が 2048 ビットではなく 3072 ビットの RSA 鍵を使用している点が異なります。そのほかの違いとして、カード所持者が従業員ではなく契約者であること、PIV 認証証明書の subjectAltName 拡張にユーザープリンシパル名(UPN)が含まれていないこと、および拡張鍵用途拡張が含まれていないことがあります。テスト用 PIV カード 2 のカード認証証明書は、テスト用カード群の中で、サブジェクト名が空である唯一の証明書です。カード所持者の指紋をいずれも撮像できなかったため、指紋データオブジェクトにはフィンガービューが含まれていません。さらに、テスト用 PIV カード 2 には Key History オブジェクトが含まれていますが、この Key History オブジェクトは、廃止された鍵がカード上に存在しないことを示しているにすぎません。
Test PIV Card 3:
テスト用 PIV カード 3:
Like Test PIV Card 1, the certificates on Test PIV Card 3 contain 2048-bit RSA keys and are signed using RSA PKCS #1 v1.5 with SHA-256. However, Test PIV Card 3 differs from Test PIV Card 1 and Test PIV Card 2 in a number of ways. The PIV Authentication certificate on Test PIV Card 3 includes an extended key usage extension that asserts the client authentication and anyExtendedKeyUsage OIDs, but not the smart card logon OID. The subject name in the PIV Authentication certificate contains the card's FASC-N rather than the cardholder's name. The PIV Authentication certificate also does not include a UPN in the subjectAltName extension. The GUID data element of the CHUID contains a UUID, and this UUID is also included in the PIV Authentication certificate, the Card Authentication certificate, and the signed data objects, as specified in SP 800-73-3. Test PIV Card 3 includes a Discovery object that indicates that the Global PIN may be used to unlock the PIV Card Application and that the Global PIN is the primary PIN used to unlock the PIV Card Application. Test PIV Card 3 is the only card in the set of test cards for which the biometric data objects are signed using a different key than the CHUID and the Security Object. Finally, Test PIV Card 3 includes a Key History object that indicates that there are three retired key management keys on the card (one 1024-bit RSA key and two 2048-bit RSA keys) and that the corresponding certificates for all three retired keys are also stored on the card. No URL is provided to obtain the retired certificates for key management from an off-card source.
テスト用 PIV カード 1 と同様に、テスト用 PIV カード 3 の証明書には 2048 ビットの RSA 鍵が含まれ、SHA-256 を用いた RSA PKCS #1 v1.5 で署名されています。ただし、テスト用 PIV カード 3 は、テスト用 PIV カード 1 およびテスト用 PIV カード 2 といくつかの点で異なります。テスト用 PIV カード 3 の PIV 認証証明書には、クライアント認証と anyExtendedKeyUsage の OID を主張する拡張鍵用途拡張が含まれていますが、スマートカードログオンの OID は含まれていません。PIV 認証証明書のサブジェクト名には、カード所持者の氏名ではなく、カードの FASC-N が含まれています。PIV 認証証明書の subjectAltName 拡張にも UPN は含まれていません。CHUID の GUID データ要素には UUID が含まれており、SP 800-73-3 で規定されているとおり、この UUID は PIV 認証証明書、カード認証証明書、および署名付きデータオブジェクトにも含まれています。テスト用 PIV カード 3 には、グローバル PIN で PIV カードアプリケーションのロックを解除できること、およびグローバル PIN が PIV カードアプリケーションのロック解除に使う主要な PIN であることを示す Discovery オブジェクトが含まれています。テスト用 PIV カード 3 は、バイオメトリクスのデータオブジェクトが CHUID および Security Object とは異なる鍵で署名されている、テスト用カード群の中で唯一のカードです。最後に、テスト用 PIV カード 3 には、カード上に 3 つの廃止された鍵管理用の鍵(1024 ビットの RSA 鍵が 1 つ、2048 ビットの RSA 鍵が 2 つ)があり、廃止された 3 つの鍵すべてに対応する証明書もカードに格納されていることを示す Key History オブジェクトが含まれています。鍵管理用の廃止された証明書をカード外の取得元から入手するための URL は提供されていません。
Test PIV Card 4:
テスト用 PIV カード 4:
All of the current certificates and data objects on Test PIV Card 4 are signed using ECDSA (Curve P-256) with SHA-256 and all of the current certificates on the card contain ECC Curve P-256 subject public keys.1 While the PIV Authentication certificate includes a UPN in the subjectAltName extension, it does not include an extended key usage extension. Test PIV Card 4 includes a Discovery object that indicates that the Global PIN may be used to unlock the PIV Card Application, but that the PIV Card Application PIN is the primary PIN used to unlock the PIV Card Application. Finally, Test PIV Card 4 includes a Key History object that indicates that there are five retired key management keys on the card (three 2048-bit RSA keys and two ECC Curve P-256 keys) and that the certificates corresponding to three of the keys are also stored on the card. A URL is provided that refers to a file containing all of the retired certificates for key management.
テスト用 PIV カード 4 上の現在の証明書とデータオブジェクトはすべて、SHA-256 を用いた ECDSA(曲線 P-256)で署名されており、カード上の現在の証明書はすべて ECC 曲線 P-256 のサブジェクト公開鍵を含んでいます。1PIV 認証証明書の subjectAltName 拡張には UPN が含まれていますが、拡張鍵用途拡張は含まれていません。テスト用 PIV カード 4 には、グローバル PIN で PIV カードアプリケーションのロックを解除できるものの、PIV カードアプリケーションのロック解除に使う主要な PIN は PIV カードアプリケーション PIN であることを示す Discovery オブジェクトが含まれています。最後に、テスト用 PIV カード 4 には、カード上に 5 つの廃止された鍵管理用の鍵(2048 ビットの RSA 鍵が 3 つ、ECC 曲線 P-256 の鍵が 2 つ)があり、そのうち 3 つの鍵に対応する証明書もカードに格納されていることを示す Key History オブジェクトが含まれています。鍵管理用の廃止された証明書をすべて含むファイルを指す URL が提供されています。
Test PIV Card 5:
テスト用 PIV カード 5:
All of the current certificates and data objects on Test PIV Card 5 are signed using ECDSA (Curve P-384) with SHA-384. The digital signature and key management keys on Test PIV Card 5 are ECC Curve P-384 while the PIV Authentication and Card Authentication keys are ECC Curve P-256. Like the PIV Authentication certificate on Test PIV Card 2, the PIV Authentication certificate on Test PIV Card 5 does not include an extended key usage extension and does not include any name forms in the subjectAltName extension other than the FASC-N. The GUID data element of the CHUID contains an IPv6 address rather than all zeros. Test PIV Card 5 includes a Key History object that indicates that there are five retired key management keys on the card (two 2048-bit RSA, two ECC Curve P-256, one ECC Curve P-384), but that none of the corresponding certificates are stored on the card. A URL is provided that refers to a file containing all of the retired certificates for key management.
テスト用 PIV カード 5 上の現在の証明書とデータオブジェクトはすべて、SHA-384 を用いた ECDSA(曲線 P-384)で署名されています。テスト用 PIV カード 5 のデジタル署名用の鍵と鍵管理用の鍵は ECC 曲線 P-384 であり、PIV 認証用の鍵とカード認証用の鍵は ECC 曲線 P-256 です。テスト用 PIV カード 2 の PIV 認証証明書と同様に、テスト用 PIV カード 5 の PIV 認証証明書には、拡張鍵用途拡張が含まれておらず、subjectAltName 拡張に FASC-N 以外の名前形式も含まれていません。CHUID の GUID データ要素には、オールゼロではなく IPv6 アドレスが含まれています。テスト用 PIV カード 5 には、カード上に 5 つの廃止された鍵管理用の鍵(2048 ビットの RSA が 2 つ、ECC 曲線 P-256 が 2 つ、ECC 曲線 P-384 が 1 つ)があるものの、対応する証明書はいずれもカードに格納されていないことを示す Key History オブジェクトが含まれています。鍵管理用の廃止された証明書をすべて含むファイルを指す URL が提供されています。
Test PIV Card 6:
テスト用 PIV カード 6:
Test PIV Card 6 only contains those data objects that are listed as mandatory in SP 800-73-3 (except for the Discovery object, which is present on every test card). Test PIV Card 6 includes a PIV Authentication certificate, but no Card Authentication certificate, digital signature certificate, or key management certificate. The subject name in the PIV Authentication certificate contains the card's FASC-N rather than the cardholder's name and the subjectAltName extension in the PIV Authentication certificate only includes the card's FASC-N. The PIV Authentication certificate does not include an extended key usage extension. The card's FASC-N indicates that the cardholder is a contractor and the NACI indicator extension in the PIV Authentication certificate indicates that the cardholder's NACI had not been completed at the time that the certificate was issued. Neither the Cardholder Facial Image nor the Printed Information buffer is present on the card.
テスト用 PIV カード 6 には、SP 800-73-3 で必須とされているデータオブジェクトのみが含まれています(Discovery オブジェクトを除きます。Discovery オブジェクトはすべてのテスト用カードに存在します)。テスト用 PIV カード 6 には PIV 認証証明書が含まれていますが、カード認証証明書、デジタル署名証明書、鍵管理証明書はありません。PIV 認証証明書のサブジェクト名には、カード所持者の氏名ではなくカードの FASC-N が含まれ、PIV 認証証明書の subjectAltName 拡張にはカードの FASC-N のみが含まれています。PIV 認証証明書には、拡張鍵用途拡張は含まれていません。カードの FASC-N はカード所持者が契約者であることを示しており、PIV 認証証明書の NACI インジケーター拡張は、証明書の発行時点でカード所持者の NACI が完了していなかったことを示しています。Cardholder Facial Image も Printed Information バッファーも、カード上には存在しません。
Test PIV Card 7:
テスト用 PIV カード 7:
Test PIV Card 7 represents a legacy PIV Card by using RSA PKCS #1 v1.5 with SHA-1 rather than RSA PKCS #1 v1.5 with SHA-256 to sign the certificates and data objects on the card. In addition, the PIV Authentication and Card Authentication keys are 1024-bit RSA rather than 2048-bit RSA. Like Test PIV Card 1, the PIV Authentication certificate on Test PIV Card 7 includes a UPN in the subjectAltName extension and includes an extended key usage extension that asserts the client authentication, smart card logon, and anyExtendedKeyUsage OIDs. Test PIV Card 7 is the only card other than Test PIV Card 3 that includes a Discovery object that indicates that the Global PIN is the primary PIN to unlock the PIV Card Application. Test PIV Card 7 also includes a Key History object that indicates that there are five retired key management keys on the card (one 1024-bit RSA key and four 2048-bit RSA keys) and that the certificates corresponding to three of these keys are stored on the card. A URL is provided that refers to a file containing all of the retired certificates for key management.
テスト用 PIV カード 7 は、カード上の証明書とデータオブジェクトの署名に、SHA-256 を用いた RSA PKCS #1 v1.5 ではなく SHA-1 を用いた RSA PKCS #1 v1.5 を使うことで、レガシーな PIV カードを表しています。加えて、PIV 認証用の鍵とカード認証用の鍵は、2048 ビットの RSA ではなく 1024 ビットの RSA です。テスト用 PIV カード 1 と同様に、テスト用 PIV カード 7 の PIV 認証証明書には、subjectAltName 拡張に UPN が含まれ、クライアント認証、スマートカードログオン、anyExtendedKeyUsage の各 OID を主張する拡張鍵用途拡張が含まれています。テスト用 PIV カード 7 は、グローバル PIN が PIV カードアプリケーションのロック解除に使う主要な PIN であることを示す Discovery オブジェクトを含む、テスト用 PIV カード 3 以外で唯一のカードです。テスト用 PIV カード 7 には、カード上に 5 つの廃止された鍵管理用の鍵(1024 ビットの RSA 鍵が 1 つ、2048 ビットの RSA 鍵が 4 つ)があり、そのうち 3 つの鍵に対応する証明書がカードに格納されていることを示す Key History オブジェクトも含まれています。鍵管理用の廃止された証明書をすべて含むファイルを指す URL が提供されています。
Test PIV Card 8:
テスト用 PIV カード 8:
The PIV Authentication, Card Authentication, digital signature, and key management certificates on Test PIV Card 8 contain long serial numbers (up to 20 octets). The PIV Authentication certificate includes a UPN, but the extended key usage extension does not assert the smart card logon OID. Instead the extended key usage extension includes OIDs for TLS client authentication, PKINT client authentication, EAP over PPP, EAP over LAN, and anyExtendedKeyUsage. The NACI indicator extension in the PIV Authentication and Card Authentication certificates indicates that the cardholder's NACI had not been completed at the time that the certificate was issued. Test PIV Card 8 includes a Discovery object that indicates that the Global PIN may be used to unlock the PIV Card Application, but that the PIV Card Application PIN is the primary PIN used to unlock the PIV Card Application. Test PIV Card 8 includes a Key History object that indicates that there are ten retired key management keys on the card (two 1024-bit RSA and eight 2048-bit RSA) and that the certificates corresponding to three of these keys are stored on the card. A URL is provided that refers to a file containing all of the retired certificates for key management. Test PIV Card 8 also represents a scenario in which the cardholder's name has changed, and so the subject name and email address in some of the older retired certificates for key management are different than in the cardholder's current certificates.
テスト用 PIV カード 8 の PIV 認証証明書、カード認証証明書、デジタル署名証明書、鍵管理証明書には、長いシリアル番号(最大 20 オクテット)が含まれています。PIV 認証証明書には UPN が含まれていますが、拡張鍵用途拡張はスマートカードログオンの OID を指定していません。その代わり、拡張鍵用途拡張には、TLS クライアント認証、PKINT クライアント認証、EAP over PPP、EAP over LAN、anyExtendedKeyUsage の OID が含まれています。PIV 認証証明書とカード認証証明書の NACI インジケーター拡張は、証明書の発行時点でカード所持者の NACI が完了していなかったことを示しています。テスト用 PIV カード 8 には、グローバル PIN で PIV カードアプリケーションのロックを解除できるものの、PIV カードアプリケーションのロック解除に使う主要な PIN は PIV カードアプリケーション PIN であることを示す Discovery オブジェクトが含まれています。テスト用 PIV カード 8 には、カード上に 10 本の廃止された鍵管理用の鍵(1024 ビットの RSA が 2 本、2048 ビットの RSA が 8 本)があり、そのうち 3 本の鍵に対応する証明書がカードに格納されていることを示す Key History オブジェクトが含まれています。鍵管理用の廃止された証明書をすべて含むファイルを指す URL が提供されています。テスト用 PIV カード 8 は、カード所持者の氏名が変更された場面も表しており、そのため、鍵管理用の廃止された古い証明書の一部では、サブジェクト名とメールアドレスが、カード所持者の現在の証明書とは異なっています。
Test PIV Card 9:
テスト用 PIV カード 9:
Test PIV Card 9 is similar to Test PIV Card 1, except that Test PIV Card 9 is expired. Test PIV Card 9 is a short-term card that was issued to a contractor whose NACI had not been completed at the time that the certificates on the card were issued.
テスト用 PIV カード 9 はテスト用 PIV カード 1 に似ていますが、テスト用 PIV カード 9 は有効期限が切れている点が異なります。テスト用 PIV カード 9 は、カード上の証明書が発行された時点で NACI が完了していなかった契約者に発行された、短期のカードです。
Test PIV Card 10:
テスト用 PIV カード 10:
Test PIV Card 10 represents a card that has been reported as lost. The PIV Authentication, Card Authentication, digital signature, and key management certificates have all been revoked with a reason code of key compromise. Test PIV Card 10 includes a Key History object that indicates that there are five retired key management keys on the card (all 2048-bit RSA keys) and that the certificate corresponding to one of these keys is stored on the card. A URL is provided that refers to a file containing all of the retired certificates for key management.
テスト用 PIV カード 10 は、紛失が届け出られたカードを表しています。PIV 認証証明書、カード認証証明書、デジタル署名証明書、鍵管理証明書はすべて、理由コードを鍵の危殆化として失効しています。テスト用 PIV カード 10 には、カード上に 5 つの失効した鍵管理用の鍵(すべて 2048 ビットの RSA 鍵)があり、そのうち 1 つの鍵に対応する証明書がカードに格納されていることを示す Key History オブジェクトが含まれています。鍵管理用の失効した証明書をすべて含むファイルを指す URL が提供されています。
Test PIV Card 11:
テスト用 PIV カード 11:
Test PIV Card 11 represents a card that was created by an adversary in order to attempt to impersonate the holder of Test PIV Card 1. None of the signatures on any of the certificates or data objects are valid. The certificates on Test PIV Card 11 are identical to the certificates on Test PIV Card 1, except that the subject public keys correspond to the private keys that are on Test PIV Card 11. The biometric data (fingerprints and facial image) are those of the adversary.
テスト用 PIV カード 11 は、テスト用 PIV カード 1 の所持者になりすまそうとする攻撃者が作成したカードを表しています。証明書やデータオブジェクトの署名は、いずれも有効ではありません。テスト用 PIV カード 11 の証明書は、サブジェクト公開鍵がテスト用 PIV カード 11 上の秘密鍵に対応している点を除き、テスト用 PIV カード 1 の証明書と同一です。バイオメトリクスデータ(指紋と顔画像)は攻撃者のものです。
Test PIV Card 12:
テスト用 PIV カード 12:
Test PIV Card 12 represents a PIV Card that was legitimately issued but where the cardholder has managed to replace the CHUID on the card with the CHUID from Test PIV Card 1 while leaving all of the other data objects on the card unchanged. This means that all of the data objects on the card are valid, but the FASC-N in the CHUID does not match the FASC-N in the biometric data objects or in the authentication certificates. If PIV biometric authentication were performed as specified in Section 6.2.3.1 of FIPS 201-1, but the check to verify that the FASC-N in the fingerprint data object matched the FASC-N in the CHUID data object was skipped, then the holder of Test PIV Card 12 could authenticate as the holder of Test PIV Card 1.
テスト用 PIV カード 12 は、正規に発行された PIV カードでありながら、カード所持者がカード上のほかのデータオブジェクトを変更しないまま、カード上の CHUID をテスト用 PIV カード 1 の CHUID に置き換えることに成功した場合を表しています。これは、カード上のすべてのデータオブジェクトは有効であるものの、CHUID 内の FASC-N が、バイオメトリクスのデータオブジェクトや認証証明書内の FASC-N と一致しないことを意味します。FIPS 201-1 の 6.2.3.1 節の規定どおりに PIV バイオメトリクス認証を実行しても、指紋データオブジェクト内の FASC-N が CHUID データオブジェクト内の FASC-N と一致することを検証する確認を省略した場合、テスト用 PIV カード 12 の所持者は、テスト用 PIV カード 1 の所持者として認証できてしまう可能性があります。
Test PIV Card 13:
テスト用 PIV カード 13:
On Test PIV Card 13, the card has not expired, but the PIV Authentication, Card Authentication, digital signature, and key management certificates have expired. Like Test PIV Card 7, the PIV Authentication and Card Authentication keys are 1024-bit RSA and all four of the cardholder's certificates were signed using RSA PKCS #1 v1.5 with SHA-1.
テスト用 PIV カード 13 では、カードの有効期限は切れていませんが、PIV 認証証明書、カード認証証明書、デジタル署名証明書、鍵管理証明書の有効期限は切れています。テスト用 PIV カード 7 と同様に、PIV 認証用の鍵とカード認証用の鍵は 1024 ビットの RSA で、カード所持者の 4 つの証明書はすべて、SHA-1 を用いた RSA PKCS #1 v1.5 で署名されています。
Test PIV Card 14:
テスト用 PIV カード 14:
On Test PIV Card 14, the certificate corresponding to the private key used to sign the CHUID, Security object, and biometric data objects on the card has been revoked with a revocation reason of key compromise. The cardholder's certificates are valid. Test PIV Card 14 includes a Key History object that indicates that there are five retired key management keys on the card (all 2048-bit RSA) and that the certificate corresponding to one of the keys is stored on the card. A URL is provided that refers to a file containing all of the retired certificates for key management.
テスト用 PIV カード 14 では、カード上の CHUID、Security object、バイオメトリクスのデータオブジェクトの署名に使われた秘密鍵に対応する証明書が、失効理由を鍵の危殆化として失効しています。カード所持者の証明書は有効です。テスト用 PIV カード 14 には、カード上に 5 つの失効した鍵管理用の鍵(すべて 2048 ビットの RSA)があり、そのうち 1 つの鍵に対応する証明書がカードに格納されていることを示す Key History オブジェクトが含まれています。鍵管理用の失効した証明書をすべて含むファイルを指す URL が提供されています。
Test PIV Card 15:
テスト用 PIV カード 15:
Like Test PIV Card 10, Test PIV Card 15 also represents a card that has been reported as lost. On Test PIV Card 15, however, all of the current certificates and data objects have been signed using ECDSA (Curve P-256) with SHA-256 and all of the cardholder's current certificates contain ECC Curve P-256 subject public keys. The PIV Authentication, Card Authentication, digital signature, and key management certificates have been revoked with a revocation reason of key compromise. Test PIV Card 15 includes a Key History object that indicates that there are five retired key management keys on the card (one 1024-bit RSA, two 2048-bit RSA, and two ECC Curve P-256) and that the certificates corresponding to three of these keys are stored on the card. A URL is provided that refers to a file containing all of the retired certificates for key management.
テスト用 PIV カード 10 と同様に、テスト用 PIV カード 15 も、紛失が届け出られたカードを表しています。ただし、テスト用 PIV カード 15 では、現在の証明書とデータオブジェクトはすべて SHA-256 を用いた ECDSA(曲線 P-256)で署名されており、カード所持者の現在の証明書はすべて ECC 曲線 P-256 のサブジェクト公開鍵を含んでいます。PIV 認証証明書、カード認証証明書、デジタル署名証明書、鍵管理証明書は、秘密鍵の侵害を失効理由として失効しています。テスト用 PIV カード 15 には、カード上に 5 つの廃止された鍵管理用の鍵(1024 ビットの RSA が 1 つ、2048 ビットの RSA が 2 つ、ECC 曲線 P-256 が 2 つ)があり、そのうち 3 つの鍵に対応する証明書がカードに格納されていることを示す Key History オブジェクトが含まれています。鍵管理用の廃止された証明書をすべて含むファイルを指す URL が提供されています。
Test PIV Card 16:
テスト用 PIV カード 16:
Test PIV-I Card 16 represents a PIV-I Card rather than a PIV Card. The GUID data element of the CHUID contains a UUID and the FASC-N data element of the CHUID contains a value that indicates that the card is a PIV-I card. The UUID from the GUID data element is included in the signed data objects and in the authentication certificates instead of the FASC-N, as specified in SP 800-73-3.
テスト用 PIV-I カード 16 は、PIV カードではなく PIV-I カードを表しています。CHUID の GUID データ要素には UUID が含まれ、CHUID の FASC-N データ要素には、カードが PIV-I カードであることを示す値が含まれています。SP 800-73-3 で規定されているとおり、GUID データ要素の UUID は、FASC-N の代わりに、署名付きデータオブジェクトと認証証明書に含まれています。
Appendix A—Acronyms
付録 A—頭字語
| CA | Certification Authority |
| CHUID | Card Holder Unique Identifier |
| CRL | Certificate Revocation List |
| EAP | Extensible Authentication Protocol |
| ECC | Elliptic Curve Cryptography |
| ECDSA | Elliptic Curve Digital Signature Algorithm |
| FASC-N | Federal Agency Smart Credential Number |
| FIPS | Federal Information Processing Standard |
| GUID | Global Unique Identification Number |
| HTTP | Hypertext Transfer Protocol |
| IETF | Internet Engineering Task Force |
| IPv6 | Internet Protocol version 6 |
| LAN | Local Area Network |
| LDAP | Lightweight Directory Access Protocol |
| NACI | National Agency Check with Inquiries |
| NIST | National Institute of Standards and Technology |
| OCSP | Online Certificate Status Protocol |
| OID | Object Identifier |
| PIN | Personal Identification Number |
| PIV | Personal Identity Verification |
| PKCS | Public-Key Cryptography Standards |
| PPP | Point-to-Point Protocol |
| RFC | Request for Comments |
| RSA | Rivest, Shamir, Adleman cryptographic algorithm |
| RSASSA-PSS | RSA Signature Scheme with Appendix - Probabilistic Signature Scheme |
| SHA | Secure Hash Algorithm |
| SP | Special Publication |
| TLS | Transport Layer Security |
| UPN | User Principal Name |
| URI | Uniform Resource Identifier |
| URN | Uniform Resource Name |
| UUID | Universally Unique Identifier |
| CA | 認証局 |
| CHUID | カード所持者固有識別子 |
| CRL | 証明書失効リスト |
| EAP | 拡張認証プロトコル |
| ECC | 楕円曲線暗号 |
| ECDSA | 楕円曲線デジタル署名アルゴリズム |
| FASC-N | 連邦機関スマート資格情報番号 |
| FIPS | 連邦情報処理規格 |
| GUID | グローバル一意識別番号 |
| HTTP | ハイパーテキスト転送プロトコル |
| IETF | インターネット技術タスクフォース |
| IPv6 | インターネットプロトコルバージョン 6 |
| LAN | ローカルエリアネットワーク |
| LDAP | Lightweight Directory Access Protocol |
| NACI | 照会付き国家機関調査 |
| NIST | 米国標準技術研究所 |
| OCSP | オンライン証明書状態プロトコル |
| OID | オブジェクト識別子 |
| PIN | 個人識別番号 |
| PIV | 個人識別検証 |
| PKCS | 公開鍵暗号標準 |
| PPP | ポイントツーポイントプロトコル |
| RFC | Request for Comments |
| RSA | Rivest、Shamir、Adleman の暗号アルゴリズム |
| RSASSA-PSS | 付録付き RSA 署名方式 - 確率的署名方式 |
| SHA | セキュアハッシュアルゴリズム |
| SP | 特別刊行物 |
| TLS | トランスポート層セキュリティ |
| UPN | ユーザープリンシパル名 |
| URI | Uniform Resource Identifier |
| URN | Uniform Resource Name |
| UUID | 汎用一意識別子 |
Appendix B—References
付録 B—参考文献
[FIPS201] Federal Information Processing Standard 201-1, Change Notice 1, Personal Identity Verification (PIV) Federal Employees and Contractors, March 2006.
[FIPS201] Federal Information Processing Standard 201-1, Change Notice 1, Personal Identity Verification (PIV) Federal Employees and Contractors, 2006 年 3 月。
[SP800-73] NIST Special Publication 800-73-3, Interfaces for Personal Identity Verification, February 2010.
[SP800-73] NIST Special Publication 800-73-3, Interfaces for Personal Identity Verification, 2010 年 2 月。
[SP800-78] NIST Special Publication 800-78-3, Cryptographic Algorithms and Key Sizes for Personal Identity Verification, December 2010.
[SP800-78] NIST Special Publication 800-78-3, Cryptographic Algorithms and Key Sizes for Personal Identity Verification, 2010 年 12 月。
[RFC4122] IETF RFC 4122, “A Universally Unique Identifier (UUID) URN Namespace,” July 2005.
[RFC4122] IETF RFC 4122, “A Universally Unique Identifier (UUID) URN Namespace,” 2005 年 7 月。