NIST IR 8183 Rev. 1 日本語訳
英語タイトル : Cybersecurity Framework Version 1.1 Manufacturing Profile日本語タイトル : サイバーセキュリティフレームワーク バージョン1.1 製造プロファイル
公開日 : 2020-10-07
原文URL : https://csrc.nist.gov/pubs/ir/8183/r1/final
翻訳編集 : 自動生成(有志による非公式の日本語訳), 原文取得日 : 2026-10-31, 訳文 : 308 / 308 ブロック
[要約] NIST IR 8183 Rev. 1 は、製造環境向けに策定されたサイバーセキュリティフレームワーク(CSF)バージョン1.1 の実装の詳細を示す報告書です。CSF の製造プロファイルは、製造業のセクターの目標と業界のベストプラクティスに沿って、製造者のサイバーセキュリティリスクを低減するためのロードマップとして使用できるものです。製造プロファイルは、サイバーセキュリティ活動を管理し、製造システムに対するサイバーリスクを低減するための、任意でリスクに基づくアプローチを提供し、製造者が採用している現行のサイバーセキュリティ標準や業界ガイドラインを補強することを意図したもので、置き換えるものではありません。報告書は、製造システムとフレームワークの概要、製造プロファイルの策定アプローチ、製造における事業・ミッション目標、製造システムの分類とリスク管理、サブカテゴリ指針を示しています。
NISTIR 8183
NISTIR 8183
Revision 1
改訂第1版
Cybersecurity Framework Version 1.1 Manufacturing Profile
サイバーセキュリティフレームワーク バージョン1.1 製造プロファイル
Keith Stouffer Timothy Zimmerman CheeYee Tang Joshua Lubell Jeffrey Cichonski Michael Pease John McCarthy
Keith Stouffer Timothy Zimmerman CheeYee Tang Joshua Lubell Jeffrey Cichonski Michael Pease John McCarthy
This publication is available free of charge from: https://doi.org/10.6028/NIST.IR.8183r1
本書は以下から無料で入手できます:https://doi.org/10.6028/NIST.IR.8183r1
NISTIR 8183
NISTIR 8183
Revision 1
改訂第1版
Cybersecurity Framework Version 1.1 Manufacturing Profile
サイバーセキュリティフレームワーク バージョン1.1 製造プロファイル
Keith Stouffer Timothy Zimmerman CheeYee Tang Michael Pease
Keith Stouffer Timothy Zimmerman CheeYee Tang Michael Pease
Intelligent Systems Division Engineering Laboratory
インテリジェントシステム部門 工学研究所
Joshua Lubell
Joshua Lubell
Systems Integration Division Engineering Laboratory
システム統合部門 工学研究所
Jeffrey Cichonski
Jeffrey Cichonski
Applied Cybersecurity Division Information Technology Laboratory
応用サイバーセキュリティ部門 情報技術研究所
John McCarthy Dakota Consulting, Inc. Silver Spring, MD
John McCarthy Dakota Consulting, Inc. Silver Spring, MD
This publication is available free of charge from: https://doi.org/10.6028/NIST.IR.8183r1
本書は以下から無料で入手できます:https://doi.org/10.6028/NIST.IR.8183r1
October 2020
2020年10月
U.S. Department of Commerce Wilbur L. Ross, Jr., Secretary
米国商務省 Wilbur L. Ross, Jr. 長官
National Institute of Standards and Technology
米国国立標準技術研究所
Walter Copan, NIST Director and Under Secretary of Commerce for Standards and Technology
Walter Copan、NIST 所長兼商務次官(標準・技術担当)
National Institute of Standards and Technology Internal Report 8183 Revision 1 60 pages (October 2020)
米国国立標準技術研究所 内部報告書 8183 改訂第1版 60ページ(2020年10月)
This publication is available free of charge from: https://doi.org/10.6028/NIST.IR.8183r1
本書は以下から無料で入手できます:https://doi.org/10.6028/NIST.IR.8183r1
Certain commercial entities, equipment, or materials may be identified in this document in order to describe an experimental procedure or concept adequately. Such identification is not intended to imply recommendation or endorsement by NIST, nor is it intended to imply that the entities, materials, or equipment are necessarily the best available for the purpose.
本書では、実験手順や概念を適切に説明するために、特定の営利団体、機器、材料に言及する場合があります。このような記載は、NISTによる推奨や承認を意味するものではなく、それらの団体、材料、機器が目的に照らして必ずしも最良であることを意味するものでもありません。
There may be references in this publication to other publications currently under development by NIST in accordance with its assigned statutory responsibilities. The information in this publication, including concepts and methodologies, may be used by federal agencies even before the completion of such companion publications. Thus, until each publication is completed, current requirements, guidelines, and procedures, where they exist, remain operative. For planning and transition purposes, federal agencies may wish to closely follow the development of these new publications by NIST.
本刊行物では、NISTに割り当てられた法的責任に従って現在策定中の他の刊行物に言及する場合があります。概念や方法論を含む本刊行物の情報は、そうした関連刊行物の完成前であっても連邦機関が使用できます。したがって、各刊行物が完成するまでは、既存の要件、指針、手順がある場合、それらが引き続き有効です。計画および移行のため、連邦機関は、NIST によるこれらの新しい刊行物の策定状況を注意深く追うことを検討してもよいです。
Organizations are encouraged to review all draft publications during public comment periods and provide feedback to NIST. All NIST Computer Security Division publications, other than the ones noted above, are available at http://csrc.nist.gov/publications.
組織には、公開意見募集期間中にすべての草案刊行物を確認し、NISTに意見を提出することが推奨されます。上記のものを除くNISTコンピュータセキュリティ部門のすべての刊行物は、http://csrc.nist.gov/publications から入手できます。
Comments on this publication may be submitted to:
本刊行物に関する意見の提出先
National Institute of Standards and Technology Attn: Applied Cybersecurity Division, Information Technology Laboratory 100 Bureau Drive (Mail Stop 2000) Gaithersburg, MD 20899-2000 Email: CSF_Manufacturing_Profile@nist.gov
National Institute of Standards and Technology Attn: Applied Cybersecurity Division, Information Technology Laboratory 100 Bureau Drive (Mail Stop 2000) Gaithersburg, MD 20899-2000 Email: CSF_Manufacturing_Profile@nist.gov
All comments are subject to release under the Freedom of Information Act (FOIA).
すべての意見は、情報自由法(FOIA)に基づいて公開される場合があります。
Reports on Computer Systems Technology
コンピュータシステム技術に関する報告書
The Information Technology Laboratory (ITL) at the National Institute of Standards and Technology (NIST) promotes the U.S. economy and public welfare by providing technical leadership for the Nation’s measurement and standards infrastructure. ITL develops tests, test methods, reference data, proof of concept implementations, and technical analyses to advance the development and productive use of information technology. ITL’s responsibilities include the development of management, administrative, technical, and physical standards and guidelines for the cost-effective security and privacy of other than national security-related information in federal information systems.
米国国立標準技術研究所(NIST)の情報技術研究所(ITL)は、国の測定・標準基盤に対する技術的リーダーシップを提供することで、米国経済と公共の福祉の向上に貢献しています。ITLは、情報技術の発展と生産的な活用を進めるため、試験、試験方法、参照データ、概念実証の実装、技術分析を開発しています。ITLの責務には、連邦情報システムにおける国家安全保障関連以外の情報のセキュリティとプライバシーについて、費用対効果の高い管理的、事務的、技術的、物理的な標準および指針を策定することが含まれます。
Abstract
概要
This document provides the Cybersecurity Framework (CSF) Version 1.1 implementation details developed for the manufacturing environment. The “Manufacturing Profile” of the CSF can be used as a roadmap for reducing cybersecurity risk for manufacturers that is aligned with manufacturing sector goals and industry best practices. This Manufacturing Profile provides a voluntary, risk-based approach for managing cybersecurity activities and reducing cyber risk to manufacturing systems. The Manufacturing Profile is meant to enhance but not replace current cybersecurity standards and industry guidelines that the manufacturer is embracing.
本書は、製造環境向けに策定されたサイバーセキュリティフレームワーク(CSF)バージョン1.1の実装の詳細を示します。CSFの「製造プロファイル」は、製造業のセクターの目標と業界のベストプラクティスに沿って、製造者のサイバーセキュリティリスクを低減するためのロードマップとして使用できます。本製造プロファイルは、サイバーセキュリティ活動を管理し、製造システムに対するサイバーリスクを低減するための、任意で、リスクに基づくアプローチを提供します。製造プロファイルは、製造者が採用している現行のサイバーセキュリティ標準や業界ガイドラインを補強することを意図したものであり、置き換えるものではありません。
Keywords
キーワード
Computer security; Cybersecurity Framework (CSF); distributed control systems (DCS); industrial control systems (ICS); information security; manufacturing; network security; programmable logic controllers (PLC); risk management; security controls; supervisory control and data acquisition (SCADA) systems.
コンピュータセキュリティ、サイバーセキュリティフレームワーク(CSF)、分散制御システム(DCS)、産業用制御システム(ICS)、情報セキュリティ、製造、ネットワークセキュリティ、プログラマブルロジックコントローラー(PLC)、リスク管理、セキュリティ管理策、監視制御およびデータ収集(SCADA)システム
Acknowledgments
謝辞
The authors gratefully acknowledge and appreciate the significant contributions from individuals and organizations in the public and private sectors, whose thoughtful and constructive comments improved the overall quality, thoroughness, and usefulness of this publication. A special acknowledgement to the members of the Department of Homeland Security Industrial Control System Joint Working Group (ICSJWG) for their exceptional contributions to this publication.
著者らは、公的部門および民間部門の個人や組織から寄せられた、思慮深く建設的な意見によって、本刊行物の全体的な品質、網羅性、有用性が向上したことに深く感謝します。とりわけ、国土安全保障省産業用制御システム合同作業部会(ICSJWG)のメンバーには、本刊行物への格別の貢献に対して特別な謝意を表します。
Note to Readers on the Update
更新に関する読者への注記
NISTIR 8183 Revision 1 updates the Manufacturing Profile to include the sub-category enhancements established in NIST Framework for Improving Critical Infrastructure Cybersecurity Version 1.1. These updates include managing cybersecurity within the supply chain, self-assessing cybersecurity risk, vulnerability disclosure, system integrity, and more comprehensive controls for identity management. Additional changes include updating language to change references from “security levels” to “impact levels.”
NISTIR 8183 改訂第1版は、NIST Framework for Improving Critical Infrastructure Cybersecurity Version 1.1 で定められたサブカテゴリの拡充を反映して、製造プロファイルを更新したものです。この更新には、サプライチェーン内のサイバーセキュリティの管理、サイバーセキュリティリスクの自己評価、脆弱性の開示、システムの完全性、およびアイデンティティ管理に関するより包括的な管理策が含まれます。そのほかの変更として、「セキュリティレベル」への言及を「影響レベル」に改めるよう文言を更新しています。
Patent Disclosure Notice
特許開示に関する通知
NOTICE: ITL has requested that holders of patent claims whose use may be required for compliance with the guidance or requirements of this publication disclose such patent claims to ITL. However, holders of patents are not obligated to respond to ITL calls for patents and ITL has not undertaken a patent search in order to identify which, if any, patents may apply to this publication.
通知:ITLは、本刊行物の指針または要件への準拠に使用が必要となる可能性のある特許請求の範囲の保有者に対し、その特許請求の範囲をITLに開示するよう求めています。ただし、特許の保有者にはITLの特許開示要請に応じる義務はなく、ITLも、本刊行物に該当する特許があるかどうかを特定するための特許調査を実施していません。
As of the date of publication and following call(s) for the identification of patent claims whose use may be required for compliance with the guidance or requirements of this publication, no such patent claims have been identified to ITL.
公表日の時点で、本刊行物の指針または要件への準拠に使用が必要となる可能性のある特許請求の範囲の特定を求めた後も、そのような特許請求の範囲はITLに特定されていません。
No representation is made or implied by ITL that licenses are not required to avoid patent infringement in the use of this publication.
ITLは、本刊行物の使用にあたって特許侵害を避けるためのライセンスが不要であることを、明示的にも黙示的にも表明するものではありません。
Executive Summary
エグゼクティブサマリー
This document provides the Cybersecurity Framework implementation details developed for the manufacturing environment. The “Manufacturing Profile” of the Cybersecurity Framework can be used as a roadmap for reducing cybersecurity risk for manufacturers that is aligned with manufacturing sector goals and industry best practices.
本書は、製造環境向けに策定されたサイバーセキュリティフレームワークの実装の詳細を示します。サイバーセキュリティフレームワークの「製造プロファイル」は、製造業のセクターの目標と業界のベストプラクティスに沿って、製造者のサイバーセキュリティリスクを低減するためのロードマップとして使用できます。
The Profile gives manufacturers:
本プロファイルは、製造者に次のものを提供します。
•A method to identify opportunities for improving the current cybersecurity posture of the manufacturing system
•製造システムの現在のサイバーセキュリティ態勢を改善する機会を特定する方法
•An evaluation of their ability to operate the control environment at their acceptable risk level
•製造者が許容できるリスクレベルで制御環境を運用する能力の評価
•A standardized approach to preparing the cybersecurity plan for ongoing assurance of the manufacturing system’s security
•製造システムのセキュリティを継続的に保証するためのサイバーセキュリティ計画を準備する標準化されたアプローチ
The Profile is built around the primary functional areas of the Cybersecurity Framework which enumerate the most basic functions of cybersecurity activities. The five primary functional areas are: Identify, Protect, Detect, Respond, and Recover. These primary functional areas comprise a starting point from which to develop a manufacturer-specific or sector-specific Profile at the defined risk levels of Low, Moderate and High.
本プロファイルは、サイバーセキュリティ活動の最も基本的な機能を列挙した、サイバーセキュリティフレームワークの主要な機能領域を軸に構成されています。5つの主要な機能領域は、識別、防御、検知、対応、復旧です。これらの主要な機能領域は、低・中・高というリスクレベルを定めたうえで、製造者固有またはセクター固有のプロファイルを策定する出発点となります。
This Manufacturing “Target” Profile focuses on desired cybersecurity outcomes and can be used as a roadmap to identify opportunities for improving the current cybersecurity posture of the manufacturing system. The Manufacturing Profile provides a prioritization of security activities to meet specific business/mission goals. Relevant and actionable security practices that can be implemented to support key business/mission goals are then identified.
この製造「目標」プロファイルは、望ましいサイバーセキュリティの成果に焦点を当てており、製造システムの現在のサイバーセキュリティ態勢を改善する機会を特定するためのロードマップとして使用できます。製造プロファイルは、特定の事業・ミッション目標を達成するためのセキュリティ活動の優先順位付けを示します。そのうえで、主要な事業・ミッション目標の支援のために実施できる、関連性が高く実行可能なセキュリティ慣行を特定します。
This Manufacturing Profile provides a voluntary, risk-based approach for managing cybersecurity activities and reducing cyber risk to manufacturing systems. The Manufacturing Profile is meant to enhance but not replace current cybersecurity standards and industry guidelines that the manufacturer is embracing.
本製造プロファイルは、サイバーセキュリティ活動を管理し、製造システムに対するサイバーリスクを低減するための、任意で、リスクに基づくアプローチを提供します。製造プロファイルは、製造者が採用している現行のサイバーセキュリティ標準や業界ガイドラインを補強することを意図したものであり、置き換えるものではありません。
Table of Contents
目次
1. Introduction
1. はじめに
The Executive Order 13636, “Improving Critical Infrastructure Cybersecurity,” [1] directed the development of the voluntary Cybersecurity Framework that provides a prioritized, flexible, repeatable, performance-based, and cost-effective approach to manage cybersecurity risk [1] for those processes, information, and systems directly involved in the delivery of critical infrastructure services.
大統領令13636「Improving Critical Infrastructure Cybersecurity」[1] は、重要インフラサービスの提供に直接関わるプロセス、情報、およびシステムにおけるサイバーセキュリティリスクを管理するための、優先順位付けされた、柔軟で、再現可能で、性能に基づく、費用対効果の高いアプローチを提供する、任意のサイバーセキュリティフレームワークの策定を指示しました [1]。
The Cybersecurity Framework is a voluntary, risk-based assemblage of industry standards and best practices designed to help organizations manage cybersecurity risks [2]. The Framework, created through collaboration between government and the private sector, uses a common language to address and manage cybersecurity risk in a cost-effective way based on business needs without imposing additional regulatory requirements.
サイバーセキュリティフレームワークは、組織がサイバーセキュリティリスクを管理するのを支援するために設計された、業界標準とベストプラクティスを任意かつリスクに基づいて集約したものです [2]。政府と民間部門の協力によって作成されたこのフレームワークは、共通の言語を用いて、追加の規制要件を課すことなく、事業上のニーズに基づく費用対効果の高い方法でサイバーセキュリティリスクに対処し、管理します。
The Manufacturing Profile (Profile) defines specific cybersecurity activities and outcomes for the protection of the manufacturing system, its components, facility, and environment. Through use of the Profile, the manufacturer can align cybersecurity activities with business requirements, risk tolerances, and resources. The Profile provides a manufacturing sector-specific approach to cybersecurity from standards, guidelines, and industry best practices.
製造プロファイル(プロファイル)は、製造システム、その構成要素、施設、および環境を保護するための具体的なサイバーセキュリティ活動と成果を定義します。製造者は、プロファイルを用いることで、サイバーセキュリティ活動を事業要件、リスク許容度、およびリソースに整合させることができます。プロファイルは、標準、指針、業界のベストプラクティスに基づく、製造業のセクターに固有のサイバーセキュリティのアプローチを提供します。
1.1 Purpose and Scope
1.1 目的と適用範囲
This document represents a “Target” Profile that focuses on the desired cybersecurity outcomes and provides an approach to the desired state of cybersecurity posture of the manufacturing system. It can be used to identify opportunities for improving a cybersecurity posture by comparing the current state with the desired (Target) state. Creating a Target Profile is Step 5 of Section 3.2: Establishing or Improving a Cybersecurity Program of the Cybersecurity Framework, Version 1.1 [2]. The Target Profile can also be used for comparison with the current state to influence process improvement priorities for the organization. The manufacturing system’s “Current” Profile represents the outcomes from the Framework Core that are currently being achieved.
本書は、望ましいサイバーセキュリティの成果に焦点を当て、製造システムのサイバーセキュリティ態勢の望ましい状態に向けたアプローチを示す「目標」プロファイルです。現在の状態と望ましい(目標)状態を比較することで、サイバーセキュリティ態勢を改善する機会を特定するのに使用できます。目標プロファイルの作成は、Cybersecurity Framework, Version 1.1 [2] の第3.2節「Establishing or Improving a Cybersecurity Program」のステップ5です。目標プロファイルは、現在の状態との比較に使用して、組織のプロセス改善の優先順位に反映させることもできます。製造システムの「現在の」プロファイルは、フレームワークコアのうち、現在達成されている成果を表します。
The Manufacturing “Target” Profile focuses on desired cybersecurity outcomes and can be used as a guideline to identify opportunities for improving the current cybersecurity posture of the manufacturing system. The Manufacturing Profile provides a prioritization of security activities to meet specific business/mission goals. Relevant and actionable security practices that can be implemented to support key business/mission goals are then identified.
この製造「目標」プロファイルは、望ましいサイバーセキュリティの成果に焦点を当てており、製造システムの現在のサイバーセキュリティ態勢を改善する機会を特定するための指針として使用できます。製造プロファイルは、特定の事業・ミッション目標を達成するためのセキュリティ活動の優先順位付けを示します。そのうえで、主要な事業・ミッション目標の支援のために実施できる、関連性が高く実行可能なセキュリティ慣行を特定します。
Comparison of Profiles (e.g., the Current Profile and Target Profile) may reveal gaps to be addressed to meet cybersecurity risk management objectives. Prioritization of gap mitigation is driven by the organization’s business needs and risk management processes. This risk-based approach enables an organization to gauge resource estimates (e.g., staffing, funding) to achieve cybersecurity goals in a cost-effective, prioritized manner. The following are examples of how the Target Profile may be used:
プロファイル同士(たとえば、現在のプロファイルと目標プロファイル)を比較すると、サイバーセキュリティリスク管理の目標を達成するために対処すべきギャップが明らかになる場合があります。ギャップを軽減する優先順位は、組織の事業上のニーズとリスク管理プロセスによって決まります。このリスクに基づくアプローチにより、組織は、サイバーセキュリティの目標を費用対効果が高く優先順位付けされた形で達成するためのリソース(たとえば、人員、資金)の見積りを行うことができます。目標プロファイルの使用例を次に示します。
•A manufacturer may utilize the Target Profile to express cybersecurity risk management requirements to an external service provider.
•製造者は、外部のサービスプロバイダーに対してサイバーセキュリティリスク管理の要件を表明するために、目標プロファイルを利用してもよいです。
•A manufacturer may express a system’s cybersecurity state through a Current Profile to report results relative to the Target Profile, or to compare with acquisition requirements.
•製造者は、目標プロファイルに対する結果を報告するため、または調達要件と比較するために、システムのサイバーセキュリティの状態を現在のプロファイルによって表してもよいです。
•A critical infrastructure owner/operator, having identified an external partner upon whom that infrastructure depends, may use the Target Profile to convey required cybersecurity outcomes.
•重要インフラの所有者/運用者は、そのインフラが依存する外部パートナーを特定したうえで、目標プロファイルを用いて、必要なサイバーセキュリティの成果を伝えてもよいです。
•A critical infrastructure sector may establish a baseline that can be used among its constituents as a sector-specific starting point from which to build tailored Target Profiles.
•重要インフラのセクターは、構成員の間で使用でき、各組織に合わせた目標プロファイルを構築するためのセクター固有の出発点として機能するベースラインを確立してもよいです。
The Manufacturing Profile provides a voluntary, risk-based approach for managing cybersecurity activities and reducing cyber risk to manufacturing systems.
製造プロファイルは、サイバーセキュリティ活動を管理し、製造システムに対するサイバーリスクを低減するための、任意で、リスクに基づくアプローチを提供します。
1.2 Audience
1.2 対象読者
This document covers details specific to manufacturing systems. Readers of this document should be acquainted with operational technology, general computer security concepts, and communication protocols such as those used in networking. The intended audience is varied and includes the following:
本書は、製造システムに固有の詳細を扱います。本書の読者は、運用技術、一般的なコンピュータセキュリティの概念、およびネットワークで使用されるような通信プロトコルに精通しているべきです。想定する対象読者は多岐にわたり、次の人々が含まれます。
•Control engineers, integrators, and architects who design or implement secure manufacturing systems.
•安全な製造システムを設計または実装する制御エンジニア、インテグレーター、アーキテクト。
•System administrators, engineers, and other information technology (IT) professionals who administer, patch, or secure manufacturing systems.
•製造システムの管理、パッチ適用、またはセキュリティ確保を行うシステム管理者、エンジニア、その他の情報技術(IT)専門家。
•Managers who are responsible for manufacturing systems.
•製造システムに責任を負う管理者。
•Senior management who are trying to understand implications and consequences as they justify and implement a manufacturing systems cybersecurity program to help mitigate impacts to business functionality.
•事業機能への影響を軽減するのに役立つ製造システムのサイバーセキュリティプログラムを正当化し、実施するにあたって、その意味や帰結を理解しようとする上級管理者。
•Researchers, academic institutions and analysts who are trying to understand the unique security needs of manufacturing systems.
•製造システム固有のセキュリティニーズを理解しようとする研究者、学術機関、アナリスト。
1.3 Document Structure
1.3 文書の構成
The remainder of this guide is divided into the following major sections:
本指針の以降の部分は、次の主要な節に分かれています。
•Section 2 provides an overview of manufacturing systems.
•第2節では、製造システムの概要を示します。
•Section 3 provides an overview of the Framework for Improving Critical Infrastructure Cybersecurity (Cybersecurity Framework).
•第3節では、Framework for Improving Critical Infrastructure Cybersecurity(サイバーセキュリティフレームワーク)の概要を示します。
•Section 4 discusses the manufacturing profile development approach.
•第4節では、製造プロファイルの策定アプローチを論じます。
•Section 5 provides rationale for integrating cybersecurity into manufacturing Business/mission objectives.
•第5節では、サイバーセキュリティを製造の事業・ミッション目標に組み込む根拠を示します。
•Section 6 discusses cyber risk management and the risk categorization of the manufacturing system.
•第6節では、サイバーリスク管理と、製造システムのリスクの分類を論じます。
•Section 7 provides the manufacturing implementation of the CSF subcategories.
•第7節では、CSFのサブカテゴリを製造において実装する内容を示します。
•References provides a list of references used in the development of this document.
•参考文献では、本書の作成に使用した参考文献の一覧を示します。
•Appendix A provides a list of acronyms and abbreviations used in this document.
•付録Aでは、本書で使用する略語の一覧を示します。
•Appendix B provides a glossary of terms used in this document.
•付録Bでは、本書で使用する用語の用語集を示します。
2. Overview of Manufacturing Systems
2. 製造システムの概要
Industrial Control Systems (ICS), which include manufacturing systems, represent different types of control systems including supervisory control and data acquisitions (SCADA) systems, distributed control systems (DCS), and other control system configurations such as Programmable Logic Controllers (PLCs) often found in the industrial sectors and critical infrastructures. An ICS consists of combinations of control components (e.g., electrical, mechanical, hydraulic, and pneumatic) that act together to achieve an industrial objective (e.g., manufacturing, transportation of matter or energy). ICS support the large and diverse manufacturing industrial sector and can be categorized as either process-based, discrete-based, or a combination of both [3].
製造システムを含む産業用制御システム(ICS)は、産業セクターや重要インフラでよく見られる監視制御・データ収集(SCADA)システム、分散制御システム(DCS)、プログラマブルロジックコントローラー(PLC)などの制御システム構成を含む、さまざまな種類の制御システムから成ります。ICSは、産業上の目的(たとえば、製造、物質やエネルギーの輸送)を達成するために連携して動作する制御構成要素(たとえば、電気的、機械的、油圧式、空気圧式)の組み合わせで構成されます。ICSは、大規模で多様な製造業の産業セクターを支えており、プロセスベース、離散ベース、またはその両方の組み合わせのいずれかに分類できます [3]。
Process-based manufacturing industries typically utilize two main process types:
プロセスベースの製造業では、通常、次の2つの主要なプロセスの種類が利用されます。
•Continuous Manufacturing Processes. These processes run continuously, often with phases to make different grades of a product. Typical continuous manufacturing processes include fuel or steam flow in a power plant, petroleum in a refinery, and distillation in a chemical plant.
•連続製造プロセス。これらのプロセスは連続的に稼働し、製品のさまざまなグレードを作るために段階が設けられることがよくあります。典型的な連続製造プロセスには、発電所における燃料や蒸気の流れ、製油所における石油、化学プラントにおける蒸留が含まれます。
•Batch Manufacturing Processes. These processes have distinct processing steps, conducted on a quantity of material. There is a distinct start and end to a batch process with the possibility of brief steady state operations during intermediate steps. Typical batch manufacturing processes include food, beverage, and biotech manufacturing.
•バッチ製造プロセス。これらのプロセスは、一定量の材料に対して実施される、明確に区分された処理工程を持ちます。バッチプロセスには明確な開始と終了があり、中間の工程では短時間の定常運転が行われる可能性があります。典型的なバッチ製造プロセスには、食品、飲料、バイオテクノロジーの製造が含まれます。
Discrete-based manufacturing industries typically conduct a series of operations on a product to create the distinct end product. Electronic and mechanical parts assembly and parts machining are typical examples of this type of industry. Both process-based and discrete-based industries utilize similar types of control systems, sensors, and networks. Some facilities are a hybrid of discrete and process-based manufacturing.
離散ベースの製造業では、通常、製品に対して一連の作業を行い、個別の最終製品を作ります。電子部品や機械部品の組み立て、部品の機械加工は、この種の産業の典型的な例です。プロセスベースの産業と離散ベースの産業は、どちらも類似の種類の制御システム、センサー、ネットワークを利用します。施設によっては、離散製造とプロセスベース製造のハイブリッドになっているものもあります。
Additionally, to support both process-based and discrete-based manufacturing processes, manufacturers must also manage the supply chain for both technology-based inputs used in their final products (e.g. programmable logic controllers, sensors, robotics, data collection systems, and other information technologies), technology-based products used by the organization, and non-technology input products (e.g., non-IT components manufactured by third-party suppliers that are utilized to manufacture the final product).
さらに、プロセスベースと離散ベースの両方の製造プロセスを支えるため、製造者は、最終製品に使用される技術ベースの投入物(たとえば、プログラマブルロジックコントローラー、センサー、ロボット、データ収集システム、その他の情報技術)、組織が使用する技術ベースの製品、および技術以外の投入物(たとえば、最終製品の製造に使用される、第三者のサプライヤーが製造する非ITの構成要素)のサプライチェーンも管理しなければなりません。
Manufacturing industries are usually located within a confined factory or plant-centric area. Communications in manufacturing industries are typically performed using fieldbus and local area network (LAN) technologies that are reliable and high speed. Wireless networking technologies are gaining popularity in manufacturing industries. Fieldbus includes, for example, DeviceNet, Modbus, and Controller Area Network (CAN) bus.
製造業は、通常、工場やプラントを中心とした限られた区域に所在します。製造業における通信は、通常、信頼性が高く高速なフィールドバスやローカルエリアネットワーク(LAN)の技術を用いて行われます。無線ネットワーク技術も製造業で普及しつつあります。フィールドバスには、たとえば DeviceNet、Modbus、Controller Area Network(CAN)バスが含まれます。
The Manufacturing sector of the critical infrastructure community includes public and private owners and operators, along with other entities operating in the manufacturing domain. Members of the distinct critical infrastructure sector perform functions that are supported by ICS and by information technology (IT). This reliance on technology, communication, and the interconnectivity of ICS and IT has changed and expanded the potential vulnerabilities and increased potential risk to manufacturing system operations.
重要インフラコミュニティの製造セクターには、公的および民間の所有者と運用者のほか、製造分野で事業を行うその他の事業体が含まれます。個別の重要インフラセクターの構成員は、ICSおよび情報技術(IT)に支えられた機能を果たしています。このような技術や通信への依存、およびICSとITの相互接続により、潜在的な脆弱性が変化・拡大し、製造システムの運用に対する潜在的なリスクが高まっています。
3. Overview of the Cybersecurity Framework
3. サイバーセキュリティフレームワークの概要
The Profile defines specific practices to address the Framework Core. It is the next layer of detail for implementing cybersecurity best practices for each category expressed in the Framework.
プロファイルは、フレームワークコアに対応するための具体的な慣行を定義します。これは、フレームワークで示された各カテゴリについて、サイバーセキュリティのベストプラクティスを実装するための、次の詳細な層です。
3.1 Framework Core
3.1 フレームワークコア
The Framework Core is a set of cybersecurity activities and desired outcomes determined to be essential across critical infrastructure sectors [2]. The Core presents industry standards, guidelines, and practices in a manner that allows for communication of cybersecurity activities and outcomes across the organization from the executive level to the implementation/operations level. The Framework Core consists of five concurrent and continuous Functions—Identify, Protect, Detect, Respond, Recover. When considered together, these Functions provide a high-level, strategic view of the organization’s management of cybersecurity risk. The Framework Core then identifies underlying key Categories and Subcategories for each Function and matches them with example Informative References such as existing standards, guidelines, and practices for each Subcategory [2].
フレームワークコアは、重要インフラのセクター全体にわたって不可欠であると判断されたサイバーセキュリティ活動と望ましい成果の集合です [2]。コアは、業界標準、指針、慣行を、経営層から実装・運用層までの組織全体でサイバーセキュリティ活動と成果を伝達できる形で示します。フレームワークコアは、識別(Identify)、防御(Protect)、検知(Detect)、対応(Respond)、復旧(Recover)という、同時並行で継続的な5つの機能で構成されます。これらの機能をあわせて考えると、組織のサイバーセキュリティリスク管理に関する、高水準で戦略的な見方が得られます。そのうえで、フレームワークコアは、各機能の基盤となる主要なカテゴリとサブカテゴリを特定し、各サブカテゴリについて、既存の標準、指針、慣行などの参考情報の例と対応付けます [2]。
The five Framework Functions can be performed concurrently and continuously to form an operational culture that addresses the dynamic cybersecurity risk.
フレームワークの5つの機能は、同時並行かつ継続的に実行することで、動的なサイバーセキュリティリスクに対処する運用文化を形成できます。
Table 1 Cybersecurity Framework Functions and Categories
表1 サイバーセキュリティフレームワークの機能とカテゴリ
| Function Unique Identifier | Function | Category Unique Identifier | Category |
|---|---|---|---|
| ID | Identify | ID.AM | Asset Management |
| ID.BE | Business Environment | ||
| ID.GV | Governance | ||
| ID.RA | Risk Assessment | ||
| ID.RM | Risk Management Strategy | ||
| ID.SC | Supply Chain Management | ||
| PR | Protect | PR.AC | Identity Management, Authentication and Access Control |
| PR.AT | Awareness and Training | ||
| PR.DS | Data Security | ||
| PR.IP | Information Protection Processes and Procedures | ||
| PR.MA | Maintenance | ||
| PR.PT | Protective Technology | ||
| DE | Detect | DE.AE | Anomalies and Events |
| DE.CM | Security Continuous Monitoring | ||
| DE.DP | Detection Processes | ||
| RS | Respond | RS.RP | Response Planning |
| RS.CO | Communications | ||
| RS.AN | Analysis | ||
| RS.MI | Mitigation | ||
| RS.IM | Improvements | ||
| RC | Recover | RC.RP | Recovery Planning |
| RC.IM | Improvements | ||
| RC.CO | Communications |
| 機能の一意識別子 | 機能 | カテゴリの一意識別子 | カテゴリ |
|---|---|---|---|
| ID | 識別(Identify) | ID.AM | 資産管理 |
| ID.BE | ビジネス環境 | ||
| ID.GV | ガバナンス | ||
| ID.RA | リスクアセスメント | ||
| ID.RM | リスク管理戦略 | ||
| ID.SC | サプライチェーン管理 | ||
| PR | 防御(Protect) | PR.AC | アイデンティティ管理、認証、アクセス制御 |
| PR.AT | 意識向上およびトレーニング | ||
| PR.DS | データセキュリティ | ||
| PR.IP | 情報保護のプロセスと手順 | ||
| PR.MA | 保守 | ||
| PR.PT | 保護技術 | ||
| DE | 検知(Detect) | DE.AE | 異常とイベント |
| DE.CM | セキュリティの継続的監視 | ||
| DE.DP | 検知プロセス | ||
| RS | 対応(Respond) | RS.RP | 対応計画 |
| RS.CO | コミュニケーション | ||
| RS.AN | 分析 | ||
| RS.MI | 緩和 | ||
| RS.IM | 改善 | ||
| RC | 復旧(Recover) | RC.RP | 復旧計画 |
| RC.IM | 改善 | ||
| RC.CO | コミュニケーション |
The five “functions” of the Framework Core are:
フレームワークコアの5つの「機能」は次のとおりです。
Identify – Develop the organizational understanding to manage cybersecurity risk to systems, assets, data, and capabilities. The activities in the Identify Function are foundational for effective use of the Framework. Understanding the business context, the resources that support critical functions and the related cybersecurity risks enables an organization to focus and prioritize its efforts, consistent with its risk management strategy and business needs. Examples of outcome Categories within this Function include: Asset Management; Business Environment; Governance; Risk Assessment; and Risk Management Strategy.
識別(Identify)– システム、資産、データ、能力に対するサイバーセキュリティリスクを管理するための組織的な理解を深めます。識別機能の活動は、フレームワークを効果的に利用するための基礎となります。事業の状況、重要な機能を支えるリソース、および関連するサイバーセキュリティリスクを理解することで、組織は、リスク管理戦略と事業上のニーズに沿って、取り組みを絞り込み、優先順位を付けることができます。この機能に含まれる成果カテゴリの例は、資産管理、ビジネス環境、ガバナンス、リスクアセスメント、リスク管理戦略です。
Protect – Develop and implement the appropriate safeguards to ensure delivery of critical infrastructure services. The activities in the Protect Function support the ability to limit or contain the impact of a potential cybersecurity event. Examples of outcome Categories within this Function include: Access Control; Awareness and Training; Data Security; Information Protection Processes and Procedures; Maintenance; and Protective Technology.
防御(Protect)– 重要インフラのサービス提供を確実にするための適切な保護対策を策定し、実装します。防御機能の活動は、潜在的なサイバーセキュリティイベントの影響を制限または封じ込める能力を支えます。この機能に含まれる成果カテゴリの例は、アクセス制御、意識向上およびトレーニング、データセキュリティ、情報保護のプロセスと手順、保守、保護技術です。
Detect – Develop and implement the appropriate activities to identify the occurrence of a cybersecurity event. The activities in the Detect Function enable timely discovery of cybersecurity events. Examples of outcome Categories within this Function include: Anomalies and Events; Security Continuous Monitoring; and Detection Processes.
検知(Detect)– サイバーセキュリティイベントの発生を特定するための適切な活動を策定し、実装します。検知機能の活動により、サイバーセキュリティイベントをタイムリーに発見できるようになります。この機能に含まれる成果カテゴリの例は、異常とイベント、セキュリティの継続的監視、検知プロセスです。
Respond – Develop and implement the appropriate activities to take action regarding a detected cybersecurity event. The activities in the Respond Function support the ability to contain the impact of a potential cybersecurity event. Examples of outcome Categories within this Function include: Response Planning; Communications; Analysis; Mitigation; and Improvements.
対応(Respond)– 検知されたサイバーセキュリティイベントに対して措置を講じるための適切な活動を策定し、実装します。対応機能の活動は、潜在的なサイバーセキュリティイベントの影響を封じ込める能力を支えます。この機能に含まれる成果カテゴリの例は、対応計画、コミュニケーション、分析、緩和、改善です。
Recover – Develop and implement the appropriate activities to maintain plans for resilience and to restore any capabilities or services that were impaired due to a cybersecurity event. The activities in the Recover Function support timely recovery to normal operations to reduce the impact from a cybersecurity event. Examples of outcome Categories within this Function include: Recovery Planning; Improvements; and Communications.
復旧(Recover)– レジリエンスのための計画を維持し、サイバーセキュリティイベントによって損なわれた能力やサービスを復元するための適切な活動を策定し、実装します。復旧機能の活動は、通常の運用へのタイムリーな復旧を支え、サイバーセキュリティイベントによる影響を軽減します。この機能に含まれる成果カテゴリの例は、復旧計画、改善、コミュニケーションです。
The Manufacturing Profile for the Cybersecurity Framework presents detailed implementation language for the cybersecurity standards expressed in the Framework categories and subcategories. The Profile is intended to support cybersecurity outcomes based on business needs that the manufacturer has selected from the Framework Categories and Subcategories [2]. The Profile can be characterized as the alignment of standards, guidelines, and practices to the Framework Core in a practical implementation scenario.
サイバーセキュリティフレームワークの製造プロファイルは、フレームワークのカテゴリとサブカテゴリで表現されたサイバーセキュリティ標準について、詳細な実装の記述を示します。プロファイルは、製造者がフレームワークのカテゴリとサブカテゴリから選択した事業上のニーズに基づくサイバーセキュリティの成果を支えることを意図しています [2]。プロファイルは、実践的な実装シナリオにおいて、標準、指針、慣行をフレームワークコアに整合させたものと特徴づけられます。
4. Manufacturing Profile Development Approach
4. 製造プロファイルの策定アプローチ
The Profile was developed to be an actionable approach for implementing the CSF subcategories into a manufacturing system and its environment. The specific statements in the subcategories in Section 7 are derived from the security controls from ISA/IEC 62443 [5] and the NIST SP 800-53 Rev. 4 [4] and are customized to the manufacturing domain using relevant informative references. Control Objectives for Information and Related Technologies (COBIT) 5 is sourced for subcategories that have no corresponding 800-53 or ISA/IEC 62443 references. Additional input came from NIST SP 800-82, Rev. 2, both in section 6.2 (Guidance on the Application of Security Controls to ICS) and in Appendix G (ICS Overlay) [3]. For informative references to an entire control family or set of controls (such as subcategory ID.GV-1’s informative reference to all “policy and procedures” controls), the approach took a holistic view of the controls comprising the family/set.
本プロファイルは、CSFのサブカテゴリを製造システムとその環境に実装するための、実行可能なアプローチとして策定されました。第7節のサブカテゴリにある個別の記述は、ISA/IEC 62443 [5] およびNIST SP 800-53 Rev. 4 [4] のセキュリティ管理策から導かれたもので、関連する参考情報を用いて製造分野に合わせて調整されています。800-53にもISA/IEC 62443にも対応する参照がないサブカテゴリについては、Control Objectives for Information and Related Technologies(COBIT)5を出典としています。さらに、NIST SP 800-82 Rev. 2 の第6.2節(Guidance on the Application of Security Controls to ICS)と付録G(ICS Overlay)からも情報を得ています [3]。管理策のファミリー全体または管理策の集合に対する参考情報(たとえば、サブカテゴリID.GV-1が、すべての「ポリシーおよび手順」の管理策を参照している場合)については、そのファミリーまたは集合を構成する管理策を包括的に捉えるアプローチを採用しました。
Section 7 provides the customized CSF subcategory language developed using informative references relevant to the manufacturing domain. In the Reference column in Section 7, hyperlinks are provided to the specific and relevant source influences for the subcategory statements.
第7節では、製造分野に関連する参考情報を用いて作成した、調整済みのCSFサブカテゴリの記述を示します。第7節の「参照」列には、サブカテゴリの記述に影響を与えた、具体的で関連性のある情報源へのハイパーリンクを示しています。
The Profile expresses tailored values for cybersecurity controls for the manufacturing system environment. These represent the application of the Categories and Subcategories from the Framework based on domain-specific relevance, business drivers, risk assessment, and the manufacturer’s priorities. Users of the Profile can also add Categories and Subcategories as needed to address unique and specific risks.
プロファイルは、製造システム環境に合わせて調整した、サイバーセキュリティ管理策の値を表します。これらは、分野固有の関連性、事業上の推進要因、リスクアセスメント、および製造者の優先事項に基づいて、フレームワークのカテゴリとサブカテゴリを適用したものです。プロファイルの利用者は、固有かつ具体的なリスクに対処するために、必要に応じてカテゴリとサブカテゴリを追加することもできます。
5. Manufacturing Business/Mission Objectives
5. 製造における事業・ミッション目標
The development of the Profile included the identification of common business/mission objectives to the manufacturing sector. These business/mission objectives provide the necessary context for identifying and managing applicable cybersecurity risk mitigation pursuits [2]. Five common business/mission objectives for the manufacturing sector were initially identified: Maintain Human Safety, Maintain Environmental Safety, Maintain Quality of Product, Maintain Production Goals, and Maintain Trade Secrets. Other business/mission objectives were identified for the manufacturing sector but not included in this initial profile. Key cybersecurity practices are identified for supporting each business/mission objective, allowing users to better prioritize actions and resources according to the user’s defined needs.
プロファイルの策定では、製造セクターに共通する事業・ミッション目標の特定を行いました。これらの事業・ミッション目標は、該当するサイバーセキュリティリスク低減の取り組みを特定し、管理するために必要な状況を提供します [2]。製造セクターに共通する5つの事業・ミッション目標として、当初、人間の安全の維持、環境の安全の維持、製品品質の維持、生産目標の維持、営業秘密の維持が特定されました。そのほかの事業・ミッション目標も製造セクターについて特定されましたが、この初版のプロファイルには含めていません。各事業・ミッション目標を支えるための主要なサイバーセキュリティ慣行が特定されており、利用者は、自らが定めたニーズに応じて、措置とリソースの優先順位をより適切に付けることができます。
These Business/Mission Objectives Are Not Listed in Prioritized Order.
これらの事業・ミッション目標は、優先順位の順に並べられているわけではありません。
Maintain Environmental Safety
環境の安全の維持
Manage cybersecurity risks that could adversely affect the environment, including both accidental and deliberate damage. Cybersecurity risk on the manufacturing system could potentially adversely affect environmental safety. Personnel should understand cybersecurity and environmental safety interdependencies.
偶発的な損害と意図的な損害の両方を含め、環境に悪影響を及ぼす可能性のあるサイバーセキュリティリスクを管理します。製造システムに対するサイバーセキュリティリスクは、環境の安全に悪影響を及ぼす可能性があります。要員は、サイバーセキュリティと環境の安全の相互依存関係を理解しておくべきです。
Maintain Human Safety
人間の安全の維持
Manage cybersecurity risks that could potentially impact human safety. Cybersecurity risk on the manufacturing system could potentially adversely affect human safety. Personnel should understand cybersecurity and safety interdependencies.
人間の安全に影響を及ぼす可能性のあるサイバーセキュリティリスクを管理します。製造システムに対するサイバーセキュリティリスクは、人間の安全に悪影響を及ぼす可能性があります。要員は、サイバーセキュリティと安全の相互依存関係を理解しておくべきです。
Maintain Production Goals
生産目標の維持
Manage cybersecurity risks that could adversely affect production goals. Cybersecurity risk on the manufacturing system, including asset damage, could potentially adversely affect production goals. Personnel should understand cybersecurity and production goal interdependencies
生産目標に悪影響を及ぼす可能性のあるサイバーセキュリティリスクを管理します。資産の損傷を含め、製造システムに対するサイバーセキュリティリスクは、生産目標に悪影響を及ぼす可能性があります。要員は、サイバーセキュリティと生産目標の相互依存関係を理解しておくべきです。
Maintain Quality of Product
製品品質の維持
Manage cybersecurity risks that could adversely affect the quality of product. Protect against compromise of integrity of the manufacturing process and associated data.
製品の品質に悪影響を及ぼす可能性のあるサイバーセキュリティリスクを管理します。製造プロセスおよび関連データの完全性が損なわれないよう保護します。
Maintain Sensitive Information
機微情報の維持
Manage cybersecurity risks that could lead to the loss or compromise of the organization’s intellectual property and sensitive business data including personally identifiable information (PII).
個人を特定できる情報(PII)を含む、組織の知的財産や機微な事業データの損失または危殆化につながる可能性のあるサイバーセキュリティリスクを管理します。
5.1 Alignment of Subcategories to Meet Mission Objectives
5.1 ミッション目標を達成するためのサブカテゴリの整合
To align cybersecurity goals with overall mission success, the Profile subcategories are prioritized in order to support specific business/mission objectives. This allows the manufacturer to focus on implementing those cybersecurity measures against threats that could directly and severely compromise their ability to perform their essential mission.
サイバーセキュリティの目標を組織全体のミッションの成功に整合させるため、プロファイルのサブカテゴリは、特定の事業・ミッション目標を支えるように優先順位付けされています。これにより、製造者は、不可欠なミッションを遂行する能力を直接かつ深刻に損なう可能性のある脅威に対するサイバーセキュリティ対策の実装に、重点を置くことができます。
For each business/mission objective, the most critical Subcategories initially determined to support the objective are highlighted in the tables under each Function. The selection of Subcategories to business/mission objectives was based on a broad range of manufacturing sectors and operations. The most critical Subcategories may differ for individual manufacturers.
各事業・ミッション目標について、当初、その目標を支えるうえで最も重要と判断されたサブカテゴリは、各機能の下の表で強調されています。事業・ミッション目標に対するサブカテゴリの選定は、幅広い製造セクターと運用に基づいて行われました。最も重要なサブカテゴリは、製造者ごとに異なる場合があります。
Identify - The Identify Function is critical in the development of the foundation for cybersecurity management, and in the understanding of cyber risk to systems, assets, data, and capabilities.
識別(Identify)- 識別機能は、サイバーセキュリティ管理の基盤を構築し、システム、資産、データ、能力に対するサイバーリスクを理解するうえで重要です。
Table 2 IDENTIFY Business Mission Objectives
表2 識別(IDENTIFY)の事業・ミッション目標
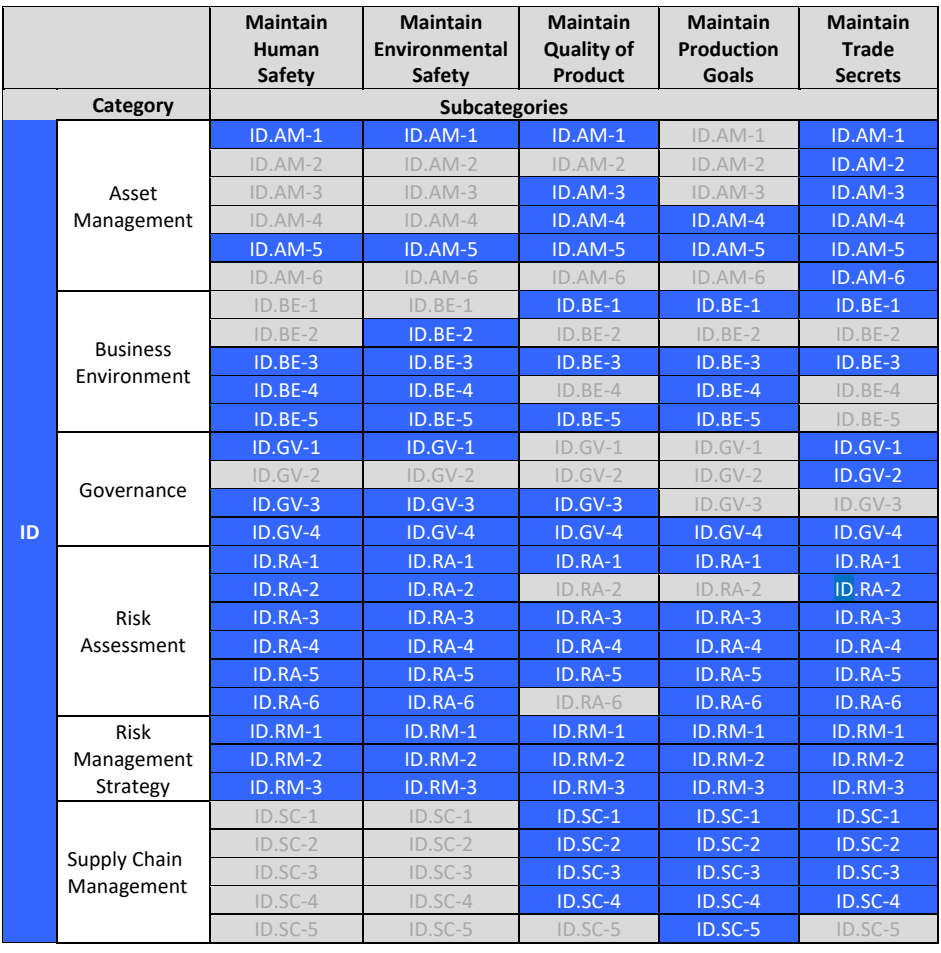
色分けされた対応表です。見出しの行は5つの事業・ミッション目的の列「Maintain Human Safety」「Maintain Environmental Safety」「Maintain Quality of Product」「Maintain Production Goals」「Maintain Trade Secrets」(人の安全の維持、環境安全の維持、製品品質の維持、生産目標の維持、営業秘密の維持)で、2行目の見出しは「Category」(カテゴリ)と「Subcategories」(サブカテゴリ)です。左端の列は機能「ID」(青)で、カテゴリは Asset Management(ID.AM-1 to ID.AM-6)、Business Environment(ID.BE-1 to ID.BE-5)、Governance(ID.GV-1 to ID.GV-4)、Risk Assessment(ID.RA-1 to ID.RA-6)、Risk Management Strategy(ID.RM-1 to ID.RM-3)、Supply Chain Management(ID.SC-1 to ID.SC-5) です。各目的の列にすべてのサブカテゴリが並び、青で塗られたセルはその目的に最も重要として強調されたサブカテゴリ、灰色の地に灰色の文字のセルは強調されていないものを示します。強調されているのは次のとおりです。Maintain Human Safety:ID.AM-1, ID.AM-5, ID.BE-3, ID.BE-4, ID.BE-5, ID.GV-1, ID.GV-3, ID.GV-4, ID.RA-1, ID.RA-2, ID.RA-3, ID.RA-4, ID.RA-5, ID.RA-6, ID.RM-1, ID.RM-2, ID.RM-3。Maintain Environmental Safety:ID.AM-1, ID.AM-5, ID.BE-2, ID.BE-3, ID.BE-4, ID.BE-5, ID.GV-1, ID.GV-3, ID.GV-4, ID.RA-1, ID.RA-2, ID.RA-3, ID.RA-4, ID.RA-5, ID.RA-6, ID.RM-1, ID.RM-2, ID.RM-3。Maintain Quality of Product:ID.AM-1, ID.AM-3, ID.AM-4, ID.AM-5, ID.BE-1, ID.BE-3, ID.BE-5, ID.GV-3, ID.GV-4, ID.RA-1, ID.RA-3, ID.RA-4, ID.RA-5, ID.RM-1, ID.RM-2, ID.RM-3, ID.SC-1, ID.SC-2, ID.SC-3, ID.SC-4。Maintain Production Goals:ID.AM-4, ID.AM-5, ID.BE-1, ID.BE-3, ID.BE-4, ID.BE-5, ID.GV-4, ID.RA-1, ID.RA-3, ID.RA-4, ID.RA-5, ID.RA-6, ID.RM-1, ID.RM-2, ID.RM-3, ID.SC-1, ID.SC-2, ID.SC-3, ID.SC-4, ID.SC-5。Maintain Trade Secrets:ID.AM-1, ID.AM-2, ID.AM-3, ID.AM-4, ID.AM-5, ID.AM-6, ID.BE-1, ID.BE-3, ID.GV-1, ID.GV-2, ID.GV-4, ID.RA-1, ID.RA-2, ID.RA-3, ID.RA-4, ID.RA-5, ID.RA-6, ID.RM-1, ID.RM-2, ID.RM-3, ID.SC-1, ID.SC-2, ID.SC-3, ID.SC-4。
Protect – The Protect Function is critical to limit the impact of a potential cybersecurity event.
防御(Protect)– 防御機能は、潜在的なサイバーセキュリティイベントの影響を制限するうえで重要です。
Table 3 PROTECT Business Mission Objectives
表3 防御(PROTECT)の事業・ミッション目標
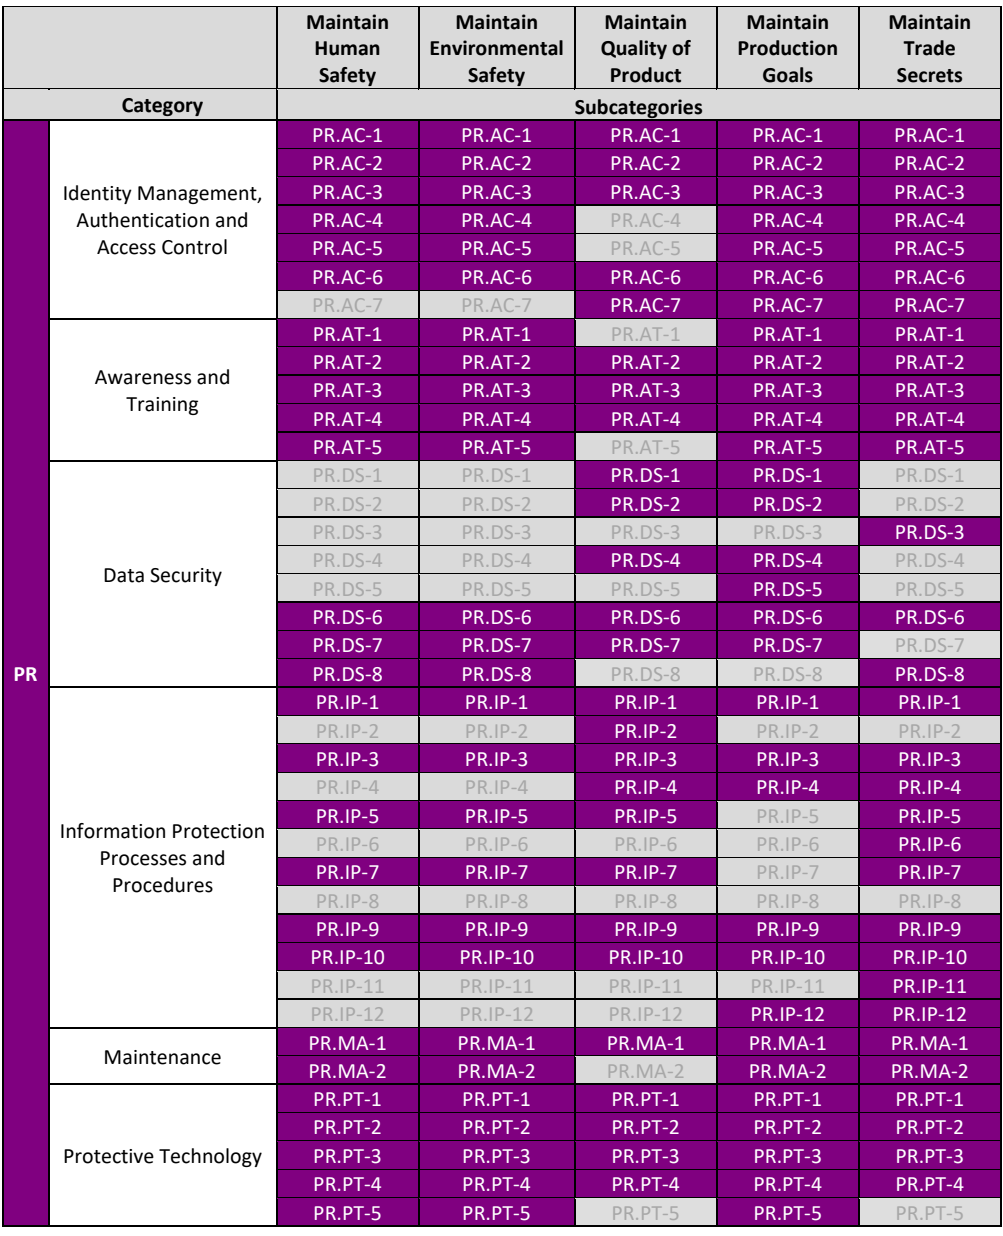
色分けされた対応表です。見出しの行は5つの事業・ミッション目的の列「Maintain Human Safety」「Maintain Environmental Safety」「Maintain Quality of Product」「Maintain Production Goals」「Maintain Trade Secrets」(人の安全の維持、環境安全の維持、製品品質の維持、生産目標の維持、営業秘密の維持)で、2行目の見出しは「Category」(カテゴリ)と「Subcategories」(サブカテゴリ)です。左端の列は機能「PR」(紫)で、カテゴリは Identity Management, Authentication and Access Control(PR.AC-1 to PR.AC-7)、Awareness and Training(PR.AT-1 to PR.AT-5)、Data Security(PR.DS-1 to PR.DS-8)、Information Protection Processes and Procedures(PR.IP-1 to PR.IP-12)、Maintenance(PR.MA-1 to PR.MA-2)、Protective Technology(PR.PT-1 to PR.PT-5) です。各目的の列にすべてのサブカテゴリが並び、紫で塗られたセルはその目的に最も重要として強調されたサブカテゴリ、灰色の地に灰色の文字のセルは強調されていないものを示します。強調されているのは次のとおりです。Maintain Human Safety:PR.AC-1, PR.AC-2, PR.AC-3, PR.AC-4, PR.AC-5, PR.AC-6, PR.AT-1, PR.AT-2, PR.AT-3, PR.AT-4, PR.AT-5, PR.DS-6, PR.DS-7, PR.DS-8, PR.IP-1, PR.IP-3, PR.IP-5, PR.IP-7, PR.IP-9, PR.IP-10, PR.MA-1, PR.MA-2, PR.PT-1, PR.PT-2, PR.PT-3, PR.PT-4, PR.PT-5。Maintain Environmental Safety:PR.AC-1, PR.AC-2, PR.AC-3, PR.AC-4, PR.AC-5, PR.AC-6, PR.AT-1, PR.AT-2, PR.AT-3, PR.AT-4, PR.AT-5, PR.DS-6, PR.DS-7, PR.DS-8, PR.IP-1, PR.IP-3, PR.IP-5, PR.IP-7, PR.IP-9, PR.IP-10, PR.MA-1, PR.MA-2, PR.PT-1, PR.PT-2, PR.PT-3, PR.PT-4, PR.PT-5。Maintain Quality of Product:PR.AC-1, PR.AC-2, PR.AC-3, PR.AC-6, PR.AC-7, PR.AT-2, PR.AT-3, PR.AT-4, PR.DS-1, PR.DS-2, PR.DS-4, PR.DS-6, PR.DS-7, PR.IP-1, PR.IP-2, PR.IP-3, PR.IP-4, PR.IP-5, PR.IP-7, PR.IP-9, PR.IP-10, PR.MA-1, PR.PT-1, PR.PT-2, PR.PT-3, PR.PT-4。Maintain Production Goals:PR.AC-1, PR.AC-2, PR.AC-3, PR.AC-4, PR.AC-5, PR.AC-6, PR.AC-7, PR.AT-1, PR.AT-2, PR.AT-3, PR.AT-4, PR.AT-5, PR.DS-1, PR.DS-2, PR.DS-4, PR.DS-5, PR.DS-6, PR.DS-7, PR.IP-1, PR.IP-3, PR.IP-4, PR.IP-9, PR.IP-10, PR.IP-12, PR.MA-1, PR.MA-2, PR.PT-1, PR.PT-2, PR.PT-3, PR.PT-4, PR.PT-5。Maintain Trade Secrets:PR.AC-1, PR.AC-2, PR.AC-3, PR.AC-4, PR.AC-5, PR.AC-6, PR.AC-7, PR.AT-1, PR.AT-2, PR.AT-3, PR.AT-4, PR.AT-5, PR.DS-3, PR.DS-6, PR.DS-8, PR.IP-1, PR.IP-3, PR.IP-4, PR.IP-5, PR.IP-6, PR.IP-7, PR.IP-9, PR.IP-10, PR.IP-11, PR.IP-12, PR.MA-1, PR.MA-2, PR.PT-1, PR.PT-2, PR.PT-3, PR.PT-4。
Detect – The Detect Function enables timely discovery of cybersecurity events. Real time awareness and continuous monitoring of the systems is critical to detect cybersecurity events.
検知(Detect)– 検知機能により、サイバーセキュリティイベントをタイムリーに発見できるようになります。システムのリアルタイムの状況把握と継続的監視は、サイバーセキュリティイベントを検知するうえで重要です。
Table 4 DETECT Business Mission Objectives
表4 検知(DETECT)の事業・ミッション目標
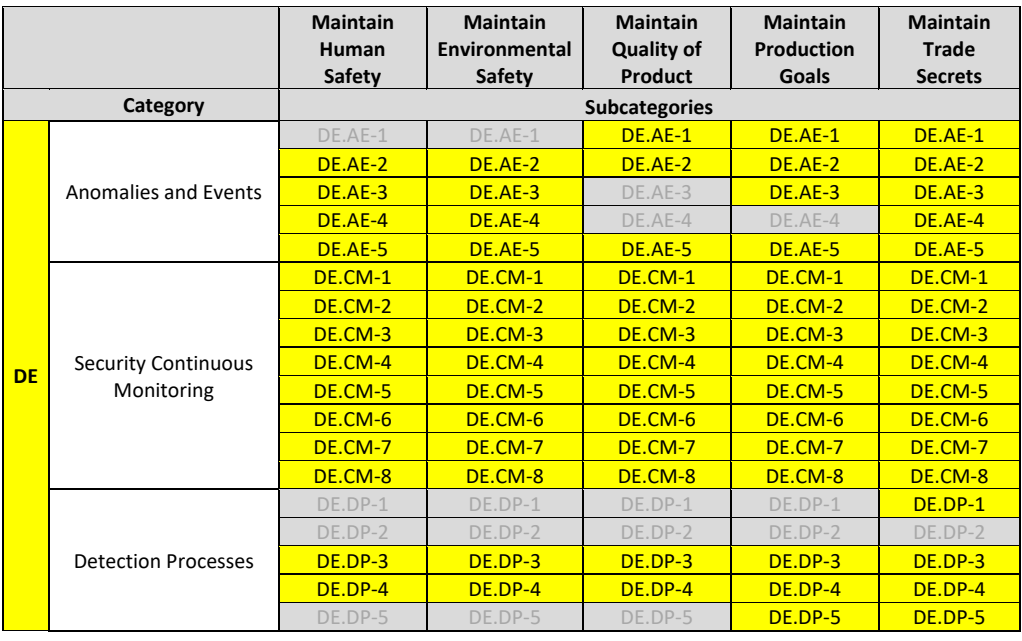
色分けされた対応表です。見出しの行は5つの事業・ミッション目的の列「Maintain Human Safety」「Maintain Environmental Safety」「Maintain Quality of Product」「Maintain Production Goals」「Maintain Trade Secrets」(人の安全の維持、環境安全の維持、製品品質の維持、生産目標の維持、営業秘密の維持)で、2行目の見出しは「Category」(カテゴリ)と「Subcategories」(サブカテゴリ)です。左端の列は機能「DE」(黄)で、カテゴリは Anomalies and Events(DE.AE-1 to DE.AE-5)、Security Continuous Monitoring(DE.CM-1 to DE.CM-8)、Detection Processes(DE.DP-1 to DE.DP-5) です。各目的の列にすべてのサブカテゴリが並び、黄で塗られたセルはその目的に最も重要として強調されたサブカテゴリ、灰色の地に灰色の文字のセルは強調されていないものを示します。強調されているのは次のとおりです。Maintain Human Safety:DE.AE-2, DE.AE-3, DE.AE-4, DE.AE-5, DE.CM-1, DE.CM-2, DE.CM-3, DE.CM-4, DE.CM-5, DE.CM-6, DE.CM-7, DE.CM-8, DE.DP-3, DE.DP-4。Maintain Environmental Safety:DE.AE-2, DE.AE-3, DE.AE-4, DE.AE-5, DE.CM-1, DE.CM-2, DE.CM-3, DE.CM-4, DE.CM-5, DE.CM-6, DE.CM-7, DE.CM-8, DE.DP-3, DE.DP-4。Maintain Quality of Product:DE.AE-1, DE.AE-2, DE.AE-5, DE.CM-1, DE.CM-2, DE.CM-3, DE.CM-4, DE.CM-5, DE.CM-6, DE.CM-7, DE.CM-8, DE.DP-3, DE.DP-4。Maintain Production Goals:DE.AE-1, DE.AE-2, DE.AE-3, DE.AE-5, DE.CM-1, DE.CM-2, DE.CM-3, DE.CM-4, DE.CM-5, DE.CM-6, DE.CM-7, DE.CM-8, DE.DP-3, DE.DP-4, DE.DP-5。Maintain Trade Secrets:DE.AE-1, DE.AE-2, DE.AE-3, DE.AE-4, DE.AE-5, DE.CM-1, DE.CM-2, DE.CM-3, DE.CM-4, DE.CM-5, DE.CM-6, DE.CM-7, DE.CM-8, DE.DP-1, DE.DP-3, DE.DP-4, DE.DP-5。
Respond – The Respond Function supports the ability to contain the impact of a potential cybersecurity event.
対応(Respond)– 対応機能は、潜在的なサイバーセキュリティイベントの影響を封じ込める能力を支えます。
Table 5 RESPOND Business Mission Objectives
表5 対応(RESPOND)の事業・ミッション目標
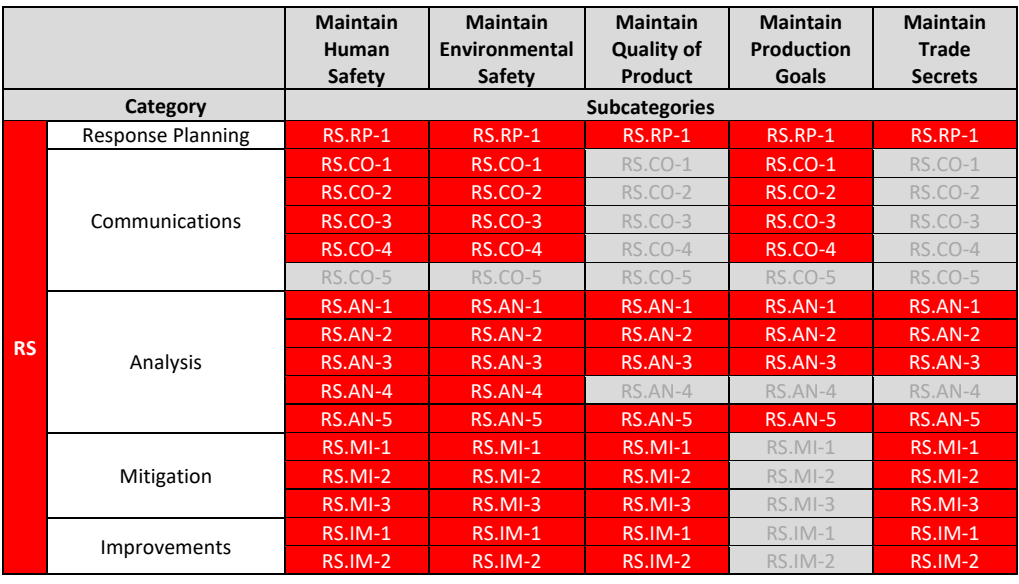
色分けされた対応表です。見出しの行は5つの事業・ミッション目的の列「Maintain Human Safety」「Maintain Environmental Safety」「Maintain Quality of Product」「Maintain Production Goals」「Maintain Trade Secrets」(人の安全の維持、環境安全の維持、製品品質の維持、生産目標の維持、営業秘密の維持)で、2行目の見出しは「Category」(カテゴリ)と「Subcategories」(サブカテゴリ)です。左端の列は機能「RS」(赤)で、カテゴリは Response Planning(RS.RP-1)、Communications(RS.CO-1 to RS.CO-5)、Analysis(RS.AN-1 to RS.AN-5)、Mitigation(RS.MI-1 to RS.MI-3)、Improvements(RS.IM-1 to RS.IM-2) です。各目的の列にすべてのサブカテゴリが並び、赤で塗られたセルはその目的に最も重要として強調されたサブカテゴリ、灰色の地に灰色の文字のセルは強調されていないものを示します。強調されているのは次のとおりです。Maintain Human Safety:RS.RP-1, RS.CO-1, RS.CO-2, RS.CO-3, RS.CO-4, RS.AN-1, RS.AN-2, RS.AN-3, RS.AN-4, RS.AN-5, RS.MI-1, RS.MI-2, RS.MI-3, RS.IM-1, RS.IM-2。Maintain Environmental Safety:RS.RP-1, RS.CO-1, RS.CO-2, RS.CO-3, RS.CO-4, RS.AN-1, RS.AN-2, RS.AN-3, RS.AN-4, RS.AN-5, RS.MI-1, RS.MI-2, RS.MI-3, RS.IM-1, RS.IM-2。Maintain Quality of Product:RS.RP-1, RS.AN-1, RS.AN-2, RS.AN-3, RS.AN-5, RS.MI-1, RS.MI-2, RS.MI-3, RS.IM-1, RS.IM-2。Maintain Production Goals:RS.RP-1, RS.CO-1, RS.CO-2, RS.CO-3, RS.CO-4, RS.AN-1, RS.AN-2, RS.AN-3, RS.AN-5。Maintain Trade Secrets:RS.RP-1, RS.AN-1, RS.AN-2, RS.AN-3, RS.AN-5, RS.MI-1, RS.MI-2, RS.MI-3, RS.IM-1, RS.IM-2。
Recover – The Recover Function supports timely recovery to normal operations to reduce the impact from a cybersecurity event. Defined Recovery objectives are needed when recovering from disruptions.
復旧(Recover)– 復旧機能は、通常の運用へのタイムリーな復旧を支え、サイバーセキュリティイベントによる影響を軽減します。中断から復旧する際には、定義された復旧目標が必要です。
Table 6 RECOVER Business Mission Objectives
表6 復旧(RECOVER)の事業・ミッション目標
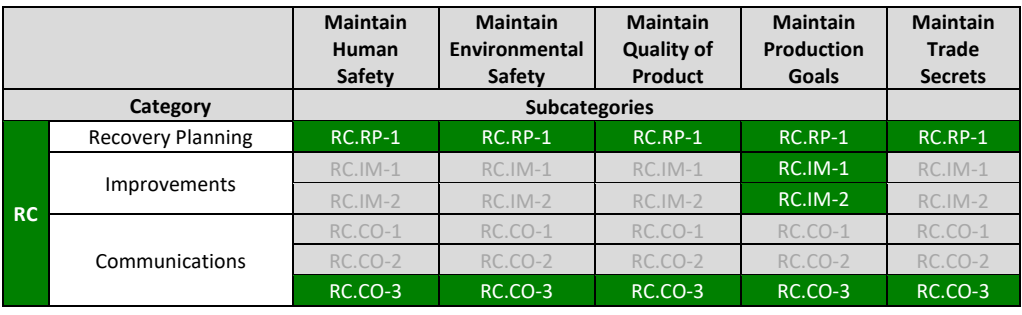
色分けされた対応表です。見出しの行は5つの事業・ミッション目的の列「Maintain Human Safety」「Maintain Environmental Safety」「Maintain Quality of Product」「Maintain Production Goals」「Maintain Trade Secrets」(人の安全の維持、環境安全の維持、製品品質の維持、生産目標の維持、営業秘密の維持)で、2行目の見出しは「Category」(カテゴリ)と「Subcategories」(サブカテゴリ)です。左端の列は機能「RC」(緑)で、カテゴリは Recovery Planning(RC.RP-1)、Improvements(RC.IM-1 to RC.IM-2)、Communications(RC.CO-1 to RC.CO-3) です。各目的の列にすべてのサブカテゴリが並び、緑で塗られたセルはその目的に最も重要として強調されたサブカテゴリ、灰色の地に灰色の文字のセルは強調されていないものを示します。強調されているのは次のとおりです。Maintain Human Safety:RC.RP-1, RC.CO-3。Maintain Environmental Safety:RC.RP-1, RC.CO-3。Maintain Quality of Product:RC.RP-1, RC.CO-3。Maintain Production Goals:RC.RP-1, RC.IM-1, RC.IM-2, RC.CO-3。Maintain Trade Secrets:RC.RP-1, RC.CO-3。
6. Manufacturing System Categorization and Risk Management
6. 製造システムの分類とリスク管理
In addition to the Business/Mission Objectives for aligning a focused set of cybersecurity controls to support critical business goals, the Manufacturing Profile is also structured into three impact levels based on the categorization of the information and processes within the manufacturing system.
重要な事業目標を支えるために焦点を絞った一連のサイバーセキュリティ管理策を整合させるための事業/ミッション目標に加えて、製造プロファイルは、製造システム内の情報とプロセスの分類に基づく3つの影響レベルで構成されています。
6.1 Categorization Process
6.1 分類プロセス
Manufacturing systems support the most critical and, sometimes, most sensitive operations and assets within an organization. The application of cybersecurity controls in these environments demands the greatest level of attention and effort to ensure that appropriate operational security and risk mitigation are achieved. The categorization process is the first step in the NIST Risk Management Framework (RMF) and provides organizations with information to support tailoring cybersecurity control implementation [3]. As defined by NIST Federal Information Processing Standard (FIPS) 199, the categorization process is based on the potential impact (e.g. LOW, MODERATE, or HIGH) if an incident or event jeopardizes the manufacturing system or components, operational assets, individuals, or the organization [8]. The Profile guidance provides LOW, MODERATE, and HIGH impact level configurations that may be utilized to identify the security capability, functionality, and specificity for supporting manufacturing systems based on the categorization of the manufacturing system.
製造システムは、組織内で最も重要で、場合によっては最も機微な運用と資産を支えています。こうした環境にサイバーセキュリティ管理策を適用するには、適切な運用上のセキュリティとリスク低減を確実に達成するために、最大限の注意と労力が求められます。分類プロセスは、NISTリスク管理フレームワーク(RMF)の最初のステップであり、サイバーセキュリティ管理策の実装を調整するのに役立つ情報を組織に提供します [3]。NIST連邦情報処理標準(FIPS)199で定義されているように、分類プロセスは、インシデントまたはイベントが製造システムや構成要素、運用資産、個人、または組織を危うくした場合の潜在的な影響(たとえば、低、中、または高)に基づいて行われます [8]。本プロファイルの指針は、低、中、高の影響レベルの構成を提供し、製造システムの分類に基づいて、製造システムを支えるセキュリティ能力、機能、具体性を特定するために利用できます。
The Profile defines the three impact levels as follows:
本プロファイルでは、3つの影響レベルを次のように定義します。
1.The potential impact is LOW if the loss of integrity, availability, or confidentiality could be expected to have a limited adverse effect on manufacturing operations, manufactured product, assets, brand image, finances, personnel, the general public, or the environment.
1.完全性、可用性、または機密性の喪失が、製造運用、製造された製品、資産、ブランドイメージ、財務、要員、一般市民、または環境に限定的な悪影響を及ぼすと予想される場合、潜在的な影響は低(LOW)です。
2.The potential impact is MODERATE if the loss of integrity, availability, or confidentiality could be expected to have a serious adverse effect on manufacturing operations, manufactured product, assets, brand image, finances, personnel, the general public, or the environment.
2.完全性、可用性、または機密性の喪失が、製造運用、製造された製品、資産、ブランドイメージ、財務、要員、一般市民、または環境に重大な悪影響を及ぼすと予想される場合、潜在的な影響は中(MODERATE)です。
3.The potential impact is HIGH if the loss of integrity, availability, or confidentiality could be expected to have a severe or catastrophic adverse effect on manufacturing operations, manufactured product, assets, brand image, finances, personnel, the general public, or the environment.
3.完全性、可用性、または機密性の喪失が、製造運用、製造された製品、資産、ブランドイメージ、財務、要員、一般市民、または環境に深刻または壊滅的な悪影響を及ぼすと予想される場合、潜在的な影響は高(HIGH)です。
The tables below provide examples of mission-based rationale for selecting the security categorization of the manufacturing system:
次の表は、製造システムのセキュリティ分類を選択するための、ミッションに基づく根拠の例を示します。
Table 7 Manufacturing System Impact Levels [3]
表7 製造システムの影響レベル [3]
| Impact Category | Low Impact | Moderate Impact | High Impact |
|---|---|---|---|
| Injury | Cuts, bruises requiring first aid | Requires hospitalization | Loss of life or limb |
| Financial Loss ($) | Tens of thousands | Hundreds of thousands | Millions |
| Environmental Release | Temporary damage | Lasting damage | Permanent damage, off-site damage |
| Interruption of Production | Temporary reductions without impacting quarterly production | Temporary reductions requiring additional shifts or overtime to meet quarterly production | Significant reduction and impact to meet quarterly production |
| Public Image | Temporary damage | Lasting damage | Permanent damage |
| 影響カテゴリ | 低影響 | 中影響 | 高影響 |
|---|---|---|---|
| 負傷 | 応急処置を必要とする切り傷、打撲 | 入院が必要 | 生命または四肢の喪失 |
| 金銭的損失($) | 数万 | 数十万 | 数百万 |
| 環境への放出 | 一時的な損害 | 長期的な損害 | 恒久的な損害、敷地外への損害 |
| 生産の中断 | 四半期の生産に影響しない一時的な減産 | 四半期の生産量を満たすために追加のシフトや残業を要する一時的な減産 | 四半期の生産量を満たすうえで著しい減産と影響が生じる |
| 社会的イメージ | 一時的な損害 | 長期的な損害 | 恒久的な損害 |
Table 8 Manufacturing System Impact Levels Based on Product Produced and Industry Concerns [3]
表8 製造される製品と業界の懸念に基づく製造システムの影響レベル [3]
| Category | Low Impact | Moderate Impact | High Impact |
|---|---|---|---|
| Product Produced | Non-hazardous materials or products Non-ingested consumer products | Some hazardous products or steps during production High amount of proprietary information | Critical infrastructure Hazardous materials Ingested products |
| Industry Examples | Plastic injection molding Warehousing | Automotive metal stamping Pulp and paper Semiconductors Automotive production | Utilities Petrochemical Food and beverage Pharmaceutical |
| カテゴリ | 低影響 | 中影響 | 高影響 |
|---|---|---|---|
| 製造される製品 | 危険性のない材料または製品 摂取されない消費者向け製品 | 製造中に危険な製品または工程がある 専有情報が多い | 重要インフラ 危険物 摂取される製品 |
| 業界の例 | プラスチック射出成形 倉庫業 | 自動車の金属プレス加工 パルプ・製紙 半導体 自動車生産 | 公益事業 石油化学 食品・飲料 医薬品 |
A limited adverse effect means that, for example, the loss of integrity, availability, or confidentiality might:
限定的な悪影響とは、たとえば、完全性、可用性、または機密性の喪失によって、次のことが起こる可能性があることを意味します。
•cause a degradation in mission capability to an extent and duration that the system can perform its primary functions, but the effectiveness of the functions is noticeably reduced;
•システムが主要な機能を果たせる程度と期間で、ミッション能力が低下しますが、機能の有効性は目に見えて低下します。
•result in minor damage to operational assets that is repairable without further disruption to operations;
•運用上の資産に軽微な損害が生じますが、運用をさらに中断することなく修復できます。
•result in minor financial loss;
•軽微な金銭的損失が生じます。
•result in minor harm to individuals requiring only basic first aid.
•個人に軽微な危害が生じますが、基本的な応急処置のみで足ります。
A serious adverse effect means that, for example, the loss of integrity, availability, or confidentiality might:
重大な悪影響とは、たとえば、完全性、可用性、または機密性の喪失によって、次のことが起こる可能性があることを意味します。
•cause a significant degradation in mission capability to an extent and duration that the system can perform its primary functions, but the effectiveness of the functions is significantly reduced;
•システムが主要な機能を果たせる程度と期間で、ミッション能力が著しく低下しますが、機能の有効性は大幅に低下します。
•result in significant damage to operational assets that is repairable (or replaceable) with limited impact on operational capabilities;
•運用上の資産に重大な損害が生じますが、運用能力への影響を限定して修復(または交換)できます。
•result in significant financial loss;
•重大な金銭的損失が生じます。
•result in significant harm to individuals requiring hospitalization but does not involve loss of life or serious life-threatening injuries.
•個人に入院を要する重大な危害が生じますが、生命の喪失や生命を脅かす重傷は伴いません。
A severe or catastrophic adverse effect means that, for example, the loss of integrity, availability, or confidentiality might:
深刻または壊滅的な悪影響とは、たとえば、完全性、可用性、または機密性の喪失によって、次のことが起こる可能性があることを意味します。
•cause a severe degradation in or loss of mission capability to an extent and duration that the system is not able to perform one or more of its primary functions;
•システムが主要な機能の1つ以上を果たせなくなる程度と期間で、ミッション能力が深刻に低下または喪失します。
•result in major damage to operational assets that requires significant time to repair or replace resulting in extended downtime;
•運用上の資産に、修復または交換に長時間を要し、長期の停止につながる大きな損害が生じます。
•result in major financial loss;
•大きな金銭的損失が生じます。
•result in severe or catastrophic harm to individuals involving loss of life or serious life-threatening injuries.
•個人に、生命の喪失や生命を脅かす重傷を伴う深刻または壊滅的な危害が生じます。
6.2 Profile’s Hierarchical Supporting Structure
6.2 プロファイルの階層的な支援構造
The Profile guidance is scalable and supports intensifying security protections where needed, while maintaining a conventional baseline. Each higher impact level builds from the baseline starting with the Low designation. Unless otherwise noted, the Moderate and High each include or enhance all of the stipulations from the levels below.
プロファイルの指針は拡張可能であり、従来のベースラインを維持しながら、必要な箇所でセキュリティ保護を強化することを支えます。影響レベルが上がるごとに、低という指定のベースラインを土台に積み上げられます。特に断りがない限り、中と高は、それぞれ下位のレベルの規定をすべて含むか、または強化します。
•A Moderate categorization includes all Moderate and Low security implementations
•中の分類には、中と低のすべてのセキュリティ実装が含まれます
•A High categorization includes all High, Moderate, and Low security implementations
•高の分類には、高、中、低のすべてのセキュリティ実装が含まれます
Each impact level is positioned as the platform to support the next higher impact level implementation, or categorization. The impact level implementation starts with Low and increases in rigor through the Moderate and High implementations. The Low impact level represents the starting baseline for all manufacturing systems. The Moderate impact level will implement the Low security guidance as well as the Moderate. The High impact level will implement all of the Low and Moderate guidance as well as the High inputs. Section 7 provides CSF subcategory language for each impact level customized to the manufacturing domain.
各影響レベルは、次に高い影響レベルの実装、すなわち分類を支える土台として位置付けられます。影響レベルの実装は低から始まり、中、高の実装へと厳格さが増していきます。低影響レベルは、すべての製造システムの出発点となるベースラインです。中影響レベルでは、低のセキュリティ指針に加えて、中の指針を実装します。高影響レベルでは、低と中のすべての指針に加えて、高の入力も実装します。第7節では、製造分野に合わせて調整した、各影響レベルのCSFサブカテゴリの記述を示します。
6.3 Risk Management
6.3 リスク管理
The Profile relies on the manufacturer’s risk management processes to inform and prioritize decisions regarding cybersecurity. It supports recurring risk assessments and validation of business drivers to help manufacturers select target states for cybersecurity activities that reflect desired outcomes.
プロファイルは、サイバーセキュリティに関する意思決定に情報を提供し、優先順位を付けるために、製造者のリスク管理プロセスに依拠します。また、定期的なリスクアセスメントと事業上の推進要因の妥当性確認を支援し、製造者が、望ましい成果を反映したサイバーセキュリティ活動の目標状態を選択するのに役立ちます。
To manage cybersecurity risks, a clear understanding of the business drivers and security considerations specific to the Manufacturing system and its environment is required. Each organization’s risk is unique, along with its use of ICS and IT, thus the implementation of the profile will vary.
サイバーセキュリティリスクを管理するには、製造システムとその環境に固有の事業上の推進要因とセキュリティ上の考慮事項を明確に理解する必要があります。各組織のリスクは、ICSやITの使用状況とともに固有のものであるため、プロファイルの実装は組織によって異なります。
The Manufacturing Profile is meant to enhance but not replace current cybersecurity standards and industry guidelines that the manufacturer is currently embracing. Manufacturers can determine activities that are important to critical service delivery and can prioritize investments to maximize the impact of each dollar spent. Ultimately, the Profile is aimed at reducing and better managing cybersecurity risks. The Profile, along with the Cybersecurity Framework, are not one-size-fits-all approaches to managing cybersecurity risk for critical infrastructure. Manufacturers will continue to have unique risks – different threats, different vulnerabilities, different risk tolerances – and how they implement security practices will vary.
製造プロファイルは、製造者が現在採用しているサイバーセキュリティ標準や業界ガイドラインを補強することを意図したものであり、置き換えるものではありません。製造者は、重要なサービスの提供にとって重要な活動を決定し、投資に優先順位を付けて、費やした1ドルごとの効果を最大化することができます。最終的に、プロファイルは、サイバーセキュリティリスクを低減し、より適切に管理することを目的としています。プロファイルは、サイバーセキュリティフレームワークとともに、重要インフラのサイバーセキュリティリスクを管理するための万能のアプローチではありません。製造者は、異なる脅威、異なる脆弱性、異なるリスク許容度といった固有のリスクを今後も抱え続けるため、セキュリティ慣行の実装方法も異なります。
7. Manufacturing Profile Subcategory Guidance
7. 製造プロファイルのサブカテゴリ指針
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| IDENTIFY | Asset Management (ID.AM) | ID.AM-1 | Low Impact Document an inventory of manufacturing system components that reflects the current system. Manufacturing system components include for example PLCs, sensors, actuators, robots, machine tools, firmware, network switches, routers, power supplies, and other networked components or devices. System component inventory is reviewed and updated as defined by the organization. Information deemed necessary for effective accountability of manufacturing system components includes, for example, hardware inventory specifications, component owners, networked components or devices, machine names and network addresses. Inventory specifications include, for example, manufacturer, device type, model, serial number, and physical location. | ISA/IEC 62443-2-1:2009 4.2.3.4 ISA/IEC 62443-3-3:2013 SR 7.8 CM-8 CM-8 (1)(3)(5) CM-8 (2)(4) |
Moderate Impact Identify individuals who are both responsible and accountable for administering manufacturing system components. | ||||
High Impact Identify mechanisms for detecting the presence of unauthorized hardware and firmware components within the manufacturing system. Where safe and feasible, these mechanisms should be automated. | ||||
| ID.AM-2 | Low Impact Document an inventory of manufacturing system software and firmware components that reflects the current system. Manufacturing system software components include for example software license information, software version numbers, Human Machine Interface (HMI) and other ICS component applications, software, operating systems. System software inventory is reviewed and updated as defined by the organization. | ISA/IEC 62443-2-1:2009 4.2.3.4 ISA/IEC 62443-3-3:2013 SR 7.8 CM-8 CM-8 (1)(3)(5) CM-8 (2)(4) | ||
Moderate Impact Identify individuals who are both responsible and accountable for administering manufacturing system software. | ||||
High Impact Identify mechanisms for detecting the presence of unauthorized software within the manufacturing system. Where safe and feasible, these mechanisms should be automated. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 識別(IDENTIFY) | 資産管理(ID.AM) | ID.AM-1 | 低影響 現在のシステムを反映した、製造システムの構成要素の目録を文書化します。 製造システムの構成要素には、たとえば、PLC、センサー、アクチュエーター、ロボット、工作機械、ファームウェア、ネットワークスイッチ、ルーター、電源装置、その他のネットワーク接続された構成要素やデバイスが含まれます。システム構成要素の目録は、組織が定めるところに従って見直し、更新します。 製造システムの構成要素の効果的な説明責任のために必要と判断される情報には、たとえば、ハードウェア目録の仕様、構成要素の所有者、ネットワーク接続された構成要素やデバイス、マシン名、ネットワークアドレスが含まれます。目録の仕様には、たとえば、製造者、デバイスの種類、モデル、シリアル番号、物理的な所在地が含まれます。 | ISA/IEC 62443-2-1:2009 4.2.3.4 ISA/IEC 62443-3-3:2013 SR 7.8 CM-8 CM-8 (1)(3)(5) CM-8 (2)(4) |
中影響 製造システムの構成要素の管理について、責任と説明責任の両方を負う個人を特定します。 | ||||
高影響 製造システム内に許可されていないハードウェアおよびファームウェアの構成要素が存在することを検知する仕組みを特定します。安全かつ実現可能な場合には、これらの仕組みを自動化すべきです。 | ||||
| ID.AM-2 | 低影響 現在のシステムを反映した、製造システムのソフトウェアおよびファームウェアの構成要素の目録を文書化します。 製造システムのソフトウェア構成要素には、たとえば、ソフトウェアのライセンス情報、ソフトウェアのバージョン番号、ヒューマンマシンインターフェース(HMI)およびその他のICS構成要素のアプリケーション、ソフトウェア、オペレーティングシステムが含まれます。システムのソフトウェア目録は、組織が定めるところに従って見直し、更新します。 | ISA/IEC 62443-2-1:2009 4.2.3.4 ISA/IEC 62443-3-3:2013 SR 7.8 CM-8 CM-8 (1)(3)(5) CM-8 (2)(4) | ||
中影響 製造システムのソフトウェアの管理について、責任と説明責任の両方を負う個人を特定します。 | ||||
高影響 製造システム内に許可されていないソフトウェアが存在することを検知する仕組みを特定します。安全かつ実現可能な場合には、これらの仕組みを自動化すべきです。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| IDENTIFY | Asset Management (ID.AM) | ID.AM-3 | Low Impact Document all connections within the manufacturing system, and between the manufacturing system and other systems. All connections are documented, authorized, and reviewed. Connection information includes, for example, the interface characteristics, data characteristics, ports, protocols, addresses, description of the data, security requirements, and the nature of the connection. | ISA/IEC 62443-2-1:2009 4.2.3.4 CA-3 AC-4 |
Moderate and High Impact Map the flow of information within the manufacturing system and to external systems. | ||||
| ID.AM-4 | Low Impact Identify and document all external connections for the manufacturing system. Examples of external systems include engineering design services, and those that are controlled under separate authority, personal devices, and other hosted services. | AC-20 SA-9(2) | ||
Moderate and High Impact Require external providers to identify the functions, ports, protocols, and other services required for use with the manufacturing system. | ||||
| ID.AM-5 | Low, Moderate and High Impact Identify and prioritize manufacturing system components and functions based on their classification, criticality, and business value. Identify the types of information in possession, custody, or control for which security safeguards are needed (e.g. sensitive or protected information). | ISA/IEC 62443-2-1:2009 4.2.3.6 CP-2 | ||
| ID.AM-6 | Low, Moderate and High Impact Establish and maintain personnel cybersecurity roles and responsibilities for the manufacturing system. Include cybersecurity roles and responsibilities for third-party providers. Require third-party providers to notify the organization of any personnel transition (including transfers or terminations) involving personnel with physical or logical access to the manufacturing system components. Third-party providers include, for example, service providers, contractors, and other organizations providing manufacturing system development, technology services, outsourced applications, or network and security management. | ISA/IEC 62443-2-1:2009 4.3.2.3.3 CP-2 PS-7 |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 識別(IDENTIFY) | 資産管理(ID.AM) | ID.AM-3 | 低影響 製造システム内のすべての接続、および製造システムとその他のシステムとの間のすべての接続を文書化します。すべての接続は、文書化され、許可され、見直されます。 接続情報には、たとえば、インターフェースの特性、データの特性、ポート、プロトコル、アドレス、データの説明、セキュリティ要件、接続の性質が含まれます。 | ISA/IEC 62443-2-1:2009 4.2.3.4 CA-3 AC-4 |
中および高影響 製造システム内、および外部システムとの間の情報の流れをマッピングします。 | ||||
| ID.AM-4 | 低影響 製造システムのすべての外部接続を特定し、文書化します。 外部システムの例には、エンジニアリング設計サービス、別個の権限の下で管理されるもの、個人用デバイス、その他のホスト型サービスが含まれます。 | AC-20 SA-9(2) | ||
中および高影響 製造システムでの使用に必要な機能、ポート、プロトコル、その他のサービスを特定するよう、外部プロバイダーに求めます。 | ||||
| ID.AM-5 | 低・中・高影響 製造システムの構成要素と機能を、その分類、重要度、事業上の価値に基づいて特定し、優先順位を付けます。 セキュリティ保護対策が必要な、保有、保管、または管理している情報の種類(たとえば、機微な情報や保護対象の情報)を特定します。 | ISA/IEC 62443-2-1:2009 4.2.3.6 CP-2 | ||
| ID.AM-6 | 低・中・高影響 製造システムに関する要員のサイバーセキュリティ上の役割と責任を確立し、維持します。第三者プロバイダーのサイバーセキュリティ上の役割と責任も含めます。 製造システムの構成要素に物理的または論理的にアクセスできる要員の異動(配置転換や退職を含む)があった場合には、組織に通知するよう、第三者プロバイダーに求めます。 第三者プロバイダーには、たとえば、サービスプロバイダー、請負業者、および製造システムの開発、技術サービス、外部委託されたアプリケーション、またはネットワークとセキュリティの管理を提供するその他の組織が含まれます。 | ISA/IEC 62443-2-1:2009 4.3.2.3.3 CP-2 PS-7 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| IDENTIFY | Business Environment (ID.BE) | ID.BE-1 | Low and Moderate Impact Define and communicate the organization’s role in the supply chain. Identify the upstream and downstream supply channels that are outside of the organization's operations. Identify the overall mission supported by the manufacturing system. | CP-2(1)(3)(8) SA-12 |
High Impact Protect against supply chain threats to the manufacturing system, system components, or system services by employing security safeguards as part of a comprehensive, defense-in-depth security strategy. | ||||
| ID.BE-2 | Low, Moderate and High Impact Define and communicate the manufacturer's place in critical infrastructure and its industry sector. Define and communicate critical infrastructure and key resources relevant to the manufacturing system. Develop, document, and maintain a critical infrastructure and key resources protection plan. | PM-8 | ||
| ID.BE-3 | Low, Moderate and High Impact Define and communicate priorities for manufacturing missions, objectives, and activities with consideration for security and the resulting risk to manufacturing operations, components, and individuals. Identify critical manufacturing system components and functions by performing a criticality analysis. | ISA/IEC 62443-2-1:2009 4.2.2.1 PM-11 | ||
| ID.BE-4 | Low Impact Identify and prioritize supporting services for critical manufacturing system processes and components. Provide an uninterruptable power supply for identified critical manufacturing system components to facilitate the transition of the manufacturing system to long-term alternate power in the event of a primary power source loss. | PM-8 PE-11 PE-9(1) | ||
Moderate and High Impact Identify alternate and redundant supporting services for critical manufacturing system processes and components. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 識別(IDENTIFY) | ビジネス環境(ID.BE) | ID.BE-1 | 低および中影響 サプライチェーンにおける組織の役割を定義し、伝達します。 組織の運用の外にある、上流および下流の供給経路を特定します。製造システムが支えるミッション全体を特定します。 | CP-2(1)(3)(8) SA-12 |
高影響 包括的な多層防御のセキュリティ戦略の一環としてセキュリティ保護対策を採用することで、製造システム、システム構成要素、またはシステムサービスに対するサプライチェーンの脅威から保護します。 | ||||
| ID.BE-2 | 低・中・高影響 重要インフラと自らの産業セクターにおける製造者の位置付けを定義し、伝達します。 製造システムに関連する重要インフラおよび主要資源を定義し、伝達します。重要インフラおよび主要資源の保護計画を策定し、文書化し、維持します。 | PM-8 | ||
| ID.BE-3 | 低・中・高影響 セキュリティ、および製造運用、構成要素、個人にもたらされるリスクを考慮して、製造のミッション、目標、活動の優先順位を定義し、伝達します。 重要度分析を実施することで、重要な製造システムの構成要素と機能を特定します。 | ISA/IEC 62443-2-1:2009 4.2.2.1 PM-11 | ||
| ID.BE-4 | 低影響 重要な製造システムのプロセスと構成要素を支えるサービスを特定し、優先順位を付けます。 主電源が失われた場合に、製造システムが長期的な代替電源へ移行しやすくなるよう、特定した重要な製造システムの構成要素に無停電電源装置を備えます。 | PM-8 PE-11 PE-9(1) | ||
中および高影響 重要な製造システムのプロセスと構成要素を支える、代替用および冗長なサービスを特定します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| IDENTIFY | Business Environment (ID.BE) | ID.BE-5 | Low Impact Define resilience requirements for the manufacturing system to support delivery of critical services. | CP-2 CP-2(3) CP-2(8) CP-2(2) CP-2(4)(5) |
Moderate Impact Define recovery time objective and recovery point objective for the resumption of essential manufacturing system processes. Identify critical manufacturing system assets that support essential manufacturing system processes. | ||||
High Impact Conduct capacity planning for manufacturing system processing, telecommunications, and environmental support as required during contingency operations. Conduct contingency planning for the continuance of essential manufacturing functions and services with little or no loss of operational continuity and sustain that continuity until full system restoration. | ||||
| Governance (ID.GV) | ID.GV-1 | Low, Moderate and High Impact Develop and disseminate a security policy that provides an overview of the security requirements for the manufacturing system. The policy includes, for example, the identification and assignment of roles, responsibilities, management commitment, coordination among organizational entities, and compliance. It also reflects coordination among organizational entities responsible for the different aspects of security (i.e., technical, physical, personnel, cyber-physical, access control, media protection, vulnerability management, maintenance, monitoring), and covers the full life cycle of the manufacturing system. Review and update the security policy as determined necessary. Ensure the security policy is approved by a senior official with responsibility and accountability for the risk being incurred by manufacturing operations. | ISA/IEC 62443-2-1:2009 4.3.2.6 800-53 Security Policies-1 | |
| ID.GV-2 | Low, Moderate and High Impact Develop and disseminate a security program for the manufacturing system that includes, for example, the identification of personnel security roles and assignment of responsibilities, management commitment, coordination among organizational entities, and compliance. This includes security requirements, roles and responsibilities for third-party providers. Review and update the security program as determined necessary. | ISA/IEC 62443-2-1:2009 4.3.2.3.3 PM-1, PS-7 | ||
| ID.GV-3 | Low, Moderate and High Impact Ensure that legal and regulatory requirements affecting the manufacturing operations regarding cybersecurity are understood and managed. | ISA/IEC 62443-2-1:2009 4.4.3.7 800-53 Security Policies-1 | ||
| ID.GV-4 | Low, Moderate and High Impact Develop a comprehensive strategy to manage risk to manufacturing operations. Include cybersecurity considerations in the risk management strategy. Review and update the risk management strategy as determined necessary. Determine and allocate required resources to protect the manufacturing system. | ISA/IEC 62443-2-1:2009 4.2.3.1, 4.2.3.3, 4.2.3.8, 4.2.3.9 PM-9, PM-11 |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 識別(IDENTIFY) | ビジネス環境(ID.BE) | ID.BE-5 | 低影響 重要なサービスの提供を支えるために、製造システムのレジリエンス要件を定義します。 | CP-2 CP-2(3) CP-2(8) CP-2(2) CP-2(4)(5) |
中影響 不可欠な製造システムのプロセスを再開するための、目標復旧時間と目標復旧時点を定義します。 不可欠な製造システムのプロセスを支える、重要な製造システムの資産を特定します。 | ||||
高影響 緊急時対応の運用中に必要となる、製造システムの処理、通信、環境面の支援について、容量計画を実施します。 運用の継続性の損失をほとんど、またはまったく生じさせずに不可欠な製造機能とサービスを継続するための緊急時対応計画を実施し、システムが完全に復元されるまでその継続性を維持します。 | ||||
| ガバナンス(ID.GV) | ID.GV-1 | 低・中・高影響 製造システムのセキュリティ要件の概要を示すセキュリティポリシーを策定し、周知します。このポリシーには、たとえば、役割と責任の特定と割り当て、経営層のコミットメント、組織間の調整、コンプライアンスが含まれます。また、セキュリティのさまざまな側面(すなわち、技術、物理、要員、サイバーフィジカル、アクセス制御、媒体保護、脆弱性管理、保守、監視)を担当する組織間の調整を反映し、製造システムのライフサイクル全体を対象とします。セキュリティポリシーは、必要と判断した場合に見直し、更新します。 セキュリティポリシーが、製造運用によって負うリスクに対する責任と説明責任を持つ上級職員によって承認されていることを確実にします。 | ISA/IEC 62443-2-1:2009 4.3.2.6 800-53 Security Policies-1 | |
| ID.GV-2 | 低・中・高影響 製造システムのセキュリティプログラムを策定し、周知します。このプログラムには、たとえば、要員のセキュリティ上の役割の特定と責任の割り当て、経営層のコミットメント、組織間の調整、コンプライアンスが含まれます。これには、第三者プロバイダーのセキュリティ要件、役割、責任も含まれます。セキュリティプログラムは、必要と判断した場合に見直し、更新します。 | ISA/IEC 62443-2-1:2009 4.3.2.3.3 PM-1, PS-7 | ||
| ID.GV-3 | 低・中・高影響 サイバーセキュリティに関して製造運用に影響する法的要件および規制要件が理解され、管理されていることを確実にします。 | ISA/IEC 62443-2-1:2009 4.4.3.7 800-53 Security Policies-1 | ||
| ID.GV-4 | 低・中・高影響 製造運用に対するリスクを管理するための包括的な戦略を策定します。リスク管理戦略にサイバーセキュリティの考慮事項を含めます。リスク管理戦略は、必要と判断した場合に見直し、更新します。 製造システムを保護するために必要なリソースを決定し、割り当てます。 | ISA/IEC 62443-2-1:2009 4.2.3.1, 4.2.3.3, 4.2.3.8, 4.2.3.9 PM-9, PM-11 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| IDENTIFY | Risk Assessment (ID.RA) | ID.RA-1 | Low and Moderate Impact Develop a plan to identify, document, and report vulnerabilities that exist on the manufacturing system. Include the use of vulnerability scanning where safe and feasible on the manufacturing system, its components, or a representative system. Develop a plan for continuous monitoring of the security posture of the manufacturing system to facilitate ongoing awareness of vulnerabilities. Conduct risk assessments on the manufacturing system that take into account vulnerabilities and potential impact to manufacturing operations and assets. | ISA/IEC 62443-2-1:2009 4.2.3, 4.2.3.7, 4.2.3.9, 4.2.3.12 CA-2 CA-7 RA-3 CA-2(2) RA-5(4) |
High Impact Conduct performance/load testing and penetration testing on the manufacturing system with care to ensure that manufacturing operations are not adversely impacted by the testing process. Identify where manufacturing system vulnerabilities may be exposed to adversaries. Production systems may need to be taken off-line before testing can be conducted. If the manufacturing system is taken off-line for testing, tests are scheduled to occur during planned manufacturing outages whenever possible. If penetration testing is performed on non-manufacturing networks, extra care is taken to ensure that tests do not propagate into the manufacturing network. | ||||
| ID.RA-2 | Low and Moderate Impact Establish and maintain ongoing contact with security groups and associations to receive security alerts and advisories. Security groups and associations include, for example, special interest groups, forums, professional associations, news groups, and/or peer groups of security professionals in similar organizations. Implement a threat awareness program that includes a cross-organization information-sharing capability. Organizations should consider having both an unclassified and classified information sharing capability. Collaborate and share information about potential vulnerabilities and incidents. The Department of Homeland Security (DHS) National Cybersecurity & Communications Integration Center (NCCIC) [6] serves as a centralized location where operational elements involved in cybersecurity and communications reliance are coordinated and integrated. The Industrial Control Systems Cyber Emergency Response Team (ICS-CERT) [7] collaborates with international and private sector Computer Emergency Readiness Teams (CERTs) to share control systems-related security incidents and mitigation measures. | ISA/IEC 62443-2-1:2009 4.2.3, 4.2.3.9, 4.2.3.12 PM-15 PM-16 SI-5(1) | ||
High Impact Identify where automated mechanisms can be implemented to make security alert and advisory information available to relevant organization stakeholders. | ||||
| ID.RA-3 | Low, Moderate and High Impact Conduct and document periodic assessment of risk to the manufacturing system to identify threats and likelihood of impact to manufacturing operations and assets. The risk assessment includes threats from insiders and external parties. | ISA/IEC 62443-2-1:2009 4.2.3, 4.2.3.9, 4.2.3.12 RA-3 |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 識別(IDENTIFY) | リスクアセスメント(ID.RA) | ID.RA-1 | 低および中影響 製造システムに存在する脆弱性を特定し、文書化し、報告する計画を策定します。製造システム、その構成要素、または代表的なシステムで安全かつ実現可能な場合には、脆弱性スキャンの使用を含めます。 脆弱性への継続的な認識を促進するため、製造システムのセキュリティ態勢を継続的に監視する計画を策定します。 脆弱性と、製造運用および資産への潜在的な影響を考慮した、製造システムのリスクアセスメントを実施します。 | ISA/IEC 62443-2-1:2009 4.2.3, 4.2.3.7, 4.2.3.9, 4.2.3.12 CA-2 CA-7 RA-3 CA-2(2) RA-5(4) |
高影響 テストの過程が製造運用に悪影響を与えないよう注意しながら、製造システムの性能/負荷テストとペネトレーションテストを実施します。 製造システムの脆弱性が攻撃者にさらされる可能性のある箇所を特定します。 テストを実施する前に、本番システムをオフラインにする必要がある場合があります。テストのために製造システムをオフラインにする場合、可能な限り、計画された製造停止の間にテストが行われるようにスケジュールします。製造以外のネットワークでペネトレーションテストを実施する場合は、テストが製造ネットワークに波及しないよう、特に注意を払います。 | ||||
| ID.RA-2 | 低および中影響 セキュリティアラートや勧告を受け取るため、セキュリティグループや団体との継続的な連絡を確立し、維持します。セキュリティグループや団体には、たとえば、特別利益団体、フォーラム、専門家団体、ニュースグループ、または類似組織のセキュリティ専門家によるピアグループが含まれます。組織横断的な情報共有の能力を含む脅威認識プログラムを実施します。組織は、非機密と機密の両方の情報共有能力を持つことを検討すべきです。 潜在的な脆弱性やインシデントについて、協力し、情報を共有します。国土安全保障省(DHS)の National Cybersecurity & Communications Integration Center(NCCIC)[6] は、サイバーセキュリティと通信への依存に関わる運用要素を調整し、統合する中央拠点としての役割を果たします。Industrial Control Systems Cyber Emergency Response Team(ICS-CERT)[7] は、国際的な、および民間部門のコンピュータ緊急対応チーム(CERT)と協力して、制御システムに関連するセキュリティインシデントと緩和策を共有します。 | ISA/IEC 62443-2-1:2009 4.2.3, 4.2.3.9, 4.2.3.12 PM-15 PM-16 SI-5(1) | ||
高影響 セキュリティアラートや勧告の情報を、関連する組織のステークホルダーが利用できるようにするために、自動化された仕組みを実装できる箇所を特定します。 | ||||
| ID.RA-3 | 低・中・高影響 製造運用と資産に影響が及ぶ脅威と可能性を特定するため、製造システムのリスクの定期的なアセスメントを実施し、文書化します。リスクアセスメントには、内部関係者と外部関係者による脅威を含めます。 | ISA/IEC 62443-2-1:2009 4.2.3, 4.2.3.9, 4.2.3.12 RA-3 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| IDENTIFY | Risk Assessment (ID.RA) | ID.RA-4 | Low, Moderate and High Impact Conduct criticality reviews of the manufacturing system that define the likelihood and potential adverse impacts to manufacturing operations, assets, and individuals if compromised or disabled. | ISA/IEC 62443-2-1:2009 4.2.3, 4.2.3.9, 4.2.3.12 RA-2 |
| ID.RA-5 | Low, Moderate and High Impact Conduct risk assessments of the manufacturing system incorporating threats, vulnerabilities, likelihood, and impact to manufacturing operations, assets, and individuals. Disseminate risk assessment results to relevant stakeholders. | RA-3 PM-16 | ||
| ID.RA-6 | Low, Moderate and High Impact Develop and implement a comprehensive strategy to manage risk to the manufacturing system that includes the identification and prioritization of risk responses. | PM-9 | ||
| Risk Management Strategy (ID.RM) | ID.RM-1 | Low, Moderate and High Impact Establish a risk management process for the manufacturing system that effectively identifies, communicates, and facilitates addressing risk-related issues and information among key stakeholders internally and externally. | ISA/IEC 62443-2-1:2009 4.3.4.2 PM-9 | |
| ID.RM-2 | Low, Moderate and High Impact Define the risk tolerance for the manufacturing system. | ISA/IEC 62443-2-1:2009 4.3.2.6.5 PM-9 | ||
| ID.RM-3 | Low, Moderate and High Impact Ensure the risk tolerance for the manufacturing system is informed by the organization's role in critical infrastructure and sector-specific risk analysis. | PM-9, PM-8 | ||
| Supply Chain (ID.SC) | ID.SC-1 | Low, Moderate and High Impact Implement a cyber supply chain risk management process that effectively identifies, assesses, communicates, and facilitates addressing risk-related issues associated with the sharing of sensitive information or the use of information technology, operational technology, services, technology-based input products, and non-technology-based input products supporting the manufacturing system. The cyber supply chain risk management process should be approved by organizational stakeholders including those responsible for informational technology and operational technology systems. | SA-9 | |
| ID.SC-2 | Low, Moderate and High Impact Conduct and document cyber supply chain risk assessments at least annually or when a change to the manufacturing system, operational environment, or supply chain occurs. This assessment should identify and prioritize potential negative impacts to the organization from the sharing of sensitive information or the use of information technology, operational technology, services, technology-based input products, or non-technology-based input products supporting the manufacturing system. Disseminate results to relevant stakeholders including those responsible for informational technology and operational technology systems. | RA-3 |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 識別(IDENTIFY) | リスクアセスメント(ID.RA) | ID.RA-4 | 低・中・高影響 製造システムが危殆化または無効化された場合に、製造運用、資産、個人に及ぶ悪影響の可能性と潜在的な影響を定義する、製造システムの重要度レビューを実施します。 | ISA/IEC 62443-2-1:2009 4.2.3, 4.2.3.9, 4.2.3.12 RA-2 |
| ID.RA-5 | 低・中・高影響 脅威、脆弱性、可能性、および製造運用、資産、個人への影響を取り入れた、製造システムのリスクアセスメントを実施します。リスクアセスメントの結果を、関連するステークホルダーに周知します。 | RA-3 PM-16 | ||
| ID.RA-6 | 低・中・高影響 リスク対応の特定と優先順位付けを含む、製造システムのリスクを管理するための包括的な戦略を策定し、実装します。 | PM-9 | ||
| リスク管理戦略(ID.RM) | ID.RM-1 | 低・中・高影響 リスクに関する問題と情報を、内部および外部の主要なステークホルダーの間で効果的に特定し、伝達し、対処しやすくする、製造システムのリスク管理プロセスを確立します。 | ISA/IEC 62443-2-1:2009 4.3.4.2 PM-9 | |
| ID.RM-2 | 低・中・高影響 製造システムのリスク許容度を定義します。 | ISA/IEC 62443-2-1:2009 4.3.2.6.5 PM-9 | ||
| ID.RM-3 | 低・中・高影響 製造システムのリスク許容度が、重要インフラにおける組織の役割と、セクター固有のリスク分析に基づいて決定されていることを確実にします。 | PM-9, PM-8 | ||
| サプライチェーン(ID.SC) | ID.SC-1 | 低・中・高影響 機微な情報の共有、または製造システムを支える情報技術、運用技術、サービス、技術ベースの投入製品、非技術ベースの投入製品の使用に関連するリスクの問題を、効果的に特定、評価、伝達し、対処しやすくする、サイバーサプライチェーンリスク管理プロセスを実装します。サイバーサプライチェーンリスク管理プロセスは、情報技術システムおよび運用技術システムを担当する者を含む、組織のステークホルダーによって承認されるべきです。 | SA-9 | |
| ID.SC-2 | 低・中・高影響 少なくとも年1回、または製造システム、運用環境、サプライチェーンに変更があったときに、サイバーサプライチェーンのリスクアセスメントを実施し、文書化します。このアセスメントでは、機微な情報の共有、または製造システムを支える情報技術、運用技術、サービス、技術ベースの投入製品、非技術ベースの投入製品の使用によって組織に生じうる悪影響を特定し、優先順位を付けるべきです。結果を、情報技術システムおよび運用技術システムを担当する者を含む、関連するステークホルダーに周知します。 | RA-3 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| IDENTIFY | Supply Chain (ID.SC) | ID.SC-3 | Low Impact Implement contractual cybersecurity requirements for suppliers and third-party partners requiring access to sensitive information or providing information technology, operational technology, services, technology-based input products, or non-technology-based input products supporting the manufacturing system. Cyber supply chain risk assessment results should be used in the development of cybersecurity requirements. | SA-9 SA-11 SA-12 |
Moderate Impact Implement contract cybersecurity requirements for suppliers and third-party partners to implement a verifiable flaw remediation process, and correct flaws identified during cybersecurity testing and evaluation. | ||||
High Impact Implement contract requirements permitting the organization to review the cybersecurity programs implemented by suppliers and third-party partners. Implement contract requirements for suppliers and third-party partners to implement a documented development life cycle for the information technology, operational technology, services, technology-based input products, or non-technology-based input products supporting the manufacturing system. | ||||
| ID.SC-4 | Low and Moderate Impact Review assessments of suppliers and third-party partner compliance with contractual obligations by routinely reviewing audits, test results, and other evaluations. | AU-2 AU-6 PS-7 | ||
High Impact Review assessments of suppliers and third-party partner compliance with contractual obligations by routinely reviewing third-party independent audits, test results, and other evaluations. | ||||
| ID.SC-5 | Low and Moderate Impact Identify and document key personnel from suppliers and third-party partners to include as stakeholders in response and recovery planning activities. | CP-4, IR-3, IR-4 CP-4, IR-3, IR-4 | ||
High Impact Identify and document key personnel from suppliers and third-party partners to include as stakeholders in testing and execution of the response and recovery plans. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 識別(IDENTIFY) | サプライチェーン(ID.SC) | ID.SC-3 | 低影響 機微な情報へのアクセスを必要とする、または製造システムを支える情報技術、運用技術、サービス、技術ベースの投入製品、非技術ベースの投入製品を提供するサプライヤーおよび第三者パートナーに対して、契約上のサイバーセキュリティ要件を実装します。サイバーサプライチェーンのリスクアセスメントの結果は、サイバーセキュリティ要件の策定に用いるべきです。 | SA-9 SA-11 SA-12 |
中影響 サプライヤーおよび第三者パートナーに、検証可能な欠陥是正プロセスを実装し、サイバーセキュリティのテストおよび評価の際に特定された欠陥を修正することを求める、契約上のサイバーセキュリティ要件を実装します。 | ||||
高影響 サプライヤーおよび第三者パートナーが実施するサイバーセキュリティプログラムを組織が見直すことを認める契約要件を実装します。 サプライヤーおよび第三者パートナーに、製造システムを支える情報技術、運用技術、サービス、技術ベースの投入製品、非技術ベースの投入製品について、文書化された開発ライフサイクルを実装することを求める契約要件を実装します。 | ||||
| ID.SC-4 | 低および中影響 監査、テスト結果、その他の評価を定期的に見直すことで、サプライヤーおよび第三者パートナーによる契約上の義務の遵守に関する評価を見直します。 | AU-2 AU-6 PS-7 | ||
高影響 第三者による独立した監査、テスト結果、その他の評価を定期的に見直すことで、サプライヤーおよび第三者パートナーによる契約上の義務の遵守に関する評価を見直します。 | ||||
| ID.SC-5 | 低および中影響 対応および復旧の計画活動のステークホルダーとして含めるため、サプライヤーおよび第三者パートナーの主要な要員を特定し、文書化します。 | CP-4, IR-3, IR-4 CP-4, IR-3, IR-4 | ||
高影響 対応計画および復旧計画のテストと実行のステークホルダーとして含めるため、サプライヤーおよび第三者パートナーの主要な要員を特定し、文書化します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Identity Management, Authentication and Access Control (PR.AC) | PR.AC-1 | Low Impact Establish and manage identification mechanisms and credentials for users of the manufacturing system. | ISA/IEC 62443-2-1:2009 4.3.3.5.1; SR 1.1, 1.2, 1.3, 1.4, 1.5,1.7 IA-Family AC-2(1) AC-2(5) AC-2(12)(13) |
Moderate Impact Establish and manage identification mechanisms and credentials for users and devices of the manufacturing system. Implement automated mechanisms where feasible to support the management and auditing of information system credentials. | ||||
High Impact Deactivate system credentials after a specified time period of inactivity, unless this would result in a compromise to safe operation of the process. Monitor the manufacturing system for atypical use of system credentials. Credentials associated with significant risk are disabled. | ||||
| PR.AC-2 | Low Impact Protect physical access to the manufacturing facility. Determine access requirements during emergency situations. Maintain and review visitor access records to the facility where the manufacturing system resides. Physical access controls may include, for example, lists of authorized individuals, identity credentials, escort requirements, guards, fences, turnstiles, locks, monitoring of facility access. | ISA/IEC 62443-2-1:2009 4.3.3.3.2 PE-Family PE-9 (1) PE-3 (1) | ||
Moderate Impact Protect power equipment, power cabling, network cabling, and network access interfaces for the manufacturing system from accidental damage, disruption, and physical tampering. Ensure availability and integrity of wireless systems, especially safety related systems. Implement redundant and physically separated power systems for critical manufacturing operations. | ||||
High Impact Control physical access to the manufacturing system in addition to the physical access for the facility. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | アイデンティティ管理、認証、アクセス制御(PR | PR.AC-1 | 低影響 製造システムの利用者のための識別の仕組みと認証情報を確立し、管理します。 | ISA/IEC 62443-2-1:2009 4.3.3.5.1; SR 1.1, 1.2, 1.3, 1.4, 1.5,1.7 IA-Family AC-2(1) AC-2(5) AC-2(12)(13) |
中影響 製造システムの利用者およびデバイスのための識別の仕組みと認証情報を確立し、管理します。情報システムの認証情報の管理と監査を支援するため、実現可能な場合には自動化された仕組みを実装します。 | ||||
高影響 プロセスの安全な運用が損なわれる場合を除き、指定された期間にわたって使用されなかったシステムの認証情報を無効化します。 製造システムを監視し、システムの認証情報が通常とは異なる形で使用されていないかを確認します。重大なリスクに関連する認証情報は無効にします。 | ||||
| PR.AC-2 | 低影響 製造施設への物理的なアクセスを保護します。緊急事態におけるアクセス要件を決定します。 製造システムが設置されている施設への来訪者のアクセス記録を維持し、見直します。 物理的アクセス制御には、たとえば、許可された個人の一覧、身分証明用の認証情報、付き添いの要件、警備員、フェンス、回転式ゲート、錠、施設へのアクセスの監視が含まれる場合があります。 | ISA/IEC 62443-2-1:2009 4.3.3.3.2 PE-Family PE-9 (1) PE-3 (1) | ||
中影響 製造システムの電力設備、電源ケーブル、ネットワークケーブル、ネットワークアクセスインターフェースを、偶発的な損傷、中断、物理的な改ざんから保護します。無線システム、特に安全に関連するシステムの可用性と完全性を確保します。 重要な製造運用のために、冗長で物理的に分離された電源システムを実装します。 | ||||
高影響 施設への物理的なアクセスに加えて、製造システムへの物理的なアクセスも制御します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Identity Management, Authentication and Access Control (PR.AC) | PR.AC-3 | Low Impact Establish usage restrictions, connection requirements, implementation guidance, and authorizations for remote access to the manufacturing system. Provide an explicit indication of active remote access connections to users physically present at the devices. Remote access methods include, for example, wireless, dial-up, broadband, Virtual Private Network (VPN) connections, mobile device connections, and communications through external networks. | ISA/IEC 62443-2-1:2009 4.3.3.6.6 ISA/IEC 62443-3-3:2013 SR 1.13,2.6 AC-17, AC-19, AC-20 SC-15 AC-17(1)(2)(3)(4) AC-20(1)(2) |
Moderate and High Impact Allow remote access only through approved and managed access points. Monitor remote access to the manufacturing system and implement cryptographic mechanisms where determined necessary. Allow only authorized use of privileged functions from remote access. Establish agreements and verify security for connections with external systems. | ||||
| PR.AC-4 | Low Impact Define and manage access permissions for users of the manufacturing system. Identify and document user actions that can be performed on the manufacturing system without identification or authentication (e.g. during emergencies). | ISA/IEC 62443-2-1:2009 4.3.3.7.3; 62443-3-3:2013 SR 2.1 AC-Family AC-2(1)(3) AC-5 AC-6(1)(2)(5)(9) AC-2(11)(12)(13) | ||
Moderate Impact Implement automated mechanisms where feasible to support the management of manufacturing system user accounts, including the disabling, auditing, notification, and removal of user accounts. Implement separation of duties for manufacturing system users. Limit, document, and explicitly authorize privileged user access to the manufacturing system. Audit the execution of privileged functions on the manufacturing system. Separation of duties includes, for example: dividing operational functions and system support functions among different roles; conducting system support functions with different individuals; and ensuring security personnel administering access control functions do not also administer audit functions. | ||||
High Impact Enforce account usage restrictions for specific time periods and locality. Monitor manufacturing system usage for atypical use. Disable accounts of users posing a significant risk. Specific restrictions can include, for example, restricting usage to certain days of the week, time of day, or specific durations of time. Privileged user access through non-local connections to the manufacturing system is restricted and managed. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | アイデンティティ管理、認証、アクセス制御(PR | PR.AC-3 | 低影響 製造システムへのリモートアクセスについて、使用上の制限、接続要件、実装指針、認可を確立します。 稼働中のリモートアクセス接続を、デバイスの現場にいる利用者に明示します。 リモートアクセスの方法には、たとえば、無線、ダイヤルアップ、ブロードバンド、仮想プライベートネットワーク(VPN)接続、モバイルデバイスの接続、外部ネットワークを通じた通信が含まれます。 | ISA/IEC 62443-2-1:2009 4.3.3.6.6 ISA/IEC 62443-3-3:2013 SR 1.13,2.6 AC-17, AC-19, AC-20 SC-15 AC-17(1)(2)(3)(4) AC-20(1)(2) |
中および高影響 リモートアクセスは、承認され管理されたアクセスポイントを通じてのみ許可します。 製造システムへのリモートアクセスを監視し、必要と判断した場合には暗号による仕組みを実装します。リモートアクセスからの特権機能の使用は、許可されたものに限ります。外部システムとの接続について、合意を確立し、セキュリティを検証します。 | ||||
| PR.AC-4 | 低影響 製造システムの利用者のアクセス許可を定義し、管理します。識別または認証なしに製造システム上で実行できる利用者の操作(たとえば、緊急時)を特定し、文書化します。 | ISA/IEC 62443-2-1:2009 4.3.3.7.3; 62443-3-3:2013 SR 2.1 AC-Family AC-2(1)(3) AC-5 AC-6(1)(2)(5)(9) AC-2(11)(12)(13) | ||
中影響 製造システムの利用者アカウントの無効化、監査、通知、削除を含む管理を支援するため、実現可能な場合には自動化された仕組みを実装します。製造システムの利用者について職務の分離を実施します。製造システムへの特権利用者のアクセスを制限し、文書化し、明示的に認可します。製造システム上での特権機能の実行を監査します。 職務の分離には、たとえば、運用機能とシステム支援機能を異なる役割に分けること、システム支援機能を異なる個人が実施すること、アクセス制御機能を管理するセキュリティ要員が監査機能を管理しないようにすることが含まれます。 | ||||
高影響 特定の期間や場所に応じたアカウント使用の制限を適用します。製造システムの使用を監視し、通常とは異なる使用を確認します。重大なリスクをもたらす利用者のアカウントを無効にします。 具体的な制限には、たとえば、使用を特定の曜日、時間帯、または特定の時間の長さに制限することが含まれます。ローカルでない接続を通じた製造システムへの特権利用者のアクセスは、制限され、管理されます。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Identity Management, Authentication and Access Control (PR.AC) | PR.AC-5 | Low Impact Protect network integrity of the manufacturing system, incorporating network segmentation and segregation where appropriate. Identify and control connections between system components. Monitor and control connections and communications at the external boundary and at key internal boundaries within the manufacturing system. Implement boundary protection devices. Boundary protection mechanisms include, for example, routers, gateways, unidirectional gateways, data diodes, and firewalls separating system components into logically separate networks or subnetworks. | ISA/IEC 62443-2-1:2009 4.3.3.4 62443-3-3:2013 SR 3.1, 3.8 SC-7 AC-4 SC-7(8) SC-7(21) |
Moderate Impact Limit external connections to the manufacturing system. Monitor and use managed interfaces to conduct external system connections. Deny by default connections to the managed interface. Disable split tunneling and covert channel options in conjunction with remote devices. Ensure the manufacturing system fails securely in the event of the operational failure of a boundary protection device. | ||||
High Impact Implement, where feasible, authenticated proxy servers for defined communications traffic between the manufacturing system and external networks. Isolate manufacturing system components performing different missions. | ||||
| PR.AC-6 | Low and Moderate Impact Implement procedures for verifying identity of individuals before issuing credentials that provide access to the manufacturing systems. | IA-5 | ||
High Impact Issue unique credentials bound to each verified user, device, and process interacting with the manufacturing systems. Ensure credentials are authenticated and the unique identifiers are captured when performing system interactions. | IA-5 | |||
| PR.AC-7 | Low Impact Perform a risk assessment on manufacturing user transactions to document and implement the authentication mechanisms required (e.g. single- or multi-factor) for each transaction. | IA-1, IA-2, IA-4, IA-5, IA-8 | ||
Moderate Impact Perform a risk assessment on manufacturing system transactions and the associated user, device, or other asset authentication mechanism to document and implement the authentication mechanisms required (e.g. single- or multi-factor) for each transaction. | IA-1, IA-2, IA-4, IA-5, IA-8 | |||
High Impact Implement multi-factor or certificate-based authentication for transactions within the manufacturing systems determined to be critical. | IA-2 (1) (2) (3) |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | アイデンティティ管理、認証、アクセス制御(PR | PR.AC-5 | 低影響 必要に応じてネットワークのセグメント化と分離を取り入れ、製造システムのネットワークの完全性を保護します。システム構成要素間の接続を特定し、制御します。製造システムの外部境界と内部の主要な境界における接続と通信を監視し、制御します。境界保護デバイスを実装します。 境界保護の仕組みには、たとえば、システム構成要素を論理的に分離されたネットワークまたはサブネットワークに分けるルーター、ゲートウェイ、単方向ゲートウェイ、データダイオード、ファイアウォールが含まれます。 | ISA/IEC 62443-2-1:2009 4.3.3.4 62443-3-3:2013 SR 3.1, 3.8 SC-7 AC-4 SC-7(8) SC-7(21) |
中影響 製造システムへの外部接続を制限します。外部システムへの接続は、管理されたインターフェースを監視し、使用して行います。管理されたインターフェースへの接続は、デフォルトで拒否します。リモートデバイスに関連して、スプリットトンネリングと隠れチャネルのオプションを無効にします。境界保護デバイスに運用上の障害が発生した場合に、製造システムが安全に機能停止するようにします。 | ||||
高影響 実現可能な場合には、製造システムと外部ネットワークの間の特定の通信トラフィックに、認証済みのプロキシサーバーを実装します。 異なるミッションを担う製造システムの構成要素を分離します。 | ||||
| PR.AC-6 | 低および中影響 製造システムへのアクセスを提供する認証情報を発行する前に、個人の身元を確認する手順を実装します。 | IA-5 | ||
高影響 製造システムとやり取りする、検証済みの各利用者、デバイス、プロセスに紐づけた一意の認証情報を発行します。 システムとのやり取りを行う際に、認証情報が認証され、一意の識別子が記録されるようにします。 | IA-5 | |||
| PR.AC-7 | 低影響 製造における利用者のトランザクションについてリスクアセスメントを実施し、各トランザクションに必要な認証の仕組み(たとえば、単一要素または多要素)を文書化し、実装します。 | IA-1, IA-2, IA-4, IA-5, IA-8 | ||
中影響 製造システムのトランザクション、およびそれに関連する利用者、デバイス、その他の資産の認証の仕組みについてリスクアセスメントを実施し、各トランザクションに必要な認証の仕組み(たとえば、単一要素または多要素)を文書化し、実装します。 | IA-1, IA-2, IA-4, IA-5, IA-8 | |||
高影響 重要と判断された製造システム内のトランザクションに、多要素認証または証明書に基づく認証を実装します。 | IA-2 (1) (2) (3) |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Awareness and Training (PR.AT) | PR.AT-1 | Low Impact Provide security awareness training for all manufacturing system users and managers. Training could include, for example, a basic understanding of the protections and user actions needed to maintain security of the system, responding to suspected cybersecurity incidents, and awareness of operational security. | ISA/IEC 62443-2-1:2009 4.3.2.4.2 AT-2 AT-2(2) |
Moderate and High Impact Incorporate insider threat recognition and reporting into security awareness training. | ||||
| PR.AT-2 | Low, Moderate and High Impact Ensure that users with privileged access to the manufacturing system understand the requirements and responsibilities of their assignments. Establish standards for measuring, building, and validating individual qualifications for privileged users. | ISA/IEC 62443-2-1:2009 4.3.2.4.2 AT-3 PM-13 | ||
| PR.AT-3 | Low Impact Establish and enforce security requirements for third-party providers and users. Ensure that third-party providers understand their responsibilities regarding the security of the manufacturing system and the responsibilities of their assignments. Require notifications be given for any personnel transfers, termination, or transition involving personnel with physical or logical access to the manufacturing system components. Ensure that providers of external system services comply with defined security requirements. Monitor and audit external service providers for security compliance. | ISA 62443-2-1:2009 4.3.2.4.2 PS-7 SA-9 SA-9(2) | ||
Moderate and High Impact Require external service providers to identify the functions, ports, protocols, and services necessary for the connection services. | ||||
| PR.AT-4 | Low, Moderate and High Impact Ensure that senior executives understand the requirements for the security and protection of the manufacturing system, and their responsibilities for achieving them. | ISA/IEC 62443-2-1:2009 4.3.2.4.2 AT-3 | ||
| PR.AT-5 | Low, Moderate and High Impact Ensure that personnel responsible for the physical protection and security of the manufacturing system and facility are trained and understand their responsibilities. Establish standards for measuring, building, and validating individual qualifications for physical security personnel. | ISA/IEC 62443-2-1:2009 4.3.2.4.2 AT-3 PM-13 |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | 意識向上およびトレーニング(PR.AT) | PR.AT-1 | 低影響 製造システムのすべての利用者と管理者に、セキュリティ意識向上トレーニングを提供します。 トレーニングには、たとえば、システムのセキュリティを維持するために必要な保護策と利用者の行動の基本的な理解、疑わしいサイバーセキュリティインシデントへの対応、運用上のセキュリティに対する意識が含まれます。 | ISA/IEC 62443-2-1:2009 4.3.2.4.2 AT-2 AT-2(2) |
中および高影響 内部脅威の認識と報告を、セキュリティ意識向上トレーニングに組み込みます。 | ||||
| PR.AT-2 | 低・中・高影響 製造システムへの特権アクセス権を持つ利用者が、割り当てられた任務の要件と責任を理解していることを確実にします。 特権利用者の個人の資格を測定し、育成し、検証するための基準を確立します。 | ISA/IEC 62443-2-1:2009 4.3.2.4.2 AT-3 PM-13 | ||
| PR.AT-3 | 低影響 第三者プロバイダーおよび利用者に対するセキュリティ要件を確立し、実施します。第三者プロバイダーが、製造システムのセキュリティに関する自らの責任と、割り当てられた任務の責任を理解していることを確実にします。製造システムの構成要素に物理的または論理的にアクセスできる要員の異動、退職、または配置転換があった場合には、通知することを求めます。 外部システムサービスのプロバイダーが、定められたセキュリティ要件を遵守していることを確実にします。外部サービスプロバイダーを監視し、セキュリティ要件の遵守について監査します。 | ISA 62443-2-1:2009 4.3.2.4.2 PS-7 SA-9 SA-9(2) | ||
中および高影響 接続サービスに必要な機能、ポート、プロトコル、サービスを特定するよう、外部サービスプロバイダーに求めます。 | ||||
| PR.AT-4 | 低・中・高影響 上級幹部が、製造システムのセキュリティと保護に関する要件と、それを達成するための自らの責任を理解していることを確実にします。 | ISA/IEC 62443-2-1:2009 4.3.2.4.2 AT-3 | ||
| PR.AT-5 | 低・中・高影響 製造システムと施設の物理的な保護とセキュリティを担当する要員が、トレーニングを受け、自らの責任を理解していることを確実にします。 物理セキュリティ要員の個人の資格を測定し、育成し、検証するための基準を確立します。 | ISA/IEC 62443-2-1:2009 4.3.2.4.2 AT-3 PM-13 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Data Security (PR.DS) | PR.DS-1 | Low Impact None | ISA/IEC 62443-3-3:2013 SR 3.4, 4.1 SC-28 |
Moderate and High Impact Protect manufacturing system information determined to be critical while at rest. | ||||
| PR.DS-2 | Low Impact None | ISA/IEC 62443-3-3:SR 3.1,3.8,4.1 SC-8 SC-8(1) | ||
Moderate and High Impact Protect manufacturing system information determined to be critical when in transit. Implement cryptographic mechanisms where determined necessary to prevent unauthorized access, distortion, or modification of system data and audit records. | ||||
| PR.DS-3 | Low Impact Enforce accountability for all manufacturing system components throughout the system lifecycle, including removal, transfers, and disposition. Sanitize portable media prior to disposal, release, or reuse. All system components entering and exiting the facility are authorized, monitored, and controlled, and records are maintained of those items. | ISA/IEC 62443-2-1:2009 4. 4.3.3.3.9 ISA/IEC 62443-3-3:2013 SR 4.2 PE-16 MP-6 CM-8(1) CM-8(2) MP-6(1) | ||
Moderate Impact Update the inventory of manufacturing system components as an integral part of component installations, removals, and system updates. | ||||
High Impact Implement automated mechanisms where safe and feasible to maintain an up-to-date, complete, accurate, and readily available inventory of manufacturing system components. Ensure that disposal actions are approved, tracked, documented, and verified. | ||||
| PR.DS-4 | Low Impact Ensure that adequate resources are maintained for manufacturing system information processing, networking, telecommunications, and data storage. Off-load audit records from the manufacturing system for processing to an alternate system. | ISA/IEC 62443-3-3:2013 SR 7.1, 7.2 CP-2 AU-4(1) SC-5 | ||
Moderate and High Impact Protect the manufacturing system against, or limit the effects of, denial of service attacks. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | データセキュリティ(PR.DS) | PR.DS-1 | 低影響 なし | ISA/IEC 62443-3-3:2013 SR 3.4, 4.1 SC-28 |
中および高影響 重要と判断された製造システムの情報を、保存時に保護します。 | ||||
| PR.DS-2 | 低影響 なし | ISA/IEC 62443-3-3:SR 3.1,3.8,4.1 SC-8 SC-8(1) | ||
中および高影響 重要と判断された製造システムの情報を、伝送時に保護します。 システムデータと監査記録に対する、許可されていないアクセス、歪曲、改変を防ぐため、必要と判断した場合には暗号による仕組みを実装します。 | ||||
| PR.DS-3 | 低影響 撤去、移管、処分を含め、システムのライフサイクル全体にわたって、製造システムのすべての構成要素に対する説明責任を徹底します。 可搬媒体は、廃棄、解放、再利用の前にサニタイズします。施設に出入りするすべてのシステム構成要素は、許可され、監視され、管理され、それらの品目の記録が維持されます。 | ISA/IEC 62443-2-1:2009 4. 4.3.3.3.9 ISA/IEC 62443-3-3:2013 SR 4.2 PE-16 MP-6 CM-8(1) CM-8(2) MP-6(1) | ||
中影響 構成要素の設置、撤去、システム更新に不可欠な作業として、製造システムの構成要素の目録を更新します。 | ||||
高影響 安全かつ実現可能な場合には、製造システムの構成要素の最新で、完全で、正確で、すぐに利用できる目録を維持するための自動化された仕組みを実装します。 処分の措置が、承認され、追跡され、文書化され、検証されるようにします。 | ||||
| PR.DS-4 | 低影響 製造システムの情報処理、ネットワーキング、通信、データストレージのために、十分なリソースが維持されるようにします。 製造システムの監査記録を代替システムにオフロードし、そこで処理します。 | ISA/IEC 62443-3-3:2013 SR 7.1, 7.2 CP-2 AU-4(1) SC-5 | ||
中および高影響 サービス拒否攻撃から製造システムを保護するか、その影響を抑えます。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Data Security (PR.DS) | PR.DS-5 | Low Impact Protect the manufacturing system against data leaks. Monitor the manufacturing system at the external boundary and at key internal points to detect unauthorized access and use. Develop and document access agreements for all users of the manufacturing system. | ISA/IEC 62443-3-3:2013 SR 5.2 SI-4 SC-7 PS-6 AC-4 SC-7(3)(4), SI-4(4) PE-19 |
Moderate and High Impact Regulate the information flow within the manufacturing system and to outside systems. Enforce controls restricting connections to only authorized interfaces. Heighten system monitoring activity whenever there is an indication of increased risk to manufacturing operations and assets. Protect the system from information leakage due to electromagnetic signals emanations. | ||||
| PR.DS-6 | Low Impact None | ISA/IEC 62443-3-3:SR 3.1, 3.3, 3.4, SI-7(1) SI-7(7) SI-7(2) SI-7(5) | ||
Moderate Impact Implement software, firmware, and information integrity checks to detect unauthorized changes to manufacturing system components during storage, transport, startup and when determined necessary. Incorporate the detection of unauthorized changes to the manufacturing system into the system's incident response capability. | ||||
High Impact Implement automated tools where feasible to provide notification upon discovering discrepancies during integrity verification. Implement automatic response capability with pre-defined security safeguards when integrity violations are discovered. | ||||
| PR.DS-7 | Low and Moderate Impact None | CM-2 | ||
High Impact Implement an off-line development and testing system for implementing and testing changes to the manufacturing system. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | データセキュリティ(PR.DS) | PR.DS-5 | 低影響 データ漏えいから製造システムを保護します。 許可されていないアクセスと使用を検知するため、外部境界と内部の主要な箇所で製造システムを監視します。 製造システムのすべての利用者について、アクセスに関する合意書を作成し、文書化します。 | ISA/IEC 62443-3-3:2013 SR 5.2 SI-4 SC-7 PS-6 AC-4 SC-7(3)(4), SI-4(4) PE-19 |
中および高影響 製造システム内、および外部システムとの間の情報の流れを規制します。 接続を許可されたインターフェースのみに制限する管理策を適用します。 製造運用や資産へのリスクが高まっている兆候があるときはいつでも、システムの監視活動を強化します。 電磁信号の放射による情報漏えいから、システムを保護します。 | ||||
| PR.DS-6 | 低影響 なし | ISA/IEC 62443-3-3:SR 3.1, 3.3, 3.4, SI-7(1) SI-7(7) SI-7(2) SI-7(5) | ||
中影響 保管時、輸送時、起動時、および必要と判断したときに、製造システムの構成要素に対する許可されていない変更を検知するため、ソフトウェア、ファームウェア、情報の完全性チェックを実装します。 製造システムに対する許可されていない変更の検知を、システムのインシデント対応能力に組み込みます。 | ||||
高影響 完全性の検証中に不一致を発見した際に通知するため、実現可能な場合には自動化されたツールを実装します。 完全性の違反が発見されたときに、あらかじめ定義されたセキュリティ保護対策による自動対応能力を実装します。 | ||||
| PR.DS-7 | 低および中影響 なし | CM-2 | ||
高影響 製造システムへの変更を実装し、テストするための、オフラインの開発・テストシステムを実装します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Data Security (PR.DS) | PS.DS-8 | Low and Moderate Impact None | SI-7 |
High Impact Implement hardware integrity checks to detect unauthorized tampering (e.g. tamper evident tape or labels, computer port protection, power-on self-tests, etc.) to manufacturing system hardware determined to be critical. Incorporate the detection of unauthorized tampering to the manufacturing system hardware into the organization incident response capability. | ||||
| Information Protection Processes and Procedures (PR.IP) | PR.IP-1 | Low Impact Develop, document, and maintain a baseline configuration for the manufacturing system. Baseline configurations include for example, information about manufacturing system components (e.g. software license information, software version numbers, HMI and other ICS component applications, software, operating systems), current version numbers and patch information on operating systems and applications; and configuration settings/parameters), network topology, and the logical placement of those components within the system architecture. Configure the manufacturing system to provide only essential capabilities. Review the baseline configuration and disable unnecessary capabilities. | ISA/IEC 62443-2-1:2009 4.3.4.3.2, ISA/IEC 62443-3-3:2013 SR 7.6 CM-2 CM-6 CM-7 CM-7(1) CM-2(1)(3) CM-7(2) CM-9 SC-24 CM-7(5) CM-2(2) CM-3(1) CM-5(1)(2) | |
Moderate Impact Review and update the baseline configuration of the manufacturing system as an integral part of system component installations and upgrades. Retain previous versions of the baseline configuration to support rollback. Implement software program usage restrictions. Develop a configuration management plan for the manufacturing system. The plan includes, for example, configuration processes, roles, lifecycle definition, configuration items, and control methods. Define configuration parameters, capabilities, and fail to known state procedures such that, upon a system failure (or failure conditions), assets revert to a state that achieves a predetermined mode of operation. Implement a deny-all, permit-by-exception policy to allow the execution of only authorized software programs. | ||||
High Impact Implement automated mechanisms where feasible to maintain an up-to-date, complete, accurate, and readily available baseline configuration of the manufacturing system. Automated system support includes for example, documentation, notification, and management of the change control process on the manufacturing system. Review system changes to determine whether unauthorized changes have occurred. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | データセキュリティ(PR.DS) | PR.DS-8 | 低および中影響 なし | SI-7 |
高影響 重要と判断された製造システムのハードウェアに対する、許可されていない改ざんを検知するため、ハードウェアの完全性チェック(たとえば、改ざん検知テープやラベル、コンピューターポートの保護、電源投入時の自己診断など)を実装します。 製造システムのハードウェアに対する許可されていない改ざんの検知を、組織のインシデント対応能力に組み込みます。 | ||||
| 情報保護のプロセスと手順(PR.IP) | PR.IP-1 | 低影響 製造システムのベースライン構成を策定し、文書化し、維持します。 ベースライン構成には、たとえば、製造システムの構成要素に関する情報(ソフトウェアのライセンス情報、ソフトウェアのバージョン番号、HMIおよびその他のICS構成要素のアプリケーション、ソフトウェア、オペレーティングシステム)、オペレーティングシステムとアプリケーションの現在のバージョン番号とパッチ情報、構成設定/パラメーター、ネットワークトポロジー、およびシステムアーキテクチャ内でのそれらの構成要素の論理的な配置が含まれます。 製造システムを、不可欠な機能のみを提供するように構成します。 ベースライン構成を見直し、不要な機能を無効にします。 | ISA/IEC 62443-2-1:2009 4.3.4.3.2, ISA/IEC 62443-3-3:2013 SR 7.6 CM-2 CM-6 CM-7 CM-7(1) CM-2(1)(3) CM-7(2) CM-9 SC-24 CM-7(5) CM-2(2) CM-3(1) CM-5(1)(2) | |
中影響 システム構成要素の設置とアップグレードに不可欠な作業として、製造システムのベースライン構成を見直し、更新します。ロールバックに備えて、ベースライン構成の以前のバージョンを保持します。 ソフトウェアプログラムの使用制限を実装します。 製造システムの構成管理計画を策定します。 この計画には、たとえば、構成プロセス、役割、ライフサイクルの定義、構成品目、管理方法が含まれます。 システムの障害(または障害状態)が発生した際に、資産があらかじめ定められた運用モードを実現する状態に戻るよう、構成パラメーター、機能、既知の状態へのフェイル手順を定義します。 許可されたソフトウェアプログラムのみの実行を認めるため、すべて拒否し、例外のみ許可するポリシーを実装します。 | ||||
高影響 製造システムの最新で、完全で、正確で、すぐに利用できるベースライン構成を維持するため、実現可能な場合には自動化された仕組みを実装します。 自動化されたシステム支援には、たとえば、製造システムの変更管理プロセスの文書化、通知、管理が含まれます。 許可されていない変更が行われたかどうかを判断するため、システムの変更を見直します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Information Protection Processes and Procedures (PR.IP) | PR.IP-2 | Low Impact Manage the manufacturing system using a system development life cycle that includes security considerations. Include security requirements into the acquisition process of the manufacturing system and its components. | ISA/IEC 62443-2-1:2009 4.3.4.3.3 SA-3 SA-4 SA-4(1)(2) SA-8 SA-10 |
Moderate and High Impact Require the developer of the manufacturing system and system components to provide a description of the functional properties of security controls, and design and implementation information for security-relevant system interfaces. Apply security engineering principles into the specification, design, development, implementation, and modification of the manufacturing system. Implement configuration management and change control during the development of the manufacturing system and its components, and include flaw tracking and resolution, and security testing. | ||||
| PR.IP-3 | Low Impact Implement configuration change control for the manufacturing system and its components. Conduct security impact analyses in connection with change control reviews. | ISA/IEC 62443-2-1:2009 4.3.4.3.2 ISA/IEC 62443-3-3:2013 SR 7.6 CM-3 CM-4 CM-3(2) CM-3(1) CM-4(1) | ||
Moderate Impact Test, validate, and document changes to the manufacturing system before implementing the changes on the operational system. Review and authorize proposed configuration-controlled changes prior to implementing them on the manufacturing system. | ||||
High Impact Implement automated mechanisms where feasible to support the change control process. Conduct security impact analysis in a separate test environment before implementation into an operational environment for planned changes to the manufacturing system. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | 情報保護のプロセスと手順(PR.IP) | PR.IP-2 | 低影響 セキュリティの考慮事項を含むシステム開発ライフサイクルを用いて、製造システムを管理します。 製造システムとその構成要素の調達プロセスに、セキュリティ要件を含めます。 | ISA/IEC 62443-2-1:2009 4.3.4.3.3 SA-3 SA-4 SA-4(1)(2) SA-8 SA-10 |
中および高影響 製造システムおよびシステム構成要素の開発者に、セキュリティ管理策の機能的特性の記述と、セキュリティに関連するシステムインターフェースの設計および実装の情報を提供するよう求めます。 製造システムの仕様策定、設計、開発、実装、変更に、セキュリティ工学の原則を適用します。 製造システムとその構成要素の開発中に、構成管理と変更管理を実施し、欠陥の追跡と解決、およびセキュリティテストを含めます。 | ||||
| PR.IP-3 | 低影響 製造システムとその構成要素の構成変更管理を実装します。 変更管理のレビューに関連して、セキュリティ影響分析を実施します。 | ISA/IEC 62443-2-1:2009 4.3.4.3.2 ISA/IEC 62443-3-3:2013 SR 7.6 CM-3 CM-4 CM-3(2) CM-3(1) CM-4(1) | ||
中影響 製造システムへの変更を、運用システムに実装する前に、テストし、妥当性を確認し、文書化します。 構成管理の対象となる変更案を、製造システムに実装する前に、見直し、認可します。 | ||||
高影響 変更管理プロセスを支援するため、実現可能な場合には自動化された仕組みを実装します。 製造システムへの計画された変更については、運用環境に実装する前に、別個のテスト環境でセキュリティ影響分析を実施します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Information Protection Processes and Procedures (PR.IP) | PR.IP-4 | Low Impact Conduct and maintain backups for manufacturing system data. Manufacturing system data includes for example software, configurations and settings, documentation, system configuration data including computer configuration backups, application configuration backups, operational control limits, control bands and set points for pre-incident operation for all ICS programmable equipment | ISA/IEC 62443-2-1:2009 4.3.4.3.9 ISA/IEC 62443-3-3:2013 SR 7.3, 7.4 CP-9 CP-4 CP-9(1) CP-4(1) CP-6 CP-9(2) CP-9(3) |
Moderate Impact Verify the reliability and integrity of backups. Coordinate backup testing with organizational elements responsible for related plans. Establish a separate alternate storage site for system backups and ensure the same security safeguards are employed. | ||||
High Impact Include into contingency plan testing the conducting of restorations from backup data. Store critical manufacturing system backup information separately. | ||||
| PR.IP-5 | Low and Moderate Impact Define, implement, and enforce policy and regulations regarding emergency and safety systems, fire protection systems, and environment controls for the manufacturing system. Fire suppression mechanisms should take the manufacturing environment into account (e.g., water sprinkler systems could be hazardous in specific environments). | ISA/IEC 62443-2-1:2009 4.3.3.3.1 PE-Family PE-13(1)(2) | ||
High Impact Implement fire detection devices that activate and notify key personnel automatically in the event of a fire. | ||||
| PR.IP-6 | Low and Moderate Impact Ensure that manufacturing system data is destroyed according to policy. | ISA/IEC 62443-2-1:4.3.3.3.1 ISA/IEC 62443-3-3:2013 SR 4.2 MP-6 MP-6(1)(2)(3) | ||
High Impact Ensure that media sanitization actions are approved, tracked, documented, and verified. Test sanitation equipment and procedures. Apply nondestructive sanitization techniques to portable storage devices connecting to the manufacturing system. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | 情報保護のプロセスと手順(PR.IP) | PR.IP-4 | 低影響 製造システムのデータのバックアップを実施し、維持します。 製造システムのデータには、たとえば、ソフトウェア、構成と設定、文書、コンピューター構成のバックアップ、アプリケーション構成のバックアップ、インシデント前の運用に関するすべてのICSプログラマブル機器の運用制御限界値、制御帯域、設定値などのシステム構成データが含まれます。 | ISA/IEC 62443-2-1:2009 4.3.4.3.9 ISA/IEC 62443-3-3:2013 SR 7.3, 7.4 CP-9 CP-4 CP-9(1) CP-4(1) CP-6 CP-9(2) CP-9(3) |
中影響 バックアップの信頼性と完全性を検証します。 バックアップのテストを、関連する計画を担当する組織の部署と調整します。 システムのバックアップのために別個の代替保管場所を設け、同じセキュリティ保護対策が講じられるようにします。 | ||||
高影響 緊急時対応計画のテストに、バックアップデータからの復元の実施を含めます。 重要な製造システムのバックアップ情報を、別に保管します。 | ||||
| PR.IP-5 | 低および中影響 製造システムの緊急時システムおよび安全システム、防火システム、環境制御に関するポリシーと規則を定義し、実装し、施行します。 消火の仕組みは、製造環境を考慮すべきです(たとえば、スプリンクラー設備は、特定の環境では危険となる場合があります)。 | ISA/IEC 62443-2-1:2009 4.3.3.3.1 PE-Family PE-13(1)(2) | ||
高影響 火災が発生した場合に、自動的に作動して主要な要員に通知する火災検知デバイスを実装します。 | ||||
| PR.IP-6 | 低および中影響 製造システムのデータが、ポリシーに従って破棄されるようにします。 | ISA/IEC 62443-2-1:4.3.3.3.1 ISA/IEC 62443-3-3:2013 SR 4.2 MP-6 MP-6(1)(2)(3) | ||
高影響 媒体のサニタイズ措置が、承認され、追跡され、文書化され、検証されるようにします。サニタイズ用の機器と手順をテストします。 製造システムに接続する可搬型記憶装置には、非破壊のサニタイズ技法を適用します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Information Protection Processes and Procedures (PR.IP) | PR.IP-7 | Low Impact Incorporate improvements derived from the monitoring, measurements, assessments, and lessons learned into protection process revisions. Ensure that the security plan for the manufacturing system facilitates the review, testing, and continual improvement of the security protection processes. | ISA/IEC 62443-2-1:2009 4.4.3.1, 4.4.3.2, 4.4.3.3, 4.4.3.4, PM-6, CA-2, CA-7, SI-4, PL-2, PM-14 CA-2(1), CA-7(1) |
Moderate and High Impact Implement independent teams to assess the protection process. Independent teams, for example, may include internal or external impartial personnel. Impartiality implies that assessors are free from any perceived or actual conflicts of interest regarding the development, operation, or management of the manufacturing system under assessment or to the determination of security control effectiveness. | ||||
| PR.IP-8 | Low, Moderate and High Impact Collaborate and share information about manufacturing system related security incidents and mitigation measures with designated sharing partners. Implement automated mechanisms where feasible to assist in information collaboration. | AC-21 AC-21(1) | ||
| PR.IP-9 | Low Impact Develop and maintain response and recovery plans that identify essential functions and associated contingency requirements, as well as providing a roadmap for implementing incident response. Plans should incorporate recovery objectives, restoration priorities, metrics, contingency roles, personnel assignments and contact information. Address maintaining essential functions despite system disruption, and the eventual restoration of the manufacturing system. Define incident types, resources and management support needed to effectively maintain and mature the incident response and contingency capabilities. | ISA/IEC 62443-2-1:2009 4.3.2.5.3, CP-2 IR-8 CP-2(1) | ||
Moderate and High Impact Coordinate contingency plan development with stakeholders responsible for related plans. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | 情報保護のプロセスと手順(PR.IP) | PR.IP-7 | 低影響 監視、測定、評価、教訓から得られた改善を、保護プロセスの改訂に取り入れます。 製造システムのセキュリティ計画が、セキュリティ保護プロセスの見直し、テスト、継続的な改善を促進するようにします。 | ISA/IEC 62443-2-1:2009 4.4.3.1, 4.4.3.2, 4.4.3.3, 4.4.3.4, PM-6, CA-2, CA-7, SI-4, PL-2, PM-14 CA-2(1), CA-7(1) |
中および高影響 保護プロセスを評価する独立したチームを設けます。 独立したチームには、たとえば、内部または外部の公平な要員が含まれる場合があります。 公平性とは、評価者が、評価対象の製造システムの開発、運用、管理に関して、またはセキュリティ管理策の有効性の判定に関して、認識される、または実際の利益相反を持たないことを意味します。 | ||||
| PR.IP-8 | 低・中・高影響 製造システムに関連するセキュリティインシデントと緩和策について、指定された共有先のパートナーと協力し、情報を共有します。 情報の連携を支援するため、実現可能な場合には自動化された仕組みを実装します。 | AC-21 AC-21(1) | ||
| PR.IP-9 | 低影響 不可欠な機能と関連する緊急時対応要件を特定し、インシデント対応を実装するためのロードマップを示す、対応計画と復旧計画を策定し、維持します。計画には、復旧目標、復元の優先順位、指標、緊急時の役割、要員の割り当て、連絡先情報を含めるべきです。システムの中断にもかかわらず不可欠な機能を維持すること、および製造システムを最終的に復元することに対処します。 インシデント対応能力と緊急時対応能力を効果的に維持し、成熟させるために必要な、インシデントの種類、リソース、経営層の支援を定義します。 | ISA/IEC 62443-2-1:2009 4.3.2.5.3, CP-2 IR-8 CP-2(1) | ||
中および高影響 緊急時対応計画の策定を、関連する計画を担当するステークホルダーと調整します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Information Protection Processes and Procedures (PR.IP) | PR.IP-10 | Low Impact Review response and recovery plans to determine the effectiveness of the plans, and the readiness to execute the plans. | ISA/IEC 62443-2-1:2009 4.3.2.5.7 ISA/IEC 62443-3-3:2013 SR 3.3 CP-4, PM-14 CP-4(1) IR-3(2) |
Moderate and High Impact Test response and recovery plans to determine the effectiveness of the plans, and the readiness to execute the plans. Coordinate testing of response and recovery plans with relevant stakeholders. Related plans include, for example, Business Continuity Plans, Disaster Recovery Plans, Continuity of Operations Plans, Crisis Communications Plans, Critical Infrastructure Plans, Cyber Incident Response Plans, and Occupant Emergency Plans. | ||||
| PR.IP-11 | Low, Moderate and High Impact Develop and maintain a personnel security program for the manufacturing system. Personnel security program should include policy, position risk designations, personnel screening, terminations and transfers, access agreements, third-party roles and responsibilities, and personnel sanctions. | ISA/IEC 62443-2-1:2009 4.3.3.2.1 PS- Family | ||
| PR.IP-12 | Low Impact Establish and maintain a process that allows continuous review of vulnerabilities and defines strategies to mitigate them. | RA-3, SI-2 RA-5(5) RA-5(4) | ||
Moderate Impact Restrict access to privileged vulnerability data. | ||||
High Impact Identify where manufacturing system vulnerabilities may be exposed to adversaries. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | 情報保護のプロセスと手順(PR.IP) | PR.IP-10 | 低影響 対応計画と復旧計画の有効性と、計画を実行する準備状況を判断するため、計画を見直します。 | ISA/IEC 62443-2-1:2009 4.3.2.5.7 ISA/IEC 62443-3-3:2013 SR 3.3 CP-4, PM-14 CP-4(1) IR-3(2) |
中および高影響 対応計画と復旧計画の有効性と、計画を実行する準備状況を判断するため、計画をテストします。 対応計画と復旧計画のテストを、関連するステークホルダーと調整します。 関連する計画には、たとえば、事業継続計画、災害復旧計画、業務継続計画、危機コミュニケーション計画、重要インフラ計画、サイバーインシデント対応計画、居住者緊急時計画が含まれます。 | ||||
| PR.IP-11 | 低・中・高影響 製造システムの要員セキュリティプログラムを策定し、維持します。要員セキュリティプログラムには、ポリシー、職位のリスク指定、要員の審査、退職と異動、アクセスに関する合意書、第三者の役割と責任、要員に対する制裁を含めるべきです。 | ISA/IEC 62443-2-1:2009 4.3.3.2.1 PS- Family | ||
| PR.IP-12 | 低影響 脆弱性を継続的に見直し、その緩和戦略を定義するプロセスを確立し、維持します。 | RA-3, SI-2 RA-5(5) RA-5(4) | ||
中影響 特権的な脆弱性データへのアクセスを制限します。 | ||||
高影響 製造システムの脆弱性が攻撃者にさらされる可能性のある箇所を特定します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Maintenance (PR.MA) | PR.MA-1 | Low Impact Schedule, perform, document and review records of maintenance and repairs on manufacturing system components. Establish a process for maintenance personnel authorization, and escort non-authorized maintenance personnel. Verify impacted security controls following maintenance or repairs. | ISA/IEC 62443-2-1:2009 4.3.3.3.7 MA-2 MA-5 MA-2 MA-3 MA-6 MA-3(1) MA-3(2) MA-2(2) MA-3(3) |
Moderate Impact Enforce approval requirements, control, and monitoring of maintenance tools for use on the manufacturing system. Maintenance tools can include, for example, hardware/software diagnostic test equipment, hardware/software packet sniffers and laptops. Perform preventative maintenance at defined intervals. Inspect maintenance tools brought into the facility. Scan maintenance tools and portable storage devices for malicious code before they are used on the manufacturing system. | ||||
High Impact Implement automated mechanisms where feasible to schedule, conduct, and document maintenance and repairs; and to produce records of maintenance activity. Prevent the unauthorized removal of maintenance equipment containing manufacturing system information. | ||||
| PR.MA-2 | Low and Moderate Impact Enforce approval requirements, control, and monitoring, of remote maintenance activities. Implement strong authenticators, record keeping, and session termination for remote maintenance. | ISA/IEC 62443-2-1:2009 4.3.3.6.5 MA-4 MA-4(3) | ||
High Impact Require that diagnostic services pertaining to remote maintenance be performed from a system that implements a security capability comparable to the capability implemented on the manufacturing system. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | 保守(PR.MA) | PR.MA-1 | 低影響 製造システムの構成要素の保守と修理について、スケジュールを立て、実施し、文書化し、その記録を見直します。 保守要員の認可プロセスを確立し、認可されていない保守要員に付き添います。 保守または修理の後、影響を受けたセキュリティ管理策を検証します。 | ISA/IEC 62443-2-1:2009 4.3.3.3.7 MA-2 MA-5 MA-2 MA-3 MA-6 MA-3(1) MA-3(2) MA-2(2) MA-3(3) |
中影響 製造システムで使用する保守ツールについて、承認要件、制御、監視を徹底します。保守ツールには、たとえば、ハードウェア/ソフトウェアの診断テスト機器、ハードウェア/ソフトウェアのパケットスニファー、ノートパソコンが含まれる場合があります。 予防保守を、定められた間隔で実施します。 施設に持ち込まれた保守ツールを検査します。 保守ツールおよび可搬型記憶装置は、製造システムで使用する前に、悪意のあるコードがないかスキャンします。 | ||||
高影響 保守と修理のスケジュール設定、実施、文書化、および保守活動の記録の作成のために、実現可能な場合には自動化された仕組みを実装します。 製造システムの情報を含む保守用機器の許可されていない持ち出しを防止します。 | ||||
| PR.MA-2 | 低および中影響 リモート保守活動について、承認要件、制御、監視を徹底します。 リモート保守のために、強力な認証器、記録の保持、セッションの終了を実装します。 | ISA/IEC 62443-2-1:2009 4.3.3.6.5 MA-4 MA-4(3) | ||
高影響 リモート保守に関する診断サービスを、製造システムに実装されている能力と同等のセキュリティ能力を実装したシステムから実施することを求めます。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Protective Technology (PR.PT) | PR.PT-1 | Low Impact Generate audit records containing information that establishes what type of event occurred, when the event occurred, where the event occurred, the source of the event, the outcome of the event, and the identity of any individuals or manufacturing components associated with the event. Generate time stamps from an internal system clock that is mapped to Coordinated Universal Time (UTC) or Greenwich Mean Time (GMT). | ISA/IEC 62443-2-1:2009 4.3.3.3.9, ISA/IEC 62443-3-3:2013 SR 2.8, AU-3 AU-5 AU-8 AU-5 AU-2(3) AU-6(1) AU-7(1) AU-6(6) AU-12(1) AU-12(3) |
Moderate Impact Ensure that audit processing failures on the manufacturing system generate alerts and trigger defined responses. Review and update audit events. Implement automated mechanisms to integrate audit review, analysis, and reporting. Compare and synchronize the internal system clocks to an authoritative time source. Authoritative time sources include for example, an internal Network Time Protocol (NTP) server, radio clock, atomic clock, GPS time source. | ||||
High Impact Integrate analysis of audit records with physical access monitoring. Conduct time correlation of audit records. Enable authorized individuals to extend audit capabilities when required by events. | ||||
| PR.PT-2 | Low Impact Implement safeguards to restrict the use of portable storage devices. | ISA/IEC 62443-3-3:2013 SR 2.3 MP-2 MP-4 MP-7 | ||
Moderate and High Impact Protect and control portable storage devices containing manufacturing system data while in transit and in storage. Scan all portable storage devices for malicious code before they are used on the manufacturing system | ||||
| PR.PT-3 | Low Impact Configure the manufacturing system to provide only essential capabilities. | ISA/IEC 62443-2-1:2009 4.3.3.5.1, ISA/IEC 62443-3-3:2013 SR 1.1, SR AC-3 CM-7(1) CM-7(5) | ||
Moderate and High Impact Disable defined functions, ports, protocols, and services within the manufacturing system deemed to be unnecessary. Implement technical safeguards to enforce a deny-all, permit-by-exception policy to only allow the execution of authorized software programs. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | 保護技術(PR.PT) | PR.PT-1 | 低影響 発生したイベントの種類、イベントが発生した日時と場所、イベントの発生源、イベントの結果、およびイベントに関連する個人または製造構成要素の識別情報を確定する情報を含む監査記録を生成します。 協定世界時(UTC)またはグリニッジ標準時(GMT)に対応付けられた内部システムクロックから、タイムスタンプを生成します。 | ISA/IEC 62443-2-1:2009 4.3.3.3.9, ISA/IEC 62443-3-3:2013 SR 2.8, AU-3 AU-5 AU-8 AU-5 AU-2(3) AU-6(1) AU-7(1) AU-6(6) AU-12(1) AU-12(3) |
中影響 製造システムでの監査処理の失敗がアラートを生成し、定められた対応を開始するようにします。 監査イベントを見直し、更新します。 監査のレビュー、分析、報告を統合するための自動化された仕組みを実装します。 内部システムクロックを、信頼できる時刻源と比較し、同期します。信頼できる時刻源には、たとえば、内部のネットワークタイムプロトコル(NTP)サーバー、電波時計、原子時計、GPS時刻源が含まれます。 | ||||
高影響 監査記録の分析を、物理的アクセスの監視と統合します。 監査記録の時刻相関を実施します。 イベントによって必要となった場合に、許可された個人が監査能力を拡張できるようにします。 | ||||
| PR.PT-2 | 低影響 可搬型記憶装置の使用を制限する保護対策を実装します。 | ISA/IEC 62443-3-3:2013 SR 2.3 MP-2 MP-4 MP-7 | ||
中および高影響 製造システムのデータを含む可搬型記憶装置を、伝送時および保管時に保護し、管理します。すべての可搬型記憶装置は、製造システムで使用する前に、悪意のあるコードがないかスキャンします | ||||
| PR.PT-3 | 低影響 製造システムを、不可欠な機能のみを提供するように構成します。 | ISA/IEC 62443-2-1:2009 4.3.3.5.1, ISA/IEC 62443-3-3:2013 SR 1.1, SR AC-3 CM-7(1) CM-7(5) | ||
中および高影響 製造システム内で不要と判断された、定義済みの機能、ポート、プロトコル、サービスを無効にします。 許可されたソフトウェアプログラムのみの実行を認めるため、すべて拒否し、例外のみ許可するポリシーを適用する技術的な保護対策を実装します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| PROTECT | Protective Technology (PR.PT) | PR.PT-4 | Low Impact Monitor and control communications at the external boundary and at key internal boundaries within the manufacturing system. | ISA/IEC 62443-3-3:2013 SR 3.1, SR SC-7 AC-4 SC-7(3) SC-7(4) |
Moderate and High Impact Control the flow of information within the manufacturing system and between interconnected systems. Information flow may be supported, for example, by labeling or coloring physical connectors as an aid to manual hookup. Inspection of message content may enforce information flow policy. For example, a message containing a command to an actuator may not be permitted to flow between the control network and any other network. Physical addresses (e.g., a serial port) may be implicitly or explicitly associated with labels or attributes (e.g., hardware I/O address). Manual methods are typically static. Label or attribute policy mechanisms may be implemented in hardware, firmware, and software that controls or has device access, such as device drivers and communications controllers. Limit external connections to the system. Manage the interface for external telecommunication services by establishing a traffic flow policy, protecting the confidentiality and integrity of the information being transmitted, reviewing and documenting each exception to the traffic flow policy. | ||||
| PR.PT-5 | Low Impact None | PL-8 PL-8 | ||
Moderate Impact Implement IT resiliency mechanisms to support normal and adverse manufacturing situations. | ||||
High Impact Implement OT resiliency mechanisms to support normal and adverse manufacturing situations. | ||||
| DETECT | Anomalies and Events (DE.AE) | DE.AE-1 | Low, Moderate and High Impact Ensure that a baseline of network operations and expected data flows for the manufacturing system is developed, documented, and maintained to detect events. | ISA/IEC 62443-2-1:2009 4.4.3.3 CM-2 |
| DE.AE-2 | Low Impact Review and analyze detected events within the manufacturing system to understand attack targets and methods. | ISA/IEC 62443-2-1:2009 4.3.4.5.6, ISA/IEC 62443-3-3:2013 SR 2.8, 2.9 AU-6, IR-4 AU-6(1) IR-4(1) | ||
Moderate and High Impact Implement automated mechanisms where feasible to review and analyze detected events within the manufacturing system. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 防御(PROTECT) | 保護技術(PR.PT) | PR.PT-4 | 低影響 製造システムの外部境界と内部の主要な境界における通信を監視し、制御します。 | ISA/IEC 62443-3-3:2013 SR 3.1, SR SC-7 AC-4 SC-7(3) SC-7(4) |
中および高影響 製造システム内、および相互接続されたシステム間の情報の流れを制御します。 情報の流れは、たとえば、手動での接続を補助するため、物理コネクターにラベルを付けたり色分けしたりすることで支援できます。メッセージ内容の検査によって、情報フローのポリシーを適用することもできます。たとえば、アクチュエーターへのコマンドを含むメッセージは、制御ネットワークとその他のネットワークとの間を流れることが許可されない場合があります。物理アドレス(たとえば、シリアルポート)は、ラベルや属性(たとえば、ハードウェアのI/ システムへの外部接続を制限します。 トラフィックフローのポリシーの確立、伝送される情報の機密性と完全性の保護、トラフィックフローのポリシーに対する各例外の見直しと文書化によって、外部通信サービスのインターフェースを管理します。 | ||||
| PR.PT-5 | 低影響 なし | PL-8 PL-8 | ||
中影響 通常時および異常時の製造状況を支えるため、ITのレジリエンスの仕組みを実装します。 | ||||
高影響 通常時および異常時の製造状況を支えるため、OTのレジリエンスの仕組みを実装します。 | ||||
| 検知(DETECT) | 異常とイベント(DE.AE) | DE.AE-1 | 低・中・高影響 イベントを検知するため、製造システムのネットワーク運用と想定されるデータフローのベースラインが策定され、文書化され、維持されるようにします。 | ISA/IEC 62443-2-1:2009 4.4.3.3 CM-2 |
| DE.AE-2 | 低影響 攻撃の標的と手法を理解するため、製造システム内で検知されたイベントを見直し、分析します。 | ISA/IEC 62443-2-1:2009 4.3.4.5.6, ISA/IEC 62443-3-3:2013 SR 2.8, 2.9 AU-6, IR-4 AU-6(1) IR-4(1) | ||
中および高影響 製造システム内で検知されたイベントを見直し、分析するため、実現可能な場合には自動化された仕組みを実装します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| DETECT | Anomalies and Events (DE.AE) | DE.AE-3 | Low and Moderate Impact Ensure that event data is compiled and correlated across the manufacturing system using various sources such as event reports, audit monitoring, network monitoring, physical access monitoring, and user/administrator reports. | ISA/IEC 62443-3-3:2013 SR 6.1 IR-5 AU-6(5)(6) AU-12(1) |
High Impact Integrate analysis of events where feasible with the analysis of vulnerability scanning information; performance data; manufacturing system monitoring, and facility monitoring to further enhance the ability to identify inappropriate or unusual activity. | ||||
| DE.AE-4 | Low Impact Determine negative impacts to manufacturing operations, assets, and individuals resulting from detected events, and correlate with risk assessment outcomes. | RA-3 IR-4(1), SI-4(2) IR-4(4) | ||
Moderate Impact Implement automated mechanisms to support impact analysis. | ||||
High Impact Correlate detected event information and responses to achieve perspective on event impact across the organization. | ||||
| DE.AE-5 | Low Impact Define incident alert thresholds for the manufacturing system. | ISA/IEC 62443-2-1:2009 4.2.3.10 IR-4, IR-5, AU-2, AU-3, IR-8 IR-4(1), IR-5(1) | ||
Moderate and High Impact Implement automated mechanisms where feasible to assist in the identification of security alert thresholds. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 検知(DETECT) | 異常とイベント(DE.AE) | DE.AE-3 | 低および中影響 イベントレポート、監査の監視、ネットワークの監視、物理的アクセスの監視、利用者/管理者の報告など、さまざまな情報源を用いて、イベントデータが製造システム全体にわたって収集され、相関付けられるようにします。 | ISA/IEC 62443-3-3:2013 SR 6.1 IR-5 AU-6(5)(6) AU-12(1) |
高影響 不適切な、または異常な活動を特定する能力をさらに高めるため、可能な場合には、イベントの分析を、脆弱性スキャンの情報、性能データ、製造システムの監視、施設の監視の分析と統合します。 | ||||
| DE.AE-4 | 低影響 検知されたイベントによって製造運用、資産、個人に生じる悪影響を判断し、リスクアセスメントの結果と相関付けます。 | RA-3 IR-4(1), SI-4(2) IR-4(4) | ||
中影響 影響分析を支援するための自動化された仕組みを実装します。 | ||||
高影響 組織全体でのイベントの影響についての見通しを得るため、検知されたイベントの情報と対応を相関付けます。 | ||||
| DE.AE-5 | 低影響 製造システムのインシデントアラートのしきい値を定義します。 | ISA/IEC 62443-2-1:2009 4.2.3.10 IR-4, IR-5, AU-2, AU-3, IR-8 IR-4(1), IR-5(1) | ||
中および高影響 セキュリティアラートのしきい値の特定を支援するため、実現可能な場合には自動化された仕組みを実装します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| DETECT | Security Continuous Monitoring (DE.CM) | DE.CM-1 | Low Impact Conduct ongoing security status monitoring of the manufacturing system network to detect defined cybersecurity events and indicators of potential cybersecurity events. Detect unauthorized local, network, and remote connections, and identify unauthorized use of the manufacturing system. Generate audit records for defined cybersecurity events. Monitor network communications at the external boundary of the system and at key internal boundaries within the system. Heighten system monitoring activity whenever there is an indication of increased risk. | ISA/IEC 62443-3-3:2013 SR 6.2 CA-7 AC-2 SI-4 AU-12 SC-7, SI-4(4) SI-4 AC-2 (1)(2)(3)(4), SI-4(2) SI-4(5) AC-2(12) |
Moderate Impact Implement automated mechanisms to support detection of cybersecurity events. Generate system alerts when indications of compromise or potential compromise occur. | ||||
High Impact Monitor for and report atypical usage of the manufacturing system. | ||||
| DE.CM-2 | Low Impact Conduct ongoing security status monitoring of the manufacturing system facility to detect physical security incidents. | ISA/IEC 62443-2-1:2009 4.3.3.3.8 CA-7, PE-6, PE-3 CA-7(1) PE-6(1), PE-6(4) PE-3(1) | ||
Moderate and High Impact Implement independent teams to monitor the security of the physical environment. Monitor physical intrusion alarms and surveillance equipment. Monitor physical access to the manufacturing system and devices in addition to the facility. | ||||
| DE.CM-3 | Low, Moderate and High Impact Conduct security status monitoring of personnel activity associated with the manufacturing system. Enforce software usage and installation restrictions. | ISA/IEC 62443-3-3:2013 SR 6.2 CA-7 CM-10, CM-11 |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 検知(DETECT) | セキュリティの継続的監視(DE.CM) | DE.CM-1 | 低影響 定義されたサイバーセキュリティイベントと、潜在的なサイバーセキュリティイベントの指標を検知するため、製造システムのネットワークのセキュリティ状態を継続的に監視します。 許可されていないローカル接続、ネットワーク接続、リモート接続を検知し、製造システムの許可されていない使用を特定します。 定義されたサイバーセキュリティイベントについて、監査記録を生成します。 システムの外部境界と、システム内の主要な内部境界で、ネットワーク通信を監視します。 リスクが高まっている兆候があるときはいつでも、システムの監視活動を強化します。 | ISA/IEC 62443-3-3:2013 SR 6.2 CA-7 AC-2 SI-4 AU-12 SC-7, SI-4(4) SI-4 AC-2 (1)(2)(3)(4), SI-4(2) SI-4(5) AC-2(12) |
中影響 サイバーセキュリティイベントの検知を支援するための、自動化された仕組みを実装します。 侵害または侵害の可能性の兆候が生じたときに、システムアラートを生成します。 | ||||
高影響 製造システムの通常とは異なる使用を監視し、報告します。 | ||||
| DE.CM-2 | 低影響 物理的なセキュリティインシデントを検知するため、製造システムの施設のセキュリティ状態を継続的に監視します。 | ISA/IEC 62443-2-1:2009 4.3.3.3.8 CA-7, PE-6, PE-3 CA-7(1) PE-6(1), PE-6(4) PE-3(1) | ||
中および高影響 物理環境のセキュリティを監視する独立したチームを設けます。 物理的な侵入警報と監視機器を監視します。 施設に加えて、製造システムとデバイスへの物理的なアクセスを監視します。 | ||||
| DE.CM-3 | 低・中・高影響 製造システムに関連する要員の活動について、セキュリティ状態の監視を実施します。 ソフトウェアの使用とインストールの制限を適用します。 | ISA/IEC 62443-3-3:2013 SR 6.2 CA-7 CM-10, CM-11 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| DETECT | Security Continuous Monitoring (DE.CM) | DE.CM-4 | Low Impact Deploy malicious code protection mechanisms throughout the manufacturing system where safe and feasible to detect and eradicate malicious code. Update malicious code protection mechanisms whenever new releases are available in accordance with the configuration management policy and procedures for the manufacturing system. | ISA/IEC 62443-2-1:2009 4.3.4.3.8 ISA/IEC 62443-3-3:2013 SR 3.2 SI-3 SI-3d SI-3(2) |
Moderate and High Impact Manage for false positives during malicious code detection and eradication. Automatically update malicious code protection mechanisms where safe and feasible. | ||||
| DE.CM-5 | Low Impact None | ISA/IEC 62443-3-3:2013 SR 2.4 SC-18 | ||
Moderate and High Impact Define acceptable and detect unacceptable mobile code and mobile code technologies. Mobile code technologies include, for example, Java, JavaScript, ActiveX, Postscript, PDF, Shockwave movies, Flash animations, and VBScript. Enforce usage restrictions and establish implementation guidance for acceptable mobile code and mobile code technologies for use with the manufacturing system. The use of mobile code technologies is determined after careful consideration and after verification that it does not adversely impact the operational performance of the manufacturing system. | ||||
| DE.CM-6 | Low Moderate and High Impact Conduct ongoing security status monitoring of external service provider activity on the manufacturing system. Detect defined cybersecurity events and indicators of potential cybersecurity events from external service providers. Monitor compliance of external providers with personnel security policies and procedures, and contract security requirements. | CA-7 SI-4 PS-7, SA-4, SA-9, MA-5 | ||
| DE.CM-7 | Low Impact Conduct ongoing security status monitoring on the manufacturing system for unauthorized personnel, connections, devices, access points, and software. Monitor for system inventory discrepancies. | CA-7 CM-8 SI-4 CM-3 | ||
Moderate and High Impact Deploy monitoring devices strategically within the manufacturing system to collect essential information to detect specific events of interest. Monitor for unauthorized configuration changes to the manufacturing system. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 検知(DETECT) | セキュリティの継続的監視(DE.CM) | DE.CM-4 | 低影響 悪意のあるコードを検知して駆除するため、安全かつ実現可能な場合には、製造システム全体に悪意のあるコード対策の仕組みを展開します。 新しいリリースが利用可能になったときはいつでも、製造システムの構成管理のポリシーおよび手順に従って、悪意のあるコード対策の仕組みを更新します。 | ISA/IEC 62443-2-1:2009 4.3.4.3.8 ISA/IEC 62443-3-3:2013 SR 3.2 SI-3 SI-3d SI-3(2) |
中および高影響 悪意のあるコードの検知と駆除における誤検知を管理します。 安全かつ実現可能な場合には、悪意のあるコード対策の仕組みを自動的に更新します。 | ||||
| DE.CM-5 | 低影響 なし | ISA/IEC 62443-3-3:2013 SR 2.4 SC-18 | ||
中および高影響 許容できるモバイルコードおよびモバイルコード技術を定義し、許容できないものを検知します。 モバイルコード技術には、たとえば、Java、JavaScript、ActiveX、Postscript、PDF、Shockwaveムービー、Flashアニメーション、VBScriptが含まれます。 製造システムで使用することが許容されるモバイルコードおよびモバイルコード技術について、使用上の制限を適用し、実装の指針を確立します。 モバイルコード技術の使用は、慎重に検討し、製造システムの運用性能に悪影響を与えないことを検証したうえで決定します。 | ||||
| DE.CM-6 | 低・中・高影響 製造システム上での外部サービスプロバイダーの活動について、セキュリティ状態の継続的な監視を実施します。 外部サービスプロバイダーによる、定義されたサイバーセキュリティイベントと、潜在的なサイバーセキュリティイベントの指標を検知します。 外部プロバイダーが、要員セキュリティのポリシーおよび手順、ならびに契約上のセキュリティ要件を遵守しているかを監視します。 | CA-7 SI-4 PS-7, SA-4, SA-9, MA-5 | ||
| DE.CM-7 | 低影響 許可されていない要員、接続、デバイス、アクセスポイント、ソフトウェアについて、製造システムのセキュリティ状態を継続的に監視します。 システムの目録との不一致を監視します。 | CA-7 CM-8 SI-4 CM-3 | ||
中および高影響 対象とする特定のイベントを検知するために必要不可欠な情報を収集するため、製造システム内の戦略的な箇所に監視デバイスを配置します。 製造システムに対する、許可されていない構成変更を監視します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| DETECT | Security Continuous Monitoring (DE.CM) | DE.CM-8 | Low, Moderate and High Impact Conduct vulnerability scans on the manufacturing system where safe and feasible. Include analysis, remediation, and information sharing in the vulnerability scanning process. Implement control system-specific vulnerability scanning tools and techniques where safe and feasible. Active vulnerability scanning, which introduces network traffic, is used with care on manufacturing systems to ensure that system functions are not adversely impacted by the scanning process. | ISA/IEC 62443-2-1:2009 4.2.3.1 RA-5 |
| Detection Processes (DE.DP) | DE.DP-1 | Low, Moderate and High Impact Define roles and responsibilities for detection activities on the manufacturing system and ensure accountability. | ISA/IEC 62443-2-1:2009 4.4.3.1 CA-2, CA-7, PM-14 | |
| DE.DP-2 | Low, Moderate and High Impact Conduct detection activities in accordance with applicable federal and state laws, industry regulations and standards, policies, and other applicable requirements. | ISA/IEC 62443-2-1:2009 4.4.3.2 CA-2 | ||
| DE.DP-3 | Low, Moderate and High Impact Validate that event detection processes are operating as intended. | ISA/IEC 62443-2-1:2009 4.4.3.2 ISA/IEC 62443-3-3:2013 SR 3.3 PM-14 | ||
| DE.DP-4 | Low Impact Communicate event detection information to defined personnel. Event detection information includes for example, alerts on atypical account usage, unauthorized remote access, wireless connectivity, mobile device connection, altered configuration settings, contrasting system component inventory, use of maintenance tools and nonlocal maintenance, physical access, temperature and humidity, equipment delivery and removal, communications at the information system boundaries, use of mobile code, use of Voice over Internet Protocol (VoIP), and malware disclosure. | ISA/IEC 62443-2-1:2009 4.3.4.5.9 ISA/IEC 62443-3-3:2013 SR 6.1 AU-6 SI-4 AU-6(1) SI-4(5) | ||
Moderate and High Impact Implement automated mechanisms and system generated alerts to support event detection communication. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 検知(DETECT) | セキュリティの継続的監視(DE.CM) | DE.CM-8 | 低・中・高影響 安全かつ実現可能な場合には、製造システムの脆弱性スキャンを実施します。脆弱性スキャンのプロセスに、分析、是正、情報共有を含めます。 安全かつ実現可能な場合には、制御システムに固有の脆弱性スキャンのツールと技法を実装します。 ネットワークトラフィックを発生させるアクティブな脆弱性スキャンは、スキャンのプロセスによってシステムの機能に悪影響が及ばないよう、製造システムでは注意して使用します。 | ISA/IEC 62443-2-1:2009 4.2.3.1 RA-5 |
| 検知プロセス(DE.DP) | DE.DP-1 | 低・中・高影響 製造システムにおける検知活動の役割と責任を定義し、説明責任を確実にします。 | ISA/IEC 62443-2-1:2009 4.4.3.1 CA-2, CA-7, PM-14 | |
| DE.DP-2 | 低・中・高影響 適用される連邦法および州法、業界の規則および標準、ポリシー、その他の適用される要件に従って、検知活動を実施します。 | ISA/IEC 62443-2-1:2009 4.4.3.2 CA-2 | ||
| DE.DP-3 | 低・中・高影響 イベント検知プロセスが意図したとおりに動作していることを検証します。 | ISA/IEC 62443-2-1:2009 4.4.3.2 ISA/IEC 62443-3-3:2013 SR 3.3 PM-14 | ||
| DE.DP-4 | 低影響 イベント検知の情報を、定められた要員に伝達します。 イベント検知の情報には、たとえば、通常とは異なるアカウントの使用、許可されていないリモートアクセス、無線接続、モバイルデバイスの接続、変更された構成設定、システム構成要素の目録との相違、保守ツールおよび非ローカル保守の使用、物理的アクセス、温度と湿度、機器の搬入と搬出、情報システムの境界での通信、モバイルコードの使用、Voice over Internet Protocol(VoIP)の使用、マルウェアの開示に関するアラートが含まれます。 | ISA/IEC 62443-2-1:2009 4.3.4.5.9 ISA/IEC 62443-3-3:2013 SR 6.1 AU-6 SI-4 AU-6(1) SI-4(5) | ||
中および高影響 イベント検知の伝達を支援するため、自動化された仕組みとシステムが生成するアラートを実装します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| DETECT | Detection Processes (DE.DP) | DE.DP-5 | Low Impact Incorporate improvements derived from the monitoring, measurements, assessments, and lessons learned into detection process revisions. Ensure the security plan for the manufacturing system provides for the review, testing, and continual improvement of the security detection processes. | ISA/IEC 62443-2-1:2009 4.4.3.4 CA-2, CA-7, SI-4 PL-2, PM-14 CA-2(1), CA-7(1) CA-2(7) |
Moderate Impact Implement independent teams to assess the detection process. | ||||
High Impact Conduct specialized assessments including in-depth monitoring, vulnerability scanning, malicious user testing, insider threat assessment, performance/load testing, and verification and validation testing on the manufacturing system. | ||||
| RESPOND | Response Planning (RS.RP) | RS.RP-1 | Low, Moderate and High Impact Execute the response plan during or after a cybersecurity event on the manufacturing system. | ISA/IEC 62443-2-1:2009 4.3.4.5.1 IR-8, IR-4 |
| Communications (RS.CO) | RS.CO-1 | Low, Moderate and High Impact Ensure personnel understand objectives, restoration priorities, task sequences and assignment responsibilities for event response. | ISA/IEC 62443-2-1:2009 4.3.4.5.2 CP-2, CP-3, IR-8 | |
| RS.CO-2 | Low Impact Implement prompt reporting to appropriate stakeholders for cybersecurity events on the manufacturing system. Ensure that cybersecurity events on the manufacturing system are reported consistent with the response plan. | ISA/IEC 62443-2-1:2009 4.3.4.5.5 IR-6 AU-6 IR-6(1) | ||
Moderate and High Impact Implement automated mechanisms to assist in the reporting of cybersecurity events. | ||||
| RS.CO-3 | Low, Moderate and High Impact Share cybersecurity incident information with relevant stakeholders per the response plan. | ISA/IEC 62443-2-1:2009 4.3.4.5.2 CA-2, CA-7, CP-2f | ||
| RS.CO-4 | Low Impact Coordinate cybersecurity incident response actions with all relevant stakeholders. Stakeholders for incident response include for example, mission/business owners, manufacturing system owners, integrators, vendors, human resources offices, physical and personnel security offices, legal departments, operations personnel, and procurement offices. | ISA/IEC 62443-2-1:2009 4.3.4.5.5 CP-2, CP-2(1), IR-4 IR-4(1) | ||
Moderate and High Impact Implement automated mechanisms to support stakeholder coordination. |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 検知(DETECT) | 検知プロセス(DE.DP) | DE.DP-5 | 低影響 監視、測定、評価、教訓から得られた改善を、検知プロセスの改訂に取り入れます。 製造システムのセキュリティ計画が、セキュリティ検知プロセスの見直し、テスト、継続的な改善を規定するようにします。 | ISA/IEC 62443-2-1:2009 4.4.3.4 CA-2, CA-7, SI-4 PL-2, PM-14 CA-2(1), CA-7(1) CA-2(7) |
中影響 検知プロセスを評価する独立したチームを設けます。 | ||||
高影響 詳細な監視、脆弱性スキャン、悪意のある利用者によるテスト、内部脅威の評価、性能/負荷テスト、検証および妥当性確認テストを含む、製造システムの専門的な評価を実施します。 | ||||
| 対応(RESPOND) | 対応計画(RS.RP) | RS.RP-1 | 低・中・高影響 製造システムでサイバーセキュリティイベントが発生している間または発生した後に、対応計画を実行します。 | ISA/IEC 62443-2-1:2009 4.3.4.5.1 IR-8, IR-4 |
| コミュニケーション(RS.CO) | RS.CO-1 | 低・中・高影響 要員が、イベント対応の目標、復元の優先順位、作業の順序、割り当てられた責任を理解していることを確実にします。 | ISA/IEC 62443-2-1:2009 4.3.4.5.2 CP-2, CP-3, IR-8 | |
| RS.CO-2 | 低影響 製造システムでのサイバーセキュリティイベントについて、適切なステークホルダーへ速やかに報告する仕組みを実装します。 製造システムでのサイバーセキュリティイベントが、対応計画に沿って報告されるようにします。 | ISA/IEC 62443-2-1:2009 4.3.4.5.5 IR-6 AU-6 IR-6(1) | ||
中および高影響 サイバーセキュリティイベントの報告を支援するための、自動化された仕組みを実装します。 | ||||
| RS.CO-3 | 低・中・高影響 対応計画に従って、サイバーセキュリティインシデントの情報を関連するステークホルダーと共有します。 | ISA/IEC 62443-2-1:2009 4.3.4.5.2 CA-2, CA-7, CP-2f | ||
| RS.CO-4 | 低影響 サイバーセキュリティインシデント対応の措置を、関連するすべてのステークホルダーと調整します。 インシデント対応のステークホルダーには、たとえば、ミッション/事業の所有者、製造システムの所有者、インテグレーター、ベンダー、人事部門、物理セキュリティおよび要員セキュリティ部門、法務部門、運用要員、調達部門が含まれます。 | ISA/IEC 62443-2-1:2009 4.3.4.5.5 CP-2, CP-2(1), IR-4 IR-4(1) | ||
中および高影響 ステークホルダーとの調整を支援するための、自動化された仕組みを実装します。 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| RESPOND | Communications (RS.CO) | RS.CO-5 | Low, Moderate and High Impact Share cybersecurity event information voluntarily, as appropriate, with industry security groups to achieve broader cybersecurity situational awareness. For example, the DHS National Cybersecurity & Communications Integration Center (NCCIC) [6] serves as a centralized location where operational elements involved in cybersecurity and communications reliance are coordinated and integrated. The Industrial Control Systems Cyber Emergency Response Team (ICS-CERT) [7] collaborates with international and private sector Computer Emergency Readiness Teams (CERTs) to share control systems-related cybersecurity incidents and mitigation measures. | PM-15, SI-5 |
| Analysis (RS.AN) | RS.AN-1 | Low Impact Investigate cybersecurity-related notifications generated from detection systems. | ISA/IEC 62443-2-1:2009 4.3.4.5.6 ISA/IEC 62443-3-3:2013 SR 6.1 IR-4, CA-7, AU-6 IR-5(1), SI-4(2) | |
Moderate and High Impact Implement automated mechanisms to assist in the investigation and analysis of cybersecurity-related notifications. | ||||
| RS.AN-2 | Low Impact Understand the full implication of the cybersecurity incident based on thorough investigation and analysis results. Correlate detected event information and incident responses with risk assessment outcomes to achieve perspective on incident impact across the organization. | ISA/IEC 62443-2-1:2009 4.3.4.5.6 IR-4(4) IR-4(1), SI-4(2) | ||
Moderate and High Impact Implement automated mechanisms to support incident impact analysis. | ||||
| RS.AN-3 | Low Impact Conduct forensic analysis on collected cybersecurity event information to determine root cause. | ISA/IEC 62443-3-3:SR 2.8, 2.9, 2.10 IR-4 AU-7(1) | ||
Moderate and High Impact Provide on-demand audit review, analysis, and reporting for after-the-fact investigations of cybersecurity incidents. | ||||
| RS.AN-4 | Low, Moderate and High Impact Categorize cybersecurity incidents according to level of severity and impact consistent with the response plan. | 62443-2-1:2009 4.3.4.5.6 RA-3, PM-9, IR-4 |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 対応(RESPOND) | コミュニケーション(RS.CO) | RS.CO-5 | 低・中・高影響 より広範なサイバーセキュリティの状況認識を得るため、適宜、サイバーセキュリティイベントの情報を業界のセキュリティグループと自発的に共有します。 たとえば、DHSのNational Cybersecurity & Communications Integration Center(NCCIC)[6] は、サイバーセキュリティおよび通信への依存に関わる運用要素を調整し、統合する中央拠点としての役割を果たします。Industrial Control Systems Cyber Emergency Response Team(ICS-CERT)[7] は、国際的なコンピュータ緊急対応チームおよび民間部門のコンピュータ緊急対応チーム(CERT)と協力して、制御システムに関連するサイバーセキュリティインシデントと緩和策を共有します。 | PM-15, SI-5 |
| 分析(RS.AN) | RS.AN-1 | 低影響 検知システムが生成したサイバーセキュリティ関連の通知を調査します。 | ISA/IEC 62443-2-1:2009 4.3.4.5.6 ISA/IEC 62443-3-3:2013 SR 6.1 IR-4, CA-7, AU-6 IR-5(1), SI-4(2) | |
中および高影響 サイバーセキュリティ関連の通知の調査と分析を支援するための、自動化された仕組みを実装します。 | ||||
| RS.AN-2 | 低影響 徹底した調査と分析の結果に基づいて、サイバーセキュリティインシデントがもたらすすべての意味合いを理解します。 組織全体でのインシデントの影響についての見通しを得るため、検知されたイベントの情報およびインシデント対応措置を、リスクアセスメントの結果と相関付けます。 | ISA/IEC 62443-2-1:2009 4.3.4.5.6 IR-4(4) IR-4(1), SI-4(2) | ||
中および高影響 インシデントの影響分析を支援するための、自動化された仕組みを実装します。 | ||||
| RS.AN-3 | 低影響 根本原因を特定するため、収集したサイバーセキュリティイベントの情報に対してフォレンジック分析を実施します。 | ISA/IEC 62443-3-3:SR 2.8, 2.9, 2.10 IR-4 AU-7(1) | ||
中および高影響 サイバーセキュリティインシデントの事後調査のために、オンデマンドの監査レビュー、分析、報告を提供します。 | ||||
| RS.AN-4 | 低・中・高影響 サイバーセキュリティインシデントを、対応計画に沿って、深刻度と影響の程度に応じて分類します。 | 62443-2-1:2009 4.3.4.5.6 RA-3, PM-9, IR-4 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| RESPOND | Analysis (RS.AN) | RS.AN-5 | Low and Moderate Impact Implement vulnerability management processes and procedures to incorporate processing, analyzing, and remediating vulnerabilities identified from internal and external sources | SI-5, PM-15 |
High Impact Implement automated mechanisms to disseminate and track remediation efforts for vulnerability information captured from internal and external sources to key stakeholders | SI-5(1) | |||
| Mitigation (RS.MI) | RS.MI-1 | Low, Moderate and High Impact Contain cybersecurity incidents to minimize impact on the manufacturing system. | ISA/IEC 62443-2-1:2009 4.3.4.5.6 62443-3-3:2013 SR 5.1, SR IR-4, IR-4(1) | |
| RS.MI-2 | Low Impact Mitigate cybersecurity incidents occurring on the manufacturing system. | ISA/IEC 62443-2-1:2009 4.3.4.5.6, IR-4 IR-4(1) | ||
Moderate and High Impact Implement automated mechanisms to support the cybersecurity incident mitigation process. | ||||
| RS.MI-3 | Low, Moderate and High Impact Ensure that vulnerabilities identified while responding to a cybersecurity incident are mitigated or documented as accepted risks. | RA-5, RA-3 | ||
| Improvements (RS.IM) | RS.IM-1 | Low, Moderate and High Impact Incorporate lessons learned from ongoing incident handling activities into incident response procedures, training, and testing, and implement the resulting changes accordingly. | ISA/IEC 62443-2-1:2009 4.3.4.5.10 IR-4 | |
| RS.IM-2 | Low, Moderate and High Impact Update the response plans to address changes to the organization, manufacturing system, attack vectors, or environment of operation and problems encountered during plan implementation, execution, or testing. Updates may include, for example, responses to disruptions or failures, and predetermined procedures. Enable a process for the response plan to evolve to reflect new threats, improved technology, and lessons learned. | CP-2 |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 対応(RESPOND) | 分析(RS.AN) | RS.AN-5 | 低および中影響 内部および外部の情報源から特定された脆弱性の処理、分析、是正を組み込んだ、脆弱性管理のプロセスと手順を実装します | SI-5, PM-15 |
高影響 内部および外部の情報源から取得した脆弱性情報について、是正の取り組みを主要なステークホルダーに周知し、追跡するための、自動化された仕組みを実装します | SI-5(1) | |||
| 緩和(RS.MI) | RS.MI-1 | 低・中・高影響 製造システムへの影響を最小限に抑えるため、サイバーセキュリティインシデントを封じ込めます。 | ISA/IEC 62443-2-1:2009 4.3.4.5.6 62443-3-3:2013 SR 5.1, SR IR-4, IR-4(1) | |
| RS.MI-2 | 低影響 製造システムで発生しているサイバーセキュリティインシデントを緩和します。 | ISA/IEC 62443-2-1:2009 4.3.4.5.6, IR-4 IR-4(1) | ||
中および高影響 サイバーセキュリティインシデントの緩和プロセスを支援するための、自動化された仕組みを実装します。 | ||||
| RS.MI-3 | 低・中・高影響 サイバーセキュリティインシデントへの対応中に特定された脆弱性が、緩和されるか、受容されたリスクとして文書化されるようにします。 | RA-5, RA-3 | ||
| 改善(RS.IM) | RS.IM-1 | 低・中・高影響 継続中のインシデント処理活動から得られた教訓を、インシデント対応の手順、トレーニング、テストに取り入れ、その結果生じる変更を適宜実装します。 | ISA/IEC 62443-2-1:2009 4.3.4.5.10 IR-4 | |
| RS.IM-2 | 低・中・高影響 組織、製造システム、攻撃ベクトル、運用環境の変化、および計画の実装、実行、テスト中に遭遇した問題に対処するため、対応計画を更新します。 更新には、たとえば、中断や障害への対応、あらかじめ定められた手順が含まれる場合があります。 新たな脅威、改善された技術、教訓を反映して対応計画が進化していくプロセスを整えます。 | CP-2 |
| Function | Category | Subcategory | Manufacturing Profile Guidance | Reference |
|---|---|---|---|---|
| RECOVER | Recovery Planning (RC.RP) | RC.RP-1 | Low and Moderate Impact Execute the recovery plan during or after a cybersecurity incident on the manufacturing system. Restore the manufacturing system within a predefined time-period from configuration-controlled and integrity-protected information representing a known, operational state for the components. | IR-8, CP-10 CP-10(4) CP-2(5) |
High Impact Continue essential manufacturing functions and services with little or no loss of operational continuity and sustain continuity until full system restoration. | ||||
| Improvements (RC.IM) | RC.IM-1 | Low, Moderate and High Impact Incorporate lessons learned from ongoing recovery activities into system recovery procedures, training, and testing, and implement the resulting changes accordingly. | ISA/IEC 62443-2-1 4.4.3.4 IR-4 | |
| RC.IM-2 | Low, Moderate and High Impact Update the recovery plan to address changes to the organization, manufacturing system, or environment of operation and problems encountered during plan implementation, execution, or testing. Ensure that updates are integrated into the recovery plans. | CP-2, IR-8 | ||
| Communications (RC.CO) | RC.CO-1 | Low Impact Centralize and coordinate information distribution, and manage the public facing representation of the organization. Public relations management may include, for example, managing media interactions, coordinating and logging all requests for interviews, handling and ‘triaging’ phone calls and e-mail requests, matching media requests with appropriate and available internal experts who are ready to be interviewed, screening all of information provided to the media, ensuring personnel are familiar with public relations and privacy policies. | COBIT 5 EDM03.02 | |
Moderate Impact Assign a Public Relations Officer. | ||||
High Impact Pre-define media contacts. Implement external assets to manage public relations. | ||||
| RC.CO-2 | Low, Moderate and High Impact Implement a crisis response strategy to protect against negative impact and repair organizational reputation. Crisis response strategies include, for example, actions to shape attributions of the crisis, change perceptions of the organization in crisis, and reduce the negative effect generated by the crisis. | COBIT 5 EDM03.02 | ||
| RC.CO-3 | Low, Moderate and High Impact Communicate recovery activities to all relevant stakeholders, and executive and management teams. | CP-2 IR-4 |
| 機能 | カテゴリ | サブカテゴリ | 製造プロファイルの指針 | 参照 |
|---|---|---|---|---|
| 復旧(RECOVER) | 復旧計画(RC.RP) | RC.RP-1 | 低および中影響 製造システムでサイバーセキュリティインシデントが発生している間または発生した後に、復旧計画を実行します。 構成管理の対象であり完全性が保護された、構成要素の既知の運用状態を表す情報から、あらかじめ定められた期間内に製造システムを復元します。 | IR-8, CP-10 CP-10(4) CP-2(5) |
高影響 運用の継続性の損失をほとんど、またはまったく生じさせずに不可欠な製造機能とサービスを継続し、システムが完全に復元されるまでその継続性を維持します。 | ||||
| 改善(RC.IM) | RC.IM-1 | 低・中・高影響 継続中の復旧活動から得られた教訓を、システム復旧の手順、トレーニング、テストに取り入れ、その結果生じる変更を適宜実装します。 | ISA/IEC 62443-2-1 4.4.3.4 IR-4 | |
| RC.IM-2 | 低・中・高影響 組織、製造システム、運用環境の変化、および計画の実装、実行、テスト中に遭遇した問題に対処するため、復旧計画を更新します。 更新が復旧計画に組み込まれるようにします。 | CP-2, IR-8 | ||
| コミュニケーション(RC.CO) | RC.CO-1 | 低影響 情報の配布を一元化して調整し、組織の外向けの表現を管理します。広報の管理には、たとえば、メディアとのやり取りの管理、取材依頼のすべての調整と記録、電話や電子メールの依頼への対応と「トリアージ」、メディアの依頼と、取材を受ける準備のできた適切で対応可能な社内の専門家との対応付け、メディアに提供するすべての情報の審査、要員が広報とプライバシーのポリシーに習熟していることの確実化が含まれる場合があります。 | COBIT 5 EDM03.02 | |
中影響 広報責任者を任命します。 | ||||
高影響 メディアの連絡先をあらかじめ定義します。 広報を管理するための外部の資源を導入します。 | ||||
| RC.CO-2 | 低・中・高影響 悪影響から保護し、組織の評判を回復するための、危機対応戦略を実装します。危機対応戦略には、たとえば、危機の原因帰属を形づくる行動、危機にある組織に対する認識を変える行動、危機によって生じる悪影響を軽減する行動が含まれます。 | COBIT 5 EDM03.02 | ||
| RC.CO-3 | 低・中・高影響 復旧活動を、関連するすべてのステークホルダー、および経営層と管理層のチームに伝達します。 | CP-2 IR-4 |
References
参考文献
[1] Executive Order 13636 (2013) Improving Critical Infrastructure Cybersecurity. (The White House, Washington, DC), DCPD-201300091, February 12, 2013. https://www.govinfo.gov/app/details/DCPD-201300091
[1] Executive Order 13636 (2013) Improving Critical Infrastructure Cybersecurity. (The White House, Washington, DC), DCPD-201300091, February 12, 2013. https://www.govinfo.gov/app/details/DCPD-201300091
[2] National Institute of Standards and Technology (2018) Framework for Improving Critical Infrastructure Cybersecurity, Version 1.1. (National Institute of Standards and Technology, Gaithersburg, MD). https://doi.org/10.6028/NIST.CSWP.04162018
[2] National Institute of Standards and Technology (2018) Framework for Improving Critical Infrastructure Cybersecurity, Version 1.1. (National Institute of Standards and Technology, Gaithersburg, MD). https://doi.org/10.6028/NIST.CSWP.04162018
[3] Stouffer KA, Lightman S, Pillitteri VY, Abrams M, Hahn A (2015) Guide to Industrial Control Systems (ICS) Security. (National Institute of Standards and Technology, Gaithersburg, MD), NIST Special Publication (SP) 800-82, Rev. 2. https://doi.org/10.6028/NIST.SP.800-82r2
[3] Stouffer KA, Lightman S, Pillitteri VY, Abrams M, Hahn A (2015) Guide to Industrial Control Systems (ICS) Security. (National Institute of Standards and Technology, Gaithersburg, MD), NIST Special Publication (SP) 800-82, Rev. 2. https://doi.org/10.6028/NIST.SP.800-82r2
[4] Joint Task Force Transformation Initiative (2013) Security and Privacy Controls for Federal Information Systems and Organizations. (National Institute of Standards and Technology, Gaithersburg, MD), NIST Special Publication (SP) 800-53, Rev. 4, Includes updates as of January 22, 2015. https://doi.org/10.6028/NIST.SP.800-53r4
[4] Joint Task Force Transformation Initiative (2013) Security and Privacy Controls for Federal Information Systems and Organizations. (National Institute of Standards and Technology, Gaithersburg, MD), NIST Special Publication (SP) 800-53, Rev. 4, Includes updates as of January 22, 2015. https://doi.org/10.6028/NIST.SP.800-53r4
[5] The International Society of Automation (2020) ISA99, Industrial Automation and Control Systems Security. Available at https://www.isa.org/isa99/ [ISA/IEC 62443 Series of Standards on Industrial Automation and Control Systems (IACS) Security.]
[5] The International Society of Automation (2020) ISA99, Industrial Automation and Control Systems Security. 入手先: https://www.isa.org/isa99/ [ISA/IEC 62443 Series of Standards on Industrial Automation and Control Systems (IACS) Security.]
[6] Cybersecurity and Infrastructure Security Agency (2020) National Cybersecurity and Communications Integration Center (NCCIC). Available at https://www.cisa.gov/national-cybersecurity-communications-integration-center
[6] Cybersecurity and Infrastructure Security Agency (2020) National Cybersecurity and Communications Integration Center (NCCIC). 入手先: https://www.cisa.gov/national-cybersecurity-communications-integration-center
[7] Cybersecurity and Infrastructure Security Agency (2020) Industrial Control Systems. Available at https://www.us-cert.gov/ics [Formerly the site for the Industrial Control Systems Cyber Emergency Response Team (ICS-CERT).]
[7] Cybersecurity and Infrastructure Security Agency (2020) Industrial Control Systems. 入手先: https://www.us-cert.gov/ics [Formerly the site for the Industrial Control Systems Cyber Emergency Response Team (ICS-CERT).]
[8] National Institute of Standards and Technology (2004) Standards for Security Categorization of Federal Information and Information Systems. (U.S. Department of Commerce, Washington, DC), Federal Information Processing Standards Publication (FIPS) 199. https://doi.org/10.6028/NIST.FIPS.199
[8] National Institute of Standards and Technology (2004) Standards for Security Categorization of Federal Information and Information Systems. (U.S. Department of Commerce, Washington, DC), Federal Information Processing Standards Publication (FIPS) 199. https://doi.org/10.6028/NIST.FIPS.199
Appendix A - Acronyms and Abbreviations
付録A - 略語
Selected acronyms and abbreviations used in the Manufacturing Profile are defined below.
製造プロファイルで使用している主な略語を、次のとおり定義します。
CAN Controller Area Network
CAN Controller Area Network(コントローラーエリアネットワーク)
CSF Cybersecurity Framework
CSF Cybersecurity Framework(サイバーセキュリティフレームワーク)
DCS Distributed Control System
DCS Distributed Control System(分散制御システム)
FIPS Federal Information Processing Standards
FIPS Federal Information Processing Standards(連邦情報処理標準)
HMI Human Machine Interface
HMI Human Machine Interface(ヒューマンマシンインターフェース)
ICS Industrial Control System
ICS Industrial Control System(産業用制御システム)
ICS-CERT Industrial Control Systems Cyber Emergency Response Team
ICS-CERT Industrial Control Systems Cyber Emergency Response Team(産業用制御システムサイバー緊急対応チーム)
IEC International Electrotechnical Commission
IEC International Electrotechnical Commission(国際電気標準会議)
ISA The International Society of Automation
ISA The International Society of Automation(国際オートメーション学会)
IT Information Technology
IT Information Technology(情報技術)
LAN Local Area Network
LAN Local Area Network(ローカルエリアネットワーク)
NCCIC National Cybersecurity & Communications Integration Center
NCCIC National Cybersecurity & Communications Integration Center(国家サイバーセキュリティ・通信統合センター)
NIST National Institute of Standards and Technology
NIST National Institute of Standards and Technology(米国国立標準技術研究所)
NVD National Vulnerability Database
NVD National Vulnerability Database(脆弱性データベース)
OT Operational Technology
OT Operational Technology(運用技術)
PLC Programmable Logic Controller
PLC Programmable Logic Controller(プログラマブルロジックコントローラー)
RF Radio Frequency
RF Radio Frequency(無線周波数)
RTU Remote Terminal Unit
RTU Remote Terminal Unit(遠隔端末装置)
SCADA Supervisory Control and Data Acquisition
SCADA Supervisory Control and Data Acquisition(監視制御およびデータ収集)
US-CERT United States Computer Emergency Readiness Team
US-CERT United States Computer Emergency Readiness Team(米国コンピュータ緊急対応チーム)
VPN Virtual Private Network
VPN Virtual Private Network(仮想プライベートネットワーク)
Appendix B - Glossary
付録B - 用語集
Selected terms used in the Manufacturing Profile are defined below.
製造プロファイルで使用している主な用語を、次のとおり定義します。
Actuator - A device for moving or controlling a mechanism or system. It is operated by a source of energy, typically electric current, hydraulic fluid pressure, or pneumatic pressure, and converts that energy into motion. An actuator is the mechanism by which a control system acts upon an environment. The control system can be simple (a fixed mechanical or electronic system), software-based (e.g. a printer driver, robot control system), or a human or other agent. [800-82]
Actuator - 機構やシステムを動かしたり制御したりする装置です。電流、作動油の圧力、空気圧などのエネルギー源によって動作し、そのエネルギーを動きに変換します。アクチュエーターは、制御システムが環境に働きかけるための機構です。制御システムは、単純なもの(固定された機械的または電子的なシステム)、ソフトウェアベースのもの(たとえば、プリンタードライバー、ロボット制御システム)、または人間やその他の主体の場合があります。[800-82]
Business/Mission Objectives - Broad expression of business goals. Specified target outcome for business operations.
Business/Mission Objectives - 事業目標を広く表現したものです。事業運営の目標とする成果を明示したものです。
Capacity Planning - Systematic determination of resource requirements for the projected output, over a specific period. [businessdictionary.com]
Capacity Planning - 特定の期間における予測生産量に必要なリソース要件を、体系的に決定することです。[businessdictionary.com]
Category - The subdivision of a Function into groups of cybersecurity outcomes closely tied to programmatic needs and particular activities.
Category - 機能を、プログラム上のニーズや特定の活動と密接に結び付いたサイバーセキュリティの成果のグループに細分したものです。
Critical Infrastructure - Essential services and related assets that underpin American society and serve as the backbone of the nation's economy, security, and health. [DHS]
Critical Infrastructure - 米国社会を支え、国の経済、安全保障、健康の基幹となる、不可欠なサービスと関連資産です。[DHS]
Criticality Reviews - A determination of the ranking and priority of manufacturing system components, services, processes, and inputs in order to establish operational thresholds and recovery objectives.
Criticality Reviews - 運用上のしきい値と復旧目標を定めるため、製造システムの構成要素、サービス、プロセス、投入物の順位と優先度を判断することです。
Critical Services - The subset of mission essential services required to conduct manufacturing operations. Function or capability that is required to maintain health, safety, the environment and availability for the equipment under control. [62443]
Critical Services - 製造運用を行うために必要な、ミッションに不可欠なサービスの部分集合です。制御対象の機器の健全性、安全、環境、可用性を維持するために必要な機能または能力です。[62443]
Cyber Risk - Risk of financial loss, operational disruption, or damage, from the failure of the digital technologies employed for informational and/or operational functions introduced to a manufacturing system via electronic means from the unauthorized access, use, disclosure, disruption, modification, or destruction of the manufacturing system.
Cyber Risk - 情報機能または運用機能に用いるデジタル技術が電子的手段を通じて製造システムに導入され、その製造システムへの不正なアクセス、使用、開示、中断、改変または破壊によって当該技術が機能しなくなることから生じる、金銭的損失、運用の中断または損害のリスクです。
Cybersecurity - The process of protecting information by preventing, detecting, and responding to attacks. [CSF]
Cybersecurity - 攻撃を防止し、検知し、攻撃に対応することで、情報を保護するプロセスです。[CSF]
Defense-in-depth - The application of multiple countermeasures in a layered or stepwise manner to achieve security objectives. The methodology involves layering heterogeneous security technologies in the common attack vectors to ensure that attacks missed by one technology are caught by another. [62443 1-1]
Defense-in-depth - セキュリティ目標を達成するために、複数の対策を階層的または段階的に適用することです。この手法では、一般的な攻撃ベクトルに異種のセキュリティ技術を重ねて配置し、ある技術が見逃した攻撃を別の技術が捕捉できるようにします。[62443 1-1]
Environmental Support – Any environmental factor for which the organization determines that it needs to continue to provide support in a contingency situation, even if in a degraded state.
Environmental Support – 縮退した状態であっても、緊急事態において組織が支援を継続する必要があると判断する、あらゆる環境要因です。
This could include factors such as power, air conditioning, humidity control, fire protection, lighting, etc.
これには、電力、空調、湿度管理、防火、照明などの要因が含まれます。
For example, while developing the contingency plan, the organization may determine that it is necessary to continue to ensure the appropriate temperature and humidity during a contingency situation so they would plan for the capacity to support that via supplemental/mobile air conditioning units, backup power, etc. and the associated procedures to ensure cutover operations. Such determinations are based on an assessment of risk, system categorization (impact level), and organizational risk tolerance.
たとえば、組織は、緊急時対応計画を策定する中で、緊急事態においても適切な温度と湿度を確保し続ける必要があると判断する場合があります。その場合、補助用またはモバイル型の空調ユニット、予備電源などによってそれを支える容量と、切り替え運用を確実にするための関連手順を計画します。このような判断は、リスクアセスメント、システムの分類(影響レベル)、および組織のリスク許容度に基づいて行われます。
Event - Any observable occurrence on a manufacturing system. Events can include cybersecurity changes that may have an impact on manufacturing operations (including mission, capabilities, or reputation). [CSF]
Event - 製造システム上で観察可能なあらゆる事象です。イベントには、製造運用(ミッション、能力、評判を含む)に影響を及ぼす可能性のあるサイバーセキュリティ上の変化が含まれる場合があります。[CSF]
Fail to Known State – Upon a disruption event that causes the system to fail, it fails to a pre-determined state. Failure in a known safe state helps to prevent systems from failing to a state that may cause injury to individuals or destruction to property. Preserving manufacturing system state information facilitates system restart and return to the operational mode of organizations with less disruption of mission/business processes. [NVD.NIST]
Fail to Known State – システムを障害に至らせる中断イベントが発生した際に、システムがあらかじめ定められた状態に移行して機能停止することです。既知の安全な状態で機能停止することで、個人への傷害や財産の破壊につながる可能性のある状態にシステムが陥ることを防ぐのに役立ちます。製造システムの状態情報を保持しておくと、システムの再起動と組織の運用モードへの復帰が容易になり、ミッション/事業プロセスの中断を抑えられます。[NVD.NIST]
Firmware - Software program or set of instructions programmed on the flash ROM of a hardware device. It provides the necessary instructions for how the device communicates with the other computer hardware. [Techterms.com]
Firmware - ハードウェアデバイスのフラッシュROMにプログラムされたソフトウェアプログラムまたは命令の集合です。デバイスがほかのコンピューターハードウェアとどのように通信するかについて、必要な命令を提供します。[Techterms.com]
Framework - The Cybersecurity Framework developed for defining protection of critical infrastructure. It provides a common language for understanding, managing, and expressing cybersecurity risk both internally and externally. Includes activities to achieve specific cybersecurity outcomes, and references examples of guidance to achieve those outcomes.
Framework - 重要インフラの保護を定義するために策定されたサイバーセキュリティフレームワークです。サイバーセキュリティリスクを組織内外で理解し、管理し、表現するための共通言語を提供します。特定のサイバーセキュリティの成果を達成するための活動を含み、それらの成果を達成するための指針の例を参照しています。
Function - Primary unit within the Cybersecurity Framework. Exhibits basic cybersecurity activities at their highest level.
Function - サイバーセキュリティフレームワークの主要な単位です。基本的なサイバーセキュリティ活動を、最も高い水準で示します。
Incident - An occurrence that actually or potentially jeopardizes the confidentiality, integrity, or availability of an information system or the information the system processes, stores, or transmits or that constitutes a violation or imminent threat of violation of security policies, security procedures, or acceptable use policies. [CSF]
Incident - 情報システム、またはシステムが処理、保存、伝送する情報の機密性、完全性、可用性を、現実に、または潜在的に危うくする事象、あるいはセキュリティポリシー、セキュリティ手順、許容される使用のポリシーの違反または差し迫った違反の脅威となる事象です。[CSF]
Informative References - Specific sections of standards, guidelines, and practices common among critical infrastructure sectors that illustrate a method to achieve the outcomes associated with each Subcategory in the Cybersecurity Framework.
Informative References - サイバーセキュリティフレームワークの各サブカテゴリに関連する成果を達成する方法を示す、重要インフラのセクターに共通する標準、指針、慣行の特定の節です。
Integrator - A value-added engineering organization that focuses on industrial control and information systems, manufacturing execution systems, and plant automation, that has application knowledge and technical expertise, and provides an integrated solution to an engineering problem. This solution includes final project engineering, documentation, procurement of hardware, development of custom software, installation, testing, and commissioning. [CSIA.com]
Integrator - 産業用制御システムおよび情報システム、製造実行システム、工場の自動化に重点を置き、アプリケーションの知識と技術的専門性を持ち、エンジニアリング上の課題に対する統合的なソリューションを提供する、付加価値型のエンジニアリング組織です。このソリューションには、最終的なプロジェクトエンジニアリング、文書化、ハードウェアの調達、カスタムソフトウェアの開発、設置、テスト、稼働開始が含まれます。[CSIA.com]
Manufacturing Operations - Activities concerning the facility operation, system processes, materials input/output, maintenance, supply and distribution, health, and safety, emergency response, human resources, security, information technology and other contributing measures to the manufacturing enterprise.
Manufacturing Operations - 製造企業に関わる施設運営、システムプロセス、材料の入出力、保守、供給と流通、健康と安全、緊急対応、人事、セキュリティ、情報技術、およびその他の関連措置に関する活動です。
Network Access - any access across a network connection in lieu of local access (i.e., user being physically present at the device).
Network Access - ローカルアクセス(すなわち、利用者がデバイスの場所に物理的にいる状態)の代わりに、ネットワーク接続を介して行うあらゆるアクセスです。
Non-local Connection - A connection to the manufacturing system affording the user access to system resources and system functionality while physically not present.
Non-local Connection - 利用者が物理的に現場にいない状態で、システムのリソースと機能にアクセスできるようにする、製造システムへの接続です。
Non-Technology-Based Input Product – Manufactured component parts or materials used in the organization manufacturing process that do not incorporate information technology and are provided by third-parties.
Non-Technology-Based Input Product – 組織の製造プロセスで使用される、情報技術を組み込んでおらず、第三者から提供される、製造された部品または材料です。
Overlay - A fully specified set of security controls, control enhancements, and supplemental guidance derived from tailoring a security baseline to fit the user’s specific environment and mission. [800-53]
Overlay - セキュリティベースラインを、利用者の特定の環境とミッションに合うように調整して得られた、完全に規定されたセキュリティ管理策、管理策の強化、補足指針の集合です。[800-53]
Operational technology - Hardware and software that detects or causes a change through the direct monitoring and/or control of physical devices, processes and events in the enterprise. [Gartner.com]
Operational technology - 企業内の物理的なデバイス、プロセス、イベントを直接監視または制御することによって、変化を検知する、または変化を引き起こすハードウェアとソフトウェアです。[Gartner.com]
Programmable Logic Controller - A solid-state control system that has a user-programmable memory for storing instructions for the purpose of implementing specific functions such as I/O control, logic, timing, counting, three mode (PID) control, communication, arithmetic, and data and file processing. [800-82]
Programmable Logic Controller - I/O制御、論理、タイミング、カウント、3モード(PID)制御、通信、演算、データおよびファイルの処理といった特定の機能を実装するための命令を保存する、利用者がプログラム可能なメモリを持つ、半導体式の制御システムです。[800-82]
Port - The entry or exit point from a computer for connecting communications or peripheral devices. [800-82]
Port - 通信機器や周辺機器を接続するための、コンピューターの入口または出口です。[800-82]
Profile - A representation of the outcomes that a particular system or organization has selected from the Framework Categories and Subcategories. [CSF]
Profile - 特定のシステムまたは組織が、フレームワークのカテゴリとサブカテゴリから選択した成果を表したものです。[CSF]
•Target Profile - the desired outcome or ‘to be’ state of cybersecurity implementation
•目標プロファイル(Target Profile)- サイバーセキュリティの実装における望ましい成果、すなわち「あるべき」状態
•Current Profile – the ‘as is’ state of system cybersecurity
•現在のプロファイル(Current Profile)– システムのサイバーセキュリティの「現状」
Protocol - A set of rules (i.e., formats and procedures) to implement and control some type of association (e.g., communication) between systems. [800-82]
Protocol - システム間のある種の関連付け(たとえば、通信)を実装し、制御するための規則(すなわち、形式と手順)の集合です。[800-82]
Remote Access - Access by users (or information systems) communicating external to an information system security perimeter. Network access is any access across a network connection in lieu of local access (i.e., user being physically present at the device). [800-53]
Remote Access - 情報システムのセキュリティ境界の外部から通信する利用者(または情報システム)によるアクセスです。ネットワークアクセスとは、ローカルアクセス(すなわち、利用者がデバイスの場所に物理的にいる状態)の代わりに、ネットワーク接続を介して行うあらゆるアクセスです。[800-53]
Resilience Requirements - The business-driven availability and reliability characteristics for the manufacturing system that specify recovery tolerances from disruptions and major incidents.
Resilience Requirements - 中断や重大なインシデントからの復旧の許容範囲を規定する、製造システムに対する事業主導の可用性と信頼性の特性です。
Risk Assessment - The process of identifying risks to agency operations (including mission, functions, image, or reputation), agency assets, or individuals by determining the probability of occurrence, the resulting impact, and additional security controls that would mitigate this impact. Part of risk management, synonymous with risk analysis. Incorporates threat and vulnerability analyses. [800-82]
Risk Assessment - 発生確率、その結果生じる影響、およびその影響を緩和する追加のセキュリティ管理策を判断することによって、機関の業務(ミッション、機能、イメージ、評判を含む)、機関の資産、または個人に対するリスクを特定するプロセスです。リスク管理の一部であり、リスク分析と同義です。脅威分析と脆弱性分析を組み込みます。[800-82]
Risk Tolerance - The level of risk that the Manufacturer is willing to accept in pursuit of strategic goals and objectives. [800-53]
Risk Tolerance - 製造者が、戦略的な目標と目的を追求するうえで、受け入れてもよいと考えるリスクの水準です。[800-53]
Router - A computer that is a gateway between two networks at OSI layer 3 and that relays and directs data packets through that inter-network. The most common form of router operates on IP packets. [800-82]
Router - OSI参照モデルの第3層で2つのネットワーク間のゲートウェイとなり、そのネットワーク間でデータパケットを中継し、振り向けるコンピューターです。最も一般的なルーターは、IPパケットを扱います。[800-82]
Security Control - The management, operational, and technical controls (i.e., safeguards or countermeasures) prescribed for a system to protect the confidentiality, integrity, and availability of the system, its components, processes, and data. [800-82]
Security Control - システム、その構成要素、プロセス、データの機密性、完全性、可用性を保護するために、システムに対して規定される管理的、運用的、技術的な管理策(すなわち、保護対策または対抗策)です。[800-82]
Subcategory - The subdivision of a Category into specific outcomes of technical and/or management activities. Examples of Subcategories include “External information systems are catalogued,” “Data-at-rest is protected,” and “Notifications from detection systems are investigated.” [CSF]
Subcategory - カテゴリを、技術的活動や管理的活動の具体的な成果に細分したものです。サブカテゴリの例には、「外部の情報システムが目録化されている」「保存データが保護されている」「検知システムからの通知が調査されている」があります。[CSF]
Supporting Services - Providers of external system services to the manufacturer through a variety of consumer-producer relationships including but not limited to: joint ventures; business partnerships; outsourcing arrangements (i.e., through contracts, interagency agreements, lines of business arrangements); licensing agreements; and/or supply chain exchanges. Supporting services include, for example, Telecommunications, engineering services, power, water, software, tech support, and security. [800-53]
Supporting Services - ジョイントベンチャー、事業提携、外部委託の取り決め(すなわち、契約、機関間合意、事業分野の取り決めによるもの)、ライセンス契約、サプライチェーン上の取引など(ただしこれらに限らない)、さまざまな消費者と生産者の関係を通じて、製造者に外部システムのサービスを提供するプロバイダーです。支援サービスには、たとえば、通信、エンジニアリングサービス、電力、水道、ソフトウェア、技術サポート、セキュリティが含まれます。[800-53]
Switch - A device that channels incoming data from any of multiple input ports to the specific output port that will take the data toward its intended destination. [Whatis.com]
Switch - 複数の入力ポートのいずれかから入ってきたデータを、そのデータを目的地へ向かわせる特定の出力ポートへ導くデバイスです。[Whatis.com]
System Categorization - The characterization of a manufacturing system, its components, and operations, based on an assessment of the potential impact that a loss of availability, integrity, or confidentiality would have on organizational operations, organizational assets, or individuals. [FIPS 199]
System Categorization - 可用性、完全性、または機密性の喪失が、組織の業務、組織の資産、または個人に及ぼす潜在的な影響の評価に基づいて、製造システム、その構成要素、運用を特徴付けることです。[FIPS 199]
Technology-Based Input Product – Manufactured components used in the organization manufacturing process incorporating information technology and provided by third-parties (e.g. PLC, Sensors, Data Collection Systems, Workstations, Servers, etc).
Technology-Based Input Product – 情報技術を組み込んだ、組織の製造プロセスで使用される第三者提供の製造部品(たとえば、PLC、センサー、データ収集システム、ワークステーション、サーバーなど)です。
Third-Party Relationships - relationships with external entities. External entities may include, for example, service providers, vendors, supply-side partners, demand-side partners, alliances, consortiums, and investors, and may include both contractual and non-contractual parties. [DHS]
Third-Party Relationships - 外部の事業体との関係です。外部の事業体には、たとえば、サービスプロバイダー、ベンダー、供給側のパートナー、需要側のパートナー、提携先、コンソーシアム、投資家が含まれ、契約関係にある者と契約関係にない者の両方を含む場合があります。[DHS]
Third-party Providers - Service providers, integrators, vendors, telecommunications, and infrastructure support that are external to the organization that operates the manufacturing system.
Third-party Providers - 製造システムを運用する組織の外部にある、サービスプロバイダー、インテグレーター、ベンダー、通信事業者、インフラ支援事業者です。
Thresholds - Values used to establish concrete decision points and operational control limits to trigger management action and response escalation.
Thresholds - 管理上の措置と対応のエスカレーションを引き起こす、具体的な判断点と運用管理の限界値を確立するために使用される値です。