NIST SP 800-166 日本語訳
英語タイトル : Derived PIV Application and Data Model Test Guidelines日本語タイトル : 派生PIVアプリケーションおよびデータモデル試験ガイドライン
公開日 : 2016-06-06
原文URL : https://csrc.nist.gov/pubs/sp/800/166/final
翻訳編集 : 自動生成(有志による非公式の日本語訳), 原文取得日 : 2026-09-30, 訳文 : 741 / 741 ブロック
[要約] SP 800-166 は、リムーバブル・ハードウェア・トークンおよびモバイル端末に実装された派生 PIV アプリケーションと、関連する派生 PIV データオブジェクトを試験するための要件と試験アサーションを示します。派生 PIV アプリケーションの適合性を確認する試験と、派生 PIV データモデルの試験について、試験の概要、構成、適合基準、試験文書、導出試験要件、試験アサーションを扱います。SP 800-157 が定める派生 PIV クレデンシャルの仕様に適合していることを検証し、相互運用可能な FIPS 201 製品の調達を容易にすることを目的とします。
NIST Special Publication 800-166
NIST特別刊行物 800-166
Derived PIV Application and Data Model Test Guidelines
派生PIVアプリケーションおよびデータモデル試験ガイドライン
David Cooper Hildegard Ferraiolo
David Cooper、Hildegard Ferraiolo
Ramaswamy Chandramouli
Ramaswamy Chandramouli
Nabil Ghadiali Jason Mohler Steven Brady
Nabil Ghadiali、Jason Mohler、Steven Brady
This publication is available free of charge from: http://dx.doi.org/10.6028/NIST.SP.800-166
本刊行物は以下から無料で入手できる:http://dx.doi.org/10.6028/NIST.SP.800-166
C O M P U T E R S E C U R I T Y
コンピュータセキュリティ
[NIST のロゴ。公的な標章のため、この非公式サイトには掲載していません。原本 PDF を参照してください。]
NIST Special Publication 800-166
NIST特別刊行物 800-166
Derived PIV Application and Data Model Test Guidelines
派生PIVアプリケーションおよびデータモデル試験ガイドライン
David Cooper Hildegard Ferraiolo
David Cooper、Hildegard Ferraiolo
Ramaswamy Chandramouli Computer Security Division Information Technology Laboratory
Ramaswamy Chandramouli コンピュータセキュリティ部門 情報技術研究所
Nabil Ghadiali National Gallery of Art Washington, DC
Nabil Ghadiali National Gallery of Art ワシントンD.C.
Jason Mohler Steven Brady
Jason Mohler、Steven Brady
Electrosoft Services, Inc.
Electrosoft Services, Inc.
Reston, VA
バージニア州レストン
This publication is available free of charge from http://dx.doi.org/10.6028/NIST.SP.800-166
本刊行物は以下から無料で入手できる http://dx.doi.org/10.6028/NIST.SP.800-166
June 2016
2016年6月
U.S. Department of Commerce Penny Pritzker, Secretary
米国商務省 長官 Penny Pritzker
National Institute of Standards and Technology
国立標準技術研究所
Willie May, Under Secretary of Commerce for Standards and Technology and Director
Willie May、商務・標準技術担当次官兼所長
Authority
権限
This publication has been developed by NIST in accordance with its statutory responsibilities under the Federal Information Security Modernization Act (FISMA) of 2014, 44 U.S.C. § 3541 et seq., Public Law (P.L.) 113-283. NIST is responsible for developing information security standards and guidelines, including minimum requirements for federal information systems, but such standards and guidelines shall not apply to national security systems without the express approval of appropriate federal officials exercising policy authority over such systems. This guideline is consistent with the requirements of the Office of Management and Budget (OMB) Circular A-130.
本刊行物は、2014年連邦情報セキュリティ近代化法(FISMA、合衆国法典第44編§3541以下、公法113-283)に基づく法定責務に従ってNISTが策定しました。NISTは、連邦情報システムの最低要件を含む情報セキュリティ標準およびガイドラインを策定する責任を負います。ただし、国家安全保障システムに関する政策権限を行使する適切な連邦当局者の明示的な承認がない限り、これらの標準およびガイドラインは国家安全保障システムには適用されません。本ガイドラインは行政管理予算局(OMB)通達A-130の要件と整合しています。
Nothing in this publication should be taken to contradict the standards and guidelines made mandatory and binding on Federal agencies by the Secretary of Commerce under statutory authority. Nor should these guidelines be interpreted as altering or superseding the existing authorities of the Secretary of Commerce, Director of the OMB, or any other Federal official. This publication may be used by nongovernmental organizations on a voluntary basis and is not subject to copyright in the United States. Attribution would, however, be appreciated by NIST.
本刊行物のいかなる記述も、商務長官が法的権限に基づいて連邦機関に義務付け、拘束力を持たせた標準およびガイドラインに反するものと解釈してはなりません。また、本ガイドラインは商務長官、OMB長官その他の連邦当局者が有する既存の権限を変更または置き換えるものと解釈してはなりません。本刊行物は非政府組織が任意に使用できます。米国内では著作権の対象ではありませんが、NISTは出典の明記を歓迎します。
National Institute of Standards and Technology Special Publication 800-166 Natl. Inst. Stand. Technol. Spec. Publ. 800-166, 143 pages (June 2016) CODEN: NSPUE2
米国国立標準技術研究所 Special Publication 800-166 Natl. Inst. Stand. Technol. Spec. Publ. 800-166, 143ページ(2016年6月) CODEN: NSPUE2
This publication is available free of charge from: http://dx.doi.org/10.6028/NIST.SP.800-166
本刊行物は以下から無料で入手できる:http://dx.doi.org/10.6028/NIST.SP.800-166
Certain commercial entities, equipment, or materials may be identified in this document in order to describe an experimental procedure or concept adequately. Such identification is not intended to imply recommendation or endorsement by NIST, nor is it intended to imply that the entities, materials, or equipment are necessarily the best available for the purpose.
実験手順または概念を適切に説明するために、本文書では特定の商業事業者、機器、または資材を挙げることがあります。そうした記載は、NISTによる推奨または支持を意味するものではなく、それらの事業者、資材、または機器がその目的にとって必ずしも最良であることを意味するものでもありません。
There may be references in this publication to other publications currently under development by NIST in accordance with its assigned statutory responsibilities. The information in this publication, including concepts and methodologies, may be used by federal agencies even before the completion of such companion publications. Thus, until each publication is completed, current requirements, guidelines, and procedures, where they exist, remain operative. For planning and transition purposes, federal agencies may wish to closely follow the development of these new publications by NIST.
本出版物には、NISTが法定の責務に従って現在策定中の他の出版物への参照が含まれている場合があります。本出版物の情報(概念および方法論を含む)は、そうした関連出版物の完成前であっても連邦政府機関が利用してもよいです。したがって、各出版物が完成するまでは、現行の要件、ガイドライン、および手順が存在する場合にはそれらが引き続き有効です。計画および移行のため、連邦政府機関はNISTによるこれらの新しい出版物の策定状況を注視するとよいです。
Organizations are encouraged to review all draft publications during public comment periods and provide feedback to NIST. Many NIST cybersecurity publications, other than the ones noted above, are available at http://csrc.nist.gov/publications.
組織は、パブリックコメント期間中にすべての草案を確認し、NISTにフィードバックを提供することが推奨されます。上記以外の多くのNISTサイバーセキュリティ出版物は、http://csrc.nist.gov/publications で入手できます。
Comments on this publication may be submitted to:
本刊行物に関する意見の送付先:
National Institute of Standards and Technology Attn: Computer Security Division, Information Technology Laboratory 100 Bureau Drive (Mail Stop 8930) Gaithersburg, MD 20899-8930 Email: pivtesting@nist.gov
National Institute of Standards and Technology Attn: Computer Security Division, Information Technology Laboratory 100 Bureau Drive (Mail Stop 8930) Gaithersburg, MD 20899-8930 Email: pivtesting@nist.gov
Reports on Computer Systems Technology
コンピュータシステム技術に関する報告書
The Information Technology Laboratory (ITL) at the National Institute of Standards and Technology (NIST) promotes the U.S. economy and public welfare by providing technical leadership for the Nation’s measurement and standards infrastructure. ITL develops tests, test methods, reference data, proof of concept implementations, and technical analyses to advance the development and productive use of information technology. ITL’s responsibilities include the development of management, administrative, technical, and physical standards and guidelines for the cost-effective security and privacy of other than national security-related information in federal information systems. The Special Publication 800-series reports on ITL’s research, guidelines, and outreach efforts in information system security, and its collaborative activities with industry, government, and academic organizations.
国立標準技術研究所(NIST)の情報技術研究所(ITL)は、米国の計量・標準基盤に技術的なリーダーシップを提供し、米国経済と公共福祉の向上を図っています。ITLは、情報技術の発展と有効活用を促進するため、試験、試験方法、参照データ、概念実証の実装、技術分析を開発しています。また、連邦情報システムにおける国家安全保障関連以外の情報の費用対効果に優れたセキュリティとプライバシーを確保するため、管理、運用、技術、物理面の標準およびガイドラインを策定します。特別刊行物800シリーズは、情報システムのセキュリティに関するITLの研究、ガイドライン、普及活動ならびに産業界、政府、学術機関との協力活動を報告するものです。
Abstract
概要
NIST Special Publication (SP) 800-157 contains technical guidelines for the implementation of standards-based, secure, reliable, interoperable Public Key Infrastructure (PKI)-based identity credentials that are issued for mobile devices by federal departments and agencies to individuals who possess and prove control over a valid Personal Identity Verification (PIV) Card. This document, SP 800-166, contains the requirements and test assertions for testing the Derived PIV Application and associated Derived PIV data objects implemented on removable hardware tokens and within mobile devices. The tests reflect the design goals of interoperability and interface functions.
NIST特別刊行物(SP)800-157は、連邦政府機関が、正規の個人識別確認(PIV)カードを所持し、その管理を証明する個人に対してモバイル端末用に発行する、標準準拠で安全、信頼性が高く、相互運用可能な公開鍵基盤(PKI)ベースのID資格情報の実装に関する技術ガイドラインを定めています。本書SP 800-166は、リムーバブル・ハードウェア・トークンおよびモバイル端末内に実装された派生PIVアプリケーションと関連する派生PIVデータオブジェクトを試験するための要件と試験アサーションを示します。試験は、相互運用性とインターフェース機能という設計目標を反映しています。
Keywords
キーワード
authentication; derived PIV application; derived PIV application data model; derived PIV credential; derived test requirements (DTR); FIPS 201; implementation under test (IUT); mobile devices; Personal Identity Verification (PIV); test assertions; token command interface.
認証、派生PIVアプリケーション、派生PIVアプリケーション・データモデル、派生PIV資格情報、派生試験要件(DTR)、FIPS 201、試験対象実装(IUT)、モバイル端末、個人識別確認(PIV)、試験アサーション、トークン・コマンド・インターフェース
Acknowledgements
謝辞
The authors (David Cooper, Hildegard Ferraiolo and Ramaswamy Chandramouli of NIST; Nabil Ghadiali of the National Gallery of Art; and Jason Mohler and Steven Brady of Electrosoft Services, Inc.), wish to thank their colleagues who reviewed drafts of this document and contributed to its development. Special gratitude to the General Services Administration (GSA) FIPS 201 Evaluation Program (GSA FIPS 201 EP) team for their review and contributions to the document.
著者(NISTのDavid Cooper、Hildegard Ferraiolo、Ramaswamy Chandramouli、National Gallery of ArtのNabil Ghadiali、Electrosoft Services, Inc.のJason MohlerおよびSteven Brady)は、本書の草稿を査読し、作成に貢献した同僚に謝意を表します。特に、査読と文書への貢献を行った一般調達局(GSA)のFIPS 201評価プログラム(GSA FIPS 201 EP)チームに深く感謝します。
Audience
対象読者
This document is targeted at vendors of Derived PIV Applications, issuers of Derived PIV Credentials, and entities that will conduct tests on these applications and credentials. Readers are assumed to have a working knowledge of SP 800-157, FIPS 201 and other PIV guidelines, and applicable technologies. This document is intended to:
本書の対象は、派生PIVアプリケーションのベンダー、派生PIV資格情報の発行者、およびこれらのアプリケーションと資格情報を試験する組織です。読者は、SP 800-157、FIPS 201、その他のPIVガイドラインおよび関連技術に関する実務知識を持つことを前提とします。本書は次のことを目的とします。
+ Enable developers of Derived PIV Applications to design their applications as specified in SP 800-157 for interface, data object container size and access requirements.
+ 派生PIVアプリケーションの開発者が、インターフェース、データオブジェクト・コンテナのサイズ、アクセス要件について、SP 800-157の仕様に従ってアプリケーションを設計できるようにします。
+ Enable issuers of Derived PIV Credentials to ensure that Derived PIV data objects conform to the requirements specified in SP 800-157.
+ 派生PIV資格情報の発行者が、派生PIVデータオブジェクトがSP 800-157の要件に適合することを確認できるようにします。
+ Enable developers and issuers to develop self-tests as part of the development effort and issuance process.
+ 開発者と発行者が、開発作業および発行プロセスの一環として自己試験を作成できるようにします。
+ Enable entities performing conformance tests on Derived PIV Applications and Derived PIV data objects to develop tests that cover the test suite provided in this document.
+ 派生PIVアプリケーションおよび派生PIVデータオブジェクトの適合性試験を行う組織が、本書の試験スイートを網羅する試験を作成できるようにします。
Table of Contents
目次
7. DERIVED TEST REQUIREMENTS FOR DATA MODEL OF THE DERIVED PIV APPLICATION27
7. 派生PIVアプリケーションのデータモデルに関する派生試験要件 — 27
7.1 BER-TLV CONFORMANCE — 27
7.1 BER-TLV適合性 — 27
7.2 SIGNED DATA OBJECT CONFORMANCE — 30
7.2 署名付きデータオブジェクトの適合性 — 30
7.3 PKI CONFORMANCE — 31
7.3 PKI適合性 — 31
8. TEST ASSERTIONS FOR THE DERIVED PIV APPLICATION — 40
8. 派生PIVアプリケーションの試験アサーション — 40
8.1 TRANSPORT LAYER CONFORMANCE — 40
8.1 トランスポート層の適合性 — 40
8.2 DERIVED PIV APPLICATION DATA OBJECT ACCESS/STORAGE CONFORMANCE — 41
8.2 派生PIVアプリケーションのデータオブジェクトのアクセス/保管に関する適合性 — 41
8.3 DERIVED PIV APPLICATION COMMAND INTERFACE CONFORMANCE — 43
8.3 派生PIVアプリケーションのコマンド・インターフェースの適合性 — 43
9. TEST ASSERTIONS FOR THE DERIVED PIV APPLICATION DATA MODEL — 88
9. 派生PIVアプリケーション・データモデルの試験アサーション — 88
9.1 BER-TLV CONFORMANCE — 88
9.1 BER-TLV適合性 — 88
9.2 SIGNED DATA OBJECT CONFORMANCE — 95
9.2 署名付きデータオブジェクトの適合性 — 95
9.3 PKI CONFORMANCE — 102
9.3 PKI適合性 — 102
List of Appendices
付録一覧
List of Figures
図一覧
List of Tables
表一覧
1. Introduction
1. はじめに
1.1 Background
1.1 背景
Federal Information Processing Standard (FIPS) 201, Personal Identity Verification (PIV) for Federal Employees and Contractors [FIPS201], specified a common set of identity credentials for the purpose of Homeland Security Presidential Directive 12 [HSPD12] in a smart card form factor, known as the PIV Card. [FIPS201] originally required that all PIV credentials and associated keys be stored on the PIV Card, and although the use of the PIV Card for electronic authentication works well with traditional desktop and laptop computers, it is not optimized for mobile devices.1
Federal Information Processing Standard(FIPS)201, Personal Identity Verification (PIV) for Federal Employees and Contractors [FIPS201] は、Homeland Security Presidential Directive 12 [HSPD12] の目的のために、PIVカードと呼ばれるスマートカード形状の共通の識別クレデンシャル群を規定しました。[FIPS201] は当初、すべてのPIVクレデンシャルと関連する鍵をPIVカードに格納することを要求していました。PIVカードを用いた電子認証は従来のデスクトップコンピュータやラップトップコンピュータではうまく機能しますが、モバイルデバイス向けには最適化されていません。1
In response to the growing use of mobile devices within the Federal Government, [FIPS201] was revised to permit the issuance of an additional credential specifically for mobile devices. This PIV credential is called a Derived PIV Credential, for which the corresponding private key is stored in a cryptographic module within a mobile device. The use of this Derived PIV Credential is restricted to provide PIV-enabled authentication services on mobile devices in order to authenticate the credential holder to remote systems.
連邦政府でのモバイル端末利用の拡大に対応し、[FIPS201]はモバイル端末専用の追加資格情報を発行できるよう改訂されました。このPIV資格情報は「派生PIV資格情報」と呼ばれ、対応する秘密鍵はモバイル端末内の暗号モジュールに保存されます。この派生PIV資格情報の用途は、モバイル端末上でPIV対応の認証サービスを提供し、資格情報の保有者をリモートシステムに対して認証することに限定されます。
1.2 Purpose and Scope
1.2 目的と適用範囲
The objective of this document is to provide test requirements and test assertions that could be used to validate the compliance/conformance of the following: (i) the Derived PIV Application and (ii) the Derived PIV data model. Because NIST Special Publication (SP) 800-157, Guidelines for Derived Personal Identity Verification (PIV) Credentials [SP800-157], was developed for meeting interoperability goals of [FIPS201], the conformance tests in this document provide the assurance that the Derived PIV Application and associated derived PIV data objects that have passed these tests are conformant to the specification. This in turn facilitates procurement of [FIPS201]-products that are interoperable and meet the goals of [HSPD12].
本文書の目的は、(i) 派生PIVアプリケーションおよび (ii) 派生PIVデータモデルの準拠性/適合性を検証するために使用できるテスト要件とテストアサーションを提供することです。NIST Special Publication(SP)800-157, Guidelines for Derived Personal Identity Verification (PIV) Credentials [SP800-157] は [FIPS201] の相互運用性の目標を満たすために策定されたものであるため、本文書の適合性テストは、これらのテストに合格した派生PIVアプリケーションおよび関連する派生PIVデータオブジェクトが仕様に適合していることを保証します。これにより、相互運用可能で [HSPD12] の目標を満たす [FIPS201] 製品の調達が容易になります。
[SP800-157] specifies the use of removable tokens with form factors that may be inserted into mobile devices, such as Secure Digital (SD) Cards, Universal Service Bus (USB) tokens, Universal Integrated Circuit Cards (UICC - the new generation of Subscriber Identity Module (SIM) cards), and non-removable tokens that are embedded in mobile devices. [SP800-157] does not define an application interface for embedded tokens, because these tokens are built into the mobile device and the interface to these tokens is natively supported. Since [SP800-157] does not specify application interface requirements for embedded tokens, testing the interfaces for embedded tokens is outside the scope of this document.2 In addition, this document does not provide conformance tests for any other software, such as the back-end access control software, issuance software, or any specialized service provider software used for logical access.
[SP800-157] は、モバイルデバイスに挿入できる形状のリムーバブルトークン(Secure Digital(SD)カード、Universal Service Bus(USB)トークン、Universal Integrated Circuit Card(UICC:新世代のSubscriber Identity Module(SIM)カード)など)と、モバイルデバイスに組み込まれた非リムーバブルトークンの使用を規定しています。組込みトークンはモバイルデバイスに内蔵され、そのインタフェースはネイティブにサポートされるため、[SP800-157] は組込みトークン用のアプリケーションインタフェースを定義していません。[SP800-157] が組込みトークンのアプリケーションインタフェース要件を規定していないことから、組込みトークンのインタフェースのテストは本文書の適用範囲外です。2また、本文書は、バックエンドのアクセス制御ソフトウェア、発行ソフトウェア、論理アクセスに用いられる特殊なサービスプロバイダソフトウェアなど、他のソフトウェアの適合性テストも提供しません。
1.3 Document Overview
1.3 文書の概要
The document is organized as follows:
本書は次のように構成されています。
+ Section 2 provides a conceptual overview of the test architecture, the test setup and components, and the types of tests (Derived PIV Application and Data Model of the Derived PIV Application) covered within this document.
+ 第2章では、試験アーキテクチャ、試験の準備と構成要素、および本書が扱う試験の種類(派生PIVアプリケーションと派生PIVアプリケーションのデータモデル)を概説します。
+ Section 3 describes the structure of the test guidelines and explains Derived test requirements (DTR) and test assertions (TA) construction.
+ 第3節では、試験ガイドラインの構成を説明し、導出試験要件(DTR)および試験アサーション(TA)の構成方法を説明します。
+ Section 4 details the conformance criteria for each type of test.
+ 第4節では、各試験種別の適合基準を詳述します。
+ Section 5 explains the documentation necessary to conduct testing.
+ 第5節では、試験実施に必要な文書を説明します。
+ Section 6 includes DTRs that apply to the Derived PIV Application based on specifications in [SP800-157].
+ 第6節では、[SP800-157]の仕様に基づき、派生PIVアプリケーションに適用されるDTRを示します。
+ Section 7 includes DTRs that apply to the Data Model of the Derived PIV Application based on specifications in [SP800-157].
+ 第7節では、[SP800-157]の仕様に基づき、派生PIVアプリケーションのデータモデルに適用されるDTRを示します。
+ Section 8 provides test assertions that are used to test the DTRs of the Derived PIV Application listed in Section 6.
+ 第8節では、第6節に示す派生PIVアプリケーションのDTRを試験するための試験アサーションを示します。
+ Section 9 provides test assertions that are used to test the DTRs of the Derived PIV Application data model listed in Section 7.
+ 第9節では、第7節に示す派生PIVアプリケーションのデータモデルのDTRを試験するための試験アサーションを示します。
+ Appendix A contains guidelines for functional and data model testing of Derived PIV Credentials on embedded (non-removable) tokens.
+ 付録Aでは、組込み型(取り外し不可)トークン上の派生PIV資格情報の機能試験およびデータモデル試験に関するガイドラインを示します。
+ Appendix B contains a list of acronyms used in the document.
+ 付録Bでは、本書で使用する略語一覧を示します。
+ Appendix C contains a glossary of terms used in the document.
+ 付録Cでは、本書で使用する用語の用語集を示します。
+ Appendix D contains the list of documents used as references by this document.
+ 付録Dでは、本書が参照する文書一覧を示します。
2. Test Overview
2. 試験の概要
2.1 Test Architecture
2.1 試験アーキテクチャ
SP 800-166 covers the following two types of tests for removable tokens: (i) Derived PIV Application and (ii) Data Model of the Derived PIV Application. The conceptual architecture for these tests is highlighted with dashed lines and shown in Figure 1.
SP 800-166では、取り外し可能なトークンを対象とする次の2種類の試験を扱います。(i) 派生PIVアプリケーション、(ii) 派生PIVアプリケーションのデータモデル。これらの試験の概念アーキテクチャを図1に破線で示します。
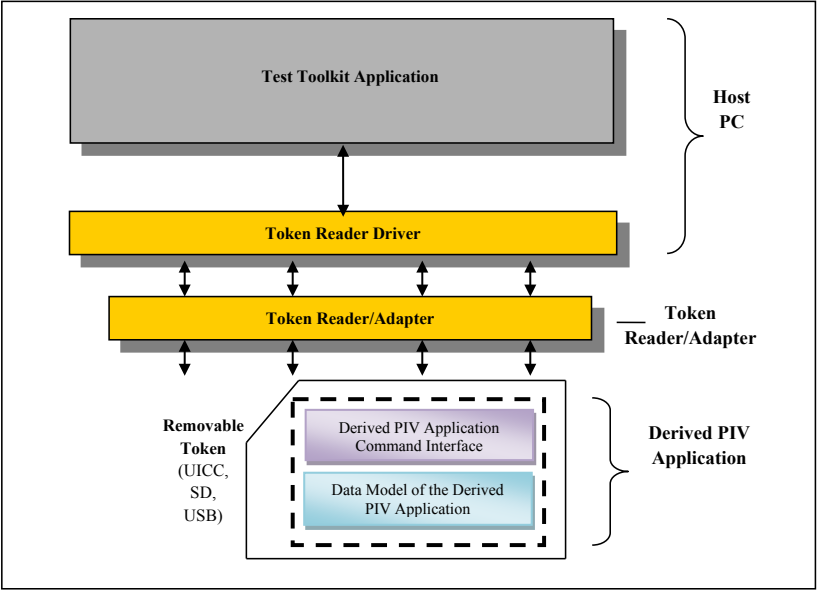
図1-派生PIVアプリケーション適合性試験アーキテクチャ。枠で囲まれた階層図である。上部の灰色の Test Toolkit Application(試験ツールキットアプリケーション)の箱が、両方向矢印で黄色の Token Reader Driver(トークンリーダードライバー)の帯と結ばれ、この2つが波括弧で Host PC(ホストPC)としてまとめられている。4本の両方向矢印が トークンリーダードライバーと黄色の Token Reader/Adapter(トークンリーダー/アダプター)の帯を結び、右側に Token Reader/Adapter と記されている。そこからさらに4本の両方向矢印が、Removable Token (UICC, SD, USB)(取り外し可能なトークン(UICC、SD、USB))と記されたトークンの輪郭へ下りる。トークンの中の破線の枠に Derived PIV Application Command Interface(派生PIVアプリケーションのコマンドインターフェース)と Data Model of the Derived PIV Application(派生PIVアプリケーションのデータモデル)の2つの箱があり、波括弧で Derived PIV Application(派生PIVアプリケーション)としてまとめられている。
Test Toolkit Application
試験ツールキットアプリケーション
Host PC
ホストPC
Token Reader Driver
トークンリーダードライバー
Token
トークン
Token Reader/Adapter
トークンリーダー/アダプター
Reader/Adapter
リーダー/アダプター
Removable
取り外し可能
Derived PIV Application
派生PIVアプリケーション
Derived PIV
派生PIV
Command Interface
コマンドインターフェース
Token
トークン
Application
アプリケーション
(UICC,
(UICC、
Data Model of the Derived
データモデル:派生
SD,
SD、
PIV Application
PIVアプリケーション
USB)
USB)
Figure 1 - Derived PIV Application Conformance Test Architecture
図1-派生PIVアプリケーション適合性試験アーキテクチャ
The Derived PIV Application resides on the removable hardware cryptographic token,3 implements the commands in the Derived PIV Application command interface,4 and provides access to data objects on the Derived PIV Application.
派生PIVアプリケーションは、取り外し可能なハードウェア暗号トークン上に存在し3、派生PIVアプリケーションのコマンドインターフェースに定義されたコマンドを実装し4、派生PIVアプリケーション上のデータオブジェクトへのアクセスを提供します。
Given that [SP800-157] does not specify an application interface or an explicit data model for embedded tokens, vendors may implement Derived PIV Credentials on these devices in a manner of their choosing. Test entities may develop test assertions to test Derived PIV Credentials implemented on such tokens using functional testing developed specifically for the environment and application that they are being used within. Appendix A provides guidelines on testing Derived PIV Credentials (i.e., Derived PIV Authentication certificates) as well as other certificates (digital signature certificate, key management certificates, etc.) that may be stored on embedded tokens.
[SP800-157]は組込み型トークン向けのアプリケーションインターフェースや明示的なデータモデルを規定していないため、ベンダーはこれらのデバイスに派生PIV資格情報を任意の方法で実装できます。試験機関は、対象の環境およびアプリケーション向けに特別に開発した機能試験を用いて、こうしたトークン上に実装された派生PIV資格情報を試験するための試験アサーションを作成できます。付録Aでは、組込み型トークンに保存される派生PIV資格情報(すなわち派生PIV認証証明書)およびその他の証明書(デジタル署名証明書、鍵管理証明書など)の試験ガイドラインを示します。
2.2 Derived PIV Application Test
2.2 派生PIVアプリケーション試験
These tests are intended to ensure that tokens with Derived PIV Applications, sold and supplied by vendors, conform to the requirements specified in SP 800-157. In general, these tests cover the following:
これらの試験は、ベンダーが販売・提供する派生PIVアプリケーション搭載トークンが、SP 800-157に規定された要件に適合していることを確認することを目的とします。一般に、試験対象は次のとおり。
+ Transport layer conformance, which ensures interoperability and portability of the Derived PIV Application token between mobile devices.
+ トランスポート層の適合性。モバイルデバイス間で派生PIVアプリケーショントークンの相互運用性および可搬性を確保します。
+ The Derived PIV Application data object access/storage conformance, which ensures that the application is set up and is conformant to [SP800-157] with regards to data object container sizes, data object identifiers, password requirements as well as the security conditions for accessing and storing each of the associated data objects.
+ 派生PIVアプリケーションのデータオブジェクトアクセス/保存の適合性。データオブジェクトのコンテナサイズ、データオブジェクト識別子、パスワード要件、各データオブジェクトのアクセス・保存に関するセキュリティ条件について、アプリケーションが適切に設定され[SP800-157]に適合していることを確認します。
+ The Derived PIV Application command interface as per [SP800-157], and includes the security conditions for executing each command in the interface with appropriate response statuses.
+ [SP800-157]に準拠した派生PIVアプリケーションのコマンドインターフェース。インターフェース内の各コマンドを実行する際のセキュリティ条件と、適切な応答ステータスを含みます。
The tests should be performed via test scripts that communicate directly with the hardware cryptographic token through the API of the associated reader drivers and includes the following categories of tests.
試験は、関連するリーダードライバーのAPIを介してハードウェア暗号トークンと直接通信する試験スクリプトで実施し、次の種類の試験を含めるべきです。
2.2.1 Transport Layer Conformance
2.2.1 トランスポート層の適合性
Transport layer conformance tests ensure that an implementation on a specific removable hardware token (i.e., UICC or USB) is compliant with industry standards specified in [SP800-157] and that portability of the token is achieved across mobile devices.
トランスポート層適合性試験では、特定の取り外し可能なハードウェアトークン(UICCまたはUSB)上の実装が[SP800-157]に規定された業界標準に準拠し、モバイルデバイス間でトークンの可搬性が確保されていることを確認します。
2.2.2 Derived PIV Application Data Object Access/Storage Conformance
2.2.2 派生PIVアプリケーションのデータオブジェクトアクセス/保存の適合性
The Derived PIV Application data object access/storage conformance tests ensure that the Derived PIV Application is set up and configured per the requirements specified in [SP800-157]. It covers requirements that apply to the removable hardware cryptographic token and includes testing that covers containers for the following data objects:
派生PIVアプリケーションのデータオブジェクトアクセス/保存適合性試験では、派生PIVアプリケーションが[SP800-157]の要件に従って設定・構成されていることを確認します。取り外し可能なハードウェア暗号トークンに適用される要件を対象とし、次のデータオブジェクト用コンテナを試験します。
+ The one mandatory data object as defined in [SP800-157]:
+ [SP800-157]に規定される必須データオブジェクト1つ:
•X.509 Certificate for Derived PIV Authentication.
•派生PIV認証用X.509証明書。
+ The twenty-five optional data objects, defined in [SP800-157]:
+ [SP800-157]に規定される任意データオブジェクト25個:
•X.509 Certificate for Digital Signature,
•デジタル署名用X.509証明書、
•X.509 Certificate for Key Management,
•鍵管理用X.509証明書、
•Discovery Object,
•検出オブジェクト、
•Key History Object,
•鍵履歴オブジェクト、
•20 Retired X.509 Certificates for Key Management, and
•20 件の廃止済み鍵管理用X.509証明書、および
•Security Object.
•セキュリティオブジェクト。
The containers will be validated for the following conditions:
各コンテナについて、次の条件を検証します。
•Presence of containers for the mandatory data object and all supported optional data objects as specified in the vendor documentation;
•ベンダ文書に規定されたとおり、必須データオブジェクトおよびサポートされるすべてのオプションデータオブジェクトのコンテナが存在すること。
•Accessibility and storage of data objects using the appropriate BER-TLV tags (specified identifiers as per Section 4, Part 1 of NIST SP 800-73, Interfaces for Personal Identity Verification [SP800-73]);
•適切なBER-TLVタグ(NIST SP 800-73, Interfaces for Personal Identity Verification [SP800-73] のPart 1, Section 4に従って規定された識別子)を用いたデータオブジェクトへのアクセスと格納。
•Appropriate container size allocations for each of the data objects;
•各データオブジェクトに対する適切なコンテナサイズの割当て。
•Data objects access rule (password vs. no password); and
•データオブジェクトのアクセス規則(パスワードの有無)、および
•Security condition for data objects access/storage (cryptographic authentication).
•データオブジェクトのアクセス/格納のためのセキュリティ条件(暗号認証)。
2.2.3 Derived PIV Application Command Interface Conformance
2.2.3 派生PIVアプリケーションのコマンドインタフェースの適合性
These tests will validate that the implementation under test can successfully execute the commands in the Derived PIV Application token command interface as mandated by [SP800-157]. Successful execution constitutes the Derived PIV Application responding with appropriate data and response status words to the commands sent by a test system. It also involves setting state variables per the specification. For example, the criteria for successful execution of the SELECT command involve the following:
これらのテストでは、テスト対象の実装が、[SP800-157] で義務付けられた派生PIVアプリケーションのトークンコマンドインタフェースのコマンドを正しく実行できることを検証します。正しい実行とは、テストシステムから送信されたコマンドに対して、派生PIVアプリケーションが適切なデータとレスポンスステータスワードを返すことをいいます。また、仕様に従って状態変数を設定することも含みます。たとえば、SELECTコマンドの正しい実行の基準は次のとおりです。
•The response status word returned is '90 00'.
•返されるレスポンスステータスワードが'90 00'です。
•The application property template is returned with the correct format and content.
•アプリケーションプロパティテンプレートが正しい形式と内容で返されます。
•The “Derived PIV Application” is the value of “currently selected application” (state variable)
•「派生PIVアプリケーション」が「現在選択されているアプリケーション」(状態変数)の値である
The Derived PIV Application token command interface test suite includes conformance tests for the following commands:
派生PIVアプリケーショントークンのコマンドインターフェース試験スイートには、次のコマンドの適合性試験が含まれます。
•Data access commands–
•データアクセスコマンド:
•SELECT
•SELECT
•GET DATA
•GET DATA
•Authentication commands–
•認証コマンド:
•GENERAL AUTHENTICATE
•GENERAL AUTHENTICATE
•VERIFY
•VERIFY
•CHANGE REFERENCE DATA
•CHANGE REFERENCE DATA
•RESET RETRY COUNTER
•RESET RETRY COUNTER
•Credential initialization and administration commands–
•クレデンシャルの初期化および管理コマンド:
•PUT DATA
•PUT DATA
•GENERATE ASYMMETRIC KEY PAIR.
•GENERATE ASYMMETRIC KEY PAIR。
The token commands will be validated against the following conditions:
トークンコマンドは次の条件に基づいて検証します。
•Precondition for use (password, cryptographic authentication),
•使用の前提条件(パスワード、暗号認証)
•Expected response status word, and
•想定されるレスポンスステータスワード
•Appropriate state variables set in the Derived PIV Application.
•派生PIVアプリケーションで設定される適切な状態変数
2.3 Data Model of the Derived PIV Application Tests
2.3 派生PIVアプリケーションのデータモデルのテスト
These tests are intended to ensure that issuers populate the containers within the Derived PIV Application with data objects that conform to [SP800-157], [SP800-73] and [SP800-78]. In general, these tests cover the following:
これらの試験は、発行者が派生PIVアプリケーション内のコンテナに、[SP800-157]、[SP800-73]、[SP800-78]に準拠するデータオブジェクトを格納していることを確認することを目的とします。一般に、試験対象は次のとおり。
•Data objects are formatted correctly,
•データオブジェクトが正しい形式である
•Field values are in accordance with the specifications, and
•フィールド値が仕様に従っている
•Data consistency and value computations such as signatures are accurate.
•データの整合性と、署名などの値の計算が正確です。
The tests should be performed via test scripts that communicate directly with the hardware cryptographic token through the API of the associated reader drivers and includes the following categories of tests.
試験は、関連するリーダードライバーのAPIを介してハードウェア暗号トークンと直接通信する試験スクリプトで実施し、次の種類の試験を含めるべきです。
2.3.1 BER-TLV Format Conformance
2.3.1 BER-TLV形式の適合性
These tests validate that the tags and lengths of various data objects conform to specifications in [SP800-157].
これらのテストでは、各種データオブジェクトのタグと長さが [SP800-157] の仕様に適合していることを検証します。
2.3.2 Signed Data Object Conformance
2.3.2 署名付きデータオブジェクトの適合性
For the Security Object, the tests check to ensure that the fields in the signature block conform to the Cryptographic Message Syntax (CMS).
セキュリティオブジェクトについては、署名ブロック内のフィールドが暗号メッセージ構文(CMS)に準拠していることを試験で確認します。
2.3.3 PKI Conformance
2.3.3 PKI適合性
The Public Key Infrastructure (PKI) conformance tests ensure that the mandatory Derived PIV Authentication certificate, the optional digital signature certificate, key management certificates, and the Derived PIV Credential Issuer’s (content signing) certificate, conform to the certificate profiles as specified in the X.509 Certificate and Certificate Revocation List (CRL) Extensions Profile for the Shared Service Providers (SSP) Program [PROF]. Additionally, the Derived PIV Application is also tested to check if asymmetric keys are pairs (public and private components) and are using the appropriate cryptographic algorithms in accordance with NIST SP 800-78, Cryptographic Algorithms and Key Sizes for Personal Identity Verification [SP800-78].
公開鍵基盤(PKI)適合性試験では、必須の派生PIV認証証明書、任意のデジタル署名証明書、鍵管理証明書、および派生PIV資格情報発行者の(コンテンツ署名用)証明書が、「共有サービスプロバイダー(SSP)プログラム向けX.509証明書および証明書失効リスト(CRL)拡張プロファイル」[PROF]に規定された証明書プロファイルに準拠していることを確認します。さらに、派生PIVアプリケーションを試験し、非対称鍵が公開鍵と秘密鍵のペアであること、およびNIST SP 800-78「個人識別確認のための暗号アルゴリズムおよび鍵長」[SP800-78]に従った適切な暗号アルゴリズムを使用していることを確認します。
2.4 Test Setup
2.4 試験のセットアップ
The test setup for the application and data model tests for the Derived PIV Application consists of the following components:
派生PIVアプリケーションのアプリケーション試験およびデータモデル試験のセットアップは、次の構成要素から成ります。
+ Test toolkit application software that resides on a personal computer (PC) with a Universal Serial Bus (USB) port;
+ ユニバーサルシリアルバス(USB)ポートを備えたパーソナルコンピュータ(PC)上で動作する試験ツールキットアプリケーションソフトウェア;
+ Readers and appropriate drivers:
+ リーダーおよび適切なドライバー:
For implementations on an SD, MiniSD or microSD token5–
SD、MiniSDまたはmicroSDトークン上の実装の場合5-
•A Secure Digital (SD) Memory Card Reader
•セキュアデジタル(SD)メモリーカードリーダー
•A Memory Card Reader Adapter (for Mini, and Micro SD Cards)
•メモリーカードリーダーアダプター(Mini SDカードおよびMicro SDカード用)
For implementation on an UICC token–
UICCトークンへの実装の場合–
•A PC/SC compliant UICC/SIM Card Reader
•PC/SC準拠のUICC/SIMカードリーダー
For implementations on micro USB–
マイクロUSBへの実装の場合–
•A Universal Micro USB to USB Cable;
•汎用マイクロUSB-USBケーブル;
+ The implementation under test (IUT), which could be either:
+ 試験対象実装(IUT)。次のいずれかである:
•A Derived PIV Application, or
•派生PIVアプリケーション、または
•The data object stored on a Derived PIV Application token.6
•派生PIVアプリケーション・トークンに格納されるデータオブジェクト。6
3. Test Guidelines Structure
3. テストガイドラインの構成
3.1 Derived Test Requirements
3.1 派生テスト要件
Derived test requirements (DTRs) identify conformity conditions based on the normative specifications in [SP800-157] and any other referenced supporting publications (e.g., [FIPS201], [SP800-73], [SP800-78]).
派生テスト要件(DTR)は、[SP800-157] の規範的な仕様と、参照されるその他の補助的な出版物(例:[FIPS201]、[SP800-73]、[SP800-78])に基づいて適合条件を特定します。
In general, each DTR consists of the following elements:
一般に、各DTRは次の要素から構成される:
1.An Identifier, which is a code starting with ‘DTR’ (Identifiers follow a running sequence based on a logical grouping of requirements);
1.識別子。これは「DTR」で始まるコードである(識別子は、要件を論理的に分類した順に連番で付与される);
2.A DTR Description, which is a statement taken/derived from the specification. These DTR descriptions include explicit statements using the words "shall," "must," and other terms used to signify the importance of the requirement; and
2.DTRの説明。仕様から引用または導出した記述です。この説明には、要件の重要性を示す「shall」「must」などの語を用いた明示的な記述が含まれる;および
3.For traceability, each DTR includes a reference to the section of [SP800-157], any other applicable specification such as [FIPS201], [SP800-73], [SP800-78] or [PROF] from which the DTR has been taken.
3.トレーサビリティを確保するため、各DTRには、そのDTRの引用元となった[SP800-157]の節、または[FIPS201]、[SP800-73]、[SP800-78]、[PROF]などの該当仕様への参照が含まれます。
3.2 Test Assertions
3.2 テストアサーション
A test assertion is an action or a set of actions that is performed to measure conformity to one or more DTRs. Test assertions provide procedures to guide the tester in executing and managing the test.
試験アサーションとは、1つ以上のDTRへの適合性を測定するために実施される単一または一連のアクションです。試験アサーションは、試験担当者が試験を実行し管理するための手順を示します。
In general, each test assertion consists of the following elements:
一般に、各試験アサーションは次の要素から構成される:
1.An Identifier, which is a code starting with ‘TA’ (Identifiers follow a running sequence based on categories of tests);
1.識別子。これは「TA」で始まるコードである(識別子は試験のカテゴリに基づき連番で付与される);
2.The Purpose of the test;
2.試験の目的;
3.For the purpose of traceability, each test assertion makes specific references to the related DTR(s). Overall there is a many-to-many relationship between test assertions and DTRs (i.e., one test assertion can map to many DTRs and one DTR can be mapped to many test assertions);
3.トレーサビリティのため、各試験アサーションは関連するDTRを具体的に参照します。試験アサーションとDTRの間には全体として多対多の関係がある(すなわち、1つの試験アサーションが複数のDTRに対応する場合も、1つのDTRが複数の試験アサーションに対応する場合もある);
4.Vendor/Issuer Documentation, which specifies the information that is needed in order to be able to execute the test. In general, vendors submit documentation for testing the Derived PIV Application while issuers submit documentation for testing the Data Model of the Derived PIV Application;
4.ベンダー/発行者の文書。試験を実行できるようにするために必要な情報を定めます。一般に、ベンダーは派生PIVアプリケーションの試験用文書を提出し、発行者は派生PIVアプリケーションのデータモデルの試験用文書を提出する;
5.Precondition(s), which describe starting conditions and any prerequisites;
5.前提条件。開始時の条件および前提要件を記述する;
6.Test Scenario, which explains the test procedure in steps;
6.試験シナリオ。試験手順を段階ごとに説明する;
7.Expected Result, which specifies the success criteria; and
7.期待される結果。成功基準を定める;および
8.Postcondition(s), which describes the final state after completion of the test scenario.
8.事後条件。試験シナリオの完了後の最終状態を記述します。
The test assertions for some of the DTRs do not have test scenarios. In such cases, documentation and/or test artifacts may be reviewed to determine compliance with the DTR.
一部のDTRに対する試験アサーションには試験シナリオがありません。そのような場合は、DTRへの適合性を判断するために、文書および/または試験成果物を確認してもよいです。
4. Conformance Criteria
4. 適合基準
Conformance criteria are based on the compliance of the “conformity condition” under the test with the requirements defined in [SP800-157] or any other referenced special publication (e.g., [FIPS201], [SP800-73], [SP800-78]) The criterion for success for each test assertion is based on the type of test being conducted.
適合基準は、試験対象の「適合条件」が[SP800-157]またはその他の参照される特別刊行物(例:[FIPS201]、[SP800-73]、[SP800-78])で定められた要件を満たしているかに基づきます。各試験アサーションの成功基準は、実施する試験の種類に基づきます。
4.1 Conformance Criteria for Derived PIV Application on Removable Tokens
4.1 着脱式トークン上の派生PIVアプリケーションの適合基準
The Derived PIV Application tests validate conformance to [SP800-157] of a Derived PIV Application developed by a vendor. The criterion for success is documented as part of the expected result or the required vendor documentation for each test assertion. Overall conformance of a removable token’s Derived PIV Application is based on passing the following three categories of tests:
派生PIVアプリケーションの試験では、ベンダーが開発した派生PIVアプリケーションが[SP800-157]に適合するかを検証します。成功基準は、各試験アサーションの期待される結果または必須のベンダー文書の一部として記載されます。着脱式トークン上の派生PIVアプリケーション全体の適合性は、次の3種類の試験すべてに合格することに基づく:
1.Transport layer conformance tests,
1.トランスポート層の適合性試験、
2.Derived PIV Application data object access/storage conformance tests, and
2.派生PIVアプリケーションのデータオブジェクトへのアクセス/保存に関する適合性試験、および
3.Derived PIV Application command interface conformance tests.
3.派生PIVアプリケーションのコマンドインターフェース適合性試験。
4.2 Conformance Criteria for Data Model of the Derived PIV Application
4.2 派生PIVアプリケーションのデータモデルの適合基準
The data model tests validate the data objects that are loaded onto a conformant Derived PIV Application’s removable token by an issuer. The criterion for success is documented as part of the expected result or the required issuer documentation for each test assertion. Overall conformance of the data model of the Derived PIV Application is based on passing the following three categories of tests:
データモデル試験では、発行者が適合する派生PIVアプリケーションの着脱式トークンに読み込むデータオブジェクトを検証します。成功基準は、各試験アサーションの期待される結果または必須の発行者文書の一部として記載されます。派生PIVアプリケーションのデータモデル全体の適合性は、次の3種類の試験すべてに合格することに基づく:
1.BER-TLV format conformance tests,
1.BER-TLV形式の適合性試験、
2.Signed Data Object conformance tests, and
2.署名付きデータオブジェクトの適合性試験、および
3.PKI conformance tests.
3.PKI適合性試験。
Testing entities may also validate individual credentials (e.g., Derived PIV Authentication certificate, digital signature certificate, key management certificate) stored on embedded (non-removable) tokens. As described in Appendix A, in many cases it will also be possible to perform functional testing of the corresponding private keys.
試験実施機関は、着脱式でないトークンに格納された個々のクレデンシャル(例:派生PIV認証証明書、電子署名証明書、鍵管理証明書)を検証してもよいです。付録Aで説明するように、多くの場合、対応する秘密鍵の機能試験も実施できます。
5. Test Documentation
5. 試験文書
There are two sets of documentation that are part of the compliance testing process: vendor/issuer provided and testing entity generated. These documentations apply to both: (i) Derived PIV Application tests and (ii) Data Model of the Derived PIV Application tests.
適合性試験のプロセスに関係する文書は、ベンダー/発行者が提供するものと試験実施機関が作成するものの2種類です。これらの文書は、(i) 派生PIVアプリケーションの試験、および (ii) 派生PIVアプリケーションのデータモデルの試験の両方に適用されます。
The vendor/issuer documentation consists of the following:
ベンダー/発行者の文書には次のものが含まれる:
+ Technical documentation: Technical details for the Derived PIV Application and its data model (as implemented). It includes, at a minimum, all the required information necessary to meet individual test assertions as documented in Section 8 (Test Assertions for the Derived PIV Application) or Section 9 (Test Assertions for the Data Model of the Derived PIV Application) of this document, depending on which tests are being performed; and
+ 技術文書:実装された派生PIVアプリケーションおよびそのデータモデルの技術的詳細。少なくとも、実施する試験に応じて、この文書の第8節(派生PIVアプリケーションの試験アサーション)または第9節(派生PIVアプリケーションのデータモデルの試験アサーション)に記載された各試験アサーションを満たすために必要な情報をすべて含む;および
+ Security-related information: (a) Derived PIV Application Password, (b) Password Unblocking Key (PUK), (c) cryptographic algorithms supported by the application, and (d) the number of unsuccessful attempts using: (i) wrong Derived PIV Application Password and (ii) wrong PUK.
+ セキュリティ関連情報:(a) 派生PIVアプリケーションのパスワード、(b) パスワードロック解除キー(PUK)、(c) アプリケーションがサポートする暗号アルゴリズム、および (d) 次の誤入力による失敗回数:(i) 誤った派生PIVアプリケーション・パスワード、(ii) 誤ったPUK。
The testing entity documents are generated during testing and report test results. They include:
試験実施機関の文書は試験中に作成され、試験結果を報告します。これらには次のものが含まれる:
+ Test logs: A test log is kept for each test run on any component and is used to summarize the results of all the tests run; and
+ 試験ログ:各コンポーネントに対する各試験実行についてログを作成し、実行したすべての試験結果の要約に用いる;および
+ Test reports: These provide the background (environmental information) for each of the test assertions as well as summary of outcomes from test runs (from test logs) associated with each test assertion.
+ 試験報告書:各試験アサーションの背景(環境情報)と、試験アサーションごとの試験実行(試験ログに記録)結果の要約を示します。
6. Derived Test Requirements for the Derived PIV Application on Removable Tokens
原本PDFの抜粋画像

6. 着脱式トークン上の派生PIVアプリケーションに関する派生試験要求事項
This section lists requirements that apply to a Derived PIV Application resident on a removable token, such as an SD card, USB token, or UICC, that may be inserted into mobile devices. The requirements are aimed towards vendors of Derived PIV Applications to ensure that these applications are implemented correctly and are in accordance to the specification.
この節では、モバイル機器に挿入できるSDカード、USBトークン、UICCなどの着脱式トークン上に存在する派生PIVアプリケーションに適用される要件を列挙します。これらの要件は、派生PIVアプリケーションが正しく実装され、仕様に準拠するよう、そのベンダーを対象としています。
6.1 Transport Layer Conformance7
6.1 トランスポート層の適合性7
6.1.1 UICC
6.1.1 UICC
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.01.01.01 | For a Universal Integrated Circuit Card (UICC) used to host a Derived PIV Application, the UICC shall implement the GlobalPlatform Card Secure Element Configuration v1.0 [GPSE]. | • [SP800-157], Section 3.3.1.2 - Removable UICC with Cryptographic Module |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.01.01.01 | 汎用集積回路カード(UICC)を 派生PIVアプリケーション のホストに使用する場合、UICCは GlobalPlatform Card Secure Element Configuration v1.0 [GPSE] を実装しなければなりません。 | • [SP800-157], 第3.3.1.2節 - Removable UICC with Cryptographic Module |
6.1.2 USB
6.1.2 USB
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.01.02.01 | For a USB Integrated Circuit(s) Card Device (ICCD) used to host a Derived PIV Application, the ICCD shall comply with the Universal Serial Bus Device Class - Smart Card ICCD Specification for USB Integrated Circuit(s) Card Devices [ICCDSPEC]. | • [SP800-157], Section 3.3.1.3 - USB Token with Cryptographic Module |
| DTR-06.01.02.02 | USB tokens with cryptographic modules that support a Derived PIV Application shall be compliant with the specifications in SP 800-96, PIV Card to Reader Interoperability Guidelines [SP800-96], for Application Protocol Data Unit (APDU) support for contact card readers. | • [SP800-157], Section 3.3.1.3 - USB Token with Cryptographic Module |
| DTR-06.01.02.03 | The APDUs for the Derived PIV Application (as specified in Appendix B of [SP800-157]) shall be transported to the secure element using the Bulk-Out command pipe and the responses shall be received from the secure element using the Bulk-In command pipe. | • [SP800-157], Section 3.3.1.3 - USB Token with Cryptographic Module |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.01.02.01 | USB Integrated Circuit(s) Card Device(ICCD)を 派生PIVアプリケーション のホストに使用する場合、ICCDは Universal Serial Bus Device Class - Smart Card ICCD Specification for USB Integrated Circuit(s) Card Devices [ICCDSPEC] に準拠しなければなりません。 | • [SP800-157], 第3.3.1.3節 - USB Token with Cryptographic Module |
| DTR-06.01.02.02 | 派生PIVアプリケーションをサポートする暗号モジュール付きUSBトークンは、接触式カードリーダー向けのアプリケーションプロトコルデータユニット(APDU)のサポートについて、SP 800-96, PIV Card to Reader Interoperability Guidelines [SP800-96] の仕様に準拠しなければなりません。 | • [SP800-157], 第3.3.1.3節 - USB Token with Cryptographic Module |
| DTR-06.01.02.03 | 派生PIVアプリケーションのAPDU([SP800-157]の付録Bに規定)は、Bulk-Outコマンドパイプを用いてセキュアエレメントに転送しなければならず、応答はBulk-Inコマンドパイプを用いてセキュアエレメントから受信しなければなりません。 | • [SP800-157], 第3.3.1.3節 - USB Token with Cryptographic Module |
6.2 Derived PIV Application Data Object Access/Storage Conformance
6.2 派生PIVアプリケーションのデータオブジェクトのアクセス/保管に関する適合性
6.2.1 General
6.2.1 一般
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.02.01.01 | The Derived PIV Application shall only support a contact interface. | • [SP800-157], Appendix B.1.2.1 - Derived PIV Application Data Object Containers and associated Access Rules |
| DTR-06.02.01.02 | There shall be at most one Derived PIV Application on any hardware cryptographic token. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.1.1 - SELECT Card Command |
| DTR-06.02.01.03 | The AID of the Derived Personal Identity Verification Application shall be: 'A0 00 00 03 08 00 00 20 00 01 00'. | • [SP800-157], Appendix B.1.1 - Derived PIV Application Identifier |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.02.01.01 | 派生PIVアプリケーションは接触インターフェースのみをサポートしなければなりません。 | • [SP800-157], 付録B.1.2.1 - 派生PIVアプリケーション Data Object Containers and associated Access Rules |
| DTR-06.02.01.02 | 任意のハードウェア暗号トークン上に存在する派生PIVアプリケーションは、多くても1つでなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.1.1節 - SELECT Card Command |
| DTR-06.02.01.03 | Derived Personal Identity Verification ApplicationのAIDは 'A0 00 00 03 08 00 00 20 00 01 00' でなければなりません。 | • [SP800-157], 付録B.1.1 - 派生PIVアプリケーション Identifier |
6.2.2 Derived PIV Application Data Objects and Representation
6.2.2 派生PIVアプリケーションのデータオブジェクトと表現
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.02.02.01 | The Derived PIV Application shall contain an X.509 Certificate for Derived PIV Authentication container and optionally the following containers: (i) X.509 Certificate for Digital Signature, (ii) X.509 Certificate for Key Management, (iii) Discovery Object, (iv) Key History Object, (v) up to 20 Retired X.509 Certificates for Key Management and (vi) Security Object. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 10 |
| DTR-06.02.02.02 | The minimum capacity for the X.509 Certificate for Derived PIV Authentication shall be 1905 bytes. | • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 7 |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.02.02.01 | 派生PIVアプリケーションは、X.509 Certificate for Derived PIV Authenticationコンテナを含まなければならず、任意で次のコンテナを含んでもよい:(i) X.509 Certificate for Digital Signature、(ii) X.509 Certificate for Key Management、(iii) Discovery Object、(iv) Key History Object、(v) 最大20個の Retired X.509 Certificates for Key Management、(vi) Security Object。 | • [SP800-157], 付録B.1.2 - 派生PIVアプリケーション Data Model Elements • [SP800-73], 第1部, 付録A - PIV Data Model, Table 10 |
| DTR-06.02.02.02 | X.509 Certificate for Derived PIV Authenticationの最小容量は1905バイトでなければなりません。 | • [SP800-73], 第1部, 付録A - PIV Data Model, Table 7 |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.02.02.03 | The minimum capacity for the X.509 Certificate for Digital Signature shall be 1905 bytes. | • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 7 |
| DTR-06.02.02.04 | The minimum capacity for the X.509 Certificate for Key Management shall be 1905 bytes. | • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 7 |
| DTR-06.02.02.05 | The minimum capacity for the Discovery Object shall be 19 bytes. | • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 7 |
| DTR-06.02.02.06 | The minimum capacity for the Key History Object shall be 128 bytes. | • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 7 |
| DTR-06.02.02.07 | The minimum capacity for each Retired X.509 Certificate for Key Management shall be 1905 bytes. | • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 7 |
| DTR-06.02.02.08 | The minimum capacity for the Security Object container shall be 3000 bytes. | • [SP800-157], Appendix B.1.2.1 - Derived PIV Application Data Object Containers and associated Access Rules |
| DTR-06.02.02.09 | The status words that may be returned on the Derived PIV Application command interface are as specified in Section 5.6 of [SP800-73], Part 1. | • [SP800-157], Appendix B.4.3 - Derived PIV Application Status Words |
| DTR-06.02.02.10 | “Basic encoding rules – tag length value” (BER-TLV) tags for the various mandatory and optional data objects within the Derived PIV Application are the same as for the corresponding data objects (mapped as per the Table B-1 of [SP800-157]) of the PIV Card Application as described in Section 4 of [SP800-73], Part 1. | • [SP800-157], Appendix B.1.3 - Derived PIV Application Data Objects Representation |
| DTR-06.02.02.11 | Key reference values used on the Derived PIV Application interfaces shall be in accordance with Table 6-1 of [SP800-78] and Table 4a and Table 4b of [SP800-73], Part 1 with the mappings defined in Table B-2 of [SP800-157]. | • [SP800-157], Appendix B.1.4.1 - Derived PIV Application Key References and Security Conditions of Use |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.02.02.03 | X.509 Certificate for Digital Signatureの最小容量は1905バイトでなければなりません。 | • [SP800-73], 第1部, 付録A - PIV Data Model, Table 7 |
| DTR-06.02.02.04 | X.509 Certificate for Key Managementの最小容量は1905バイトでなければなりません。 | • [SP800-73], 第1部, 付録A - PIV Data Model, Table 7 |
| DTR-06.02.02.05 | Discovery Objectの最小容量は19バイトでなければなりません。 | • [SP800-73], 第1部, 付録A - PIV Data Model, Table 7 |
| DTR-06.02.02.06 | Key History Objectの最小容量は128バイトでなければなりません。 | • [SP800-73], 第1部, 付録A - PIV Data Model, Table 7 |
| DTR-06.02.02.07 | 各 Retired X.509 Certificate for Key Managementの最小容量は1905バイトでなければなりません。 | • [SP800-73], 第1部, 付録A - PIV Data Model, Table 7 |
| DTR-06.02.02.08 | Security Objectコンテナの最小容量は3000バイトでなければなりません。 | • [SP800-157], 付録B.1.2.1 - 派生PIVアプリケーション Data Object Containers and associated Access Rules |
| DTR-06.02.02.09 | 派生PIVアプリケーションのコマンドインターフェースで返される場合があるステータスワードは、[SP800-73]第1部の第5 | • [SP800-157], 付録B.4.3 - 派生PIVアプリケーション Status Words |
| DTR-06.02.02.10 | 派生PIVアプリケーション内の各種の必須およびオプションのデータオブジェクトに対する「Basic encoding rules – tag length value」(BER-TLV)タグは、[SP800-73]第1部の第4節に記載されたPIV Card Applicationの対応するデータオブジェクト([SP800-157]の表B-1に従って対応付けたもの)のタグと同じです。 | • [SP800-157], 付録B.1.3 - 派生PIVアプリケーション Data Objects Representation |
| DTR-06.02.02.11 | 派生PIVアプリケーションのインターフェースで使用する鍵参照値は、[SP800-78]の表6-1、[SP800-73]第1部の表4aおよび表4bに従い、[SP800-157]の表B-2で定義された対応付けを用いなければなりません。 | • [SP800-157], 付録B.1.4.1 - 派生PIVアプリケーション Key References and Security Conditions of Use |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.02.02.12 | The algorithm identifiers for the cryptographic algorithms that may be recognized on the Derived PIV Application interfaces are the asymmetric and symmetric identifiers specified in Table 6-2 and Table 6-3 of [SP800-78]. The cryptographic mechanism identifiers that may be recognized on the Derived PIV Application interfaces are those specified in Table 5 of [SP800-73], Part 1. | • [SP800-157], Appendix B.1.4.2 - Derived PIV Application Cryptographic Algorithm and Mechanism Identifiers |
| DTR-06.02.02.13 | The Derived PIV Application Password shall be between 6 and 8 bytes in length. The Derived PIV Application shall enforce the minimum length requirement of six bytes for the Derived PIV Application Password (i.e., shall verify that at least the first six bytes of the value presented to the token command interface are in the range [0x30 – 0x39, 0x41 – 0x5A, 0x61 – 0x7A]). | • [SP800-157], Appendix B.2.1 - Authentication of an Individual |
| DTR-06.02.02.14 | If the actual length of the Derived PIV Application Password is less than 8 bytes, it shall be padded to 8 bytes with 'FF' when presented to the token command interface. The 'FF' padding bytes shall be appended to the actual value of the password. | • [SP800-157], Appendix B.2.1 - Authentication of an Individual |
| DTR-06.02.02.15 | The bytes comprising the Derived PIV Application Password shall be limited to values 0x30 – 0x39, 0x41 – 0x5A, and 0x61 – 0x7A, the ASCII values for the decimal digits '0' – '9', upper case characters 'A' – 'Z', and lower case characters 'a' – 'z' respectively. | • [SP800-157], Appendix B.2.1 - Authentication of an Individual |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.02.02.12 | 派生PIVアプリケーションのインターフェースで認識される場合がある暗号アルゴリズムのアルゴリズム識別子は、[SP800-78]の表6-2および表6-3に規定された公開鍵および共通鍵の識別子です。派生PIVアプリケーションのインターフェースで認識される場合がある暗号メカニズム識別子は、[SP800-73]第1部の表5に規定されたものです。 | • [SP800-157], 付録B.1.4.2 - 派生PIVアプリケーション Cryptographic Algorithm and Mechanism Identifiers |
| DTR-06.02.02.13 | 派生PIVアプリケーションのパスワードの長さは6〜8バイトでなければなりません。派生PIVアプリケーションは、派生PIVアプリケーションのパスワードの最小長である6バイトを強制しなければならない(すなわち、トークンのコマンドインターフェースに提示された値の少なくとも先頭6バイトが [0x30 – 0x39, 0x41 – 0x5A, 0x61 – 0x7A] の範囲にあることを検証しなければなりません)。 | • [SP800-157], 付録B.2.1 - Authentication of an Individual |
| DTR-06.02.02.14 | 派生PIVアプリケーションのパスワードの実際の長さが8バイト未満の場合、トークンのコマンドインターフェースに提示する際に 'FF' で8バイトまでパディングしなければなりません。'FF' のパディングバイトは、パスワードの実際の値の後に付加しなければなりません。 | • [SP800-157], 付録B.2.1 - Authentication of an Individual |
| DTR-06.02.02.15 | 派生PIVアプリケーションのパスワードを構成するバイトは、値 0x30 – 0x39、0x41 – 0x5A、0x61 – 0x7A に限定しなければなりません。これらはそれぞれ、10進数字 '0' – '9'、英大文字 'A' – 'Z'、英小文字 'a' – 'z' のASCII値です。 | • [SP800-157], 付録B.2.1 - Authentication of an Individual |
6.3 Derived PIV Application Command Interface Conformance
6.3 派生PIVアプリケーションのコマンドインターフェース適合性
6.3.1 General
6.3.1 一般
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.01.01 | The command interface for the Derived PIV Application shall implement all of the card commands supported by the PIV Card Application as described in [SP800-73], Part 2, which include: SELECT, GET DATA, VERIFY, CHANGE REFERENCE DATA, RESET RETRY COUNTER, GENERAL AUTHENTICATE, PUT DATA, GENERATE ASYMMETRIC KEY PAIR. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.01.01 | 派生PIVアプリケーションのコマンドインターフェースは、[SP800-73]第2部に記載されたPIV Card Applicationがサポートするすべてのカードコマンドを実装しなければなりません。これには、SELECT、GET DATA、VERIFY、CHANGE REFERENCE DATA、RESET RETRY COUNTER、GENERAL AUTHENTICATE、PUT DATA、GENERATE ASYMMETRIC KEY PAIR が含まれます。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.01.02 | Token commands indicated with a 'Yes' in the Command Chaining column in Table 2 of [SP800-73], Part 2 shall support command chaining for transmitting a data string too long for a single command as defined in [ISO7816-4]. | • [SP800-73], Part 2, Section 3 - PIV Card Application Card Command Interface |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.01.02 | [SP800-73]第2部の表2のCommand Chaining列に 'Yes' と示されたトークンコマンドは、[ISO7816-4]で定義されているとおり、1つのコマンドには長すぎるデータ列を送信するためのコマンドチェーンをサポートしなければなりません。 | • [SP800-73], 第2部, 第3節 - PIV Card Application Card Command Interface |
6.3.2 SELECT Command
6.3.2 SELECTコマンド
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.02.01 | The Derived PIV Application can be selected as the current application on the removable hardware cryptographic token by providing the full AID as follows: 'A0 00 00 03 08 00 00 20 00 01 00'. | • [SP800-157], Appendix B.1.1 - Derived PIV Application Identifier |
| DTR-06.03.02.02 | The token platform shall support a default selected application. In other words, there shall be a currently selected application immediately after a cold or warm reset. This application is the default selected application. The default application may be the Derived PIV Application, or it may be another application. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface |
| DTR-06.03.02.03 | Upon selection, the Derived PIV Application shall return the application property template described in Table 3 of [SP800-73], Part 2, with the exception that the returned AID is the AID listed in Appendix B.1.1 of [SP800-157]. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.1.1 - SELECT Card Command |
| DTR-06.03.02.04 | The Derived PIV Application can also be made the currently selected application by providing a right-truncated version – that is, without the two-byte version number, '01 00' – in the data field of the SELECT command 'A0 00 00 03 08 00 00 20 00' | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.1.1 - SELECT Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.02.01 | 派生PIVアプリケーションは、完全なAID 'A0 00 00 03 08 00 00 20 00 01 00' を指定することで、取り外し可能なハードウェア暗号トークン上の現在のアプリケーションとして選択できます。 | • [SP800-157], 付録B.1.1 - 派生PIVアプリケーション Identifier |
| DTR-06.03.02.02 | トークンプラットフォームは、デフォルトで選択されるアプリケーションをサポートしなければなりません。つまり、コールドリセットまたはウォームリセットの直後に、現在選択されているアプリケーションが存在しなければなりません。このアプリケーションがデフォルトで選択されるアプリケーションです。デフォルトのアプリケーションは、派生PIVアプリケーションでもよく、別のアプリケーションでもよいです。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface |
| DTR-06.03.02.03 | 選択時、派生PIVアプリケーションは、[SP800-73]第2部の表3に記載されたapplication property templateを返さなければなりません。ただし、返されるAIDは[SP800-157]の付録B | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.1.1節 - SELECT Card Command |
| DTR-06.03.02.04 | 派生PIVアプリケーションは、SELECTコマンドのデータフィールドに右側を切り詰めた版、すなわち2バイトのバージョン番号 '01 00' を除いた 'A0 00 00 03 08 00 00 20 00' を指定することでも、現在選択されているアプリケーションにできます。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.1.1節 - SELECT Card Command |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.02.05 | The complete AID, including the two-byte version, of the Derived PIV Application that became the currently selected application upon successful execution of the SELECT command (using the full or right-truncated PIV AID) shall be returned in the application property template. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.1.1 - SELECT Card Command |
| DTR-06.03.02.06 | If the currently selected application is the Derived PIV Application when the SELECT command is sent and the AID in the data field of the SELECT command is either the AID of the Derived PIV Application or its right-truncated version thereof, then the Derived PIV Application shall continue to be the currently selected application and the setting of all security status indicators in the Derived PIV Application shall be unchanged. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.1.1 - SELECT Card Command |
| DTR-06.03.02.07 | If the currently selected application is the Derived PIV Application when the SELECT command is sent and the AID in the data field of the SELECT command is an invalid AID, then the Derived PIV Application shall remain the currently selected application and the Derived PIV Application security status indicator shall remain unchanged. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.1.1 - SELECT Card Command |
| DTR-06.03.02.08 | If the currently selected application is the Derived PIV Application when the SELECT command is given and the AID in the data field of the SELECT command is not the Derived PIV Application (nor the right-truncated version thereof), but a valid AID supported by the token, then the Derived PIV Application shall be deselected and the Derived PIV Application security status indicators in the Derived PIV Application shall be set to FALSE. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.1.1 - SELECT Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.02.05 | SELECTコマンド(完全なPIV AIDまたは右側を切り詰めたPIV AIDを使用)の実行が成功して現在選択されているアプリケーションになった派生PIVアプリケーションの、2バイトのバージョンを含む完全なAIDは、application property templateで返さなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.1.1節 - SELECT Card Command |
| DTR-06.03.02.06 | SELECTコマンドの送信時に現在選択されているアプリケーションが派生PIVアプリケーションであり、SELECTコマンドのデータフィールドのAIDが派生PIVアプリケーションのAIDまたはその右側を切り詰めた版のいずれかである場合、派生PIVアプリケーションは引き続き現在選択されているアプリケーションでなければならず、派生PIVアプリケーション内のすべてのセキュリティ状態インジケータの設定は変更されてはなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.1.1節 - SELECT Card Command |
| DTR-06.03.02.07 | SELECTコマンドの送信時に現在選択されているアプリケーションが派生PIVアプリケーションであり、SELECTコマンドのデータフィールドのAIDが無効なAIDである場合、派生PIVアプリケーションは引き続き現在選択されているアプリケーションでなければならず、派生PIVアプリケーションのセキュリティ状態インジケータは変更されてはなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.1.1節 - SELECT Card Command |
| DTR-06.03.02.08 | SELECTコマンドの送信時に現在選択されているアプリケーションが派生PIVアプリケーションであり、SELECTコマンドのデータフィールドのAIDが派生PIVアプリケーション(またはその右側を切り詰めた版)ではなく、トークンがサポートする有効なAIDである場合、派生PIVアプリケーションの選択を解除しなければならず、派生PIVアプリケーション内のセキュリティ状態インジケータをFALSEに設定しなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.1.1節 - SELECT Card Command |
6.3.3 GET DATA Command
6.3.3 GET DATAコマンド
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.03.01 | The GET DATA command retrieves the data content of the single data object whose tag is given in the data field. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.1.2 - GET DATA Card Command |
| DTR-06.03.03.02 | The Lc value is '05' for all Derived PIV data objects except for the 0x7E interindustry tag (Discovery Object), which has an Lc value of '03'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.1.2 - GET DATA Card Command |
| DTR-06.03.03.03 | The GET RESPONSE command is used in conjunction with GET DATA to accomplish the reading of larger Derived PIV data objects. | • [SP800-73], Part 2, Section 3.1.2 - GET DATA Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.03.01 | GET DATAコマンドは、データフィールドで指定されたタグを持つ単一のデータオブジェクトのデータ内容を取得します。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.1.2節 - GET DATA Card Command |
| DTR-06.03.03.02 | Lc の値は、0x7E interindustryタグ(Discovery Object)を除くすべてのDerived PIVデータオブジェクトで '05' であり、0x7E interindustryタグ(Discovery Object)では Lc の値は '03' です。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.1.2節 - GET DATA Card Command |
| DTR-06.03.03.03 | GET RESPONSEコマンドは、GET DATAと組み合わせて、より大きなDerived PIVデータオブジェクトの読み取りを行うために使用します。 | • [SP800-73], 第2部, 第3.1.2節 - GET DATA Card Command |
6.3.4 GENERAL AUTHENTICATE Command
6.3.4 GENERAL AUTHENTICATEコマンド
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.04.01 | The GENERAL AUTHENTICATE command shall be used with the Derived PIV authentication keys ('9A' and '9B') using cryptographic algorithms from Table 6-2 of [SP800-78] to authenticate the token or a token application to the client application (INTERNAL AUTHENTICATE), to authenticate an entity to the token (EXTERNAL AUTHENTICATE), and to perform a mutual authentication between the token and an entity external to the token (MUTUAL AUTHENTICATE). | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.4 - GENERAL AUTHENTICATE Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.04.01 | GENERAL AUTHENTICATEコマンドは、[SP800-78]の表6-2の暗号アルゴリズムを用いて、Derived PIV認証鍵('9A' および '9B')とともに使用し、トークンまたはトークンアプリケーションをクライアントアプリケーションに対して認証し(INTERNAL AUTHENTICATE)、エンティティをトークンに対して認証し(EXTERNAL AUTHENTICATE)、トークンとトークン外部のエンティティとの間で相互認証を行う(MUTUAL AUTHENTICATE)ために使用しなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.4節 - GENERAL AUTHENTICATE Card Command |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.04.02 | The GENERAL AUTHENTICATE command shall be used with the digital signature key ('9C') (if implemented) to realize the signing functionality on the Derived PIV Application programming interface using cryptographic algorithms specified in Table 3-1 of [SP800-78]. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.4 - GENERAL AUTHENTICATE Card Command |
| DTR-06.03.04.03 | The GENERAL AUTHENTICATE command shall be used with the key management key ('9D') (if implemented) and the retired key management keys ('82' – '95') (if implemented) to realize key establishment schemes specified in [SP800-78] (ECDH and RSA). | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.4 - GENERAL AUTHENTICATE Card Command |
| DTR-06.03.04.04 | The GENERAL AUTHENTICATE command supports command chaining to permit the uninterrupted transmission of long command data fields to the Derived PIV Application. If a token command other than the GENERAL AUTHENTICATE command is received by the Derived PIV Application before the termination of a GENERAL AUTHENTICATE chain, then the Derived PIV Application shall rollback to the state it was in immediately prior to the reception of the first command in the interrupted chain. In other words, an interrupted GENERAL AUTHENTICATE chain has no effect on the Derived PIV Application. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.4 - GENERAL AUTHENTICATE Card Command |
| DTR-06.03.04.05 | For cryptographic operations with larger keys, e.g., RSA 2048, the GET RESPONSE command is used to return the complete result of the cryptographic operation. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.4 - GENERAL |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.04.02 | GENERAL AUTHENTICATEコマンドは、[SP800-78]の表3-1に規定された暗号アルゴリズムを用いて、派生PIVアプリケーションのプログラミングインターフェース上で署名機能を実現するために、デジタル署名鍵('9C')(実装されている場合)とともに使用しなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.4節 - GENERAL AUTHENTICATE Card Command |
| DTR-06.03.04.03 | GENERAL AUTHENTICATEコマンドは、[SP800-78]に規定された鍵確立方式(ECDHおよびRSA)を実現するために、鍵管理鍵('9D')(実装されている場合)および廃止済み鍵管理鍵('82' – '95')(実装されている場合)とともに使用しなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.4節 - GENERAL AUTHENTICATE Card Command |
| DTR-06.03.04.04 | GENERAL AUTHENTICATEコマンドは、長いコマンドデータフィールドを派生PIVアプリケーションへ中断なく送信できるよう、コマンドチェーンをサポートします。GENERAL AUTHENTICATEチェーンが終了する前に、GENERAL AUTHENTICATE以外のトークンコマンドを派生PIVアプリケーションが受信した場合、派生PIVアプリケーションは、中断されたチェーンの最初のコマンドを受信する直前の状態にロールバックしなければなりません。つまり、中断されたGENERAL AUTHENTICATEチェーンは派生PIVアプリケーションに影響を与えません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.4節 - GENERAL AUTHENTICATE Card Command |
| DTR-06.03.04.05 | RSA 2048などのより大きな鍵を用いる暗号操作では、GET RESPONSEコマンドを使用して暗号操作の完全な結果を返します。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.4節 - GENERAL |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| AUTHENTICATE Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| AUTHENTICATE Card Command |
6.3.5 VERIFY Command
6.3.5 VERIFYコマンド
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.05.01 | Key reference '80' shall be able to be verified by the Derived PIV Application VERIFY command. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.1 - VERIFY Card Command |
| DTR-06.03.05.02 | When the key reference is '80' and the current value of the retry counter associated with the key reference is zero, then the comparison shall not be made, and the Derived PIV Application shall return the status word '69 83'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.1 - VERIFY Card Command |
| DTR-06.03.05.03 | When the key reference is '80' and the authentication data in the command data field does not satisfy the criteria in Appendix B.2.1 of [SP800-157], then the token command shall fail and the Derived PIV Application shall return either the status word '6A 80' or '63 CX'. If status word '6A 80' is returned, the security status and the retry counter of the key reference shall remain unchanged. If status word '63 CX' is returned, the security status of the key reference shall be set to FALSE and the retry counter associated with the key reference shall be decremented by one. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.1 - VERIFY Card Command |
| DTR-06.03.05.04 | When the key reference is '80' and the authentication data in the command data field is properly formatted and does not match reference data associated with the key reference, then the token command shall fail, the Derived PIV | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.05.01 | 鍵参照 '80' は、派生PIVアプリケーションのVERIFYコマンドで検証できなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.1節 - VERIFY Card Command |
| DTR-06.03.05.02 | 鍵参照が '80' で、その鍵参照に関連付けられたリトライカウンタの現在値がゼロの場合、比較を行ってはならず、派生PIVアプリケーションはステータスワード '69 83' を返さなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.1節 - VERIFY Card Command |
| DTR-06.03.05.03 | 鍵参照が '80' で、コマンドデータフィールド内の認証データが[SP800-157]の付録B | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.1節 - VERIFY Card Command |
| DTR-06.03.05.04 | 鍵参照が '80' で、コマンドデータフィールド内の認証データが正しい形式であり、その鍵参照に関連付けられた参照データと一致しない場合、トークンコマンドは失敗しなければならず、派生PIVアプリケーション | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| Application shall return the status word '63 CX', the security status of the key reference shall be set to FALSE, and the retry counter associated with the key reference (i.e., '80') shall be decremented by one. | • [SP800-73], Part 2, Section 3.2.1 - VERIFY Card Command | |
| DTR-06.03.05.05 | If P1='FF', and Lc and the command data field are absent, the command shall reset the security status of the key reference in P2. The security status of the key reference specified in P2 shall be set to FALSE and the retry counter associated with the key reference shall remain unchanged. | • [SP800-73], Part 2, Section 3.2.1 - VERIFY Card Command |
| DTR-06.03.05.06 | If the token command succeeds, then the security status of the key reference (i.e., '80') shall be set to TRUE and the retry counter associated with the key reference shall be set to the reset retry value associated with the key reference. | • [SP800-73], Part 2, Section 3.2.1 - VERIFY Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| Applicationはステータスワード '63 CX' を返さなければならず、その鍵参照のセキュリティ状態はFALSEに設定しなければならず、その鍵参照(すなわち '80')に関連付けられたリトライカウンタは1減らさなければなりません。 | • [SP800-73], 第2部, 第3.2.1節 - VERIFY Card Command | |
| DTR-06.03.05.05 | P1='FF' で、Lc とコマンドデータフィールドが存在しない場合、このコマンドは P2 の鍵参照のセキュリティ状態をリセットしなければなりません。P2 で指定された鍵参照のセキュリティ状態はFALSEに設定しなければならず、その鍵参照に関連付けられたリトライカウンタは変更されてはなりません。 | • [SP800-73], 第2部, 第3.2.1節 - VERIFY Card Command |
| DTR-06.03.05.06 | トークンコマンドが成功した場合、その鍵参照(すなわち '80')のセキュリティ状態はTRUEに設定しなければならず、その鍵参照に関連付けられたリトライカウンタは、その鍵参照に関連付けられたリセットリトライ値に設定しなければなりません。 | • [SP800-73], 第2部, 第3.2.1節 - VERIFY Card Command |
6.3.6 CHANGE REFERENCE DATA Command
6.3.6 CHANGE REFERENCE DATAコマンド
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.06.01 | Only reference data associated with key references '80' and '81' specific to the Derived PIV Application (i.e., local key references) may be changed by the Derived PIV Application CHANGE REFERENCE DATA command. The PIV Card Application may allow the reference data associated with other key references to be changed by the PIV Card Application CHANGE REFERENCE DATA, if PIV Card Application will only perform the command with other key references if the requirements specified in Section 2.9.2 of FIPS 201-2 are satisfied. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.2 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.02 | If any key reference value is specified that is not supported by the card, the Derived PIV Application shall return the status word '6A 88'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.2 - CHANGE REFERENCE DATA Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.06.01 | 派生PIVアプリケーションのCHANGE REFERENCE DATAコマンドで変更できるのは、派生PIVアプリケーション固有の鍵参照 '80' および '81'(すなわちローカル鍵参照)に関連付けられた参照データのみです。PIV Card Applicationが、FIPS 201-2の第2 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.2節 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.02 | カードがサポートしていない鍵参照値が指定された場合、派生PIVアプリケーションはステータスワード '6A 88' を返さなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.2節 - CHANGE REFERENCE DATA Card Command |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.06.03 | Key reference '80' reference data shall be changed by the Derived PIV Application CHANGE REFERENCE DATA command. The ability to change reference data associated with key references '81' using the Derived PIV Application CHANGE REFERENCE DATA command is optional. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.2 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.04 | If the current value of the retry counter associated with the key reference is zero, then the reference data associated with the key reference (i.e., '80' or '81') shall not be changed and the Derived PIV Application shall return the status word '69 83'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.2 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.05 | If the authentication data in the command data field does not match the current value of the reference data or if either the authentication data or the new reference data in the command data field of the command does not satisfy the criteria in Appendix B.2.1 of [SP800-157] (for the Derived PIV Application Password) or the criteria in Section 2.4.3 of [SP800-73], Part 2 (for the PUK), the Derived PIV Application shall not change the reference data associated with the key reference and shall return either status word '6A 80' or '63 CX'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.2 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.06 | If the authentication data in the command data field satisfies the criteria in Appendix B.2.1 of [SP800-157] (for the Derived PIV Application Password) or the criteria in Section 2.4.3 of [SP800-73], Part 2 (for the PUK), and matches the current value of the reference data, but the new reference data in the command data field of the command does not satisfy the criteria in Appendix B.2.1 of [SP800-157] (for the Derived | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.2 - CHANGE REFERENCE |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.06.03 | 鍵参照 '80' の参照データは、派生PIVアプリケーションのCHANGE REFERENCE DATAコマンドで変更されなければなりません。派生PIVアプリケーションのCHANGE REFERENCE DATAコマンドで鍵参照 '81' に関連付けられた参照データを変更する機能は、オプションです。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.2節 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.04 | 鍵参照に関連付けられたリトライカウンタの現在値がゼロの場合、その鍵参照(すなわち '80' または '81')に関連付けられた参照データを変更してはならず、派生PIVアプリケーションはステータスワード '69 83' を返さなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.2節 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.05 | コマンドデータフィールド内の認証データが参照データの現在値と一致しない場合、または、コマンドのコマンドデータフィールド内の認証データか新しい参照データのいずれかが、[SP800-157]の付録B | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.2節 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.06 | コマンドデータフィールド内の認証データが[SP800-157]の付録B | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.2節 - CHANGE REFERENCE |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| PIV Application Password) or the criteria in Section 2.4.3 of [SP800-73], Part 2 (for the PUK), the Derived PIV Application shall return status word '6A 80'. | DATA Card Command | |
| DTR-06.03.06.07 | If the authentication data in the command data field does not match the current value of the reference data, but both the authentication data and the new reference data in the command data field of the command satisfy the criteria in Appendix B.2.1 of [SP800-157] (for the Derived PIV Application Password) or the criteria in Section 2.4.3 of [SP800-73], Part 2 (for the PUK), the Derived PIV Application shall return status word '63 CX'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.2 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.08 | If status word '6A 80' is returned, the security status and retry counter associated with the key reference shall remain unchanged. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.2 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.09 | If status word '63 CX' is returned, the security status of the key reference shall be set to FALSE and the retry counter associated with the key reference shall be decremented by one. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.2 - CHANGE REFERENCE DATA Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| または[SP800-73]第2部の第2 | DATA Card Command | |
| DTR-06.03.06.07 | コマンドデータフィールド内の認証データが参照データの現在値と一致しませんが、コマンドのコマンドデータフィールド内の認証データと新しい参照データの両方が[SP800-157]の付録B | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.2節 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.08 | ステータスワード '6A 80' が返された場合、その鍵参照に関連付けられたセキュリティ状態とリトライカウンタは変更されてはなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.2節 - CHANGE REFERENCE DATA Card Command |
| DTR-06.03.06.09 | ステータスワード '63 CX' が返された場合、その鍵参照のセキュリティ状態はFALSEに設定しなければならず、その鍵参照に関連付けられたリトライカウンタは1減らさなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.2節 - CHANGE REFERENCE DATA Card Command |
6.3.7 RESET RETRY COUNTER Command
6.3.7 RESET RETRY COUNTERコマンド
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.07.01 | The only key reference allowed in the P2 parameter of the RESET RETRY COUNTER command is the Derived PIV Application Password (i.e., key reference '80'). The PIV Card Application may allow the reference data associated with other key references to be changed by the PIV Card Application RESET RETRY COUNTER, if PIV Card Application will only perform the command with other key references if the requirements specified in Section 2.9.2 of FIPS 201-2 are satisfied. If a key reference is specified in P2 that is not supported by the card, the Derived PIV Application shall return the status word '6A 88'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.3 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.02 | If the current value of the PUK’s retry counter is zero then the password’s retry counter shall not be reset and the Derived PIV Application shall return the status word '69 83'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.3 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.03 | If the reset retry counter authentication data (PUK) in the command data field of the command does not match reference data associated with the PUK then the Derived PIV Application shall return the status word '63 CX'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.3 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.04 | If the new reference data (password) in the command data field of the command does not satisfy the criteria in Appendix B.2.1 of [SP800-157], then the Derived PIV Application shall return the status word '6A 80'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.07.01 | RESET RETRY COUNTERコマンドのP2パラメータで許可される鍵参照は、派生PIVアプリケーションのパスワード(すなわち鍵参照 '80')のみです。PIV Card Applicationが、FIPS 201-2の第2 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.3節 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.02 | PUKのリトライカウンタの現在値がゼロの場合、パスワードのリトライカウンタをリセットしてはならず、派生PIVアプリケーションはステータスワード '69 83' を返さなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.3節 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.03 | コマンドのコマンドデータフィールド内のリセットリトライカウンタ認証データ(PUK)が、PUKに関連付けられた参照データと一致しない場合、派生PIVアプリケーションはステータスワード '63 CX' を返さなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.3節 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.04 | コマンドのコマンドデータフィールド内の新しい参照データ(パスワード)が[SP800-157]の付録B | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| Section 3.2.3 - RESET RETRY COUNTER Card Command | ||
| DTR-06.03.07.05 | If the reset retry counter authentication data (PUK) in the command data field of the command does not match reference data associated with the PUK and the new reference data (password) in the command data field of the command does not satisfy the criteria in Appendix B.2.1 of [SP800-157], then the Derived PIV Application shall return either status word '6A 80' or '63 CX'. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.3 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.06 | If the Derived PIV Application returns status word '6A 80' then the retry counter associated with the password shall not be reset, the security status of the password’s key reference shall remain unchanged, and the PUK’s retry counter shall remain unchanged. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.3 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.07 | If the Derived PIV Application returns status word '63 CX', then the retry counter associated with the password shall not be reset, the security status of the password’s key reference shall be set to FALSE, and the PUK’s retry counter shall be decremented by one. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.3 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.08 | If the token command succeeds, then the password’s retry counter shall be set to its reset retry value. Optionally, the PUK’s retry counter may be set to its initial reset retry value. The security status of the password’s key reference shall not be changed. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.3 - |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| Section 3.2.3 - RESET RETRY COUNTER Card Command | ||
| DTR-06.03.07.05 | コマンドのコマンドデータフィールド内のリセットリトライカウンタ認証データ(PUK)がPUKに関連付けられた参照データと一致せず、かつコマンドのコマンドデータフィールド内の新しい参照データ(パスワード)が[SP800-157]の付録B | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.3節 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.06 | 派生PIVアプリケーションがステータスワード '6A 80' を返す場合、パスワードに関連付けられたリトライカウンタはリセットされてはならず、パスワードの鍵参照のセキュリティ状態は変更されてはならず、PUKのリトライカウンタは変更されてはなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.3節 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.07 | 派生PIVアプリケーションがステータスワード '63 CX' を返す場合、パスワードに関連付けられたリトライカウンタはリセットされてはならず、パスワードの鍵参照のセキュリティ状態はFALSEに設定しなければならず、PUKのリトライカウンタは1減らさなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.3節 - RESET RETRY COUNTER Card Command |
| DTR-06.03.07.08 | トークンコマンドが成功した場合、パスワードのリトライカウンタはそのリセットリトライ値に設定しなければなりません。任意で、PUKのリトライカウンタを初期のリセットリトライ値に設定してもよいです。パスワードの鍵参照のセキュリティ状態は変更されてはなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.3節 - |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| RESET RETRY COUNTER Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| RESET RETRY COUNTER Card Command |
6.3.8 PUT DATA Command
6.3.8 PUT DATAコマンド
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.08.01 | The PUT DATA command shall completely replace the data content of a single data object in the Derived PIV Application with new content. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.5 - PUT DATA Card Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.08.01 | PUT DATAコマンドは、派生PIVアプリケーション内の単一のデータオブジェクトのデータ内容を、新しい内容で完全に置き換えなければなりません。 | • [SP800-157], 付録B.2 - 派生PIVアプリケーション Token Command Interface • [SP800-73], 第2部, 第3.2.5節 - PUT DATA Card Command |
6.3.9 GENERATE ASYMMETRIC KEY PAIR Command
6.3.9 GENERATE ASYMMETRIC KEY PAIRコマンド
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-06.03.09.01 | The GENERATE ASYMMETRIC KEY PAIR command initiates the generation and storing in the token of the reference data of an asymmetric key pair, i.e., a public key and a private key. The public key of the generated key pair is returned as the response to the command. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.6 - GENERATE ASYMMETRIC KEY PAIR Command |
| DTR-06.03.09.02 | If there is reference data currently associated with the key reference, it is replaced in full by the generated data. | • [SP800-157], Appendix B.2 - Derived PIV Application Token Command Interface • [SP800-73], Part 2, Section 3.2.6 - GENERATE ASYMMETRIC KEY PAIR Command |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-06.03.09.01 | GENERATE ASYMMETRIC KEY PAIRコマンドは、非対称鍵ペア、すなわち公開鍵と秘密鍵を生成してトークンに格納する処理を開始します。生成された鍵ペアの公開鍵は、コマンドへの応答として返されます。 | • [SP800-157], 付録B.2 - Derived PIV Application Token Command Interface • [SP800-73], 第2部, 第3.2.6節 - GENERATE ASYMMETRIC KEY PAIR Command |
| DTR-06.03.09.02 | 現在その鍵参照に関連付けられた参照データがある場合、それは生成されたデータで全体が置き換えられます。 | • [SP800-157], 付録B.2 - Derived PIV Application Token Command Interface • [SP800-73], 第2部, 第3.2.6節 - GENERATE ASYMMETRIC KEY PAIR Command |
7. Derived Test Requirements for Data Model of the Derived PIV Application
7. 派生PIVアプリケーションのデータモデルに関する導出試験要件
This section lists requirements that apply to the Data Model of the Derived PIV Application. They are aimed towards issuers of tokens to ensure that Derived PIV Application data objects are formatted correctly and field values are in accordance to the specification.
この節では、派生PIVアプリケーションのデータモデルに適用される要件を列挙します。これらは、派生PIVアプリケーションのデータオブジェクトが正しく形式化され、フィールド値が仕様に準拠するよう、トークンの発行者を対象としています。
7.1 BER-TLV Conformance
7.1 BER-TLV適合性
7.1.1 General
7.1.1 一般
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.01.01.01 | Before the card is issued, data objects that are created but not used shall be set to zero-length value. | • [SP800-73], Part 1, Section 4.1.1 - Data Object Content |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.01.01.01 | カードが発行される前に、作成されたが使用されないデータオブジェクトは、長さゼロの値に設定しなければなりません。 | • [SP800-73], 第1部, 第4.1.1節 - Data Object Content |
7.1.2 X.509 Certificate for Derived PIV Authentication
7.1.2 派生PIV認証用X.509証明書
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.01.02.01 | The X.509 Certificate for Derived PIV Authentication shall include all the Tag-Length-Value (TLV) elements in Table 10 of [SP800-73], Part 1 in the order listed. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 10 |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.01.02.01 | X.509 Certificate for Derived PIV Authenticationは、[SP800-73]第1部の表10にあるすべてのTag-Length-Value(TLV)要素を、列挙された順序で含まなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], 第1部, 付録A - PIV Data Model, Table 10 |
7.1.3 X.509 Certificate for Digital Signature
7.1.3 デジタル署名用X.509証明書
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.01.03.01 | If implemented, the X.509 Certificate for Digital Signature data object shall include all the TLV elements in Table 15 of [SP800-73], Part 1 in the order listed. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 15 |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.01.03.01 | X.509 Certificate for Digital Signatureデータオブジェクトが実装されている場合、X | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], 第1部, 付録A - PIV Data Model, Table 15 |
7.1.4 X.509 Certificate for Key Management
7.1.4 鍵管理用X.509証明書
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.01.04.01 | If implemented, the X.509 Certificate for Key Management data object shall include all the TLV elements in Table 16 of [SP800-73], Part 1 in the order listed. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 16 |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.01.04.01 | X.509 Certificate for Key Managementデータオブジェクトが実装されている場合、X | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], 第1部, 付録A - PIV Data Model, Table 16 |
7.1.5 Discovery Object
7.1.5 Discovery Object
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.01.05.01 | If implemented, the Discovery Object shall include all the TLV elements in Table 18 of [SP800-73], Part 1 in the order listed. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 18 |
| DTR-07.01.05.02 | If the Discovery Object is implemented, the first byte of the PIN Usage Policy shall be set to 0x40. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.01.05.03 | If the Discovery Object is implemented, the second byte of the PIN Usage Policy shall be set to 0x00. | • [SP800-73], Part 1, Section 3.3.2 – Discovery Object |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.01.05.01 | 実装されている場合、Discovery Objectは、[SP800-73]第1部の表18にあるすべてのTLV要素を、列挙された順序で含まなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], 第1部, 付録A - PIV Data Model, Table 18 |
| DTR-07.01.05.02 | Discovery Objectが実装されている場合、PIN Usage Policyの第1バイトは0x40に設定しなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.01.05.03 | Discovery Objectが実装されている場合、PIN Usage Policyの第2バイトは0x00に設定しなければなりません。 | • [SP800-73], 第1部, 第3.3.2節 – Discovery Object |
7.1.6 Key History Object
7.1.6 Key History Object
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.01.06.01 | If implemented, the Key History Object shall include all the TLV elements in Table 19 of [SP800-73], Part 1 in the order listed. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], Part 1, Appendix A - PIV |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.01.06.01 | 実装されている場合、Key History Objectは、[SP800-73]第1部の表19にあるすべてのTLV要素を、列挙された順序で含まなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], 第1部, 付録A - PIV Data Model |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| Data Model, Table 19 |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| Data Model, Table 19 |
7.1.7 Retired X.509 Certificates for Key Management
7.1.7 廃止済み鍵管理用X.509証明書
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.01.07.01 | If implemented, the Retired X.509 Certificate for Key Management data objects shall include all the TLV elements in Tables 20 - 39 of [SP800-73], Part 1 in the order listed. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 20-Table 39 |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.01.07.01 | 実装されている場合、Retired X.509 Certificate for Key Managementデータオブジェクトは、[SP800-73]第1部の表20〜39にあるすべてのTLV要素を、列挙された順序で含まなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], 第1部, 付録A - PIV Data Model, Table 20-Table 39 |
7.1.8 Security Object
7.1.8 Security Object
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.01.08.01 | If implemented, the Security Object shall include all the TLV elements in Table 12 of [SP800-73], Part 1 in the order listed. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], Part 1, Appendix A - PIV Data Model, Table 12 |
| DTR-07.01.08.02 | The Security Object shall be present in the Derived PIV Application if either the Discovery Object or the Key History object is present, and shall be absent otherwise. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.01.08.03 | All unsigned data objects (i.e., the Discovery Object and the Key History object) within the Derived PIV Application shall be included in the Security Object. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.01.08.01 | 実装されている場合、Security Objectは、[SP800-73]第1部の表12にあるすべてのTLV要素を、列挙された順序で含まなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], 第1部, 付録A - PIV Data Model, Table 12 |
| DTR-07.01.08.02 | Security Objectは、Discovery ObjectまたはKey History Objectのいずれかが存在する場合に派生PIVアプリケーション内に存在しなければならず、それ以外の場合は存在してはなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.01.08.03 | 派生PIVアプリケーション内のすべての署名なしデータオブジェクト(すなわちDiscovery ObjectおよびKey History Object)は、Security Objectに含めなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements |
7.2 Signed Data Object Conformance
7.2 署名付きデータオブジェクトの適合性
7.2.1 Security Object
7.2.1 Security Object
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.02.01.01 | The message digests produced as a result of a hash function on the contents of a Discovery Object and/or the Key History Object, if implemented, shall be identical to that data object’s message digest contained in the Security Object. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], Part 1, Section 3.1.7 – Security Object |
| DTR-07.02.01.02 | The Security Object shall contain an asymmetric digital signature as specified in Request for Comments (RFC) 5652, Cryptographic Message Syntax [RFC5652]. | • [SP800-73], Part 1, Section 3.1.7 – Security Object |
| DTR-07.02.01.03 | The digital signature is implemented as a SignedData Type. | • [SP800-73], Part 1, Section 3.1.7 – Security Object |
| DTR-07.02.01.04 | The value of the version field of the SignedData content type shall be v3. | • [SP800-73], Part 1, Section 3.1.7 – Security Object |
| DTR-07.02.01.05 | The digestAlgorithms field of the SignedData content type shall be in accordance with Table 3-2 of [SP800-78]. | • [SP800-73], Part 1, Section 3.1.7 – Security Object |
| DTR-07.02.01.06 | The eContentType of the encapContentInfo shall be id-icao-ldsSecurityObject (OID = 1.3.27.1.1.1). | • [SP800-73], Part 1, Section 3.1.7 – Security Object |
| DTR-07.02.01.07 | The eContent of the encapContentsInfo field shall contain the encoded contents of the ldsSecurity object. | • [SP800-73], Part 1, Section 3.1.7 – Security Object |
| DTR-07.02.01.08 | The signature field of the Security Object, tag 0xBB, shall include the Derived PIV Credential Issuer’s (content signing) certificate. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.02.01.09 | The digestAlgorithm field specified in the SignerInfo field is in accordance with Table 3-2 of [SP800-78]. | • [SP800-73], Part 1, Section 3.1.7 – Security Object |
| DTR-07.02.01.10 | The signatureAlgorithm field in the SignerInfo field is specified as follows: for RSA with | • [SP800-73], Part 1, Section 3.1.7 – |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.02.01.01 | 実装されている場合、Discovery Objectおよび/またはKey History Objectの内容にハッシュ関数を適用して生成したメッセージダイジェストは、Security Objectに含まれるそのデータオブジェクトのメッセージダイジェストと同一でなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [SP800-73], 第1部, 第3.1.7節 – Security Object |
| DTR-07.02.01.02 | Security Objectは、Request for Comments(RFC)5652, Cryptographic Message Syntax [RFC5652] に規定された非対称デジタル署名を含まなければなりません。 | • [SP800-73], 第1部, 第3.1.7節 – Security Object |
| DTR-07.02.01.03 | デジタル署名は、SignedData型として実装されます。 | • [SP800-73], 第1部, 第3.1.7節 – Security Object |
| DTR-07.02.01.04 | SignedDataコンテンツタイプのversionフィールドの値は v3 でなければなりません。 | • [SP800-73], 第1部, 第3.1.7節 – Security Object |
| DTR-07.02.01.05 | SignedDataコンテンツタイプのdigestAlgorithmsフィールドは、[SP800-78]の表3-2に従わなければなりません。 | • [SP800-73], 第1部, 第3.1.7節 – Security Object |
| DTR-07.02.01.06 | encapContentInfoのeContentTypeは id-icao-ldsSecurityObject(OID = 1.3.27.1.1.1)でなければなりません。 | • [SP800-73], 第1部, 第3.1.7節 – Security Object |
| DTR-07.02.01.07 | encapContentsInfoフィールドのeContentは、ldsSecurityオブジェクトのエンコードされた内容を含まなければなりません。 | • [SP800-73], 第1部, 第3.1.7節 – Security Object |
| DTR-07.02.01.08 | Security Objectのsignatureフィールド(タグ 0xBB)は、Derived PIV Credential Issuerの(コンテンツ署名用)証明書を含まなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.02.01.09 | SignerInfoフィールドで指定されるdigestAlgorithmフィールドは、[SP800-78]の表3-2に従います。 | • [SP800-73], 第1部, 第3.1.7節 – Security Object |
| DTR-07.02.01.10 | SignerInfoフィールドのsignatureAlgorithmフィールドは次のように指定されます。RSAの場合、 | • [SP800-73], 第1部, 第3.1.7節 – |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| PKCS #1 v1.5 padding, the signatureAlgorithm field shall specify the rsaEncryption OID (as per Section 3.2 of [RFC3370]), and for ECDSA and RSA with PSS padding, the signatureAlgorithm shall be in accordance with Table 3-3 of [SP800-78]. | Security Object | |
| DTR-07.02.01.11 | The SignedData content type shall include the digital signature. | • [SP800-73], Part 1, Section 3.1.7 – Security Object |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| PKCS #1 v1 | Security Object | |
| DTR-07.02.01.11 | SignedDataコンテンツタイプは、デジタル署名を含まなければなりません。 | • [SP800-73], 第1部, 第3.1.7節 – Security Object |
7.3 PKI Conformance
7.3 PKI適合性
7.3.1 X.509 Certificate for Derived PIV Authentication
7.3.1 派生PIV認証用X.509証明書
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.01.01 | The signature field in the certificate shall specify an algorithm from Table 3-3 of [SP800-78] in the AlgorithmIdentifier field. | • [SP800-78], Section 3.2.1 - Specification of Digital Signatures on Authentication Information |
| DTR-07.03.01.02 | If RSA with PSS padding is used, the parameters field of the AlgorithmIdentifier type shall assert SHA-256 (OID = 2.16.840.1.101.3.4.2.1). For RSA with PKCS #1 v1.5 padding, the parameters field is populated with NULL. For ECDSA, the parameters field is absent. | • [PROF], Worksheet titled - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.03 | The subjectPublicKeyInfo field shall assert an algorithm in the AlgorithmIdentifier in accordance with Table 3-4 of [SP800-78]. | • [SP800-78], Section 3.2.2 - Specification of Public Keys In X.509 Certificates |
| DTR-07.03.01.04 | If the public key algorithm is elliptic curve, then the parameters field contains the namedCurve choice populated with the OID for Curve P-256 (1.2.840.10045.3.1.7). | • [PROF], Worksheet titled - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.05 | The keyUsage extension shall assert only the digitalSignature bit. No other bits shall be asserted. | • [PROF], Worksheet titled - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.06 | The policyIdentifier field in the certificatePolicies must assert id-fpki- | • [PROF], Worksheet titled - Derived PIV |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.01.01 | 証明書のsignatureフィールドは、AlgorithmIdentifierフィールドに[SP800-78]の表3-3のアルゴリズムを指定しなければなりません。 | • [SP800-78], 第3.2.1節 - Specification of Digital Signatures on Authentication Information |
| DTR-07.03.01.02 | RSA(PSSパディング)を使用する場合、AlgorithmIdentifier型のparametersフィールドはSHA-256(OID = 2 | • [PROF], ワークシート題名 - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.03 | subjectPublicKeyInfoフィールドは、AlgorithmIdentifierに[SP800-78]の表3-4に従ったアルゴリズムを表明しなければなりません。 | • [SP800-78], 第3.2.2節 - Specification of Public Keys In X.509 Certificates |
| DTR-07.03.01.04 | 公開鍵アルゴリズムが楕円曲線の場合、parametersフィールドには、Curve P-256のOID(1 | • [PROF], ワークシート題名 - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.05 | keyUsage拡張は、digitalSignatureビットのみを表明しなければなりません。他のビットを表明してはなりません。 | • [PROF], ワークシート題名 - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.06 | certificatePoliciesのpolicyIdentifierフィールドは、id-fpki- | • [PROF], ワークシート題名 - Derived PIV |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| common-derived-pivAuth (OID = 2 | Authentication Certificate Profile | |
| DTR-07.03.01.07 | The subjectAltName extension shall include a UUID encoded as a URN, as specified in Section 3 of [RFC4122], A Universally Unique IDentifier (UUID) URN Namespace. | • [PROF], Worksheet titled - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.08 | The piv-interim extension (OID = 2.16.840.1.101.3.6.9.1) shall be present and contain an interim_indicator field, which is populated with a Boolean value. This extension is not critical. | • [PROF], Worksheet titled - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.09 | The authorityInfoAccess field shall contain an id-ad-ocsp accessMethod. The access location uses the Uniform Resource Identifier (URI) name form to specify the location of a Hypertext Transfer Protocol (HTTP) accessible Online Certificate Status Protocol (OCSP) server distributing status information for this certificate. | • [PROF], Worksheet titled - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.10 | The cRLDistributionPoints extension is required and must contain an HTTP URI. The URI must point to a file that has an extension of ".crl" that contains the DER encoded CRL that provides status information about the certificate. (see [RFC2585], Internet X.509 Public Key Infrastructure Operational Protocols: FTP and HTTP) | • [PROF], Worksheet titled - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.11 | The authorityInfoAccess field shall contain an id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod. The access location shall specify the location to an HTTP accessible Web server where certificates issued to the issuer of this certificate may be found. The URI must point to a file that has an extension of ".p7c" containing a certs-only CMS message (see [RFC5751], Secure/Multipurpose Internet Mail Extensions (S/MIME) Version 3.2 Message Specification). | • [PROF], Worksheet titled - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.12 | The size of the public key for the Derived PIV Authentication certificate shall be in accordance with Table 3-1 of [SP800-78]. | • [SP800-78], Section 3.1 - PIV Cryptographic Keys |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| common-derived-pivAuth(OID = 2 | Authentication Certificate Profile | |
| DTR-07.03.01.07 | subjectAltName拡張は、[RFC4122], A Universally Unique IDentifier (UUID) URN Namespace の第3節に規定されたとおり、URNとしてエンコードしたUUIDを含まなければなりません。 | • [PROF], ワークシート題名 - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.08 | piv-interim拡張(OID = 2 | • [PROF], ワークシート題名 - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.09 | authorityInfoAccessフィールドは、id-ad-ocsp accessMethodを含まなければなりません。アクセス場所は、この証明書のステータス情報を配布する、Hypertext Transfer Protocol(HTTP)でアクセス可能なOnline Certificate Status Protocol(OCSP)サーバーの場所を指定するために、Uniform Resource Identifier(URI)名形式を使用します。 | • [PROF], ワークシート題名 - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.10 | cRLDistributionPoints拡張は必須であり、HTTP URIを含まなければなりません。URIは、この証明書に関するステータス情報を提供する、DERエンコードされたCRLを含む拡張子 ".crl" のファイルを指していなければなりません。([RFC2585], Internet X.509 Public Key Infrastructure Operational Protocols: FTP and HTTP を参照) | • [PROF], ワークシート題名 - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.11 | authorityInfoAccessフィールドは、id-ad-caIssuers(1 | • [PROF], ワークシート題名 - Derived PIV Authentication Certificate Profile |
| DTR-07.03.01.12 | Derived PIV Authentication certificateの公開鍵のサイズは、[SP800-78]の表3-1に従わなければなりません。 | • [SP800-78], 第3.1節 - PIV Cryptographic Keys |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.01.13 | The public key present in the Derived PIV Authentication certificate shall correspond to the Derived PIV Authentication private key. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.03.01.14 | If the public key algorithm is RSA, the exponent shall be equal to 65 537. | • [SP800-78], Section 3.1, PIV Cryptographic Keys |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.01.13 | Derived PIV Authentication certificateに含まれる公開鍵は、認証用秘密鍵に対応していなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.03.01.14 | 公開鍵アルゴリズムがRSAの場合、指数は65 537に等しくなければなりません。 | • [SP800-78], 第3.1節, PIV Cryptographic Keys |
7.3.2 X.509 Certificate for Digital Signature
7.3.2 デジタル署名用X.509証明書
[SP800-157] does not specify any requirements on the digital signature key and certificate. The requirements listed herein follow those specified in [FIPS201] for digital signature certificates that are not issued by legacy PKIs,8 and thus do not actually apply to the X.509 Certificate for Digital Signature stored within a Derived PIV Application, with the exception that certificates that assert the id-fpki-common-policy, id-fpki-common-hardware, or id-fpki-common-High certificate policy OID are required by the corresponding certificate policy to conform to [PROF].
[SP800-157]は、デジタル署名鍵および証明書の要件を規定していません。ここに示す要件は、従来型PKIから発行されないデジタル署名証明書について[FIPS201]が定める要件に従うものであり8、したがって派生PIVアプリケーション内に格納されたデジタル署名用X.509証明書には実際には適用されません。ただし、証明書ポリシーOIDとしてid-fpki-common-policy、id-fpki-common-hardware、またはid-fpki-common-Highを指定する証明書は、対応する証明書ポリシーにより[PROF]への適合が求められます。
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.02.01 | The signature field in the certificate shall specify an algorithm from Table 3-3 of [SP800-78] in the AlgorithmIdentifier. | • [SP800-78], Section 3.2.1 - Specification of Digital Signatures on Authentication Information |
| DTR-07.03.02.02 | If RSA with PSS padding is used, the parameters field of the AlgorithmIdentifier type shall assert SHA-256 (OID = 2.16.840.1.101.3.4.2.1). For RSA with PKCS #1 v1.5 padding, the parameters field is populated with NULL. For ECDSA, the parameters field is absent. | • [PROF], Worksheet titled - End Entity Signature Certificate Profile |
| DTR-07.03.02.03 | The subjectPublicKeyInfo field shall assert an algorithm in the AlgorithmIdentifier in accordance with Table 3-4 of [SP800-78]. | • [SP800-78], Section 3.2.2 - Specification of Public Keys In X.509 Certificates |
| DTR-07.03.02.04 | If the public key algorithm is elliptic curve, then the parameters field contains the namedCurve choice populated an appropriate OID from [SP800-78]. | • [PROF], Worksheet titled - End Entity Signature Certificate Profile |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.02.01 | 証明書のsignatureフィールドは、AlgorithmIdentifierに[SP800-78]の表3-3のアルゴリズムを指定しなければなりません。 | • [SP800-78], 第3.2.1節 - Specification of Digital Signatures on Authentication Information |
| DTR-07.03.02.02 | RSA(PSSパディング)を使用する場合、AlgorithmIdentifier型のparametersフィールドはSHA-256(OID = 2 | • [PROF], ワークシート題名 - End Entity Signature Certificate Profile |
| DTR-07.03.02.03 | subjectPublicKeyInfoフィールドは、AlgorithmIdentifierに[SP800-78]の表3-4に従ったアルゴリズムを表明しなければなりません。 | • [SP800-78], 第3.2.2節 - Specification of Public Keys In X.509 Certificates |
| DTR-07.03.02.04 | 公開鍵アルゴリズムが楕円曲線の場合、parametersフィールドには、[SP800-78]の適切なOIDを設定したnamedCurve選択肢が含まれます。 | • [PROF], ワークシート題名 - End Entity Signature Certificate Profile |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.02.05 | The keyUsage extension shall assert both the digitalSignature and nonRepudiation bits. No other bits shall be asserted. | • [PROF], Worksheet titled - End Entity Signature Certificate Profile |
| DTR-07.03.02.06 | The policyIdentifier field in the certificatePolicies must assert one of the following: id-fpki-common-policy (OID = 2 | • [PROF], Worksheet titled - End Entity Signature Certificate Profile |
| DTR-07.03.02.07 | The authorityInfoAccess field shall contain an id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod. The access location shall to specify the location of an LDAP accessible directory server or HTTP accessible Web server where certificates issued to the issuer of this certificate may be found. If LDAP is used, the URI must include the DN of the entry containing the relevant certificates and specify the directory attribute in which the certificates are located. If the directory in which the certificates are stored expects the "binary" option to be specified, then the attribute type must be followed by ";binary" in the URI. If HTTP is used, the URI must point to a file that has an extension of ".p7c" containing a certs-only CMS message (see RFC 5751, Secure/Multipurpose Internet Mail Extensions (S/MIME) Version 3.2 Message Specification [RFC5751]). | • [PROF], Worksheet titled - End Entity Signature Certificate Profile |
| DTR-07.03.02.08 | The cRLDistributionPoints extension is required and must contain at least one URI, either LDAP or HTTP. If LDAP is used, the URI must include the DN of the entry containing the CRL and specify the directory attribute in which the CRL is located (certificateRevocationList) | • [PROF], Worksheet titled - End Entity Signature Certificate Profile |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.02.05 | keyUsage拡張は、digitalSignatureビットとnonRepudiationビットの両方を表明しなければなりません。他のビットを表明してはなりません。 | • [PROF], ワークシート題名 - End Entity Signature Certificate Profile |
| DTR-07.03.02.06 | certificatePoliciesのpolicyIdentifierフィールドは、次のいずれかを表明しなければならない:id-fpki-common-policy(OID = 2 | • [PROF], ワークシート題名 - End Entity Signature Certificate Profile |
| DTR-07.03.02.07 | authorityInfoAccessフィールドは、id-ad-caIssuers(1 | • [PROF], ワークシート題名 - End Entity Signature Certificate Profile |
| DTR-07.03.02.08 | cRLDistributionPoints拡張は必須であり、LDAPまたはHTTPのいずれかのURIを少なくとも1つ含まなければなりません。LDAPを使用する場合、URIは、CRLを含むエントリのDNを含み、CRLが格納されているディレクトリ属性(certificateRevocationList)を指定しなければなりません。HTTPを使用する場合、URIは、DERエンコードされたCRLを含む拡張子 ".crl" のファイルを指していなければなりません。([RFC2585], Internet X.509 Public Key Infrastructure Operational Protocols: FTP and HTTP を参照) | • [PROF], ワークシート題名 - End Entity Signature Certificate Profile |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.02.09 | The size of the public key for the digital signature certificate shall be in accordance with Table 3-1 of [SP800-78]. | • [SP800-78], Section 3.1 - PIV Cryptographic Keys |
| DTR-07.03.02.10 | The public key present in the digital signature certificate shall correspond to the digital signature private key. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.03.02.11 | If the public key algorithm is RSA, the exponent shall be equal to 65 537. | • [SP800-78], Section 3.1, PIV Cryptographic Keys |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.02.09 | デジタル署名証明書の公開鍵のサイズは、[SP800-78]の表3-1に従わなければなりません。 | • [SP800-78], 第3.1節 - PIV Cryptographic Keys |
| DTR-07.03.02.10 | デジタル署名証明書に含まれる公開鍵は、デジタル署名用秘密鍵に対応していなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.03.02.11 | 公開鍵アルゴリズムがRSAの場合、指数は65 537に等しくなければなりません。 | • [SP800-78], 第3.1節, PIV Cryptographic Keys |
7.3.3 X.509 Certificate for Key Management
7.3.3 鍵管理用X.509証明書
[SP800-157] does not specify requirements on the key management key and certificate. The requirements listed herein follow those from [FIPS201] for key management certificates that are not issued by legacy PKIs, and thus do not actually apply to the X.509 Certificate for Key Management stored within a Derived PIV Application, with the exception that certificates that assert the id-fpki-common-policy, id-fpki-common-hardware, or id-fpki-common-High certificate policy OID are required by the corresponding certificate policy to conform to [PROF].
[SP800-157]は、鍵管理鍵および証明書の要件を規定していません。ここに示す要件は、従来型PKIから発行されない鍵管理証明書について[FIPS201]が定める要件に従うものであり、したがってDerived PIV Application内に格納された鍵管理用X.509証明書には実際には適用されません。ただし、証明書ポリシーOIDとしてid-fpki-common-policy、id-fpki-common-hardware、またはid-fpki-common-Highを指定する証明書は、対応する証明書ポリシーにより[PROF]への適合が求められます。
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.03.01 | The signature field in the certificate shall specify an algorithm from Table 3-3 of [SP800-78] in the AlgorithmIdentifier. | • [SP800-78], Section 3.2.1 - Specification of Digital Signatures on Authentication Information |
| DTR-07.03.03.02 | If RSA with PSS padding is used, the parameters field of the AlgorithmIdentifier type shall assert Secure Hash Algorithm (SHA) 256 (OID = 2.16.840.1.101.3.4.2.1). For the other RSA algorithms, the parameters field is populated with NULL. For ECDSA, the parameters field is absent. | • [PROF], Worksheet titled - Key Management Certificate Profile |
| DTR-07.03.03.03 | The subjectPublicKeyInfo field shall assert an algorithm in the AlgorithmIdentifier in accordance with Table 3-4 of [SP800-78]. | • [SP800-78], Section 3.2.2 - Specification of Public Keys In X.509 Certificates |
| DTR-07.03.03.04 | If the public key algorithm is elliptic curve, then the parameters field contains the namedCurve choice populated with an appropriate OID from [SP800-78]. | • [PROF], Worksheet titled - Key Management Certificate Profile |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.03.01 | 証明書のsignatureフィールドは、AlgorithmIdentifierに[SP800-78]の表3-3のアルゴリズムを指定しなければなりません。 | • [SP800-78], 第3.2.1節 - Specification of Digital Signatures on Authentication Information |
| DTR-07.03.03.02 | RSA(PSSパディング)を使用する場合、AlgorithmIdentifier型のparametersフィールドはSecure Hash Algorithm(SHA)256(OID = 2 | • [PROF], ワークシート題名 - Key Management Certificate Profile |
| DTR-07.03.03.03 | subjectPublicKeyInfoフィールドは、AlgorithmIdentifierに[SP800-78]の表3-4に従ったアルゴリズムを表明しなければなりません。 | • [SP800-78], 第3.2.2節 - Specification of Public Keys In X.509 Certificates |
| DTR-07.03.03.04 | 公開鍵アルゴリズムが楕円曲線の場合、parametersフィールドには、[SP800-78]の適切なOIDを設定したnamedCurve選択肢が含まれます。 | • [PROF], ワークシート題名 - Key Management Certificate Profile |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.03.05 | If the public key algorithm is RSA, then the keyUsage extension shall only assert the keyEncipherment bit. If the public key algorithm is elliptic curve, then the keyUsage extension shall only assert the keyAgreement bit. | • [PROF], Worksheet titled - Key Management Certificate Profile |
| DTR-07.03.03.06 | The policyIdentifier field in the certificatePolicies must assert one of the following: id-fpki-common-policy (OID = 2 | • [PROF], Worksheet titled - Key Management Certificate Profile |
| DTR-07.03.03.07 | The authorityInfoAccess field shall contain an id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod. The access location shall to specify the location of an LDAP accessible directory server or HTTP accessible Web server where certificates issued to the issuer of this certificate may be found. If LDAP is used, the URI must include the DN of the entry containing the relevant certificates and specify the directory attribute in which the certificates are located. If the directory in which the certificates are stored expects the "binary" option to be specified, then the attribute type must be followed by ";binary" in the URI. If HTTP is used, the URI must point to a file that has an extension of ".p7c" containing a certs-only CMS message (see [RFC5751], Secure/Multipurpose Internet Mail Extensions (S/MIME) Version 3.2 Message Specification). | • [PROF], Worksheet titled - Key Management Certificate Profile |
| DTR-07.03.03.08 | The cRLDistributionPoints extension is required and must contain at least one URI, either LDAP or HTTP. If LDAP is used, the URI must include the DN of the entry containing the CRL and specify the directory attribute in which the CRL is located (certificateRevocationList) | • [PROF], Worksheet titled - Key Management Certificate Profile |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.03.05 | 公開鍵アルゴリズムがRSAの場合、keyUsage拡張はkeyEnciphermentビットのみを表明しなければなりません。公開鍵アルゴリズムが楕円曲線の場合、keyUsage拡張はkeyAgreementビットのみを表明しなければなりません。 | • [PROF], ワークシート題名 - Key Management Certificate Profile |
| DTR-07.03.03.06 | certificatePoliciesのpolicyIdentifierフィールドは、次のいずれかを表明しなければならない:id-fpki-common-policy(OID = 2 | • [PROF], ワークシート題名 - Key Management Certificate Profile |
| DTR-07.03.03.07 | authorityInfoAccessフィールドは、id-ad-caIssuers(1 | • [PROF], ワークシート題名 - Key Management Certificate Profile |
| DTR-07.03.03.08 | cRLDistributionPoints拡張は必須であり、LDAPまたはHTTPのいずれかのURIを少なくとも1つ含まなければなりません。LDAPを使用する場合、URIは、CRLを含むエントリのDNを含み、CRLが格納されているディレクトリ属性(certificateRevocationList)を指定しなければなりません。HTTPを使用する場合、URIは、DERエンコードされたCRLを含む拡張子 ".crl" のファイルを指していなければなりません。([RFC2585], Internet X.509 Public Key Infrastructure Operational Protocols: FTP and HTTP を参照) | • [PROF], ワークシート題名 - Key Management Certificate Profile |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.03.09 | The size of the public key for the key management certificate shall be in accordance with Table 3-1 of [SP800-78]. | • [SP800-78], Section 3.1 - PIV Cryptographic Keys |
| DTR-07.03.03.10 | The public key present in the key management certificate shall correspond to the key management private key. | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.03.03.11 | If the public key algorithm is RSA, the exponent shall be equal to 65 537. | • [SP800-78], Section 3.1, PIV Cryptographic Keys |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.03.09 | 鍵管理証明書の公開鍵のサイズは、[SP800-78]の表3-1に従わなければなりません。 | • [SP800-78], 第3.1節 - PIV Cryptographic Keys |
| DTR-07.03.03.10 | 鍵管理証明書に含まれる公開鍵は、鍵管理用秘密鍵に対応していなければなりません。 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements |
| DTR-07.03.03.11 | 公開鍵アルゴリズムがRSAの場合、指数は65 537に等しくなければなりません。 | • [SP800-78], 第3.1節, PIV Cryptographic Keys |
7.3.4 X.509 Certificate for the Derived PIV Credential Issuer (Content Signing)9
7.3.4 派生PIV資格情報発行者(コンテンツ署名)用X.509証明書9
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.04.01 | The signature field in the certificate shall specify one of the following algorithm OIDs: 1.2.840.113549.1.10 (id-RSASSA-PSS), 1.2.840.113549.1.11 (Sha256WithRSAEncryption), 1.2.840.10045.4.3.2 (edsa-with-Sha256), or 1.2.840.10045.4.3.3 (edsa-with-Sha384). | • [PROF], Worksheet titled - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.02 | If RSA with PSS padding is used, the parameters field of the AlgorithmIdentifier type shall assert SHA-256 (OID = 2.16.840.1.101.3.4.2.1). For RSA with PKCS #1 v1.5 padding, the parameters field is populated with NULL. For ECDSA, the parameters field is absent. | • [PROF], Worksheet titled - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.03 | The subjectPublicKeyInfo field shall assert one of the following algorithm OIDs: 1.2.840.113549.1.1.1 (RSA Encryption) or 1.2.840.10045.2.1 (Elliptic curve key). | • [PROF], Worksheet titled - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.04 | If the public key algorithm is elliptic curve, then the parameters field contains the namedCurve choice populated with one of the following OIDs: 1.2.840.10045.3.1.7 (Curve P-256) or 1.3.132.0.34 (Curve P-384). | • [PROF], Worksheet titled - Common PIV Content Signing Certificate Profile |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.04.01 | 証明書のsignatureフィールドは、次のアルゴリズムOIDのいずれかを指定しなければならない:1 | • [PROF], ワークシート題名 - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.02 | RSA(PSSパディング)を使用する場合、AlgorithmIdentifier型のparametersフィールドはSHA-256(OID = 2 | • [PROF], ワークシート題名 - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.03 | subjectPublicKeyInfoフィールドは、次のアルゴリズムOIDのいずれかを表明しなければならない:1 | • [PROF], ワークシート題名 - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.04 | 公開鍵アルゴリズムが楕円曲線の場合、parametersフィールドには、次のOIDのいずれかを設定したnamedCurve選択肢が含まれる:1 | • [PROF], ワークシート題名 - Common PIV Content Signing Certificate Profile |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| DTR-07.03.04.05 | The keyUsage extension shall assert the digitalSignature bit. No other bits shall be asserted. | • [PROF], Worksheet titled - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.06 | The policyIdentifier field in the certificatePolicies must assert the following: id-fpki-common-contentSigning (2 | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [FIPS201], Section 4.2.1, Cardholder Unique Identifier (CHUID) |
| DTR-07.03.04.07 | The extended key usage (extKeyUsage) extension shall assert the id-PIV-content-signing (OID = 2.16.840.1.101.3.6.7). | • [SP800-157], Appendix B.1.2 - Derived PIV Application Data Model Elements • [FIPS201], Section 4.2.1, Cardholder Unique Identifier (CHUID) |
| DTR-07.03.04.08 | Certificates must include an authorityInfoAccess extension with at least one instance of the caIssuers access method (1.3.6.1.5.5.7.48.2) that specifies an HTTP URI that points to a location where certificates issued to the issuer of this certificate may be found. The HTTP URI must point to a file that has an extension of ".p7c" containing a certs-only CMS message (see RFC 5751, Secure/Multipurpose Internet Mail Extensions (S/MIME) Version 3.2 Message Specification [RFC5751]). | • [PROF], Worksheet titled - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.09 | The cRLDistributionPoints extension is required and must contain at least URI, either LDAP or HTTP. If LDAP is used, the URI must include the DN of the entry containing the CRL and specify the directory attribute in which the CRL is located certificateRevocationList) | • [PROF], Worksheet titled - Common PIV Content Signing Certificate Profile |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| DTR-07.03.04.05 | keyUsage拡張は、digitalSignatureビットを表明しなければなりません。他のビットを表明してはなりません。 | • [PROF], ワークシート題名 - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.06 | certificatePoliciesのpolicyIdentifierフィールドは、次を表明しなければならない:id-fpki-common-contentSigning(2 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [FIPS201], 第4.2.1節, Cardholder Unique Identifier (CHUID) |
| DTR-07.03.04.07 | 拡張鍵用途(extKeyUsage)拡張は、id-PIV-content-signing(OID = 2 | • [SP800-157], 付録B.1.2 - Derived PIV Application Data Model Elements • [FIPS201], 第4.2.1節, Cardholder Unique Identifier (CHUID) |
| DTR-07.03.04.08 | 証明書は、caIssuersアクセスメソッド(1 | • [PROF], ワークシート題名 - Common PIV Content Signing Certificate Profile |
| DTR-07.03.04.09 | cRLDistributionPoints拡張は必須であり、URIを少なくとも1つ含まなければなりません。URIはLDAPまたはHTTPのいずれかでなければなりません。LDAPを使用する場合、URIは、CRLを含むエントリのDNを含み、CRLが格納されているディレクトリ属性(certificateRevocationList)を指定しなければなりません。 | • [PROF], ワークシート題名 - Common PIV Content Signing Certificate Profile |
| DTR No: | DTR Description | Spec. Reference |
|---|---|---|
| If HTTP is used, the URI must point to a file that has an extension of ".crl" that contains the DER encoded CRL. (see [RFC2585], Internet X.509 Public Key Infrastructure Operational Protocols: FTP and HTTP) | ||
| DTR-07.03.04.10 | The size of the subject public key in the Derived PIV Credential Issuer’s (content signing) certificate shall conform to Table 3-2 in [SP800-78]. | • [SP800-78], Section 3.2.1 – Specification of Digital Signatures on Authentication Information |
| DTR番号: | DTR説明 | 仕様の参照先 |
|---|---|---|
| HTTPを使用する場合、URIは、DERエンコードされたCRLを含む拡張子 ".crl" のファイルを指していなければなりません。([RFC2585], Internet X.509 Public Key Infrastructure Operational Protocols: FTP and HTTP を参照) | ||
| DTR-07.03.04.10 | Derived PIV Credential Issuerの(コンテンツ署名用)証明書内のサブジェクト公開鍵のサイズは、[SP800-78]の表3-2に適合しなければなりません。 | • [SP800-78], 第3.2.1節 – Specification of Digital Signatures on Authentication Information |
8. Test Assertions for the Derived PIV Application
8. 派生PIVアプリケーションの試験アサーション
This section lists the test assertions used to determine conformity to the derived test requirements (DTR) listed in Section 6. The Implementation Under Test (IUT), in this case a Derived PIV Application submitted by a vendor, must meet the stated objective(s) of the assertion by way of a test or submission of documents/artifacts in order to be deemed conformant to the associated DTR(s).
この節では、第6節に示した派生テスト要件(DTR)への適合を判定するためのテストアサーションを列挙します。ここでの被試験実装(IUT)は、ベンダーが提出したDerived PIV Applicationであり、関連するDTRへの適合と認められるには、テストまたは文書・成果物の提出によって、アサーションに記載された目的を満たさなければなりません。
8.1 Transport Layer Conformance
8.1 トランスポート層の適合性
8.1.1 UICC
8.1.1 UICC
8.1.1.1 GlobalPlatform Support for UICC Tokens
8.1.1.1 UICCトークンのGlobalPlatformサポート
| Test Assertion | TA-08.01.01.01 |
|---|---|
| Purpose | Confirms that for Universal Integrated Circuit Card (UICC) implementations used to host a Derived PIV Application, the UICC implements the GlobalPlatform Card Secure Element Configuration v1.0 [GPSE]. |
| DTR(s) | • DTR-06.01.01.01 |
| Vendor Documentation | The vendor to provide evidence in its documentation that the UICC that hosts the Derived PIV Application implements the GlobalPlatform Card Secure Element Configuration v1.0 [GPSE]. |
| テストアサーション | TA-08.01.01.01 |
|---|---|
| 目的 | 汎用集積回路カード(UICC)を 派生PIVアプリケーション のホストに使用する実装について、UICCが GlobalPlatform Card Secure Element Configuration v1.0 [GPSE] を実装していることを確認します。 |
| DTR | • DTR-06.01.01.01 |
| ベンダー文書 | ベンダーは、派生PIVアプリケーションをホストするUICCが GlobalPlatform Card Secure Element Configuration v1.0 [GPSE] を実装していることを示す証拠を、文書で提供します。 |
8.1.2 USB
8.1.2 USB
8.1.2.1 ICCD Specification Support for USB Tokens
8.1.2.1 USBトークンのICCD仕様サポート
| Test Assertion | TA-08.01.02.01 |
|---|---|
| Purpose | Confirms that for USB Integrated Circuit(s) Card Devices (ICCD) implementations used to host a Derived PIV Application, the ICCD uses the Bulk-in/Bulk-Out command pipe for APDU transport and implements the Universal Serial Bus Device Class - Smart Card ICCD Specification for USB Integrated Circuit(s) Card Devices [ICCDSPEC]. |
| DTR(s) | • DTR-06.01.02.01 • DTR-06.01.02.03 |
| Vendor Documentation | The vendor to provide evidence in its documentation that the ICCD that hosts the Derived PIV Application implements the Universal Serial Bus Device Class - Smart Card ICCD Specification for USB Integrated Circuit(s) Card Devices [ICCDSPEC]. The vendor confirms that the APDUs are received from the secure element using the Bulk-In command pipe. |
| テストアサーション | TA-08.01.02.01 |
|---|---|
| 目的 | USB Integrated Circuit(s) Card Device(ICCD)を 派生PIVアプリケーション のホストに使用する実装について、ICCDがAPDU転送にBulk-in/ |
| DTR | • DTR-06.01.02.01 • DTR-06.01.02.03 |
| ベンダー文書 | ベンダーは、派生PIVアプリケーションをホストするICCDが Universal Serial Bus Device Class - Smart Card ICCD Specification for USB Integrated Circuit(s) Card Devices [ICCDSPEC] を実装していることを示す証拠を、文書で提供します。ベンダーは、APDUがBulk-Inコマンドパイプを用いてセキュアエレメントから受信されることを確認します。 |
8.1.2.2 SP 800-96 Support for USB Tokens
8.1.2.2 USBトークンのSP 800-96サポート
| Test Assertion | TA-08.01.02.02 |
|---|---|
| Purpose | For a USB token that hosts a Derived PIV Application, confirm that the token is compliant with the specifications in [SP800-96] for APDU support for contact card readers. |
| DTR(s) | • DTR-06.01.02.02 |
| Vendor Documentation | The vendor to provide evidence in its documentation that the USB token is compliant with the specifications in [SP800-96] for APDU support for contact card readers. |
| テストアサーション | TA-08.01.02.02 |
|---|---|
| 目的 | 派生PIVアプリケーションをホストするUSBトークンについて、トークンが接触式カードリーダー向けのAPDUサポートに関する[SP800-96]の仕様に準拠していることを確認します。 |
| DTR | • DTR-06.01.02.02 |
| ベンダー文書 | ベンダーは、USBトークンが接触式カードリーダー向けのAPDUサポートに関する[SP800-96]の仕様に準拠していることを示す証拠を、文書で提供します。 |
8.2 Derived PIV Application Data Object Access/Storage Conformance
8.2 派生PIVアプリケーションのデータオブジェクトのアクセス/保存の適合性
8.2.1 General
8.2.1 一般
8.2.1.1 Support for Contact Interface
8.2.1.1 接触インターフェースのサポート
| Test Assertion | TA-08.02.01.01 |
|---|---|
| Purpose | Confirms that the Derived PIV Application only supports a contact interface. |
| DTR(s) | • DTR-06.02.01.01 |
| Vendor Documentation | The vendor to provide evidence in its documentation that the Derived PIV Application only supports a contact interface. |
| テストアサーション | TA-08.02.01.01 |
|---|---|
| 目的 | 派生PIVアプリケーションが接触インターフェースのみをサポートしていることを確認します。 |
| DTR | • DTR-06.02.01.01 |
| ベンダー文書 | ベンダーは、派生PIVアプリケーションが接触インターフェースのみをサポートしていることを示す証拠を、文書で提供します。 |
8.2.1.2 One Derived PIV Application
8.2.1.2 単一のDerived PIV Application
| Test Assertion | TA-08.02.01.02 |
|---|---|
| Purpose | Confirms that there is only one Derived PIV Application on any hardware cryptographic token. |
| DTR(s) | • DTR-06.02.01.02 |
| Vendor Documentation | The vendor to provide information in its documentation validating the compliance with this requirement. |
| テストアサーション | TA-08.02.01.02 |
|---|---|
| 目的 | 任意のハードウェア暗号トークン上に派生PIVアプリケーションが1つだけ存在することを確認します。 |
| DTR | • DTR-06.02.01.02 |
| ベンダー文書 | ベンダーは、この要件への準拠を検証する情報を文書で提供します。 |
8.2.2 Derived PIV Application Data Objects and Representation
8.2.2 派生PIVアプリケーションのデータオブジェクトと表現
8.2.2.1 Derived PIV Application Data Objects
8.2.2.1 Derived PIV Applicationデータオブジェクト
| Test Assertion | TA-08.02.02.01 |
|---|---|
| Purpose | Confirms the data objects (along with their access conditions) are implemented by the vendor of the Derived PIV Application per the specification. |
| テストアサーション | TA-08.02.02.01 |
|---|---|
| 目的 | データオブジェクト(およびそのアクセス条件)が、派生PIVアプリケーションのベンダーによって仕様どおりに実装されていることを確認します。 |
| DTR(s) | • DTR-06.02.02.01 |
|---|---|
| Vendor Documentation | The vendor to provide documentation identifying all the data objects (mandatory and optional) implemented within the Derived PIV Application. |
| DTR | • DTR-06.02.02.01 |
|---|---|
| ベンダー文書 | ベンダーは、派生PIVアプリケーション内に実装されたすべてのデータオブジェクト(必須およびオプション)を特定する文書を提供します。 |
8.2.2.2 Derived PIV Data Objects Container Capacity
8.2.2.2 Derived PIVデータオブジェクトのコンテナ容量
| Test Assertion | TA-08.02.02.02 |
|---|---|
| Purpose | Confirms the container capacity for all Derived PIV data objects implemented on the Derived PIV Application. |
| DTR(s) | • DTR-06.02.02.02 • DTR-06.02.02.03 • DTR-06.02.02.04 • DTR-06.02.02.05 • DTR-06.02.02.06 • DTR-06.02.02.07 • DTR-06.02.02.08 |
| Vendor Documentation | The vendor to provide in its documentation the implemented data objects with their minimum container sizes on the Derived PIV Application. |
| テストアサーション | TA-08.02.02.02 |
|---|---|
| 目的 | 派生PIVアプリケーション上に実装されたすべての派生PIVデータオブジェクトの格納容量を確認します。 |
| DTR | • DTR-06.02.02.02 • DTR-06.02.02.03 • DTR-06.02.02.04 • DTR-06.02.02.05 • DTR-06.02.02.06 • DTR-06.02.02.07 • DTR-06.02.02.08 |
| ベンダー文書 | ベンダーは、派生PIVアプリケーション上に実装されたデータオブジェクトと、それぞれの最小コンテナサイズを文書で提供します。 |
8.2.2.3 Status Words
8.2.2.3 ステータスワード
| Test Assertion | TA-08.02.02.03 |
|---|---|
| Purpose | Confirms that all return codes are implemented by the Derived PIV Application. |
| DTR(s) | • DTR-06.02.02.09 |
| Vendor Documentation | The vendor to provide all the status codes returned by the Derived PIV Application for the various token interface commands in its documentation. The status codes are consistent with those specified in Section 5.6 of [SP800-73], Part 1. |
| テストアサーション | TA-08.02.02.03 |
|---|---|
| 目的 | すべてのリターンコードが派生PIVアプリケーションによって実装されていることを確認します。 |
| DTR | • DTR-06.02.02.09 |
| ベンダー文書 | ベンダーは、各種トークンインターフェースコマンドに対して派生PIVアプリケーションが返すすべてのステータスコードを文書で提供します。ステータスコードは、[SP800-73]第1部の第5 |
8.2.2.4 BER-TLV for the Derived PIV Data Objects
8.2.2.4 Derived PIVデータオブジェクトのBER-TLV
| Test Assertion | TA-08.02.02.04 |
|---|---|
| Purpose | Confirms the BER-TLV tags for the data objects implemented within the Derived PIV Application. |
| DTR(s) | • DTR-06.02.02.10 |
| Vendor Documentation | The vendor to provide in its documentation the list of all the data objects implemented in the Derived PIV Application with the BER-TLV tags associated with each of them. |
| テストアサーション | TA-08.02.02.04 |
|---|---|
| 目的 | 派生PIVアプリケーション内に実装されたデータオブジェクトのBER-TLVタグを確認します。 |
| DTR | • DTR-06.02.02.10 |
| ベンダー文書 | ベンダーは、派生PIVアプリケーション内に実装されたすべてのデータオブジェクトの一覧を、それぞれに関連付けられたBER-TLVタグとともに文書で提供します。 |
8.2.2.5 Key Reference Values
8.2.2.5 鍵参照値
| Test Assertion | TA-08.02.02.05 |
|---|---|
| Purpose | Confirms that all the key references used on the Derived PIV Application interfaces are in accordance with Table 6-1 of [SP800-78] and Table 4a of [SP800-73], Part 1, with the mappings defined in Table B-2 of [SP800-157]. |
| DTR(s) | • DTR-06.02.02.11 |
| Vendor Documentation | The vendor to provide in its documentation the key references implemented by the Derived PIV Application. |
| テストアサーション | TA-08.02.02.05 |
|---|---|
| 目的 | 派生PIVアプリケーションのインターフェースで使用されるすべての鍵参照が、[SP800-78]の表6-1および[SP800-73]第1部の表4aに従い、[SP800-157]の表B-2で定義された対応付けを用いていることを確認します。 |
| DTR | • DTR-06.02.02.11 |
| ベンダー文書 | ベンダーは、派生PIVアプリケーションが実装する鍵参照を文書で提供します。 |
8.2.2.6 Algorithm Identifiers
8.2.2.6 アルゴリズム識別子
| Test Assertion | TA-08.02.02.06 |
|---|---|
| Purpose | Confirms that the required cryptographic algorithms and their identifiers are implemented by the Derived PIV Application. |
| DTR(s) | • DTR-06.02.02.12 |
| Vendor Documentation | The vendor to provide in its documentation the cryptographic algorithms and their identifiers supported by the Derived PIV Application. |
| テストアサーション | TA-08.02.02.06 |
|---|---|
| 目的 | 必要な暗号アルゴリズムとその識別子が派生PIVアプリケーションによって実装されていることを確認します。 |
| DTR | • DTR-06.02.02.12 |
| ベンダー文書 | ベンダーは、派生PIVアプリケーションがサポートする暗号アルゴリズムとその識別子を文書で提供します。 |
8.3 Derived PIV Application Command Interface Conformance
8.3 派生PIVアプリケーションのコマンドインターフェース適合性
8.3.1 SELECT Command
8.3.1 SELECTコマンド
8.3.1.1 Select using the Full and Truncated AID
8.3.1.1 完全なAIDおよび短縮AIDによる選択
| Test Assertion | TA-08.03.01.01 |
|---|---|
| Purpose | Verifies that the Derived PIV Application executes the SELECT token command for the following conditions: (i) long AID and (ii) right-truncated short AID. The application property template as specified by the vendor is returned. |
| DTR(s) | • DTR-06.02.01.03 • DTR-06.02.02.09 • DTR-06.03.02.01 • DTR-06.03.02.03 • DTR-06.03.02.04 • DTR-06.03.02.05 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. |
| テストアサーション | TA-08.03.01.01 |
|---|---|
| 目的 | 派生PIVアプリケーションが、(i) 長いAIDおよび (ii) 右側を切り詰めた短いAIDの条件で、SELECTトークンコマンドを実行することを検証します。ベンダーが指定したapplication property templateが返されます。 |
| DTR | • DTR-06.02.01.03 • DTR-06.02.02.09 • DTR-06.03.02.01 • DTR-06.03.02.03 • DTR-06.03.02.04 • DTR-06.03.02.05 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 |
| • Suitable drivers have been loaded between the test system and an instance of the reader. | |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the SELECT command without the version number • AID == 'A0 00 00 03 08 00 00 20 00' |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00' at the end. Check that the application property template conforms to Table 3 of [SP800-73], Part 2, with the exception that the returned AID is the AID listed in Section B.1.1 of [SP800-157]. 2. From Step 2, the command returns the application property template with the status word '90 00' at the end. Check that the application property template conforms to Table 3 of [SP800-73], Part 2, with the exception that the returned AID is the AID listed in Section B.1.1 of [SP800-157]. |
| Postcondition(s) | The Derived PIV Application is now the currently selected application. The application security status of the Derived PIV Application is established. |
| • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 | |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. バージョン番号なしでSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00' |
| 期待結果 | 1. 手順1について、コマンドは末尾にステータスワード '90 00' を付けてapplication property templateを返します。application property templateが[SP800-73]第2部の表3に適合していることを確認します。ただし、返されるAIDは[SP800-157]の第B 2. 手順2について、コマンドは末尾にステータスワード '90 00' を付けてapplication property templateを返します。application property templateが[SP800-73]第2部の表3に適合していることを確認します。ただし、返されるAIDは[SP800-157]の第B |
| 事後条件 | 派生PIVアプリケーションが現在選択されているアプリケーションになっています。派生PIVアプリケーションのアプリケーションセキュリティ状態が確立されています。 |
8.3.1.2 Default Selected Application
8.3.1.2 デフォルトで選択されるアプリケーション
| Test Assertion | TA-08.03.01.02 |
|---|---|
| Purpose | Confirms that a default selected application exists on the hardware token. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.02.02 |
| Vendor Documentation | The vendor to provide information in its documentation stating which is the application selected by default within its implementation. |
| テストアサーション | TA-08.03.01.02 |
|---|---|
| 目的 | デフォルトで選択されるアプリケーションがハードウェアトークン上に存在することを確認します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.02.02 |
| ベンダー文書 | ベンダーは、その実装でデフォルトで選択されるアプリケーションがどれであるかを示す情報を文書で提供します。 |
8.3.1.3 Select when Derived PIV Application is Currently Selected
8.3.1.3 Derived PIV Applicationが現在選択されている場合の選択
| Test Assertion | TA-08.03.01.03 |
|---|---|
| Purpose | Verifies that the Derived PIV Application is not deselected while the currently selected application is the Derived PIV Application and the SELECT command is sent with an AID of the Derived PIV Application. The security status remains unchanged in this case. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.02.06 |
| Vendor Documentation | None. |
| テストアサーション | TA-08.03.01.03 |
|---|---|
| 目的 | 現在選択されているアプリケーションが派生PIVアプリケーションであり、派生PIVアプリケーションのAIDを指定してSELECTコマンドが送信された場合に、派生PIVアプリケーションの選択が解除されないことを検証します。この場合、セキュリティ状態は変更されません。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.02.06 |
| ベンダー文書 | なし。 |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password’s retry counter is not 0. |
|---|---|
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Repeat Step 1 4. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07' or '11' P2, key reference, is set to '9A' indicating the Derived PIV Authentication key • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00'. 3. From Step 3, the command returns the application property template with the status word '90 00'. 4. From Step 4, the command returns the signed challenge with status word '90 00'. |
| Postcondition(s) | The Derived PIV Application is the currently selected application and the security status of the Derived PIV Application Password is TRUE. |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
|---|---|
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値の全長を8バイトにする 3. 手順1を繰り返す 4. GENERAL AUTHENTICATEコマンドを送信する • CLA は次のように設定する: 1. コマンドチェーンが不要な場合は '00'、コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07' または '11' に設定し、P2(鍵参照)をDerived PIV認証鍵を示す '9A' に設定する • コマンドのデータフィールドには、チャレンジを指定する '81'、続けてランダムに生成したチャレンジ、さらに応答を要求するための '82 00' を含める |
| 期待結果 | 1. 手順1について、コマンドはステータスワード '90 00' を付けてapplication property templateを返します。 2. 手順2について、コマンドはステータスワード '90 00' を返します。 3. 手順3について、コマンドはステータスワード '90 00' を付けてapplication property templateを返します。 4. 手順4について、コマンドはステータスワード '90 00' を付けて署名済みチャレンジを返します。 |
| 事後条件 | 派生PIVアプリケーションが現在選択されているアプリケーションであり、派生PIVアプリケーションのパスワードのセキュリティ状態がTRUEです。 |
8.3.1.4 Select with an Invalid AID when Derived PIV Application is Currently Selected
8.3.1.4 Derived PIV Applicationが現在選択されている場合の無効なAIDによる選択
| Test Assertion | TA-08.03.01.04 |
|---|---|
| Purpose | Verifies that the Derived PIV Application is not deselected while the currently selected application is the Derived PIV Application and the SELECT command is sent with an AID that is not supported. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.02 • DTR-06.03.02.07 |
| Vendor Documentation | None. |
| テストアサーション | TA-08.03.01.04 |
|---|---|
| 目的 | 現在選択されているアプリケーションが派生PIVアプリケーションであり、サポートされていないAIDを指定してSELECTコマンドが送信された場合に、派生PIVアプリケーションの選択が解除されないことを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.02 • DTR-06.03.02.07 |
| ベンダー文書 | なし。 |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password’s retry counter is not 0. |
|---|---|
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Repeat Step 1 with • AID == 'A0 00 00 03 08 00 00 00 00' (invalid AID) 4. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07' or '11'. P2, key reference, is set to '9A' indicating the Derived PIV Authentication Key • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00'. 3. From Step 3, the command returns '6A 82' (application not found). 4. From Step 4, the command returns the signed challenge with the status word '90 00'. |
| Postcondition(s) | The Derived PIV Application continues to be the currently selected application and the application security status of the Derived PIV Application Password is TRUE. |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
|---|---|
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値の全長を8バイトにする 3. 次の内容で手順1を繰り返す • AID == 'A0 00 00 03 08 00 00 00 00'(無効なAID) 4. GENERAL AUTHENTICATEコマンドを送信する • CLA は次のように設定する: 1. コマンドチェーンが不要な場合は '00'、コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07' または '11' に設定します。P2(鍵参照)をDerived PIV認証鍵を示す '9A' に設定する • コマンドのデータフィールドには、チャレンジを指定する '81'、続けてランダムに生成したチャレンジ、さらに応答を要求するための '82 00' を含める |
| 期待結果 | 1. 手順1について、コマンドはステータスワード '90 00' を付けてapplication property templateを返します。 2. 手順2について、コマンドはステータスワード '90 00' を返します。 3. 手順3について、コマンドは '6A 82'(アプリケーションが見つからない)を返します。 4. 手順4について、コマンドはステータスワード '90 00' を付けて署名済みチャレンジを返します。 |
| 事後条件 | 派生PIVアプリケーションが引き続き現在選択されているアプリケーションであり、派生PIVアプリケーションのパスワードのアプリケーションセキュリティ状態がTRUEです。 |
8.3.1.5 Select with Another Valid AID when Derived PIV Application is Currently Selected
8.3.1.5 派生PIVアプリケーションが現在選択されている状態での、別の有効なAIDによるSELECT
| Test Assertion | TA-08.03.01.05 |
|---|---|
| Purpose | Confirms that the Derived PIV Application is deselected when the currently selected application is the Derived PIV Application and the SELECT command is sent with another valid AID that is supported. |
| DTR(s) | • DTR-06.03.02.08 |
| Vendor Documentation | The vendor to provide information in its documentation validating compliance with this requirement. |
| テストアサーション | TA-08.03.01.05 |
|---|---|
| 目的 | 現在選択されているアプリケーションが派生PIVアプリケーションであり、サポートされている別の有効なAIDを指定してSELECTコマンドが送信された場合に、派生PIVアプリケーションの選択が解除されることを確認します。 |
| DTR | • DTR-06.03.02.08 |
| ベンダー文書 | ベンダーは、この要件への準拠を検証する情報を文書で提供します。 |
8.3.2 GET DATA Command
8.3.2 GET DATAコマンド
8.3.2.1 Get Data for the Various Derived PIV Data Objects
8.3.2.1 各種Derived PIVデータオブジェクトの取得
| Test Assertion | TA-08.03.02.01 |
|---|---|
| Purpose | Verifies that the Derived PIV Application accepts the GET DATA command with the access rule of each container as specified in Table 2 of [SP800-73], Part 1 as mapped to [SP800-157]. This test is applicable to the mandatory and the optional data objects specified in [SP800-157]. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.03.01 • DTR-06.03.03.02 • DTR-06.03.03.03 |
| Vendor Documentation | The vendor to provide information in its documentation stating all the optional data objects supported. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The mandatory and optional data objects supported by the Derived PIV Application are loaded. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. If the X.509 Certificate for Digital Signature is supported, send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object 4. If the X.509 Certificate for Key Management is supported, send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 5. If the Key History Object and the Retired X.509 Certificates for Key Management are supported, send the GET DATA command with A. Data field of the command containing the tag ('5FC10C') of the Key History Object B. Data field of the command containing the tag ('5FC10D' to '5FC120') of a Retired X.509 Certificate for Key Management (send a separate command for each supported Retired X.509 Certificate for Key Management) |
| テストアサーション | TA-08.03.02.01 |
|---|---|
| 目的 | 派生PIVアプリケーションが、[SP800-157]に対応付けた[SP800-73]第1部の表2に規定された各コンテナのアクセスルールに従って、GET DATAコマンドを受け付けることを検証します。この試験は、[SP800-157]に規定された必須およびオプションのデータオブジェクトに適用されます。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.03.01 • DTR-06.03.03.02 • DTR-06.03.03.03 |
| ベンダー文書 | ベンダーは、サポートするすべてのオプションのデータオブジェクトを示す情報を文書で提供します。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションがサポートする必須およびオプションのデータオブジェクトが読み込まれています。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、X.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. X.509 Certificate for Digital Signatureがサポートされている場合、次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、X.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める 4. X.509 Certificate for Key Managementがサポートされている場合、次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、X.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 5. Key History ObjectおよびRetired X.509 Certificates for Key Managementがサポートされている場合、次の内容でGET DATAコマンドを送信する A. コマンドのデータフィールドには、Key History Objectのタグ('5FC10C')を含める B. コマンドのデータフィールドには、Retired X.509 Certificate for Key Managementのタグ('5FC10D' から '5FC120')を含める(サポートされている各Retired X.509 Certificate for Key Managementについて、個別のコマンドを送信する) |
| 6. If the Discovery Object is supported, send the GET DATA command with • Data field of the command containing the tag ('7E') of the Discovery Object 7. If the Security Object is supported, send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 8. Send the GET DATA command with • Data field of the command containing a tag that does not identify any of the data objects within the Derived PIV Application. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. For Steps 2, 3, 4, 5A, 5B, 6 and 7, each command returns the requested data object along with the status word '90 00'. 3. For Step 8, the command returns status word '6A 82' (data object not found). |
| Postcondition(s) | N/A |
| 6. Discovery Objectがサポートされている場合、次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、Discovery Objectのタグ('7E')を含める 7. Security Objectがサポートされている場合、次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、Security Objectのタグ('5FC106')を含める 8. 次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、派生PIVアプリケーション内のどのデータオブジェクトも識別しないタグを含めます。 | |
| 期待結果 | 1. 手順1について、コマンドはステータスワード '90 00' を付けてapplication property templateを返します。 2. 手順2、3、4、5A、5B、6、7について、各コマンドは要求されたデータオブジェクトをステータスワード '90 00' とともに返します。 3. 手順8について、コマンドはステータスワード '6A 82'(データオブジェクトが見つからない)を返します。 |
| 事後条件 | 該当なし |
8.3.3 GENERAL AUTHENTICATE Command
8.3.3 GENERAL AUTHENTICATEコマンド
8.3.3.1 Internal Authenticate with the Derived PIV Authentication Key
8.3.3.1 Derived PIV認証鍵による内部認証
| Test Assertion | TA-08.03.03.01 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the GENERAL AUTHENTICATE command appropriately when authenticating to the test toolkit application. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.01 • DTR-06.03.04.05 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or |
| テストアサーション | TA-08.03.03.01 |
|---|---|
| 目的 | テストツールキットアプリケーションに対して認証する場合に、派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.01 • DTR-06.03.04.05 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. GENERAL AUTHENTICATEコマンドを送信する • CLA は次のように設定する: 1. コマンドチェーンが不要な場合は '00'、または |
| 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07' or '11' • P2, key reference, is set to '9A' (the Derived PIV Authentication key) • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response 3. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 4. Repeat Step 2 | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '69 82' (security status not satisfied). 3. From Step 3, the command returns status word '90 00'. 4. From Step 4, the command returns the signed challenge with status word '90 00'. Verify the signed challenge. |
| Postcondition(s) | N/A |
| 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07' または '11' に設定する • P2(鍵参照)を '9A'(Derived PIV認証鍵)に設定する • コマンドのデータフィールドには、チャレンジを指定する '81'、続けてランダムに生成したチャレンジ、さらに応答を要求するための '82 00' を含める 3. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値の全長を8バイトにする 4. 手順2を繰り返す | |
| 期待結果 | 1. 手順1について、コマンドはステータスワード '90 00' を付けてapplication property templateを返します。 2. 手順2について、コマンドはステータスワード '69 82'(セキュリティ状態が満たされていない)を返します。 3. 手順3について、コマンドはステータスワード '90 00' を返します。 4. 手順4について、コマンドはステータスワード '90 00' を付けて署名済みチャレンジを返します。署名済みチャレンジを検証します。 |
| 事後条件 | 該当なし |
8.3.3.2 Internal Authenticate with the Derived PIV Authentication Key (with an Invalid Algorithm Reference and Data Length)
8.3.3.2 派生PIV認証鍵による内部認証(無効なアルゴリズム参照およびデータ長の場合)
| Test Assertion | TA-08.03.03.02 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the GENERAL AUTHENTICATE command appropriately when authenticating to the test toolkit application using an invalid algorithm reference or data length. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.01 • DTR-06.03.04.05 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| テストアサーション | TA-08.03.03.02 |
|---|---|
| 目的 | 無効なアルゴリズム参照またはデータ長を使用してテストツールキットアプリケーションに対して認証する場合に、派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.01 • DTR-06.03.04.05 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to something other than '07' or '11' (indicating an invalid algorithm reference) • P2, key reference, is set to '9A' (the Derived PIV Authentication key) • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response 4. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07' or '11' • P2, key reference, is set to '9A' (the Derived PIV Authentication key) • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge (which is of incorrect length based on the chosen algorithm [e.g., challenge is greater than they key size]), and '82 00' in order to request a response |
|---|---|
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00'. 3. From Step 3, the command returns status word '6A 86' (incorrect parameter in P1 or P2). 4. From Step 4, the command returns status word '6A 80' (incorrect parameter in command data field). |
| Postcondition(s) | N/A |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値の全長を8バイトにする 3. GENERAL AUTHENTICATEコマンドを送信する • CLA は次のように設定する: 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07' または '11' 以外の値に設定する(無効なアルゴリズム参照を示す) • P2(鍵参照)を '9A'(Derived PIV認証鍵)に設定する • コマンドのデータフィールドには、チャレンジを指定する '81'、続けてランダムに生成したチャレンジ、さらに応答を要求するための '82 00' を含める 4. GENERAL AUTHENTICATEコマンドを送信する • CLA は次のように設定する: 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07' または '11' に設定する • P2(鍵参照)を '9A'(Derived PIV認証鍵)に設定する • コマンドのデータフィールドには、チャレンジを指定する '81'、続けてランダムに生成したチャレンジ(選択したアルゴリズムに対して長さが正しくないもの[例:チャレンジが鍵サイズより大きい])、さらに応答を要求するための '82 00' を含める |
|---|---|
| 期待結果 | 1. 手順1について、コマンドはステータスワード '90 00' を付けてapplication property templateを返します。 2. 手順2について、コマンドはステータスワード '90 00' を返します。 3. 手順3について、コマンドはステータスワード '6A 86'(P1またはP2のパラメータが正しくない)を返します。 4. 手順4について、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが正しくない)を返します。 |
| 事後条件 | 該当なし |
8.3.3.3 Mutual Authenticate with Derived PIV Token Management Key
8.3.3.3 Derived PIVトークン管理鍵による相互認証
| Test Assertion | TA-08.03.03.03 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the GENERAL AUTHENTICATE command appropriately when mutually |
| テストアサーション | TA-08.03.03.03 |
|---|---|
| 目的 | 派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに適切に応答することを検証します。対象は、 |
| authenticating to the test toolkit application using the Derived PIV Token Management Key (if supported). | |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.04.01 • DTR-06.03.04.05 |
| Vendor Documentation | The vendor to provide in its documentation whether the Derived PIV Token Management Key is supported, and if yes, the value of the key. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GENERAL AUTHENTICATE command • CLA is set to '00' • P1, algorithm reference, is set to '00', '03', '08', '0A', or '0C' • P2, key reference, is set to '9B' • Data field in the command is to include '80' requesting a witness from the Derived PIV Application 3. Send the GENERAL AUTHENTICATE command • CLA is set to '00' • P1, algorithm reference is set to the same value as specified in Step 2. • P2, key reference is set to '9B' Data field in the command is to include '80' followed by decryption of the witness sent by the Derived PIV Application and '81' followed by a challenge and then '82 00' |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns with the witness followed by status word '90 00'. 3. From Step 3, the Derived PIV Application verifies the decrypted witness and then responds with encryption of the challenge sent by Test Toolkit Application followed by status word '90 00'. Decrypt the encrypted challenge and compare it to the one sent to the token. |
| Postcondition(s) | N/A |
| Derived PIV Token Management Key(サポートされている場合)を使用してテストツールキットアプリケーションと相互認証する場合です。 | |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.04.01 • DTR-06.03.04.05 |
| ベンダー文書 | ベンダーは、Derived PIV Token Management Keyがサポートされているかどうか、サポートされている場合は鍵の値を文書に記載します。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. GENERAL AUTHENTICATEコマンドを送信する • CLAを '00' に設定する • P1(アルゴリズム参照)を '00'、'03'、'08'、'0A'、または '0C' に設定する • P2(鍵参照)を '9B' に設定する • コマンドのデータフィールドには、派生PIVアプリケーションからのウィットネスを要求する '80' を含める 3. GENERAL AUTHENTICATEコマンドを送信する • CLAを '00' に設定する • P1(アルゴリズム参照)を手順2で指定した値と同じ値に設定します。 • P2(鍵参照)を '9B' に設定します。コマンドのデータフィールドには、'80' に続けて、派生PIVアプリケーションが送信したウィットネスの復号結果、さらに '81' に続けてチャレンジ、その後に '82 00' を含める |
| 期待結果 | 1. 手順1について、コマンドはステータスワード '90 00' を付けてapplication property templateを返します。 2. 手順2について、コマンドはウィットネスに続けてステータスワード '90 00' を返します。 3. 手順3について、派生PIVアプリケーションは復号されたウィットネスを検証し、Test Toolkit Applicationが送信したチャレンジの暗号化結果に続けてステータスワード '90 00' で応答します。暗号化されたチャレンジを復号し、トークンに送信したものと比較します。 |
| 事後条件 | 該当なし |
8.3.3.4 External Authenticate with Derived PIV Token Management Key
8.3.3.4 Derived PIVトークン管理鍵による外部認証
| Test Assertion | TA-08.03.03.04 |
|---|
| テストアサーション | TA-08.03.03.04 |
|---|
| Purpose | Verifies that the Derived PIV Application responds to the GENERAL AUTHENTICATE command appropriately when externally authenticating to the test toolkit application using the Derived PIV Token Management Key (if supported). |
|---|---|
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.04.01 • DTR-06.03.04.05 |
| Vendor Documentation | The vendor to provide in its documentation whether the Derived PIV Token Management Key is supported and if yes, the value of the key. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GENERAL AUTHENTICATE command • CLA is set to '00' • P1, algorithm reference, is set to '00', '03', '08', '0A', or '0C' • P2, key reference, is set to '9B' • Data field in the command is to include '81' followed by '00' indicating it is a request for challenge 3. Send the GENERAL AUTHENTICATE command • CLA is set to '00' • P1, algorithm reference, is set to the same value as in Step 2 • P2, key reference, is set to '9B' • Data field in the command is to include '82' followed by an encrypted challenge |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns a challenge followed by status word '90 00'. 3. From Step 3, the Test Toolkit Application responds with encryption of the challenge sent by Derived PIV Application. The token returns status word '90 00'. |
| Postcondition(s) | N/A |
| 目的 | Derived PIV Token Management Key(サポートされている場合)を使用してテストツールキットアプリケーションに対して外部認証する場合に、派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに適切に応答することを検証します。 |
|---|---|
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.04.01 • DTR-06.03.04.05 |
| ベンダー文書 | ベンダーは、Derived PIV Token Management Keyがサポートされているかどうか、サポートされている場合は鍵の値を、文書で提供します。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. GENERAL AUTHENTICATEコマンドを送信する • CLA を '00' に設定する • P1(アルゴリズム参照)を '00'、'03'、'08'、'0A'、または '0C' に設定する • P2(鍵参照)を '9B' に設定する • コマンドのデータフィールドには、チャレンジの要求であることを示す '81' に続けて '00' を含める 3. GENERAL AUTHENTICATEコマンドを送信する • CLA を '00' に設定する • P1(アルゴリズム参照)を手順2と同じ値に設定する • P2(鍵参照)を '9B' に設定する • コマンドのデータフィールドには、'82' に続けて暗号化されたチャレンジを含める |
| 期待結果 | 1. 手順1について、コマンドはステータスワード '90 00' を付けてapplication property templateを返します。 2. 手順2について、コマンドはチャレンジに続けてステータスワード '90 00' を返します。 3. 手順3について、Test Toolkit Applicationは派生PIVアプリケーションが送信したチャレンジの暗号化結果で応答します。トークンはステータスワード '90 00' を返します。 |
| 事後条件 | 該当なし |
8.3.3.5 General Authenticate with the Digital Signature Key
8.3.3.5 デジタル署名鍵によるGENERAL AUTHENTICATE
| Test Assertion | TA-08.03.03.05 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the GENERAL AUTHENTICATE command appropriately when signing using the digital signature key. |
| テストアサーション | TA-08.03.03.05 |
|---|---|
| 目的 | デジタル署名鍵を使用して署名する場合に、派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに適切に応答することを検証します。 |
| DTR(s) | • DTR-06.02.02.09 • DTR-06 • DTR-06.03.04.02 • DTR-06.03.04.05 |
|---|---|
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07', '11' or '14' • P2, key reference, is set to '9C' indicating the digital signature key • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response 3. Send the VERIFY command with • P2, key reference value, is set to ‘80’ • Data field of the command will contain the correct Derived PIV Application Password, padded with ‘FF’ (if necessary) to complete the total length of the value to 8 bytes 4. Repeat Step 2 5. Repeat Step 2 |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word ‘90 00’. 2. From Step 2, the command returns status word '69 82' (security status not satisfied). 3. From Step 3, the command returns status word '90 00'. 4. From Step 4, the command returns the signed challenge with status word ‘90 00’. Verify the signature using the public key from the digital signature certificate and the challenge sent to the token. 5. From Step 5, the command returns status word '69 82' (security status not satisfied), since the digital signature key has a “PIN Always” security condition. |
| Postcondition(s) | N/A |
| DTR | • DTR-06.02.02.09 • DTR-06 • DTR-06.03.04.02 • DTR-06.03.04.05 |
|---|---|
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. GENERAL AUTHENTICATEコマンドを送信する • CLA は次のように設定する: 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07'、'11'、または '14' に設定する • P2(鍵参照)をデジタル署名鍵を示す '9C' に設定する • コマンドのデータフィールドには、チャレンジを指定する '81'、続けてランダムに生成したチャレンジ、さらに応答を要求するための '82 00' を含める 3. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を ‘80’ に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて ‘FF’ でパディングして値の全長を8バイトにする 4. 手順2を繰り返す 5. 手順2を繰り返す |
| 期待結果 | 1. 手順1について、コマンドはステータスワード ‘90 00’ を付けてapplication property templateを返します。 2. 手順2について、コマンドはステータスワード '69 82'(セキュリティ状態が満たされていない)を返します。 3. 手順3について、コマンドはステータスワード '90 00' を返します。 4. 手順4について、コマンドはステータスワード ‘90 00’ を付けて署名済みチャレンジを返します。デジタル署名証明書の公開鍵と、トークンに送信したチャレンジを用いて署名を検証します。 5. 手順5について、デジタル署名鍵には “PIN Always” セキュリティ条件があるため、コマンドはステータスワード '69 82'(セキュリティ状態が満たされていない)を返します。 |
| 事後条件 | 該当なし |
8.3.3.6 Internal Authenticate with the Digital Signature Key (with Invalid Algorithm Reference and Data Length)
8.3.3.6 デジタル署名鍵による内部認証(無効なアルゴリズム参照およびデータ長の場合)
| Test Assertion | TA-08.03.03.06 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the GENERAL AUTHENTICATE command appropriately when signing using the digital signature key with an invalid algorithm reference or data length. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.02 • DTR-06.03.04.05 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == ‘A0 00 00 03 08 00 00 20 00 01 00’ 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to something other than '07', '11' or '14' (indicating an invalid algorithm reference) • P2, key reference, is set to '9C' indicating the digital signature key • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response 4. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 5. Send the GENERAL AUTHENTICATE command |
| テストアサーション | TA-08.03.03.06 |
|---|---|
| 目的 | 無効なアルゴリズム参照またはデータ長でデジタル署名鍵を使用して署名する場合に、派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.02 • DTR-06.03.04.05 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == ‘A0 00 00 03 08 00 00 20 00 01 00’ 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値の全長を8バイトにする 3. GENERAL AUTHENTICATEコマンドを送信する • CLA は次のように設定する: 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07'、'11'、'14' 以外の値に設定する(無効なアルゴリズム参照を示す) • P2(鍵参照)をデジタル署名鍵を示す '9C' に設定する • コマンドのデータフィールドには、チャレンジを指定する '81'、続けてランダムに生成したチャレンジ、さらに応答を要求するための '82 00' を含める 4. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値の全長を8バイトにする 5. GENERAL AUTHENTICATEコマンドを送信する |
| • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07', '11' or '14' • P2, key reference, is set to '9C' indicating the digital signature key • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge (with an incorrect length based on the chosen algorithm [e.g., challenge is greater than they key size]), and '82 00' in order to request a response | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00'. 3. From Step 3, the command returns status word '6A 86' (incorrect parameter in P1 or P2). 4. From Step 4, the command returns status word '90 00'. 5. From Step 5, the command returns status word '6A 80' (incorrect parameter in command data field). |
| Postcondition(s) | N/A |
| • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07'、'11' または '14' に設定する • P2(鍵参照)を、デジタル署名鍵を示す '9C' に設定する • コマンドのデータフィールドには、チャレンジを指定する '81' に続けて、無作為に生成したチャレンジ(選択したアルゴリズムに対して不正な長さのもの[例:チャレンジが鍵サイズより大きい])と、レスポンスを要求するための '82 00' を含める | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '90 00' を返します。 3. ステップ3では、コマンドはステータスワード '6A 86'(P1またはP2のパラメータが不正)を返します。 4. ステップ4では、コマンドはステータスワード '90 00' を返します。 5. ステップ5では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 |
| 事後条件 | 該当なし |
8.3.3.7 General Authenticate with the Key Management Key
8.3.3.7 鍵管理鍵によるGENERAL AUTHENTICATE
| Test Assertion | TA-08.03.03.07 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the GENERAL AUTHENTICATE command appropriately when using the key management key. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.03 • DTR-06.03.04.05 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GENERAL AUTHENTICATE command • CLA is set to: |
| テストアサーション | TA-08.03.03.07 |
|---|---|
| 目的 | 鍵管理鍵を使用する場合に、派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.03 • DTR-06.03.04.05 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. GENERAL AUTHENTICATEコマンドを送信する • CLAを次のように設定します。 |
| 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07', '11' or '14' • P2, key reference, is set to '9D' indicating the key management key • Data field in the command is to include one of the following: 1. If P1 = '07', the template '81' contains an encrypted key 2. If P1 = '11' or '14', the template '85' contain the other party’s public key.10 3. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password value, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 4. Repeat Step 2 5. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to something other than '07', '11' or '14' (indicating incorrect algorithm) • P2, key reference, is set to '9D' indicating the key management key • Data field in the command is to include a template appropriate for the '9D' key. 6. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07', '11' or '14' • P2, key reference, is set to '9D' indicating the key management key • Data field in the command is to include a malformed template. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '69 82' (security status not satisfied). 3. From Step 3, the command returns status word '90 00'. 4. From Step 4, for algorithm reference '07' as P1 value, the command returns the transported key with status word '90 00'. Compare the |
| 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07'、'11' または '14' に設定する • P2(鍵参照)を、鍵管理鍵を示す '9D' に設定する • コマンドのデータフィールドには、次のいずれかを含めます。 1. P1 = '07' の場合、テンプレート '81' には暗号化された鍵が含まれる 2. P1 = '11' または '14' の場合、テンプレート '85' には相手側の公開鍵が含まれます。¹⁰ 3. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワード値を含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 4. ステップ2を繰り返す 5. GENERAL AUTHENTICATEコマンドを送信する • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を、'07'、'11'、'14' 以外の値(不正なアルゴリズムを示す)に設定する • P2(鍵参照)を、鍵管理鍵を示す '9D' に設定する • コマンドのデータフィールドには、'9D' 鍵に適したテンプレートを含めます。 6. GENERAL AUTHENTICATEコマンドを送信する • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07'、'11' または '14' に設定する • P2(鍵参照)を、鍵管理鍵を示す '9D' に設定する • コマンドのデータフィールドには、不正な形式のテンプレートを含めます。 | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '69 82'(セキュリティ状態が満たされていない)を返します。 3. ステップ3では、コマンドはステータスワード '90 00' を返します。 4. ステップ4では、P1の値としてアルゴリズム参照 '07' を用いた場合、コマンドはステータスワード '90 00' とともにトランスポートされた鍵を返します。比較する |
| test toolkit application’s copy of the plaintext key to the one received in the response from the token. For algorithm reference '11' or '14' as P1 value, the command returns the shared secret Z11 with status word '90 00'. Compare the shared secret computed by the token with the shared secret computed off token. 5. From Step 5, the command returns status word '6A 86' (incorrect parameter in P1 or P2). 6. From Step 6, the command returns status word '6A 80' (incorrect parameter in command data field). | |
| Postcondition(s) | N/A |
| 試験ツールキットアプリケーションが保持する平文鍵のコピーと、トークンからのレスポンスで受け取った鍵を比較します。P1の値としてアルゴリズム参照 '11' または '14' を用いた場合、コマンドはステータスワード '90 00' とともに共有シークレットZ11を返します。トークンが計算した共有シークレットと、トークン外で計算した共有シークレットを比較します。 5. ステップ5では、コマンドはステータスワード '6A 86'(P1またはP2のパラメータが不正)を返します。 6. ステップ6では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 | |
| 事後条件 | 該当なし |
8.3.3.8 General Authenticate with the Retired Key Management Keys
8.3.3.8 廃止済み鍵管理鍵によるGENERAL AUTHENTICATE
| Test Assertion | TA-08.03.03.08 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the GENERAL AUTHENTICATE command appropriately when using the retired key management keys. |
| DTR(s) | • DTR-06.02.02.03 • DTR-06.03.01.01 • DTR-06.03.04.03 • DTR-06.03.04.05 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password value, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Send the GET DATA command with • Data field of the command containing the tag of the Key History Object data object ('5FC10C'). Retrieve the key history’s data elements: • If keysWithOnCardCerts = 0 and keysWithOffCardCerts > 0 |
| テストアサーション | TA-08.03.03.08 |
|---|---|
| 目的 | 廃止済み鍵管理鍵を使用する場合に、派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.03 • DTR-06.03.01.01 • DTR-06.03.04.03 • DTR-06.03.04.05 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードの値を含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 3. 次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、Key History Objectデータオブジェクトのタグ('5FC10C')を含めます。鍵履歴のデータ要素を取得します。 • keysWithOnCardCerts = 0 かつ keysWithOffCardCerts > 0 の場合 |
| o Read the certificate(s) and key references (pairs) from the vendor provided URL file. For each key reference value in the range (0x95 – keysWithOffCardCerts + 1) through 0x95, verify that the provided URL file includes that key reference, issue a challenge for that key reference (follow Step 2 from TA-08.03.03.07), and verify the response using the public key from the corresponding certificate from the provided URL file • If keysWithOnCardCerts > 0 and keyWithOffCardCerts = 0 o For each key reference value in the range 0x82 through (0x82 + keysWithOnCardCerts – 1), read the certificates from the token and issue a challenge for each retired private key12 (follow Step 2 from TA-08.03.03.07), and verify the response using the public key from the corresponding certificate. • If keysWithOnCardCerts > 0 and keyWithOffCardCerts > 0 For each key reference value in the range 0x82 through (0x82 + keysWithOnCardCerts – 1) and in the range (0x95 – keysWithOffCardCerts + 1) through 0x95, verify that the provided URL file includes that key reference, issue a challenge for that key reference (follow Step 2 from TA-08.03.03.07), and verify the response using the public key from the corresponding certificate from the provided URL file. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00'. 3. From Step 3, the GET DATA commands return the requested data along with status word '90 00'. Each GENERAL AUTHENTICATE command: a. For key transport (as indicated by algorithm reference '07' as P1 value), the command returns the transported key with status word '90 00' at the end. Compare the test toolkit application’s copy of the plaintext key to the one received in the response from the token. b. For ECDH, (as indicated by algorithm reference '11' or '14' as P1 value), the command returns the shared secret Z with status word '90 00'. Compare the shared secret computed by the token with the shared secret computed off token. |
| Postcondition(s) | N/A |
| o ベンダーが提供するURLファイルから、証明書と鍵参照(のペア)を読み取ります。(0x95 – keysWithOffCardCerts + 1) から 0x95 までの範囲の各鍵参照値について、提供されたURLファイルにその鍵参照が含まれていることを確認し、その鍵参照に対するチャレンジを発行し(TA-08 • keysWithOnCardCerts > 0 かつ keyWithOffCardCerts = 0 の場合 o 0x82 から (0x82 + keysWithOnCardCerts – 1) までの範囲の各鍵参照値について、トークンから証明書を読み取り、廃止済みの各秘密鍵12に対するチャレンジを発行し(TA-08 • keysWithOnCardCerts > 0 かつ keyWithOffCardCerts > 0 の場合、0x82 から (0x82 + keysWithOnCardCerts – 1) までの範囲、および (0x95 – keysWithOffCardCerts + 1) から 0x95 までの範囲の各鍵参照値について、提供されたURLファイルにその鍵参照が含まれていることを確認し、その鍵参照に対するチャレンジを発行し(TA-08 | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '90 00' を返します。 3. ステップ3では、GET DATAコマンドはステータスワード '90 00' とともに要求されたデータを返します。各GENERAL AUTHENTICATEコマンドについて、次のとおりとします。 a. 鍵輸送(P1の値としてアルゴリズム参照 '07' で示される)の場合、コマンドは最後にステータスワード '90 00' を付けてトランスポートされた鍵を返します。試験ツールキットアプリケーションが保持する平文鍵のコピーと、トークンからのレスポンスで受け取った鍵を比較します。 b. ECDH(P1の値としてアルゴリズム参照 '11' または '14' で示される)の場合、コマンドはステータスワード '90 00' とともに共有シークレットZを返します。トークンが計算した共有シークレットと、トークン外で計算した共有シークレットを比較します。 |
| 事後条件 | 該当なし |
8.3.3.9 Internal Authenticate with an Invalid Key Reference
8.3.3.9 無効な鍵参照による内部認証
| Test Assertion | TA-08.03.03.09 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the GENERAL AUTHENTICATE command appropriately when authenticating to the test toolkit application using an invalid key reference. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.01 • DTR-06.03.04.02 • DTR-06.03.04.03 • DTR-06.03.04.04 • DTR-06.03.04.05 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07' or '11' • P2, key reference, is set to an incorrect key reference (one that is not supported) • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00'. |
| テストアサーション | TA-08.03.03.09 |
|---|---|
| 目的 | 無効な鍵参照を用いて試験ツールキットアプリケーションに対する認証を行う場合に、派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.04.01 • DTR-06.03.04.02 • DTR-06.03.04.03 • DTR-06.03.04.04 • DTR-06.03.04.05 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 3. GENERAL AUTHENTICATEコマンドを送信する • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07' または '11' に設定する • P2(鍵参照)を、不正な鍵参照(サポートされていないもの)に設定する • コマンドのデータフィールドには、チャレンジを指定する '81' に続けて、無作為に生成したチャレンジと、レスポンスを要求するための '82 00' を含める |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '90 00' を返します。 |
| 3. From Step 3, the command returns status word '6A 86' (incorrect parameter in P1 or P2). | |
| Postcondition(s) | N/A |
| 3. ステップ3では、コマンドはステータスワード '6A 86'(P1またはP2のパラメータが不正)を返します。 | |
| 事後条件 | 該当なし |
8.3.3.10 Support for Command Chaining
8.3.3.10 コマンド連鎖のサポート
| Test Assertion | TA-08.03.03.10 |
|---|---|
| Purpose | Confirms that the Derived PIV Application responds to the GENERAL AUTHENTICATE command and supports command chaining to permit the uninterrupted transmission of long command data fields to the Derived PIV Application. |
| DTR(s) | • DTR-06.03.04.04 • DTR-06.03.04.05 |
| Vendor Documentation | The vendor to provide information in its documentation demonstrating compliance to this requirement. The GET RESPONSE command is used to return the complete result of the cryptographic operation. In addition, if a token command other than the GENERAL AUTHENTICATE command is received by the Derived PIV Application before the termination of a GENERAL AUTHENTICATE chain, the Derived PIV Application rolls back to the state it was in immediately prior to the reception of the first command in the interrupted chain. |
| テストアサーション | TA-08.03.03.10 |
|---|---|
| 目的 | 派生PIVアプリケーションがGENERAL AUTHENTICATEコマンドに応答し、長いコマンドデータフィールドを派生PIVアプリケーションへ中断なく送信できるようにコマンドチェーンをサポートしていることを確認します。 |
| DTR | • DTR-06.03.04.04 • DTR-06.03.04.05 |
| ベンダー文書 | ベンダーは、この要件への準拠を示す情報を文書に記載して提供します。暗号演算の完全な結果を返すには、GET RESPONSEコマンドを使用します。さらに、GENERAL AUTHENTICATEチェーンが終了する前に、GENERAL AUTHENTICATE以外のトークンコマンドを派生PIVアプリケーションが受信した場合、派生PIVアプリケーションは、中断されたチェーンの最初のコマンドを受信する直前の状態にロールバックします。 |
8.3.4 VERIFY Command
8.3.4 VERIFYコマンド
8.3.4.1 Verify with a Valid Key Reference and the Correct Password
8.3.4.1 有効な鍵参照と正しいパスワードによるVERIFY
| Test Assertion | TA-08.03.04.01 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the VERIFY command with a valid key reference and sets the security status appropriately when the correct password is provided. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.02.02.13 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.05.01 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| テストアサーション | TA-08.03.04.01 |
|---|---|
| 目的 | 有効な鍵参照を指定したVERIFYコマンドに派生PIVアプリケーションが応答し、正しいパスワードが提供された場合にセキュリティ状態を適切に設定することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.02.02.13 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.05.01 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07' or '11'. P2, key reference, is set to '9A' indicating the Derived PIV Authentication key • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response |
|---|---|
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00'. 3. From Step 3, the command returns the signed challenge with status word '90 00'. |
| Postcondition(s) | N/A |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 3. GENERAL AUTHENTICATEコマンドを送信する • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07' または '11' に設定します。P2(鍵参照)を、Derived PIV Authentication keyを示す '9A' に設定する • コマンドのデータフィールドには、チャレンジを指定する '81' に続けて、無作為に生成したチャレンジと、レスポンスを要求するための '82 00' を含める |
|---|---|
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '90 00' を返します。 3. ステップ3では、コマンドはステータスワード '90 00' とともに署名済みチャレンジを返します。 |
| 事後条件 | 該当なし |
8.3.4.2 Verify and Reset Security Status
8.3.4.2 Verifyおよびセキュリティ状態のリセット
| Test Assertion | TA-08.03.04.03 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds to the VERIFY command for resetting the security status with the correct key reference. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.05.01 • DTR-06.03.05.05 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| テストアサーション | TA-08.03.04.03 |
|---|---|
| 目的 | セキュリティ状態をリセットするVERIFYコマンドに対して、派生PIVアプリケーションが正しい鍵参照で応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.01.02 • DTR-06.03.05.01 • DTR-06.03.05.05 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Reset the security status of the '80' key reference by sending the VERIFY command with • P2, key reference value, is set to '80' • P1 parameter is 'FF' and both Lc and the data field are absent 4. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07' or '11'. P2, key reference, is set to '9A' indicating the Derived PIV Authentication key • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response |
|---|---|
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00'. 3. From Step 3, the command returns status word '90 00'. 4. From Step 4, the command returns status word '69 82' (security status not satisfied). |
| Postcondition(s) | N/A |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 3. 次の内容でVERIFYコマンドを送信して、'80' 鍵参照のセキュリティ状態をリセットする • P2(鍵参照値)を '80' に設定する • P1パラメータを 'FF' とし、Lcとデータフィールドはいずれも存在しない 4. GENERAL AUTHENTICATEコマンドを送信する • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • P1(アルゴリズム参照)を '07' または '11' に設定します。P2(鍵参照)を、Derived PIV Authentication keyを示す '9A' に設定する • コマンドのデータフィールドには、チャレンジを指定する '81' に続けて、無作為に生成したチャレンジと、レスポンスを要求するための '82 00' を含める |
|---|---|
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '90 00' を返します。 3. ステップ3では、コマンドはステータスワード '90 00' を返します。 4. ステップ4では、コマンドはステータスワード '69 82'(セキュリティ状態が満たされていない)を返します。 |
| 事後条件 | 該当なし |
8.3.4.3 Verify with an Incorrect Length and Padding for the Current Password
8.3.4.3 現在のパスワードの長さおよびパディングが不正な場合のVERIFY
| Test Assertion | TA-08.03.04.04 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds correctly to the VERIFY command when the password length and padding requirements are not met. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.02.02.14 • DTR-06.03.01.01 |
| Vendor Documentation | The vendor to provide in its documentation the status word returned by the Derived PIV Application when the password length or padding requirements are not met. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. |
| テストアサーション | TA-08.03.04.04 |
|---|---|
| 目的 | パスワードの長さとパディングの要件が満たされていない場合に、派生PIVアプリケーションがVERIFYコマンドに正しく応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.02.02.14 • DTR-06.03.01.01 |
| ベンダー文書 | ベンダーは、パスワードの長さまたはパディングの要件が満たされていない場合に派生PIVアプリケーションが返すステータスワードを、文書に記載して提供します。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 |
| • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. The password shall be 6 bytes in length. • The Derived PIV Application Password’s retry counter is greater than 1.13 | |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, NOT padded with 'FF', so that the total length of the value is less than 8 bytes 3. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' to complete the total length of the value to 10 bytes 4. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded to 8 bytes with 'FF' in byte 7 and 'AA' in byte 8 5. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain an arbitrary Derived PIV Application Password which is only 5 bytes in length padded with 'FF' to complete the total length of the value to 8 bytes |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '6A 80' (incorrect parameter in command data field) or '63 CX' (verification failed, with X indicating the number of further allowed retries) (verify the error code supplied matches what is described in vendor documentation). 3. From Step 3, the command returns status word '6A 80' (incorrect parameter command data field) or '63 CX' (verification failed, with X indicating the number of further allowed retries (verify the error code supplied matches what is described in vendor documentation). 4. From Step 4, the command returns status word '6A 80' (incorrect parameter in command data field) or '63 CX' (verification failed, |
| • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。パスワードは6バイトの長さでなければなりません。 • 派生PIVアプリケーションのパスワードのリトライカウンタが1より大きい値です。13 | |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、'FF' でパディングせず、値全体の長さを8バイト未満にする 3. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、'FF' でパディングして値全体の長さを10バイトにする 4. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、7バイト目に 'FF'、8バイト目に 'AA' を入れて8バイトにパディングする 5. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、5バイトのみの任意の派生PIVアプリケーションのパスワードを含め、'FF' でパディングして値全体の長さを8バイトにする |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)または '63 CX'(検証失敗。X は許容される残りの再試行回数を示す)を返します(返されたエラーコードがベンダー文書の記述と一致することを確認します)。 3. ステップ3では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)または '63 CX'(検証失敗。X は許容される残りの再試行回数を示す)を返します(返されたエラーコードがベンダー文書の記述と一致することを確認します)。 4. ステップ4では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)または '63 CX'(検証失敗、 |
| with X indicating the number of further allowed retries) (verify the error code supplied matches what is described in vendor documentation). 5. From Step 5, the command returns status word '6A 80' (incorrect parameter in command data field) or '63 CX' (verification failed, with X indicating the number of further allowed retries) (verify the error code supplied matches what is described in vendor documentation). | |
| Postcondition(s) | N/A |
| Xは許容される残りの再試行回数を示す)を返します(返されたエラーコードがベンダー文書の記述と一致することを確認します)。 5. ステップ5では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)または '63 CX'(検証失敗。X は許容される残りの再試行回数を示す)を返します(返されたエラーコードがベンダー文書の記述と一致することを確認します)。 | |
| 事後条件 | 該当なし |
8.3.4.4 Verify with an Incorrect Format for the Current Password
8.3.4.4 現在のパスワードの形式が不正な場合のVERIFY
| Test Assertion | TA-08.03.04.05 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds appropriately to the VERIFY command when an incorrectly formatted password is passed. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.02.02.13 • DTR-06.02.02.14 • DTR-06.02.02.15 • DTR-06.03.01.01 |
| Vendor Documentation | The vendor to provide in its documentation the status word returned by the Derived PIV Application when the password format requirements are not met. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is greater than 1. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain an arbitrary Derived PIV Application Password where the first byte is 0x5B and all other non-padded bytes contain values limited to either 0x30–0x39 or 0x41-0x5A or 0x61-0x7A, padded with 'FF' to complete the total length of the value to 8 bytes 3. Repeat Step 2 five times with byte positions 2, 3, 4, 5, and 6 containing the 0x5B byte, respectively. Note: It may be necessary to send the VERIFY command with a correct Derived PIV Application Password in |
| テストアサーション | TA-08.03.04.05 |
|---|---|
| 目的 | 形式が誤ったパスワードが渡された場合に、派生PIVアプリケーションがVERIFYコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.02.02.13 • DTR-06.02.02.14 • DTR-06.02.02.15 • DTR-06.03.01.01 |
| ベンダー文書 | ベンダーは、パスワードの形式要件が満たされていない場合に派生PIVアプリケーションが返すステータスワードを、文書に記載して提供します。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが1より大きい値です。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、1バイト目が0x5Bで、パディングされていない他のすべてのバイトの値が 0x30–0x39、0x41-0x5A、0x61-0x7A のいずれかに限られる任意の派生PIVアプリケーションのパスワードを含め、'FF' でパディングして値全体の長さを8バイトにする 3. バイト位置2、3、4、5、6にそれぞれ0x5Bのバイトを入れて、ステップ2を5回繰り返します。注:必要に応じて、正しい派生PIVアプリケーションのパスワードを指定したVERIFYコマンドを |
| order to prevent the retry counter from decrementing to zero. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '6A 80' (incorrect parameter in command data field) or '63 CX' (verification failed, with X indicating the number of further allowed retries). Verify the error code supplied matches what is described in the vendor’s documentation. 3. From Step 3, all commands return status word '6A 80' (incorrect parameter command data field) or '63 CX' (verification failed, with X indicating the number of further allowed retries). Verify the error code supplied matches what is described in the vendor’s documentation. |
| Postcondition(s) | N/A |
| リトライカウンタが0まで減らないように送信します。 | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)または '63 CX'(検証失敗。X は許容される残りの再試行回数を示す)を返します。返されたエラーコードがベンダー文書の記述と一致することを確認します。 3. ステップ3では、すべてのコマンドがステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)または '63 CX'(検証失敗。X は許容される残りの再試行回数を示す)を返します。返されたエラーコードがベンダー文書の記述と一致することを確認します。 |
| 事後条件 | 該当なし |
8.3.4.5 Verify with an Incorrect Password/Blocking the Derived PIV Application
8.3.4.5 誤ったパスワードによる検証/派生PIVアプリケーションのブロック
| Test Assertion | TA-08.03.04.06 |
|---|---|
| Purpose | Verifies that the Derived PIV Application is blocked based on the retry counter when a correctly formatted, but incorrect password is sent repeatedly using the VERIFY command. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.05.02 • DTR-06.03.05.03 • DTR-06.03.05.04 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command repeatedly, until after the issuer specified maximum number of password tries is exceeded with • P2, key reference value, is set to '80' • Data field of the command will contain an arbitrary, but correctly formatted, password value other than what is obtained from the vendor, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes |
| テストアサーション | TA-08.03.04.06 |
|---|---|
| 目的 | 形式は正しいが誤ったパスワードをVERIFYコマンドで繰り返し送信した場合に、リトライカウンタに基づいて派生PIVアプリケーションがブロックされることを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.05.02 • DTR-06.03.05.03 • DTR-06.03.05.04 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 発行者が指定したパスワード試行回数の上限を超えるまで、次の内容でVERIFYコマンドを繰り返し送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、ベンダーから取得した値以外の、任意だが形式が正しいパスワード値を含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする |
| 3. Send the VERIFY command after the issuer specified maximum number of password tries is exceeded with • P2, key reference value, is set to '80' • Data field of the command will contain the correct password value, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '63 CX' until the maximum number of password tries is reached (X indicates the number of further allowed retries). The command returns status word '69 83' (authentication method blocked) when the maximum number of password tries is exceeded. 3. From Step 3, the command returns status word '69 83' (authentication method blocked). |
| Postcondition(s) | The Derived PIV Application Password’s retry counter is 0. |
| 3. 発行者が指定したパスワード試行回数の上限を超えた後に、次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しいパスワード値を含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、パスワード試行回数の上限に達するまで、コマンドはステータスワード '63 CX' を返します(X は許容される残りの再試行回数を示します)。パスワード試行回数の上限を超えると、コマンドはステータスワード '69 83'(認証方式がブロックされている)を返します。 3. ステップ3では、コマンドはステータスワード '69 83'(認証方式がブロックされている)を返します。 |
| 事後条件 | 派生PIVアプリケーションのパスワードのリトライカウンタが0です。 |
8.3.5 CHANGE REFERENCE DATA Command
8.3.5 CHANGE REFERENCE DATAコマンド
8.3.5.1 Change Reference Data with the Correct Derived PIV Application Password and with the Correct PUK
8.3.5.1 正しい派生PIVアプリケーションパスワードおよび正しいPUKによるCHANGE REFERENCE DATA
| Test Assertion | TA-08.03.05.01 |
|---|---|
| Purpose | Verifies that the Derived PIV Application can change the current password with CHANGE REFERENCE DATA command. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.05.06 • DTR-06.03.06.01 • DTR-06.03.06.03 |
| Vendor Documentation | The vendor to provide in its documentation the reset retry value of the Derived PIV Application Password |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password and PUK are recorded. • The Derived PIV Application Password’s retry counter and the PUK’s retry counter are not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct password value (password 1), concatenated without delimitation with an arbitrary new valid |
| テストアサーション | TA-08.03.05.01 |
|---|---|
| 目的 | 派生PIVアプリケーションがCHANGE REFERENCE DATAコマンドで現在のパスワードを変更できることを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.05.06 • DTR-06.03.06.01 • DTR-06.03.06.03 |
| ベンダー文書 | ベンダーは、派生PIVアプリケーションのパスワードのリセット後のリトライ値を、文書に記載して提供する |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードとPUKが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタと、PUKのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しいパスワード値(パスワード1)に、区切りなしで、任意の新しい有効な |
| password value (password 2). Both passwords should be padded (if needed) with 'FF' to complete the total length of each value to 8 bytes 3. Send the VERIFY command with • P1, is set to 'FF' • P2, key reference value, is set to '80' • LC and the command data field are absent 4. Send the VERIFY command with • P1, is set to '00' • P2, key reference value, is set to '80' • LC and the command data field are absent 5. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the new password value (password 2 from Step 2), padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes Perform Step 6 only if the Derived PIV Application supports changing the PUK with the CHANGE REFERENCE DATA command. 6. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '81' • Data field of the command will contain the correct PUK value, concatenated without delimitation with an arbitrary new PUK value. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00'. The password has now been changed. 3. From Step 3, the command returns status word '90 00' and the security status of the PIN is reset. 4. From Step 4, the command returns status word '63 CX' where X is equal to the reset retry value of the Derived PIV Application Password. 5. Form Step 5, the command returns status word '90 00' 6. From Step 6, the command returns status word '90 00' and the PUK value has been changed. |
| Postcondition(s) | The Derived PIV Application Password and PUK (if supported) are changed. |
| パスワード値(パスワード2)を連結したものを含めます。どちらのパスワードも、必要に応じて 'FF' でパディングして各値の長さを8バイトにする 3. 次の内容でVERIFYコマンドを送信する • P1を 'FF' に設定する • P2(鍵参照値)を '80' に設定する • LCとコマンドデータフィールドは存在しない 4. 次の内容でVERIFYコマンドを送信する • P1を '00' に設定する • P2(鍵参照値)を '80' に設定する • LCとコマンドデータフィールドは存在しない 5. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、新しいパスワード値(ステップ2のパスワード2)を含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにします。ステップ6は、派生PIVアプリケーションがCHANGE REFERENCE DATAコマンドによるPUKの変更をサポートしている場合にのみ実施します。 6. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '81' に設定する • コマンドのデータフィールドには、正しいPUK値に、区切りなしで、任意の新しいPUK値を連結したものを含めます。 | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '90 00' を返します。パスワードが変更されました。 3. ステップ3では、コマンドはステータスワード '90 00' を返し、PINのセキュリティ状態がリセットされます。 4. ステップ4では、コマンドはステータスワード '63 CX' を返します。ここで X は、派生PIVアプリケーションのパスワードのリセット後のリトライ値に等しい値です。 5. ステップ5では、コマンドはステータスワード '90 00' を返す 6. ステップ6では、コマンドはステータスワード '90 00' を返し、PUK値が変更されました。 |
| 事後条件 | 派生PIVアプリケーションのパスワード(およびサポートされている場合はPUK)が変更されました。 |
8.3.5.2 Change Reference Data with an Invalid Key Reference
8.3.5.2 無効な鍵参照を指定したReference Dataの変更
| Test Assertion | TA-08.03.05.02 |
|---|---|
| Purpose | Verifies that the Derived PIV Application does not change the password with the CHANGE REFERENCE DATA command with an invalid key reference. |
| テストアサーション | TA-08.03.05.02 |
|---|---|
| 目的 | 無効な鍵参照を指定したCHANGE REFERENCE DATAコマンドでは、派生PIVアプリケーションがパスワードを変更しないことを検証します。 |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.06.02 |
|---|---|
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to something that is not '80' or '81' • Data field of the command will contain the correct password value (password 1), concatenated without delimitation with an arbitrary new valid password value (password 2). Both passwords are padded with 'FF' (if necessary) to complete the total length of each value to 8 bytes 3. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the password value (password 1), padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns an error status word. 3. From Step 3, the command returns status word '90 00'. |
| Postcondition(s) | The original password ('80') is still in effect. |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.06.02 |
|---|---|
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を、'80' でも '81' でもない値に設定する • コマンドのデータフィールドには、正しいパスワード値(パスワード1)に、区切りなしで、任意の新しい有効なパスワード値(パスワード2)を連結したものを含めます。どちらのパスワードも、必要に応じて 'FF' でパディングして各値の長さを8バイトにする 3. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、パスワード値(パスワード1)を含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはエラーのステータスワードを返します。 3. ステップ3では、コマンドはステータスワード '90 00' を返します。 |
| 事後条件 | 元のパスワード('80')が引き続き有効です。 |
8.3.5.3 Change Reference Data with an Incorrect Length and Padding for the New Password or with an Incorrect Length of New PUK
8.3.5.3 新しいパスワードの長さとパディングが誤っている場合または新しいPUKの長さが誤っている場合のCHANGE REFERENCE DATA
| Test Assertion | TA-08.03.05.03 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds appropriately to the CHANGE REFERENCE DATA command when the length and padding requirements of the new password are not met or when the length of the new PUK is incorrect. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.02.02.14 • DTR-06.03.01.01 • DTR-06.03.06.05 |
| テストアサーション | TA-08.03.05.03 |
|---|---|
| 目的 | 新しいパスワードの長さとパディングの要件が満たされていない場合、または新しいPUKの長さが正しくない場合に、派生PIVアプリケーションがCHANGE REFERENCE DATAコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.02.02.14 • DTR-06.03.01.01 • DTR-06.03.06.05 |
| • DTR-06.03.06.06 • DTR-06.03.06.08 | |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password and PUK are recorded. • The Derived PIV Application Password’s retry counter and the PUK’s retry counter are not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct password value (password 1) padded to 8 bytes with 'FF' (if necessary) concatenated without delimitation with an arbitrary new password value (password 2) that is padded to less than 8 bytes 3. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct password value (password 1) padded to 8 bytes with 'FF' (if necessary) concatenated without delimitation with an arbitrary new password value (password 2) that is 6 bytes but padded to 8 bytes with 'FF' in byte 7 and 'AA' in byte 8 4. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct password (password 1) padded to 8 bytes with 'FF' (if needed) concatenated without delimitation with an arbitrary new password (password 2) that is less than 6 bytes but padded to 8 bytes with 'FF' 5. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct password (password 1) padded to 8 bytes with 'FF'(if necessary) concatenated without delimitation with an arbitrary new password (password 2) that is greater than 8 bytes in length Perform Steps 6 and 7 only if the Derived PIV Application supports changing the PUK with the CHANGE REFERENCE DATA command. 6. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to ‘81’ |
| • DTR-06.03.06.06 • DTR-06.03.06.08 | |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードとPUKが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタと、PUKのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、必要に応じて 'FF' で8バイトにパディングした正しいパスワード値(パスワード1)に、区切りなしで、8バイト未満の任意の新しいパスワード値(パスワード2)を連結したものを含める 3. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、必要に応じて 'FF' で8バイトにパディングした正しいパスワード値(パスワード1)に、区切りなしで、6バイトだが7バイト目に 'FF'、8バイト目に 'AA' を入れて8バイトにパディングした任意の新しいパスワード値(パスワード2)を連結したものを含める 4. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、必要に応じて 'FF' で8バイトにパディングした正しいパスワード(パスワード1)に、区切りなしで、6バイト未満だが 'FF' で8バイトにパディングした任意の新しいパスワード(パスワード2)を連結したものを含める 5. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、必要に応じて 'FF' で8バイトにパディングした正しいパスワード(パスワード1)に、区切りなしで、長さが8バイトを超える任意の新しいパスワード(パスワード2)を連結したものを含めます。ステップ6と7は、派生PIVアプリケーションがCHANGE REFERENCE DATAコマンドによるPUKの変更をサポートしている場合にのみ実施します。 6. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '81' に設定する |
| • Data field of the command will contain the correct PUK value (PUK 1) concatenated without delimitation with an arbitrary new PUK value (PUK 2) that is less than 8 bytes in length 7. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '81' • Data field of the command will contain the correct PUK (PUK 1) concatenated without delimitation with an arbitrary new PUK (PUK 3) that is greater than 8 bytes in length | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '6A 80' (incorrect parameter in command data field). 3. From Step 3, the command returns status word '6A 80' (incorrect parameter in command data field). 4. From Step 4, the command returns status word '6A 80' (incorrect parameter in command data field). 5. From Step 5, the command returns status word '6A 80' (incorrect parameter in command data field). 6. From Step 6, the command returns status word '6A 80' (incorrect parameter in the command data field). 7. From Step 7, the command returns status word '6A 80' (incorrect parameter in the command data field). |
| Postcondition(s) | Neither the password nor the PUK value has changed. |
| • コマンドのデータフィールドには、正しいPUK値(PUK 1)に、区切りなしで、長さが8バイト未満の任意の新しいPUK値(PUK 2)を連結したものを含める 7. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '81' に設定する • コマンドのデータフィールドには、正しいPUK(PUK 1)に、区切りなしで、長さが8バイトを超える任意の新しいPUK(PUK 3)を連結したものを含める | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 3. ステップ3では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 4. ステップ4では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 5. ステップ5では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 6. ステップ6では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 7. ステップ7では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 |
| 事後条件 | パスワードもPUK値も変更されていません。 |
8.3.5.4 Change Reference Data with an Incorrect Format for the New Password
8.3.5.4 新しいパスワードの形式が不正な場合のReference Dataの変更
| Test Assertion | TA-08.03.05.04 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds appropriately to the CHANGE REFERENCE DATA command when the new password does not satisfy the format requirements. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.02.02.14 • DTR-06.03.01.01 • DTR-06.03.06.05 • DTR-06.03.06.06 • DTR-06.03.06.08 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. |
| テストアサーション | TA-08.03.05.04 |
|---|---|
| 目的 | 新しいパスワードが形式要件を満たしていない場合に、派生PIVアプリケーションがCHANGE REFERENCE DATAコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.02.02.14 • DTR-06.03.01.01 • DTR-06.03.06.05 • DTR-06.03.06.06 • DTR-06.03.06.08 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーのインスタンスとの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 |
| • The Derived PIV Application Password’s retry counter is not 0. | |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct password (password 1) padded to 8 bytes with 'FF' (if needed) concatenated without delimitation with an arbitrary new password value that contains 0x5B in the first byte position, all other non-padded bytes contain values limited to either 0x30–0x39 or 0x41-0x5A or 0x61-0x7A (password 2). Both passwords should be padded with 'FF'(as needed) to complete the total length of each value to 8 bytes (repeat test five times with byte positions 2, 3, 4, 5, and 6 containing the 0x5B byte, respectively) |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, each time the command returns status word '6A 80' (incorrect parameter in command data field). |
| Postcondition(s) | Current password is unchanged. |
| • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 | |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、必要に応じて 'FF' で8バイトにパディングした正しいパスワード(パスワード1)に、区切りなしで、1バイト目に0x5Bを含み、パディングされていない他のすべてのバイトの値が 0x30–0x39、0x41-0x5A、0x61-0x7A のいずれかに限られる任意の新しいパスワード値(パスワード2)を連結したものを含めます。どちらのパスワードも、必要に応じて 'FF' でパディングして各値の長さを8バイトにする(バイト位置2、3、4、5、6にそれぞれ0x5Bのバイトを含めて、試験を5回繰り返す) |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、毎回、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 |
| 事後条件 | 現在のパスワードは変更されていません。 |
8.3.5.5 Change Reference Data with an Incorrect Format for the Current Password
8.3.5.5 現在のパスワードの形式が不正な場合のReference Dataの変更
| Test Assertion | TA-08.03.05.05 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds appropriately to the CHANGE REFERENCE DATA command when the current password format requirements are not met. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.02.02.14 • DTR-06.03.01.01 • DTR-06.03.06.05 • DTR-06.03.06.08 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '80' |
| テストアサーション | TA-08.03.05.05 |
|---|---|
| 目的 | 現在のパスワードが形式要件を満たしていない場合に、派生PIVアプリケーションがCHANGE REFERENCE DATAコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.02.02.14 • DTR-06.03.01.01 • DTR-06.03.06.05 • DTR-06.03.06.08 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーのインスタンスとの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '80' に設定する |
| • Data field of the command will contain an arbitrary password value that contains 0x5B in the first byte position, all other non-padded bytes contain values limited to either 0x30–0x39 or 0x41-0x5A or 0x61-0x7A concatenated without delimitation with a properly formatted new password value where all non-padded bytes contain values limited to either 0x30–0x39 or 0x41-0x5A or 0x61-0x7A. Both passwords should be padded with 'FF'(as needed) to complete the total length of each value to 8 bytes. (repeat test five times with byte positions 2, 3, 4, 5, and 6 containing the 0x5B byte, respectively) Note: In Step 2 it may be necessary to send the VERIFY command with a correct Derived PIV Application Password in order to prevent the retry counter from decrementing to zero. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns either status word: 1) '6A 80' (incorrect parameter in command data field) or 2) '63 CX' and the retry counter is decremented by 1 (where 'X' is the number of tries remaining). |
| Postcondition(s) | Current password is unchanged. |
| • コマンドのデータフィールドには、1バイト目が0x5Bで、パディングされていない他のすべてのバイトの値が 0x30–0x39、0x41-0x5A、0x61-0x7A のいずれかに限られる任意のパスワード値に、区切りなしで、パディングされていないすべてのバイトの値が 0x30–0x39、0x41-0x5A、0x61-0x7A のいずれかに限られる、形式に適合した新しいパスワード値を連結したものを含めます。どちらのパスワードも、必要に応じて 'FF' でパディングして各値の長さを8バイトにすべきです。(バイト位置2、3、4、5、6にそれぞれ0x5Bのバイトを含めて、試験を5回繰り返す)注:ステップ2では、リトライカウンタが0まで減ることを防ぐため、正しい派生PIVアプリケーションのパスワードを指定したVERIFYコマンドを送信する必要がある場合があります。 | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドは次のいずれかのステータスワードを返します。1) '6A 80'(コマンドデータフィールドのパラメータが不正)、または2) '63 CX' を返し、リトライカウンタが1減ります('X' は残りの試行回数)。 |
| 事後条件 | 現在のパスワードは変更されていません。 |
8.3.5.6 Change Reference Data with a Correctly Formatted but Incorrect Current Password or with a Correctly Formatted but Incorrect PUK
8.3.5.6 形式は正しいが誤っている現在のパスワードまたは形式は正しいが誤っているPUKによるCHANGE REFERENCE DATA
| Test Assertion | TA-08.03.05.06 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds appropriately when the CHANGE REFERENCE DATA command is sent repeatedly with a correctly formatted, but incorrect, Derived PIV Application Password or with a correctly formatted, but incorrect, PUK value. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.06.04 • DTR-06.03.06.05 • DTR-06.03.06.07 • DTR-06.03.06.09 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password and the PUK are recorded. |
| テストアサーション | TA-08.03.05.06 |
|---|---|
| 目的 | 形式は正しいが誤った派生PIVアプリケーションのパスワード、または形式は正しいが誤ったPUK値を指定したCHANGE REFERENCE DATAコマンドが繰り返し送信された場合に、派生PIVアプリケーションが適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.06.04 • DTR-06.03.06.05 • DTR-06.03.06.07 • DTR-06.03.06.09 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードとPUKが記録されています。 |
| • The reset retry values for the Derived PIV Application Password and PUK are recorded. • The Derived PIV Application Password’s retry counter and the PUK’s retry counter are not 0. | |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the CHANGE REFERENCE DATA command repeatedly until after the issuer specified maximum number of password tries is exceeded with • P2, key reference value, is set to '80' • Data field of the command will contain an incorrect, but correctly formatted, password value, concatenated without delimitation with a valid new password value. Both passwords should be padded with 'FF' (if necessary) to complete the total length of each value to 8 bytes 3. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to ‘80’ • Data field of the command will contain the correct password value, concatenated without delimitation with a valid new password value. Both passwords should be padded with ‘FF’ (if necessary) to complete the total length of each value to 8 bytes Perform Steps 4 and 5 only if the Derived PIV Application supports changing the PUK with the CHANGE REFERENCE DATA command. 4. Send the CHANGE REFERENCE DATA command repeatedly until after the issuer specified maximum number of PUK tries is exceeded with • P2, key reference value, is set to '81' • Data field of the command will contain an incorrect, but correctly formatted, PUK value, concatenated without delimitation with a valid new PUK value 5. Send the CHANGE REFERENCE DATA command with • P2, key reference value, is set to '81' • Data field of the command will contain the correct PUK value, concatenated without delimitation with a valid new PUK value |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, each time the command returns status word '63 CX' (where 'X' indicates the number of further allowed retries) and the retry counter is decremented. The command returns status word '69 83' (reference data change operation blocked) when the maximum number of tries is exceeded. 3. From Step 3, the command returns status word '69 83' (reference data change operation blocked). 4. From Step 4, each time the command returns status word '63 CX' (where 'X' indicates the number of further allowed retries) and the retry counter is decremented. The command returns status word '69 |
| • 派生PIVアプリケーションのパスワードとPUKのリセット後のリトライ値が記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタとPUKのリトライカウンタが0ではありません。 | |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 発行者が指定したパスワード試行回数の上限を超えた後まで、次の内容でCHANGE REFERENCE DATAコマンドを繰り返し送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、誤っているが形式は正しいパスワード値に、区切りなしで、有効な新しいパスワード値を連結したものを含めます。どちらのパスワードも、必要に応じて 'FF' でパディングして各値の長さを8バイトにする 3. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しいパスワード値に、区切りなしで、有効な新しいパスワード値を連結したものを含めます。どちらのパスワードも、必要に応じて 'FF' でパディングして各値の長さを8バイトにします。ステップ4と5は、派生PIVアプリケーションがCHANGE REFERENCE DATAコマンドによるPUKの変更をサポートしている場合にのみ実施します。 4. 発行者が指定したPUK試行回数の上限を超えた後まで、次の内容でCHANGE REFERENCE DATAコマンドを繰り返し送信する • P2(鍵参照値)を '81' に設定する • コマンドのデータフィールドには、誤っているが形式は正しいPUK値に、区切りなしで、有効な新しいPUK値を連結したものを含める 5. 次の内容でCHANGE REFERENCE DATAコマンドを送信する • P2(鍵参照値)を '81' に設定する • コマンドのデータフィールドには、正しいPUK値に、区切りなしで、有効な新しいPUK値を連結したものを含める |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、毎回、コマンドはステータスワード '63 CX'('X' は許容される残りの再試行回数を示す)を返し、リトライカウンタが減ります。試行回数の上限を超えると、コマンドはステータスワード '69 83'(参照データの変更操作がブロックされている)を返します。 3. ステップ3では、コマンドはステータスワード '69 83'(参照データの変更操作がブロックされている)を返します。 4. ステップ4では、毎回、コマンドはステータスワード '63 CX'('X' は許容される残りの再試行回数を示す)を返し、リトライカウンタが減ります。試行回数の上限を超えると、コマンドはステータスワード '69 |
| 83' (reference data change operation blocked) when the maximum number of tries is exceeded. 5. From Step 5, the command returns status word '69 83' (reference data change operation blocked). | |
| Postcondition(s) | The Derived PIV Application Password’s retry counter and the PUK’s retry counter are 0. |
| 83'(試行回数の上限を超えた場合に返される参照データ変更操作のブロックを示します)。 5. ステップ5では、コマンドはステータスワード '69 83'(参照データの変更操作がブロックされている)を返します。 | |
| 事後条件 | 派生PIVアプリケーションのパスワードのリトライカウンタとPUKのリトライカウンタが0です。 |
8.3.6 RESET RETRY COUNTER Command
8.3.6 RESET RETRY COUNTERコマンド
8.3.6.1 Reset Retry Counter for the Derived PIV Application Password
8.3.6.1 派生PIVアプリケーションのパスワードの再試行カウンターのリセット
| Test Assertion | TA-08.03.06.01 |
|---|---|
| Purpose | Verifies that the Derived PIV Application changes the password with the RESET RETRY COUNTER command when the PUK and command format are correct. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.01 • DTR-06.03.07.08 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The PUK is recorded. • The reset retry value for the Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter and the PUK’s retry counter are not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command contains an arbitrary, but correctly formatted password other than what is obtained from the vendor, padded with 'FF' (as necessary) to complete the total length of the value to 8 bytes 3. Send the RESET RETRY COUNTER command with • P2, key reference value, is set to '80' • Data field of the command contains the PUK value for key reference '80' concatenated without delimitation with a new password padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes. |
| テストアサーション | TA-08.03.06.01 |
|---|---|
| 目的 | PUKとコマンドの形式が正しい場合に、派生PIVアプリケーションがRESET RETRY COUNTERコマンドでパスワードを変更することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.01 • DTR-06.03.07.08 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーのインスタンスとの間に適切なドライバーが読み込まれています。 • PUKが記録されています。 • 派生PIVアプリケーションのパスワードのリセット後のリトライ値が記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタとPUKのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、ベンダーから取得した値以外の、任意だが形式が正しいパスワードを含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 3. 次の内容でRESET RETRY COUNTERコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、鍵参照 '80' に対するPUK値に、区切りなしで、新しいパスワードを連結したものを含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにします。 |
| 4. Obtain number of remaining retries of the '80' key reference by sending the VERIFY command with • P2, key reference value, is set to '80' • P1 parameter is '00' and both Lc and the data field are absent 5. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command contains the new password value, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '63 CX' (where 'X' is the number of retries remaining). The retry counter is decremented by 1. 3. From Step 3, the command returns status word '90 00'. 4. From Step 4, the command returns status word '63 CX' (where 'X' is the number of retries remaining). Verify that 'X' from this step is greater than 'X' from Step 2 and is equal to the reset retry value. 5. From Step 5, the command returns status word '90 00'. |
| Postcondition(s) | The Derived PIV Application Password has been changed. |
| 4. 次の内容でVERIFYコマンドを送信して、'80' 鍵参照の残りの再試行回数を取得する • P2(鍵参照値)を '80' に設定する • P1パラメータを '00' とし、Lcとデータフィールドはいずれも存在しない 5. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、新しいパスワード値を含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '63 CX'('X' は残りの試行回数)を返します。リトライカウンタが1減ります。 3. ステップ3では、コマンドはステータスワード '90 00' を返します。 4. ステップ4では、コマンドはステータスワード '63 CX'('X' は残りの試行回数)を返します。このステップの 'X' がステップ2の 'X' より大きく、かつリセット後のリトライ値に等しいことを確認します。 5. ステップ5では、コマンドはステータスワード '90 00' を返します。 |
| 事後条件 | 派生PIVアプリケーションのパスワードが変更されました。 |
8.3.6.2 Reset Retry Counter with an Invalid Key Reference
8.3.6.2 無効な鍵参照による再試行カウンターのリセット
| Test Assertion | TA-08.03.06.02 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds appropriately to the RESET RETRY COUNTER command for an invalid key reference. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.01 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The PUK is recorded. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the RESET RETRY COUNTER command with • P2, key reference value, is set to a value other than '80' • Data field of the command contains the PUK value for key reference '80', concatenated without delimitation with a valid new password padded |
| テストアサーション | TA-08.03.06.02 |
|---|---|
| 目的 | 無効な鍵参照を指定したRESET RETRY COUNTERコマンドに、派生PIVアプリケーションが適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.01 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーのインスタンスとの間に適切なドライバーが読み込まれています。 • PUKが記録されています。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でRESET RETRY COUNTERコマンドを送信する • P2(鍵参照値)を '80' 以外の値に設定する • コマンドのデータフィールドには、鍵参照 '80' に対するPUK値に、区切りなしで、有効な新しいパスワードをパディングした |
| with 'FF' (if necessary) to complete the total length of the value to 8 bytes | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns an error status word and the PUK’s retry counter remains unchanged. |
| Postcondition(s) | Current password is unchanged. |
| 必要に応じて 'FF' でパディングして値全体の長さを8バイトにする | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはエラーのステータスワードを返し、PUKのリトライカウンタは変化しません。 |
| 事後条件 | 現在のパスワードは変更されていません。 |
8.3.6.3 Reset Retry Counter with an Incorrect Length and Padding for the New Password
8.3.6.3 新しいパスワードの長さとパディングが誤っている場合のRESET RETRY COUNTER
| Test Assertion | TA-08.03.06.03 |
|---|---|
| Purpose | Verifies that the Derived PIV Application does not set a new password with the RESET RETRY COUNTER command when the password length and padding requirements are not met. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.04 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password and the PUK are recorded. • The Derived PIV Application Password’s retry counter and the PUK’s retry counter are not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the RESET RETRY COUNTER command with • P2, key reference value, is set to '80' • Data field of the command contains the PUK value for key reference '80' concatenated with a new password value that is less than 8 bytes in length and is not padded with 'FF' 3. Send the RESET RETRY COUNTER command with • P2, key reference value, is set to '80' • Data field of the command contains the PUK value for key reference '80' concatenated with a new password value that is padded with 'FF' to complete 10 bytes 4. Send the RESET RETRY COUNTER command with • P2, key reference value, is set to '80' • Data field of the command contains the PUK value for key reference '80' concatenated with a new password value that is 6 bytes but padded to 8 bytes with 'FF' in byte 7 and 'AA' in byte 8 5. Send the RESET RETRY COUNTER command with |
| テストアサーション | TA-08.03.06.03 |
|---|---|
| 目的 | パスワードの長さとパディングの要件が満たされていない場合に、派生PIVアプリケーションがRESET RETRY COUNTERコマンドで新しいパスワードを設定しないことを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.04 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードとPUKが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタと、PUKのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でRESET RETRY COUNTERコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、鍵参照 '80' に対するPUK値に、長さが8バイト未満で 'FF' でパディングされていない新しいパスワード値を連結したものを含める 3. 次の内容でRESET RETRY COUNTERコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、鍵参照 '80' に対するPUK値に、'FF' でパディングして10バイトにした新しいパスワード値を連結したものを含める 4. 次の内容でRESET RETRY COUNTERコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、鍵参照 '80' に対するPUK値に、6バイトだが7バイト目に 'FF'、8バイト目に 'AA' を入れて8バイトにパディングした新しいパスワード値を連結したものを含める 5. 次の内容でRESET RETRY COUNTERコマンドを送信する |
| • P2, key reference value, is set to '80' • Data field of the command contains the PUK value for key reference '80' concatenated with a new password value that is less than 6 bytes padded with 'FF' to complete 8 bytes 6. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '6A 80' (incorrect parameter in command data field). 3. From Step 3, the command returns status word '6A 80' (incorrect parameter in command data field). 4. From Step 4, the command returns status word '6A 80' (incorrect parameter in command data field). 5. From Step 5, the command returns status word '6A 80' (incorrect parameter in command data field). 6. From Step 6, the command returns status word '90 00'. |
| Postcondition(s) | Current password is unchanged. |
| • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、鍵参照 '80' に対するPUK値に、6バイト未満で 'FF' でパディングして8バイトにした新しいパスワード値を連結したものを含める 6. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 3. ステップ3では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 4. ステップ4では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 5. ステップ5では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 6. ステップ6では、コマンドはステータスワード '90 00' を返します。 |
| 事後条件 | 現在のパスワードは変更されていません。 |
8.3.6.4 Reset Retry Counter with an Incorrect Format for the New Password
8.3.6.4 新しいパスワードの形式が不正な場合の再試行カウンターのリセット
| Test Assertion | TA-08.03.06.04 |
|---|---|
| Purpose | Verifies that the Derived PIV Application does not set a new password with the RESET RETRY COUNTER command when the format requirements of the new password are not met. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.04 • DTR-06.03.07.05 • DTR-06.03.07.06 • DTR-06.03.07.07 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password and the PUK are recorded. • The Derived PIV Application Password’s retry counter and the PUK’s retry counter are not 0. |
| テストアサーション | TA-08.03.06.04 |
|---|---|
| 目的 | 新しいパスワードが形式要件を満たしていない場合に、派生PIVアプリケーションがRESET RETRY COUNTERコマンドで新しいパスワードを設定しないことを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.04 • DTR-06.03.07.05 • DTR-06.03.07.06 • DTR-06.03.07.07 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードとPUKが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタと、PUKのリトライカウンタが0ではありません。 |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the RESET RETRY COUNTER with • P2, key reference value, is set to '80' • Data field of the command contains the correct PUK value for key reference '80' concatenated without delimitation with an arbitrary new password value that contains 0x5B in the first byte position, all other non-padded bytes contain values limited to either 0x30–0x39 or 0x41-0x5A or 0x61-0x7A. The new password should be padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Repeat Step 2 five times with byte positions 2, 3, 4, 5, and 6 of the password containing the 0x5B byte, respectively. 4. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes |
|---|---|
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '6A 80' (incorrect parameter in command data field). 3. From Step 3, each time the command returns status word '6A 80' (incorrect parameter in command data field). 4. From Step 4, the command returns status word '90 00'. |
| Postcondition(s) | Current password is unchanged. |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でRESET RETRY COUNTERを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、鍵参照 '80' に対する正しいPUK値に、区切りなしで、1バイト目が0x5Bで、パディングされていない他のすべてのバイトの値が 0x30–0x39、0x41-0x5A、0x61-0x7A のいずれかに限られる任意の新しいパスワード値を連結したものを含めます。新しいパスワードは、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 3. パスワードのバイト位置2、3、4、5、6にそれぞれ0x5Bのバイトを入れて、ステップ2を5回繰り返します。 4. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする |
|---|---|
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 3. ステップ3では、毎回、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 4. ステップ4では、コマンドはステータスワード '90 00' を返します。 |
| 事後条件 | 現在のパスワードは変更されていません。 |
8.3.6.5 Reset Retry Counter with an incorrect length for the PUK
8.3.6.5 PUKの長さが不正な場合の再試行カウンターのリセット
| Test Assertion | TA-08.03.06.05 |
|---|---|
| Purpose | Verifies that the Derived PIV Application does not set a new password with the RESET RETRY COUNTER command when the PUK length is incorrect. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.04 • DTR-06.03.07.05 • DTR-06.03.07.06 • DTR-06.03.07.07 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. |
| テストアサーション | TA-08.03.06.05 |
|---|---|
| 目的 | PUKの長さが正しくない場合に、派生PIVアプリケーションがRESET RETRY COUNTERコマンドで新しいパスワードを設定しないことを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.04 • DTR-06.03.07.05 • DTR-06.03.07.06 • DTR-06.03.07.07 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 |
| • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password and the PUK are recorded. • The Derived PIV Application Password’s retry counter is not 0 and the PUK’s retry counter is greater than 1. | |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the RESET RETRY COUNTER with • P2, key reference value, is set to '80' • Data field of the command contains an arbitrary PUK value that is less than 8 bytes in length concatenated without delimitation with an arbitrary new valid password value. The new password should be padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 3. Send the RESET RETRY COUNTER with • P2, key reference value, is set to '80' • Data field of the command contains an arbitrary PUK value that is greater than 8 bytes in length concatenated without delimitation with an arbitrary new valid password value. The new password should be padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 4. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns either status word: 1) '6A 80' (incorrect parameter in command data field) or 2) '63 CX' and the PUK’s retry counter is decremented by 1 (where 'X' is the number of tries remaining). 3. From Step 3, the command returns either status word: 1) '6A 80' (incorrect parameter in command data field) or 2) '63 CX' and the PUK’s retry counter is decremented by 1 (where 'X' is the number of tries remaining). 4. From Step 4, the command returns status word '90 00'. |
| Postcondition(s) | Current password is unchanged. |
| • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードとPUKが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではなく、PUKのリトライカウンタが1より大きい値です。 | |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でRESET RETRY COUNTERを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、長さが8バイト未満の任意のPUK値に、区切りなしで、任意の有効な新しいパスワード値を連結したものを含めます。新しいパスワードは、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 3. 次の内容でRESET RETRY COUNTERを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、長さが8バイトを超える任意のPUK値に、区切りなしで、任意の有効な新しいパスワード値を連結したものを含めます。新しいパスワードは、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 4. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドは次のいずれかのステータスワードを返します。1) '6A 80'(コマンドデータフィールドのパラメータが不正)、または 2) '63 CX' で、PUKのリトライカウンタが1減ります('X' は残りの試行回数)。 3. ステップ3では、コマンドは次のいずれかのステータスワードを返します。1) '6A 80'(コマンドデータフィールドのパラメータが不正)、または 2) '63 CX' で、PUKのリトライカウンタが1減ります('X' は残りの試行回数)。 4. ステップ4では、コマンドはステータスワード '90 00' を返します。 |
| 事後条件 | 現在のパスワードは変更されていません。 |
8.3.6.6 Reset Retry Counter using an Incorrect PUK
8.3.6.6 誤ったPUKによる再試行カウンターのリセット
| Test Assertion | TA-08.03.06.06 |
|---|
| テストアサーション | TA-08.03.06.06 |
|---|
| Purpose | Verifies that the Derived PIV Application does not change the value of the Derived PIV Application Password when an incorrect PUK is provided. |
|---|---|
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.02 • DTR-06.03.07.03 • DTR-06.03.07.05 • DTR-06.03.07.06 • DTR-06.03.07.07 |
| Vendor Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Password and the PUK are recorded. • The Derived PIV Application Password’s retry counter is not 0 and the PUK’s retry counter greater than 1. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command contains an arbitrary, but correctly formatted, Derived PIV Application Password, padded with 'FF' (as necessary) to complete the total length of the value to 8 bytes 3. Send the RESET RETRY COUNTER with • P2, key reference value, is set to '80' • Data field of the command contains an incorrect PUK value concatenated without delimitation with a new valid password value padded with 'FF' to complete the total length of the value to 8 bytes. 4. Obtain number of remaining retries of the '80' key reference by sending the VERIFY command with • P2, key reference value, is set to '80' • P1 parameter is '00' and both Lc and the data field are absent 5. Send the RESET RETRY COUNTER with • P2, key reference value, is set to '80' • Data field of the command containing an incorrect PUK value concatenated without delimitation with a new password padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes. This operation is repeated until the number of resets allowed is exceeded 6. Send the RESET RETRY COUNTER with |
| 目的 | 誤ったPUKが提供された場合に、派生PIVアプリケーションが派生PIVアプリケーションのパスワードの値を変更しないことを検証します。 |
|---|---|
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.07.02 • DTR-06.03.07.03 • DTR-06.03.07.05 • DTR-06.03.07.06 • DTR-06.03.07.07 |
| ベンダー文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーションのパスワードとPUKが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではなく、PUKのリトライカウンタが1より大きい値です。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、任意だが形式が正しい派生PIVアプリケーションのパスワードを含め、必要に応じて 'FF' でパディングして値全体の長さを8バイトにする 3. 次の内容でRESET RETRY COUNTERを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、誤ったPUK値に、区切りなしで、'FF' でパディングして値全体の長さを8バイトにした有効な新しいパスワード値を連結したものを含めます。 4. 次の内容でVERIFYコマンドを送信して、'80' 鍵参照の残りの再試行回数を取得する • P2(鍵参照値)を '80' に設定する • P1パラメータを '00' とし、Lcとデータフィールドはいずれも存在しない 5. 次の内容でRESET RETRY COUNTERを送信する • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、誤ったPUK値に、区切りなしで、必要に応じて 'FF' でパディングして値全体の長さを8バイトにした新しいパスワードを連結したものを含めます。この操作を、許容されるリセット回数を超えるまで繰り返す 6. 次の内容でRESET RETRY COUNTERを送信する |
| • P2, key reference value, is set to '80' • Data field of the command contains the correct PUK value concatenated without delimitation with a new correctly-formatted password value padded to 8 bytes with 'FF' (if necessary) | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '63 CX' (X == number of retries left for the Derived PIV Application Password) 3. From Step 3, the command returns status word '63 CX' (where 'X' indicates the number of further allowed retries for the PUK) 4. From Step 4, the command returns status word '63 CX' (where 'X' is the number of retries remaining for the Derived PIV Application Password. Verify that 'X' from this step is the same as 'X' from Step 2. 5. From Step 5, the command returns status word '63 CX' (where 'X' indicates the number of further allowed retries for the PUK) and the PUK’s retry counter is decremented each time. The command returns status word '69 83' (reset operation blocked) when the command is invoked after the value of 'X' becomes 0. 6. From Step 6, the command returns status word '69 83' (reset operation blocked). |
| Postcondition(s) | The Reset Retry Counter command is blocked. |
| • P2(鍵参照値)を '80' に設定する • コマンドのデータフィールドには、正しいPUK値に、区切りなしで、必要に応じて 'FF' で8バイトにパディングした、形式の正しい新しいパスワード値を連結したものを含める | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '63 CX'(X == 派生PIVアプリケーションのパスワードの残りの試行回数)を返す 3. ステップ3では、コマンドはステータスワード '63 CX'('X' はPUKに許容される残りの再試行回数を示す)を返す 4. ステップ4では、コマンドはステータスワード '63 CX'('X' は派生PIVアプリケーションのパスワードの残りの試行回数)を返します。このステップの 'X' がステップ2の 'X' と同じであることを確認します。 5. ステップ5では、コマンドはステータスワード '63 CX'('X' はPUKに許容される残りの再試行回数を示す)を返し、PUKのリトライカウンタが毎回減ります。'X' の値が0になった後にコマンドが呼び出されると、コマンドはステータスワード '69 83'(リセット操作がブロックされている)を返します。 6. ステップ6では、コマンドはステータスワード '69 83'(リセット操作がブロックされている)を返します。 |
| 事後条件 | Reset Retry Counterコマンドがブロックされています。 |
8.3.7 PUT DATA Command
8.3.7 PUT DATAコマンド
8.3.7.1 Put Data for various Data Objects of the Derived PV Application
8.3.7.1 Derived PV Applicationの各種データオブジェクトへのPUT DATA
| Test Assertion | TA-08.03.07.01 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds appropriately to the PUT DATA command. |
| DTR(s) | • DTR-06.02.02.02 • DTR-06.02.02.03 • DTR-06.02.02.04 • DTR-06.02.02.05 • DTR-06.02.02.06 • DTR-06.02.02.07 • DTR-06.02.02.08 • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.08.01 |
| Vendor Documentation | None. |
| テストアサーション | TA-08.03.07.01 |
|---|---|
| 目的 | 派生PIVアプリケーションがPUT DATAコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.02 • DTR-06.02.02.03 • DTR-06.02.02.04 • DTR-06.02.02.05 • DTR-06.02.02.06 • DTR-06.02.02.07 • DTR-06.02.02.08 • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.08.01 |
| ベンダー文書 | なし。 |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Token Management Key is recorded. • The mutual authentication of the Derived PIV Application and the Test Toolkit Application has not been performed. • Data objects to be loaded are equal to the minimum container sizes specified for that object.14 |
|---|---|
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the PUT DATA command with • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • Data field in the command is to include the tag of the X.509 Certificate for PIV Authentication data object ('5FC105') • Data field in the command is to include data object that will be placed in the X.509 Certificate for PIV Authentication container 3. If the X.509 Certificate for Digital Signature is supported, repeat Step 2 with • Data field in the command is to include the tag of the X.509 Certificate for Digital Signature data object ('5FC10A') • Data field in the command is to include the data content that will be placed in the X.509 Certificate for Digital Signature container 4. If the X.509 Certificate for Key Management is supported, repeat Step 2 with • Data field in the command is to include the tag of the X.509 Certificate for Key Management data object ('5FC10B') • Data field in the command is to include the data object that will placed in the X.509 Certificate for Key Management container 5. If the token supports the Discovery Object, repeat Step 2 with • Data field in the command is to include the tag of the Discovery Object ('7E') • Data field in the command is to include the data object that will placed in the Discovery Object container 6. If the Security Object is supported, repeat Step 2 with • Data field in the command is to include the tag of the Security Object ('5FC106') |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション Token Management Keyが記録されています。 • 派生PIVアプリケーションと試験ツールキットアプリケーションの相互認証が実施されていません。 • ロードするデータオブジェクトが、そのオブジェクトに指定された最小コンテナサイズに等しい値です。14 |
|---|---|
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でPUT DATAコマンドを送信する • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は '00'、または 2. コマンドチェーンを使用する場合は '10'。(コマンドの最後のチェーンでは CLA を '00' に設定する) • コマンドのデータフィールドには、X.509 Certificate for PIV Authenticationデータオブジェクトのタグ('5FC105')を含める • コマンドのデータフィールドには、X.509 Certificate for PIV Authenticationコンテナに格納するデータオブジェクトを含める 3. X.509 Certificate for Digital Signatureがサポートされている場合、次の内容でステップ2を繰り返す • コマンドのデータフィールドには、X.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める • コマンドのデータフィールドには、X.509 Certificate for Digital Signatureコンテナに格納するデータの内容を含める 4. X.509 Certificate for Key Managementがサポートされている場合、次の内容でステップ2を繰り返す • コマンドのデータフィールドには、X.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める • コマンドのデータフィールドには、X.509 Certificate for Key Managementコンテナに格納するデータオブジェクトを含める 5. トークンがDiscovery Objectをサポートしている場合、次の内容でステップ2を繰り返す • コマンドのデータフィールドには、Discovery Objectのタグ('7E')を含める • コマンドのデータフィールドには、Discovery Objectコンテナに格納するデータオブジェクトを含める 6. Security Objectがサポートされている場合、次の内容でステップ2を繰り返す • コマンドのデータフィールドには、Security Objectのタグ('5FC106')を含める |
| • Data field in the command is to include the data object that will be placed the Security Object container 7. If the Key History Object is supported, repeat Step 2 with • Data field in the command is to include the tag of the Key History object ('5FC10C') • Data field in the command is to include the data object that will placed in the Key History Object container 8. If the Key History Object is supported, repeat Step 2 for each implemented retired X.509 Certificate for Key Management with • Data field in the command is to include the tag of one of the 20 retired X.509 Certificates for Key Management ('5FC10D'-'5FC120') • Data field in the command is to include the data object that will be placed the retired X.509 Certificate for Key Management container NOTE: The following tests are to be performed only if the Derived PIV Application supports the use of the '9B' key (Derived PIV Token Management Key) 9. Perform mutual authentication of Derived PIV Application and the Test Toolkit Application using Test Assertion TA-08.03.03.03 (GENERAL AUTHENTICATE). 10. Repeat Steps 2-8. Following the PUT DATA commands, perform the GET DATA commands (see TA-08.03.03.02.01) to verify that the same data that was personalized with the PUT DATA commands are returned by the GET DATA commands. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2 through Step 8, the commands return status word '69 82' (security status not satisfied). 3. From Step 9, the test results are consistent with those expected as part of TA-08.03.03.03: a. From Step 1 of TA-08.03.03.03, the command returns the application property template with the status word '90 00'. b. From Step 2 of TA-08.03.03.03, the command returns with the witness followed by status word '90 00'. c. From Step 3 of TA-08.03.03.03, the Derived PIV Application verifies the decrypted witness and then responds with encryption of the challenge sent by Test Toolkit Application followed by status word '90 00'. Decrypt the encrypted challenge and compare it to the one sent to the token. 4. From Step 10, all commands return status word '90 00', and input and output data match. |
| Postcondition(s) | N/A |
| • コマンドのデータフィールドには、Security Objectコンテナに格納するデータオブジェクトを含める 7. Key History Objectがサポートされている場合、次の内容でステップ2を繰り返す • コマンドのデータフィールドには、Key History Objectのタグ('5FC10C')を含める • コマンドのデータフィールドには、Key History Objectコンテナに格納するデータオブジェクトを含める 8. Key History Objectがサポートされている場合、実装されている廃止済みX • コマンドのデータフィールドには、20個の廃止済みX • コマンドのデータフィールドには、廃止済みX 9. テストアサーションTA-08 10. ステップ2~8を繰り返します。PUT DATAコマンドの後で、GET DATAコマンド(TA-08 | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2からステップ8では、コマンドはステータスワード '69 82'(セキュリティ状態が満たされていない)を返します。 3. ステップ9では、試験結果はTA-08 a. TA-08 b. TA-08 c. TA-08 4. ステップ10では、すべてのコマンドがステータスワード '90 00' を返し、入力データと出力データが一致します。 |
| 事後条件 | 該当なし |
8.3.8 GENERATE ASYMMETRIC KEY PAIR Command
8.3.8 GENERATE ASYMMETRIC KEY PAIRコマンド
8.3.8.1 Generate Asymmetric Key Pair for the Various Keys
8.3.8.1 各種鍵の非対称鍵ペアの生成
| Test Assertion | TA-08.03.08.01 |
|---|---|
| Purpose | Verifies that the Derived PIV Application responds appropriately to the GENERATE ASYMMETRIC KEY PAIR command. |
| DTR(s) | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.04.05 • DTR-06.03.09.01 • DTR-06.03.09.02 |
| Vendor Documentation | The vendor to provide documentation specifying the cryptographic mechanism identifiers (from Table 5 of [SP800-73], Part 1) that have been implemented. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • The Derived PIV Application Token Management Key is recorded. • The mutual authentication of the Derived PIV Application and the Test Toolkit Application has not been performed. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GENERATE ASYMMETRIC KEY PAIR command with • P2 is set to value '9A' • Data field in the command is to include either '07' or '11' as the cryptographic mechanism identifier 3. If the X.509 Certificate for Digital Signature is supported, send the GENERATE ASYMMETRIC KEY PAIR command with • P2 is set to value '9C' • Data field in the command is to include either '07', '11', '14' as the cryptographic mechanism identifier 4. If the X.509 Certificate for Key Management and the on-token generation of the key management key is supported, send the GENERATE ASYMMETRIC KEY PAIR command with • P2 is set to value '9D' • Data field in the command is to include either '07', '11', '14' as the cryptographic mechanism identifier |
| テストアサーション | TA-08.03.08.01 |
|---|---|
| 目的 | 派生PIVアプリケーションがGENERATE ASYMMETRIC KEY PAIRコマンドに適切に応答することを検証します。 |
| DTR | • DTR-06.02.02.09 • DTR-06.03.01.01 • DTR-06.03.04.05 • DTR-06.03.09.01 • DTR-06.03.09.02 |
| ベンダー文書 | ベンダーは、実装されている暗号メカニズム識別子([SP800-73] 第1部の表5にあるもの)を規定した文書を提供します。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション Token Management Keyが記録されています。 • 派生PIVアプリケーションと試験ツールキットアプリケーションの相互認証が実施されていません。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGENERATE ASYMMETRIC KEY PAIRコマンドを送信する • P2を値 '9A' に設定する • コマンドのデータフィールドには、暗号メカニズム識別子として '07' または '11' のいずれかを含める 3. X.509 Certificate for Digital Signatureがサポートされている場合、次の内容でGENERATE ASYMMETRIC KEY PAIRコマンドを送信する • P2を値 '9C' に設定する • コマンドのデータフィールドには、暗号メカニズム識別子として '07'、'11'、'14' のいずれかを含める 4. X.509 Certificate for Key Managementと鍵管理鍵のトークン上での生成がサポートされている場合、次の内容でGENERATE ASYMMETRIC KEY PAIRコマンドを送信する • P2を値 '9D' に設定する • コマンドのデータフィールドには、暗号メカニズム識別子として '07'、'11'、'14' のいずれかを含める |
| NOTE: The following tests are to be performed only if the Derived PIV Application supports the use of the '9B' key (Derived PIV Token Management Key) 5. Perform mutual authentication of Derived PIV Application and the Test Toolkit Application using Test Assertion TA-08.03.03.03 (GENERAL AUTHENTICATE) 6. Repeat Steps 2, 3, and 4. 7. Repeat Step 2 with the cryptographic mechanism identifier value in the data field set to a value that is not supported by the Derived PIV Application. 8. Repeat Step 2 with P2 set to a key reference value that is not supported by the Derived PIV Application. 9. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 10. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07' or '11' • P2, key reference, is set to '9A' • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response 11. If the X.509 Certificate for Digital Signature is supported, send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07', '11' or '14' • P2, key reference, is set to '9C' • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response 12. If the X.509 Certificate for Key Management and the on-token generation of the key management key is supported, send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or 2. '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07', '11' or '14' • P2, key reference, is set to '9D' indicating the key management key |
| 注:以下の試験は、派生PIVアプリケーションが「9B」鍵(Derived PIV Token Management Key)の使用をサポートしている場合にのみ実施する 5. テストアサーションTA-08 6. ステップ2、3、4を繰り返します。 7. データフィールドの暗号メカニズム識別子の値を、派生PIVアプリケーションがサポートしていない値に設定して、ステップ2を繰り返します。 8. P2を派生PIVアプリケーションがサポートしていない鍵参照値に設定して、ステップ2を繰り返します。 9. 次の内容でVERIFYコマンドを送信する • P2(鍵参照値)を「80」に設定する • コマンドのデータフィールドに正しい派生PIVアプリケーションのパスワードを含め、必要に応じて「FF」でパディングして、値全体の長さを8バイトにする 10. GENERAL AUTHENTICATEコマンドを送信する • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は「00」、または 2. コマンドチェーンを使用する場合は「10」に設定します。(コマンドの最後のチェーンではCLAを「00」に設定する) • P1(アルゴリズム参照)を「07」または「11」に設定する • P2(鍵参照)を「9A」に設定する • コマンドのデータフィールドには、チャレンジを指定する「81」、それに続く無作為に生成したチャレンジ、およびレスポンスを要求するための「82 00」を含める 11. X.509 Certificate for Digital Signatureがサポートされている場合、GENERAL AUTHENTICATEコマンドを送信する • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は「00」、または 2. コマンドチェーンを使用する場合は「10」に設定します。(コマンドの最後のチェーンではCLAを「00」に設定する) • P1(アルゴリズム参照)を「07」、「11」または「14」に設定する • P2(鍵参照)を「9C」に設定する • コマンドのデータフィールドには、チャレンジを指定する「81」、それに続く無作為に生成したチャレンジ、およびレスポンスを要求するための「82 00」を含める 12. X.509 Certificate for Key Managementと鍵管理鍵のトークン上での生成がサポートされている場合、GENERAL AUTHENTICATEコマンドを送信する • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は「00」、または 2. コマンドチェーンを使用する場合は「10」に設定します。(コマンドの最後のチェーンではCLAを「00」に設定する) • P1(アルゴリズム参照)を「07」、「11」または「14」に設定する • P2(鍵参照)を、鍵管理鍵を示す「9D」に設定する |
| • Data field in the command is to include one of the following: 1. If P1 = '07', the template '81' contains a key encrypted using the key management public key returned in Step 6. 2. If P1 = '11' or '14', the template '85' contain the other party’s public key.15 | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, 3, and 4, the command returns status word '69 82' (security status not satisfied). 3. From Step 5, the test results are consistent with those expected as part of TA-08.03.03.03: a. From Step 1 of TA-08.03.03.03, the command returns the application property template with the status word '90 00'. b. From Step 2 of TA-08.03.03.03, the command returns with the witness followed by status word '90 00'. c. From Step 3 of TA-08.03.03.03, the Derived PIV Application verifies the decrypted witness and then responds with encryption of the challenge sent by Test Toolkit Application followed by status word '90 00'. Decrypt the encrypted challenge and compare it to the one sent to the token. 4. From Step 6, the commands return status word '90 00' and the data field contains the '7F49' template with the generated public key, which consists of either a modulus and public exponent (RSA) or a point (elliptic curve cryptography). 5. From Step 7, the command returns status word '6A 80' (incorrect parameter command data field). 6. From Step 8, the command returns status word '6A 86' (incorrect parameter P2). 7. From Step 9, the command returns status word '90 00'. 8. From Step 10, the command returns the signed challenge with status word '90 00'. Verify the signed challenge using the Derived PIV Authentication public key that was returned in Step 6. 9. From Step 11, the command returns the signed challenge with status word '90 00'. Verify the signed challenge using the digital signature public key that was returned in Step 6. 10. From Step 12, for algorithm reference '07' as P1 value, the command returns the transported key with status word '90 00'. Compare the test toolkit application’s copy of the plaintext key to the one received in the response from the token. For algorithm reference '11' or '14' as P1 value, the command returns the shared secret Z 16 with |
| • コマンドのデータフィールドには、次のいずれかを含めます。 1. P1 = '07' の場合、テンプレート '81' には、ステップ6で返された鍵管理用公開鍵で暗号化された鍵が含まれます。 2. P1 = '11' または '14' の場合、テンプレート '85' には相手側の公開鍵が含まれます。15 | |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2、3、4では、コマンドはステータスワード '69 82'(セキュリティ状態が満たされていない)を返します。 3. ステップ5では、試験結果はTA-08 a. TA-08 b. TA-08 c. TA-08 4. ステップ6では、コマンドはステータスワード '90 00' を返し、データフィールドには、生成された公開鍵を含む '7F49' テンプレートが入ります。公開鍵は、モジュラスと公開指数(RSA)、または点(楕円曲線暗号)のいずれかで構成されます。 5. ステップ7では、コマンドはステータスワード '6A 80'(コマンドデータフィールドのパラメータが不正)を返します。 6. ステップ8では、コマンドはステータスワード '6A 86'(P2のパラメータが不正)を返します。 7. ステップ9では、コマンドはステータスワード '90 00' を返します。 8. ステップ10では、コマンドはステータスワード '90 00' とともに署名済みチャレンジを返します。ステップ6で返されたDerived PIV Authentication公開鍵を用いて、署名済みチャレンジを検証します。 9. ステップ11では、コマンドはステータスワード '90 00' とともに署名済みチャレンジを返します。ステップ6で返されたデジタル署名用公開鍵を用いて、署名済みチャレンジを検証します。 10. ステップ12では、P1の値としてアルゴリズム参照 '07' を用いた場合、コマンドはステータスワード '90 00' とともにトランスポートされた鍵を返します。試験ツールキットアプリケーションが保持する平文鍵のコピーと、トークンからのレスポンスで受け取った鍵を比較します。P1の値としてアルゴリズム参照 '11' または '14' を用いた場合、コマンドは共有シークレットZ 16と |
| status word '90 00'. Compare the shared secret computed by the token with the shared secret computed off token (using the key management public key that was returned in Step 6). | |
| Postcondition(s) | The token has newly generated private key(s). |
| ステータスワード '90 00'。トークンが計算した共有シークレットと、トークン外で(ステップ6で返された鍵管理用公開鍵を用いて)計算した共有シークレットを比較します。 | |
| 事後条件 | トークンには新たに生成された1つ以上の秘密鍵があります。 |
9. Test Assertions for the Derived PIV Application Data Model
9. 派生PIVアプリケーションのデータモデルに関する試験アサーション
This section lists the test assertions used to determine conformity to the derived test requirements (DTR) listed in Section 7. The Implementation Under Test (IUT), the Derived PIV Data Objects loaded on a Derived PIV Application by an issuer, must meet the stated objective(s) of the assertion by way of a test or submission of artifacts in order to be deemed conformant to the associated DTR(s).
この節では、7節に記載された派生試験要件(DTR)への適合性を判定するための試験アサーションを列挙します。実装対象(IUT)、すなわち発行者が派生PIVアプリケーションにロードした派生PIVデータオブジェクトは、関連するDTRに適合すると認められるために、試験または成果物の提出を通じて、アサーションに記載された目的を満たさなければなりません。
9.1 BER-TLV Conformance
9.1 BER-TLV適合性
The following assumptions apply to the test assertions within this section.
この節の試験アサーションには、次の前提を適用します。
| 1 | When the length of the value field is between 0 and 127 bytes, the length field should consist of a single byte where bit 8 is set to 0 and bits 7 to 1 encode the number of bytes in the value field. When the length of the value field is greater than 127 bytes, the length field consists of two or more bytes.17 The first byte is '81', '82', '83' or '84' where the low order nibble of each of these possible first-byte values (1, 2, 3, or 4 respectively) encodes the number of subsequent bytes in the length field. These subsequent bytes are taken together in order to be a big-endian integer encoding the number of bytes in the value field. Table 1 shows the encoding of the length field. |
| 2 | Except for the Discovery Object tag, each BER-TLV tag is encoded as three bytes. |
| 3 | Each data object returned is appended with a 2 byte status word. |
| 4 | All variable length value fields can have zero lengths, which will result in a tag length field being immediately followed by the next tag, if applicable. |
| 5 | The final byte of the command string can be set to 0x00 to retrieve an entire data object regardless of the size of that object. |
| 1 | 値フィールドの長さが0~127バイトの場合、長さフィールドは1バイトで構成され、ビット8を0に設定し、ビット7~1で値フィールドのバイト数を符号化します。 値フィールドの長さが127バイトを超える場合、長さフィールドは2バイト以上で構成されます。17 最初のバイトは '81'、'82'、'83' または '84' のいずれかであり、これらの最初のバイトの値の下位ニブル(それぞれ1、2、3、4)は、長さフィールドの後続バイト数を符号化します。これらの後続バイトをまとめて、値フィールドのバイト数を符号化したビッグエンディアンの整数として扱います。表1は長さフィールドの符号化を示します。 |
| 2 | Discovery Objectのタグを除き、各BER-TLVタグは3バイトで符号化されます。 |
| 3 | 返される各データオブジェクトの末尾には、2バイトのステータスワードが付加されます。 |
| 4 | 可変長の値フィールドはすべて長さ0にできます。その場合、該当するなら、タグの長さフィールドの直後に次のタグが続きます。 |
| 5 | コマンド文字列の最後のバイトを0x00に設定すると、データオブジェクトのサイズにかかわらず、データオブジェクト全体を取得できます。 |
| Number of bytes in the length field | First byte | Subsequent bytes | Length of the value field |
|---|---|---|---|
| 1 byte | '00' to '7F' | None | 0 to 127 |
| 2 byte | '81' | '00' to 'FF' | 0 to 255 |
| 3 byte | '82' | '0000' to 'FFFF' | 0 to 65535 |
| 4 byte | '83' | '000000' to 'FFFFFF' | 0 to 16777215 |
| 5 byte | '84' | '00000000' to 'FFFFFFFF' | 0 to 4294967295 |
| 長さフィールドのバイト数 | 最初のバイト | 後続バイト | 値フィールドの長さ |
|---|---|---|---|
| 1バイト | '00'~'7F' | なし | 0~127 |
| 2バイト | '81' | '00'~'FF' | 0~255 |
| 3バイト | '82' | '0000'~'FFFF' | 0~65535 |
| 4バイト | '83' | '000000'~'FFFFFF' | 0~16777215 |
| 5バイト | '84' | '00000000'~'FFFFFFFF' | 0~4294967295 |
9.1.1 X.509 Certificate for Derived PIV Authentication
9.1.1 派生PIV認証用X.509証明書
9.1.1.1 BER-TLV of X.509 Certificate for Derived PIV Authentication
9.1.1.1 派生PIV認証用X.509証明書のBER-TLV
| Test Assertion | TA-09.01.01.01 |
|---|---|
| Purpose | Verifies that the X.509 Certificate for Derived PIV Authentication conforms to the Derived PIV data model requirements. |
| DTR(s) | • DTR-07.01.02.01 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Read and parse the byte array in accordance with BER-TLV format. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00' along with the X.509 Certificate for Derived PIV Authentication data object. 3. From Step 3, all mandatory tags for the X.509 Certificate for Derived PIV Authentication data object are present in the order indicated in Table 10 of [SP800-73], Part 1. |
| テストアサーション | TA-09.01.01.01 |
|---|---|
| 目的 | X.509 Certificate for Derived PIV Authenticationが、Derived PIVデータモデルの要件に適合していることを検証します。 |
| DTR | • DTR-07.01.02.01 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、X.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. バイト配列をBER-TLV形式に従って読み取り、解析します。 |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはステータスワード '90 00' とともにX.509 Certificate for Derived PIV Authenticationデータオブジェクトを返します。 3. ステップ3では、X.509 Certificate for Derived PIV Authenticationデータオブジェクトの必須タグがすべて、[SP800-73] 第1部の表10に示された順序で存在します。 |
9.1.2 X.509 Certificate for Digital Signature
9.1.2 電子署名用X.509証明書
9.1.2.1 BER-TLV of X.509 Certificate for Digital Signature
9.1.2.1 デジタル署名用X.509証明書のBER-TLV
| Test Assertion | TA-09.01.02.01 |
|---|---|
| Purpose | Verifies that the X.509 Certificate for Digital Signature (if present) conforms to the Derived PIV data model requirements. |
| DTR(s) | • DTR-07.01.01.01 • DTR-07.01.03.01 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. |
| テストアサーション | TA-09.01.02.01 |
|---|---|
| 目的 | X.509 Certificate for Digital Signature(存在する場合)が、Derived PIVデータモデルの要件に適合していることを検証します。 |
| DTR | • DTR-07.01.01.01 • DTR-07.01.03.01 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object 3. If the X.509 Certificate for Digital Signature data object was retrieved in Step 2, read and parse the byte array in accordance with BER-TLV format. |
|---|---|
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns one of the following: • An X.509 Certificate for Digital Signature data object followed by status word '90 00'; • A zero-length data object followed by status word '90 00' – which indicates that a container for the X.509 certificate exists, but it has not been personalized; or • Status word '6A 82' (data object not found) – which indicates the container for the X.509 certificate does not exist 3. From Step 3, all mandatory tags for the X.509 Certificate for Digital Signature data object are present in the order indicated in Table 15 of [SP800-73], Part 1. |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、X.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める 3. ステップ2でX.509 Certificate for Digital Signatureデータオブジェクトが取得された場合、バイト配列をBER-TLV形式に従って読み取り、解析します。 |
|---|---|
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドは次のいずれかを返します。 • X.509 Certificate for Digital Signatureデータオブジェクトに続けてステータスワード '90 00'; • 長さ0のデータオブジェクトに続けてステータスワード '90 00'。これは、X • ステータスワード '6A 82'(データオブジェクトが見つかりません)。これは、X 3. ステップ3では、X.509 Certificate for Digital Signatureデータオブジェクトの必須タグがすべて、[SP800-73] 第1部の表15に示された順序で存在します。 |
9.1.3 X.509 Certificate for Key Management
9.1.3 鍵管理用X.509証明書
9.1.3.1 BER-TLV of X.509 Certificate for Key Management
9.1.3.1 鍵管理用X.509証明書のBER-TLV
| Test Assertion | TA-09.01.03.01 |
|---|---|
| Purpose | Verifies that the X.509 Certificate for Key Management (if present) conforms to the Derived PIV data model requirements. |
| DTR(s) | • DTR-07.01.01.01 • DTR-07.01.04.01 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 3. If the X.509 Certificate for Key Management data object was retrieved in Step 2, read and parse the byte array in accordance with BER-TLV format. |
| テストアサーション | TA-09.01.03.01 |
|---|---|
| 目的 | X.509 Certificate for Key Management(存在する場合)が、Derived PIVデータモデルの要件に適合していることを検証します。 |
| DTR | • DTR-07.01.01.01 • DTR-07.01.04.01 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、X.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 3. ステップ2でX.509 Certificate for Key Managementデータオブジェクトが取得された場合、バイト配列をBER-TLV形式に従って読み取り、解析します。 |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns one of the following: • An X.509 Certificate for Key Management followed by status word '90 00'; • A zero-length data object followed by status word '90 00' – which indicates that a container for the X.509 certificate exists, but it has not been personalized; or • Status word '6A 82' (data object not found) – which indicates the container for the X.509 certificate does not exist 3. From Step 3, all mandatory tags for the X.509 Certificate for Key Management are present in the order indicated in Table 16 of [SP800-73], Part 1. |
|---|
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドは次のいずれかを返します。 • X.509 Certificate for Key Managementに続けてステータスワード '90 00'; • 長さ0のデータオブジェクトに続けてステータスワード '90 00'。これは、X • ステータスワード '6A 82'(データオブジェクトが見つかりません)。これは、X 3. ステップ3では、X.509 Certificate for Key Managementの必須タグがすべて、[SP800-73] 第1部の表16に示された順序で存在します。 |
|---|
9.1.4 Discovery Object
9.1.4 Discovery Object
9.1.4.1 BER-TLV of Discovery Object and Presence of Security Object
9.1.4.1 Discovery ObjectのBER-TLVおよびSecurity Objectの存在
| Test Assertion | TA-09.01.04.01 |
|---|---|
| Purpose | Verifies that the Discovery Object (if present) conforms to the Derived PIV data model requirements. |
| DTR(s) | • DTR-07.01.01.01 • DTR-07.01.05.01 • DTR-07.01.05.02 • DTR-07.01.08.02 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. |
| Test Scenario | 1. Send the SELECT token command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('7E') of the Discovery Object. 3. If the Discovery Object was retrieved in Step 2, read and parse the byte array in accordance with BER-TLV format. 4. If the Discovery Object was retrieved in Step 2, verify that the Security Object is present within the Derived PIV Application by sending a GET DATA command to read the data object. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns one of the following: |
| テストアサーション | TA-09.01.04.01 |
|---|---|
| 目的 | Discovery Object(存在する場合)が、Derived PIVデータモデルの要件に適合していることを検証します。 |
| DTR | • DTR-07.01.01.01 • DTR-07.01.05.01 • DTR-07.01.05.02 • DTR-07.01.08.02 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 |
| テストシナリオ | 1. 次の内容でSELECTトークンコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、Discovery Objectのタグ('7E')を含めます。 3. ステップ2でDiscovery Objectが取得された場合、バイト配列をBER-TLV形式に従って読み取り、解析します。 4. ステップ2でDiscovery Objectが取得された場合、データオブジェクトを読み取るGET DATAコマンドを送信して、派生PIVアプリケーション内にSecurity Objectが存在することを検証します。 |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドは次のいずれかを返します。 |
| • A Discovery Object followed by status word '90 00'; • A zero-length data object followed by status word '90 00' – which indicates that a container for the Discovery Object exists, but it has not been personalized; or • Status word '6A 82' (data object not found) – which indicates the container for the Discovery Object does not exist) 3. From Step 3, all mandatory tags for the Discovery Object are present and are in the order indicated in Table 18 of [SP800-73], Part 1. The first byte of the PIN Usage Policy is set to 0x40 and the second byte is set to 0x00. In addition, the PIV Card Application AID in tag 0x4F is set to 'A0 00 00 03 08 00 00 20 00 01 00' 4. From Step 4, the command returns status word '90 00' along with the Security Object. |
| • Discovery Objectに続けてステータスワード '90 00'; • 長さ0のデータオブジェクトに続けてステータスワード '90 00'。これは、Discovery Objectのコンテナは存在するが個人化されていないことを示します。または • ステータスワード '6A 82'(データオブジェクトが見つかりません)。これは、Discovery Objectのコンテナが存在しないことを示す) 3. ステップ3では、Discovery Objectの必須タグがすべて存在し、[SP800-73] 第1部の表18に示された順序になっています。PIN Usage Policyの1バイト目は0x40、2バイト目は0x00に設定されています。さらに、タグ0x4FのPIV Card Application AIDは 'A0 00 00 03 08 00 00 20 00 01 00' に設定されている 4. ステップ4では、コマンドはステータスワード '90 00' とともにSecurity Objectを返します。 |
9.1.5 Key History Object
9.1.5 Key History Object
9.1.5.1 BER-TLV of Key History Object and Presence of Security Object
9.1.5.1 Key History ObjectのBER-TLVおよびSecurity Objectの存在
| Test Assertion | TA-09.01.05.01 |
|---|---|
| Purpose | Verifies that the Key History Object (if present) conforms to the Derived PIV data model requirements. |
| DTR(s) | • DTR-07.01.01.01 • DTR-07.01.06.01 • DTR-07.01.08.02 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10C') of the Key History Object. 3. If the Key History Object was retrieved in Step 2, read and parse the byte array in accordance with BER-TLV format. 4. If the Key History Object was retrieved in Step 2, verify that the Security Object is present within the Derived PIV Application by sending a GET DATA command to read this data object. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns one of the following: |
| テストアサーション | TA-09.01.05.01 |
|---|---|
| 目的 | Key History Object(存在する場合)が、Derived PIVデータモデルの要件に適合していることを検証します。 |
| DTR | • DTR-07.01.01.01 • DTR-07.01.06.01 • DTR-07.01.08.02 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、Key History Objectのタグ('5FC10C')を含めます。 3. ステップ2でKey History Objectが取得された場合、バイト配列をBER-TLV形式に従って読み取り、解析します。 4. ステップ2でKey History Objectが取得された場合、このデータオブジェクトを読み取るGET DATAコマンドを送信して、派生PIVアプリケーション内にSecurity Objectが存在することを検証します。 |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドは次のいずれかを返します。 |
| • A Key History Object followed by status word '90 00'; • A zero-length data object followed by status word '90 00' - which indicates that a container for the Key History Object exists, but it has not been personalized; or • Status word '6A 82' (data object not found) - which indicates the container for the Key History Object does not exist 3. From Step 3, all mandatory tags for the Key History Object are present in the order indicated in Table 19 of [SP800-73], Part 1. 4. From Step 4, the command returns status word '90 00' along with the Security Object. |
| • Key History Objectに続けてステータスワード '90 00'; • 長さ0のデータオブジェクトに続けてステータスワード '90 00'。これは、Key History Objectのコンテナは存在するが個人化されていないことを示します。または • ステータスワード '6A 82'(データオブジェクトが見つかりません)。これは、Key History Objectのコンテナが存在しないことを示す 3. ステップ3では、Key History Objectの必須タグがすべて、[SP800-73] 第1部の表19に示された順序で存在します。 4. ステップ4では、コマンドはステータスワード '90 00' とともにSecurity Objectを返します。 |
9.1.6 Retired X.509 Certificates for Key Management
9.1.6 退役済み鍵管理用X.509証明書
9.1.6.1 BER-TLV of Retired X.509 Certificates for Key Management
9.1.6.1 退役済み鍵管理用X.509証明書のBER-TLV
| Test Assertion | TA-09.01.06.01 |
|---|---|
| Purpose | Verifies that the Retired X.509 Certificates for Key Management (if present) conform to the Derived PIV data model requirements. |
| DTR(s) | • DTR-07.01.01.01 • DTR-07.01.07.01 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send 20 GET DATA commands with • Data field of each command containing the tag ('5FC10D' to '5FC120') for one of the 20 Retired X.509 Certificates for Key Management 3. For each Retired X.509 Certificate for Key Management retrieved in Step 2, read and parse the byte array for each in accordance with BER-TLV format. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, each command returns one of the following: • A Retired X.509 Certificate for Key Management followed by status word '90 00'; • A zero-length data object followed by status word '90 00' – which indicates that a container for the retired X.509 certificate exists, but it has not been personalized; or • Status word '6A 82' (data object not found) – which |
| テストアサーション | TA-09.01.06.01 |
|---|---|
| 目的 | 廃止済みX.509 Certificates for Key Management(存在する場合)が、Derived PIVデータモデルの要件に適合していることを検証します。 |
| DTR | • DTR-07.01.01.01 • DTR-07.01.07.01 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを20回送信する • 各コマンドのデータフィールドには、20個の廃止済みX 3. ステップ2で取得した廃止済みX.509 Certificate for Key Managementのそれぞれについて、バイト配列をBER-TLV形式に従って読み取り、解析します。 |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、各コマンドは次のいずれかを返します。 • 廃止済みX.509 Certificate for Key Managementに続けてステータスワード '90 00'; • 長さ0のデータオブジェクトに続けてステータスワード '90 00'。これは、廃止済みX • ステータスワード '6A 82'(データオブジェクトが見つかりません)。これは、 |
| indicates the container for the retired X.509 certificate does not exist) 3. From Step 3, all mandatory tags in each of the available Retired X.509 Certificates for Key Management are present in the order indicated in Table 20 to Table 39 of [SP800-73], Part 1. |
| 廃止済みX 3. ステップ3では、利用可能な廃止済みX.509 Certificate for Key Managementのそれぞれについて、必須タグがすべて、[SP800-73] 第1部の表20から表39に示された順序で存在します。 |
9.1.7 Security Object
9.1.7 Security Object
9.1.7.1 BER-TLV of Security Object and Presence of Unsigned Data Objects
9.1.7.1 Security ObjectのBER-TLVおよび署名されていないデータオブジェクトの存在
| Test Assertion | TA-09.01.07.01 |
|---|---|
| Purpose | Verifies that the Security Object conforms to the Derived PIV data model requirements and unsigned data objects are included within the Security Object on the Derived PIV Application. |
| DTR(s) | • DTR-07.01.01.01 • DTR-07.01.08.01 • DTR-07.01.08.03 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') for the Security Object 3. Read and parse the byte array in accordance with BER-TLV format. 4. Parse the tag 0xBA to extract the Data Groups to Container ID mapping instances. 5. Verify that all unsigned data objects (the Discovery and/or Key History object) are included in the Security Object. 6. Verify that the unsigned data objects exist within the Derived PIV Application by reading the data object from each container. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the Security Object followed by status word '90 00'. 3. From Step 3, all mandatory tags for the Security Object are present in the order indicated in Table 12 of [SP800-73], Part 1. |
| テストアサーション | TA-09.01.07.01 |
|---|---|
| 目的 | Security ObjectがDerived PIVデータモデルの要件に適合しており、署名されていないデータオブジェクトが派生PIVアプリケーション上のSecurity Objectに含まれていることを検証します。 |
| DTR | • DTR-07.01.01.01 • DTR-07.01.08.01 • DTR-07.01.08.03 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信する • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信する • コマンドのデータフィールドには、Security Objectのタグ('5FC106')を含める 3. バイト配列をBER-TLV形式に従って読み取り、解析します。 4. タグ0xBAを解析して、Data GroupsからContainer IDへのマッピングのインスタンスを抽出します。 5. 署名されていないすべてのデータオブジェクト(Discovery Objectまたは Key History Object、あるいはその両方)がSecurity Objectに含まれていることを検証します。 6. 各コンテナからデータオブジェクトを読み取って、署名されていないデータオブジェクトが派生PIVアプリケーション内に存在することを検証します。 |
| 期待結果 | 1. ステップ1では、コマンドはステータスワード '90 00' とともにapplication property templateを返します。 2. ステップ2では、コマンドはSecurity Objectに続けてステータスワード '90 00' を返します。 3. ステップ3では、Security Objectの必須タグがすべて、[SP800-73] 第1部の表12に示された順序で存在します。 |
| 4. From Step 5, all unsigned data objects are included in the Security Object. 5. From Step 6, all data objects found in the mapping are actually present on the Derived PIV Application as evidenced by the GET DATA commands returning the data objects along with status word '90 00'. |
| 4. ステップ5では、署名されていないすべてのデータオブジェクトがSecurity Objectに含まれています。 5. ステップ6では、マッピングで見つかったすべてのデータオブジェクトが、データオブジェクトをステータスワード '90 00' とともに返すGET DATAコマンドによって、派生PIVアプリケーション上に実際に存在することが確認されます。 |
9.2 Signed Data Object Conformance
9.2 署名付きデータオブジェクトの適合性
9.2.1 Security Object
9.2.1 Security Object
9.2.1.1 Data Object Hash Integrity Check
9.2.1.1 データオブジェクトのハッシュ完全性検査
| Test Assertion | TA-09.02.01.01 |
|---|---|
| Purpose | Verifies the integrity of the hashes of the data objects referenced in the Security Object (if present). |
| DTR(s) | • DTR-07.02.01.01 • DTR-07.01.05.02 • DTR-07.01.08.02 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Identify the various data elements that are part of the security object by parsing the Mapping of Data Group (DG) to ContainerID (i.e. TAG 0xBA). 4. Extract the ldsSecurityObject from the eContent field of the Security Object Asymmetric Signature (i.e. TAG 0xBB). 5. Get all the data objects that are present in the mapping obtained from Step 3 (i.e., the Discovery Object and/or the Key History Object). 6. Compute the hash for each data object and verify that it matches the hash value present in the ldsSecurityObject. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the Security Object and the status word '90 00'. |
| テストアサーション | TA-09.02.01.01 |
|---|---|
| 目的 | Security Objectが参照するデータオブジェクトのハッシュの完全性を検証します(存在する場合)。 |
| DTR | • DTR-07.02.01.01 • DTR-07.01.05.02 • DTR-07.01.08.02 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Mapping of Data Group (DG) to ContainerID(すなわちTAG 0xBA)を解析して、Security Objectの一部であるさまざまなデータ要素を特定します。 4. Security Object Asymmetric Signature(すなわちTAG 0xBB)のeContentフィールドからldsSecurityObjectを抽出します。 5. 手順3で得たマッピングに存在するすべてのデータオブジェクト(すなわち、Discovery Objectおよび/またはKey History Object)を取得します。 6. 各データオブジェクトのハッシュを計算し、それがldsSecurityObjectに存在するハッシュ値と一致することを検証します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドはSecurity Objectとステータスワード'90 00'を返します。 |
| 3. From Step 5, the command returns the Discovery Object and/or Key History Object. 4. From Step 6, the actual hashes of the data objects extracted in Step 5 are identical to their corresponding hash values present in the Security Object. |
| 3. 手順5より、コマンドはDiscovery Objectおよび/またはKey History Objectを返します。 4. 手順6より、手順5で抽出したデータオブジェクトの実際のハッシュは、Security Objectに存在する対応するハッシュ値と同一です。 |
9.2.1.2 Presence of CMS SignedData
9.2.1.2 CMS SignedDataの存在
| Test Assertion | TA-09.02.01.02 |
|---|---|
| Purpose | Verifies that the Security Object contains an asymmetric digital signature, implemented as a SignedData type in accordance with [RFC5652]. |
| DTR(s) | • DTR-07.02.01.02 • DTR-07.02.01.03 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Parse the obtained Security Object and extract the contents from the asymmetric digital signature field (i.e., tag 0xBB) 4. Process the contents of the digital signature |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 4, the content of the digital signature is an object that is a SignedData type which is in accordance with [RFC5652]. |
| テストアサーション | TA-09.02.01.02 |
|---|---|
| 目的 | Security Objectが、[RFC5652]に従ってSignedData型として実装された非対称デジタル署名を含むことを検証します。 |
| DTR | • DTR-07.02.01.02 • DTR-07.02.01.03 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. 取得したSecurity Objectを解析し、非対称デジタル署名フィールド(すなわちタグ0xBB)から内容を抽出する 4. デジタル署名の内容を処理する |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4より、デジタル署名の内容は、[RFC5652]に従ったSignedData型のオブジェクトです。 |
9.2.1.3 SignedData Version
9.2.1.3 SignedDataのバージョン
| Test Assertion | TA-09.02.01.03 |
|---|---|
| Purpose | Verifies that the version of the SignedData content type is v3. |
| DTR(s) | • DTR-07.02.01.04 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. |
| テストアサーション | TA-09.02.01.03 |
|---|---|
| 目的 | SignedDataコンテンツタイプのバージョンがv3であることを検証します。 |
| DTR | • DTR-07.02.01.04 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 |
| • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. | |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract the version field contents from the asymmetric signature of the Security Object (i.e., tag 0xBB) |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the value of the version field of the SignedData is v3. |
| • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 | |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectの非対称署名(すなわちタグ0xBB)からversionフィールドの内容を抽出する |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、SignedDataのversionフィールドの値はv3です。 |
9.2.1.4 SignedData digestAlgorithms
9.2.1.4 SignedDataのdigestAlgorithms
| Test Assertion | TA-09.02.01.04 |
|---|---|
| Purpose | Verifies that the digestAlgorithms field of the SignedData content type is in accordance with Table 3-2 of [SP800-78]. |
| DTR(s) | • DTR-07.02.01.05 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract the digestAlgorithms and certificates fields contents from the Security Object. 4. From the certificate obtained, extract the subjectPublicKeyInfo->subjectPublicKey and determine the type and size of the signer’s public key. 5. Determine the digest algorithm specified in the digestAlgorithms field obtained in Step 3 using Table 3-6 of [SP800-78]. 6. Match the digest algorithm obtained from Step 5 to an entry of Table 3-2 of [SP800-78] based on the public key algorithm and size (Step 4). |
| テストアサーション | TA-09.02.01.04 |
|---|---|
| 目的 | SignedDataコンテンツタイプのdigestAlgorithmsフィールドが、[SP800-78]のTable 3-2に従っていることを検証します。 |
| DTR | • DTR-07.02.01.05 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security ObjectからdigestAlgorithmsおよびcertificatesフィールドの内容を抽出します。 4. 取得した証明書からsubjectPublicKeyInfo->subjectPublicKeyを抽出し、署名者の公開鍵の種類とサイズを判定します。 5. [SP800-78]のTable 3-6を用いて、手順3で得たdigestAlgorithmsフィールドに指定されたダイジェストアルゴリズムを判定します。 6. 公開鍵アルゴリズムとサイズ(手順4)に基づいて、手順5で得たダイジェストアルゴリズムを[SP800-78]のTable 3-2のエントリと照合します。 |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 6, the digestAlgorithms field value of the SignedData is in accordance with Table 3-2 of [SP800-78]. |
|---|
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順6より、SignedDataのdigestAlgorithmsフィールドの値は[SP800-78]のTable 3-2に従っています。 |
|---|
9.2.1.5 encapContentInfo Contents
9.2.1.5 encapContentInfoの内容
| Test Assertion | TA-09.02.01.05 |
|---|---|
| Purpose | Verifies that the eContentType of the encapContentInfo is id-icao-ldsSecurityObject and the eContent field of the encapContentInfo contains the contents of the ldsSecurity object. |
| DTR(s) | • DTR-07.02.01.06 • DTR-07.02.01.07 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the encapContentInfo field contents from the Security Object. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the eContent field contains a correctly formatted ldsSecurityobject and the eContentType asserts id-icao-ldsSecurityObject in encapContentInfo. |
| テストアサーション | TA-09.02.01.05 |
|---|---|
| 目的 | encapContentInfoのeContentTypeがid-icao-ldsSecurityObjectであり、encapContentInfoのeContentフィールドがldsSecurityオブジェクトの内容を含むことを検証します。 |
| DTR | • DTR-07.02.01.06 • DTR-07.02.01.07 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security ObjectからencapContentInfoフィールドの内容を抽出して解析します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、eContentフィールドは正しい形式のldsSecurityobjectを含み、eContentTypeはencapContentInfoにおいてid-icao-ldsSecurityObjectを表明しています。 |
9.2.1.6 Derived PIV Credential Issuer’s (Content Signing) Certificate Inclusion
9.2.1.6 Derived PIV Credential発行者(コンテンツ署名)証明書の包含
| Test Assertion | TA-09.02.01.06 |
|---|---|
| Purpose | Verifies that the Security Object includes the certificate of the Derived PIV Credential Issuer (i.e., the issuer’s content signing certificate). |
| DTR(s) | • DTR-07.02.01.08 |
| Issuer Documentation | None. |
| テストアサーション | TA-09.02.01.06 |
|---|---|
| 目的 | Security Objectが、Derived PIV Credential Issuerの証明書(すなわち発行者のコンテンツ署名証明書)を含むことを検証します。 |
| DTR | • DTR-07.02.01.08 |
| 発行者文書 | なし。 |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
|---|---|
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the certificates field contents from the Security Object. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns status word '90 00' along with the Security Object. 3. From Step 3, the certificates field contains an X.509 certificate which is the Derived PIV Credential Issuer’s (content signing) certificate. |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
|---|---|
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectからcertificatesフィールドの内容を抽出して解析します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドはSecurity Objectとともにステータスワード'90 00'を返します。 3. 手順3より、certificatesフィールドは、Derived PIV Credential Issuerの(コンテンツ署名)証明書であるX |
9.2.1.7 SignerInfo digestAlgorithm
9.2.1.7 SignerInfoのdigestAlgorithm
| Test Assertion | TA-09.02.01.07 |
|---|---|
| Purpose | Verifies that the digestAlgorithm field of the SignerInfo field is in accordance with Table 3-2 of [SP800-78]. |
| DTR(s) | • DTR-07.02.01.09 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract the SignerInfo->digestAlgorithm field from the Security Object. 4. Extract the certificates field contents from the Security Object. 5. From the certificate obtained, extract the subjectPublicKeyInfo->subjectPublicKey 6. Compute the type and size of the signer’s public key. |
| テストアサーション | TA-09.02.01.07 |
|---|---|
| 目的 | SignerInfoフィールドのdigestAlgorithmフィールドが、[SP800-78]のTable 3-2に従っていることを検証します。 |
| DTR | • DTR-07.02.01.09 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security ObjectからSignerInfo->digestAlgorithmフィールドを抽出します。 4. Security Objectからcertificatesフィールドの内容を抽出します。 5. 取得した証明書からsubjectPublicKeyInfo->subjectPublicKeyを抽出します。 6. 署名者の公開鍵の種類とサイズを算出します。 |
| 7. Determine the digest algorithm specified in the digestAlgorithm field obtained in Step 3 using Table 3-6 of [SP800-78]. 8. Match the digest algorithm obtained from Step 7 to an entry of Table 3-2 of [SP800-78] based on the public key algorithm and size (Step 6). | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command the requested data object along with the returns status word '90 00'. 3. From Step 8, the digestAlgorithm field value of the SignerInfo is in accordance with Tables 3-6 and 3-2 of [SP800-78] and it matches the value present in the digestAlgorithms field of the SignedData. |
| 7. [SP800-78]のTable 3-6を用いて、手順3で得たdigestAlgorithmフィールドに指定されたダイジェストアルゴリズムを判定します。 8. 公開鍵アルゴリズムとサイズ(手順6)に基づいて、手順7で得たダイジェストアルゴリズムを[SP800-78]のTable 3-2のエントリと照合します。 | |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順8より、SignerInfoのdigestAlgorithmフィールドの値は[SP800-78]のTable 3-6およびTable 3-2に従っており、SignedDataのdigestAlgorithmsフィールドに存在する値と一致します。 |
9.2.1.8 SignerInfo signatureAlgorithm
9.2.1.8 SignerInfoのsignatureAlgorithm
| Test Assertion | TA-09.02.01.08 |
|---|---|
| Purpose | Verifies that for RSA with PKCS #1 v1.5 padding, the signatureAlgorithm field specifies the rsaEncryption OID (as per Section 3.2 of [RFC3370]) and for ECDSA and RSA with PSS padding, the signatureAlgorithm is in accordance with Table 3-3 of [SP800-78]. |
| DTR(s) | • DTR-07.02.01.10 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. From the signature block (tag 0xBB) match the SignerInfo->signatureAlgorithm field contents to an entry in Table 3-3 of [SP800-78]. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the signatureAlgorithm field specified in the SignerInfo field for RSA with PKCS #1 v1.5 padding specifies the rsaEncryption OID (as per Section 3.2 of [RFC3370]) and for ECDSA and RSA with PSS padding, the |
| テストアサーション | TA-09.02.01.08 |
|---|---|
| 目的 | PKCS #1 v1 |
| DTR | • DTR-07.02.01.10 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. 署名ブロック(タグ0xBB)から、SignerInfo->signatureAlgorithmフィールドの内容を[SP800-78]のTable 3-3のエントリと照合します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、SignerInfoフィールドに指定されたsignatureAlgorithmフィールドは、PKCS #1 v1 |
| signatureAlgorithm is in accordance with Table 3-3 of [SP800-78]. |
| signatureAlgorithmが[SP800-78]のTable 3-3に従っています。 |
9.2.1.9 Digital Signature
9.2.1.9 デジタル署名
| Test Assertion | TA-09.02.01.09 |
|---|---|
| Purpose | Verifies that the signature in the SignerInfo corresponds to the Security Object and that it is signed with the Derived PIV Credential Issuer’s (content signing) certificate. |
| DTR(s) | • DTR-07.02.01.11 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract the contents of the Security Object asymmetric signature (TAG 0xBB). 4. Extract and parse the certificates field contents from the Security Object. 5. Using the certificate extracted from the asymmetric signature block, verify the signature of the Security Object. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 5, the certificates field of the SignedData contains the Derived PIV Credential Issuer’s (content signing) certificate, which is used to verify the digital signature on the Security Object. |
| テストアサーション | TA-09.02.01.09 |
|---|---|
| 目的 | SignerInfoの署名がSecurity Objectに対応していること、およびDerived PIV Credential Issuerの(コンテンツ署名)証明書で署名されていることを検証します。 |
| DTR | • DTR-07.02.01.11 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectの非対称署名(TAG 0xBB)の内容を抽出します。 4. Security Objectからcertificatesフィールドの内容を抽出して解析します。 5. 非対称署名ブロックから抽出した証明書を用いて、Security Objectの署名を検証します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順5より、SignedDataのcertificatesフィールドは、Security Object上のデジタル署名の検証に用いられるDerived PIV Credential Issuerの(コンテンツ署名)証明書を含んでいます。 |
9.3 PKI Conformance
9.3 PKI適合性
9.3.1 X.509 Certificate for Derived PIV Authentication18
9.3.1 派生PIV認証用X.509証明書18
9.3.1.1 Signature Algorithm
9.3.1.1 署名アルゴリズム
| Test Assertion | TA-09.03.01.01 |
|---|---|
| Purpose | Verifies that the proper signature algorithm has been used to sign the Derived PIV Authentication certificate as specified in Table 3-3 of [SP800-78]. |
| DTR(s) | • DTR-07.03.01.01 • DTR-07.03.01.02 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Extract signature->algorithm field value from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00' 3. From Step 3, the algorithm value is in accordance with Table 3-3 of [SP800-78]. If the algorithm value is id-RSASSA-PSS, then the hashAlgorithm field in signature->parameters is populated with SHA-256 (OID = 2.16.840.1.101.3.4.2.1). For RSA with PKCS #1 v1.5 padding, the parameters field is populated with NULL. For ECDSA, the parameters field is absent. |
| テストアサーション | TA-09.03.01.01 |
|---|---|
| 目的 | [SP800-78]のTable 3-3に規定されているとおり、Derived PIV Authentication certificateへの署名に適切な署名アルゴリズムが使用されていることを検証します。 |
| DTR | • DTR-07.03.01.01 • DTR-07.03.01.02 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. 証明書からsignature->algorithmフィールドの値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、アルゴリズムの値は[SP800-78]のTable 3-3に従っています。アルゴリズムの値がid-RSASSA-PSSの場合、signature->parametersのhashAlgorithmフィールドにはSHA-256(OID = 2 |
9.3.1.2 Subject Public Key Algorithm
9.3.1.2 主体公開鍵アルゴリズム
| Test Assertion | TA-09.03.01.02 |
|---|---|
| Purpose | Verifies that the public key algorithm used for generating the keys is as specified in Table 3-4 of [SP800-78]. |
| DTR(s) | • DTR-07.03.01.03 • DTR-07.03.01.04 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Extract subjectPublicKeyInfo->algorithm->algorithm field value 4. Match the algorithm value to the Table 3-4 of [SP800-78]. 5. If the algorithm is elliptic curve, ensure that the OID for Curve P-256 from Table 3-5 of [SP800-78] is populated in the subjectPublicKeyInfo->algorithm->parameters->namedCurve field. Note: If the RSA algorithm is used, the subjectPublicKeyInfo->algorithm->parameters field will be NULL. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word ‘90 00’. 2. From Step 2, the command returns the requested data object along with the status word ‘90 00’. 3. From Steps 4 and 5, it is determined that the Derived PIV Authentication key is generated using an allowed asymmetric key algorithm. |
| テストアサーション | TA-09.03.01.02 |
|---|---|
| 目的 | 鍵の生成に使用された公開鍵アルゴリズムが、[SP800-78]のTable 3-4に規定されたものであることを検証します。 |
| DTR | • DTR-07.03.01.03 • DTR-07.03.01.04 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. subjectPublicKeyInfo->algorithm->algorithmフィールドの値を抽出する 4. アルゴリズムの値を[SP800-78]のTable 3-4と照合します。 5. アルゴリズムが楕円曲線の場合、[SP800-78]のTable 3-5にあるCurve P-256のOIDがsubjectPublicKeyInfo->algorithm->parameters->namedCurveフィールドに設定されていることを確認します。注:RSAアルゴリズムが使用される場合、subjectPublicKeyInfo->algorithm->parametersフィールドはNULLとなります。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4および5より、Derived PIV Authentication keyが許可された非対称鍵アルゴリズムを用いて生成されていると判定されます。 |
9.3.1.3 Public Key Size
9.3.1.3 公開鍵長
| Test Assertion | TA-09.03.01.03 |
|---|---|
| Purpose | Verifies that the key size requirements are in accordance with Table 3-1 of [SP800-78]. |
| DTR(s) | • DTR-07.03.01.12 |
| Issuer Documentation | None. |
| テストアサーション | TA-09.03.01.03 |
|---|---|
| 目的 | 鍵サイズの要件が[SP800-78]のTable 3-1に従っていることを検証します。 |
| DTR | • DTR-07.03.01.12 |
| 発行者文書 | なし。 |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
|---|---|
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Extract subjectPublicKeyInfo->algorithm->algorithm field value. 4. Extract the subjectPublicKeyInfo->subjectPublicKey from the certificate 5. Match the key size to Table 3-1 of [SP800-78]. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 5, the key size is in accordance with Table 3-1 of [SP800-78]. |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
|---|---|
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. subjectPublicKeyInfo->algorithm->algorithmフィールドの値を抽出します。 4. 証明書からsubjectPublicKeyInfo->subjectPublicKeyを抽出する 5. 鍵サイズを[SP800-78]のTable 3-1と照合します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順5より、鍵サイズは[SP800-78]のTable 3-1に従っています。 |
9.3.1.4 Key Usage Extension
9.3.1.4 Key Usage拡張
| Test Assertion | TA-09.03.01.04 |
|---|---|
| Purpose | Verifies that the Derived PIV Authentication certificate asserts the appropriate purpose for the key. |
| DTR(s) | • DTR-07.03.01.05 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Extract the value of the keyUsage extension from the certificate |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. |
| テストアサーション | TA-09.03.01.04 |
|---|---|
| 目的 | Derived PIV Authentication certificateが鍵の適切な用途を表明していることを検証します。 |
| DTR | • DTR-07.03.01.05 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. 証明書からkeyUsage拡張の値を抽出する |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 |
| 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the digitalSignature bit has been set. No other bits have been set. |
| 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、digitalSignatureビットが設定されています。他のビットは設定されていません。 |
9.3.1.5 Certificate Policy
9.3.1.5 証明書ポリシー
| Test Assertion | TA-09.03.01.05 |
|---|---|
| Purpose | Verifies that the Derived PIV Authentication certificate asserts the appropriate certificate policy OID. |
| DTR(s) | • DTR-07.03.01.06 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application token is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object. 3. Extract the value of the certificatePolicies extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the certificatePolicies extension asserts either the id-fpki-common-derived-pivAuth or id-fpki-common-derived-pivAuth-hardware OID. |
| テストアサーション | TA-09.03.01.05 |
|---|---|
| 目的 | Derived PIV Authentication certificateが適切な証明書ポリシーOIDを表明していることを検証します。 |
| DTR | • DTR-07.03.01.06 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含めます。 3. 証明書からcertificatePolicies拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、certificatePolicies拡張は、id-fpki-common-derived-pivAuthまたはid-fpki-common-derived-pivAuth-hardwareのいずれかのOIDを表明しています。 |
9.3.1.6 Authority Information Access Extension
9.3.1.6 Authority Information Access拡張
| Test Assertion | TA-09.03.01.06 |
|---|---|
| Purpose | Verifies that the authority information access extension in the Derived PIV Authentication certificate is populated with: (i) the location to the OCSP server that provides status information for this certificate and (ii) the location to an HTTP accessible Web server where certificates issued to the issuer of this certificate may be found. |
| DTR(s) | • DTR-07.03.01.09 • DTR-07.03.01.11 |
| テストアサーション | TA-09.03.01.06 |
|---|---|
| 目的 | Derived PIV Authentication certificateのauthority information access拡張に、(i) この証明書のステータス情報を提供するOCSPサーバーの場所、および (ii) この証明書の発行者に対して発行された証明書を入手できる、HTTPでアクセス可能なWebサーバーの場所が設定されていることを検証します。 |
| DTR | • DTR-07.03.01.09 • DTR-07.03.01.11 |
| Issuer Documentation | None. |
|---|---|
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Extract the the value of the authorityInfoAccess extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command the requested data object along with the returns status word '90 00'. 3. From Step 3, an accessMethod containing id-ad-ocsp (1.3.6.1.5.5.7.48.1) is present that contains an accessLocation of type uniformResourceIdentifier where the scheme is “http” (not “https”). An id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod is also present where the accessLocation is of type uniformResourceIdentifier and the scheme is “http.” |
| 発行者文書 | なし。 |
|---|---|
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. 証明書からauthorityInfoAccess拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、id-ad-ocsp(1 |
9.3.1.7 Asymmetric Key Pair
9.3.1.7 非対称鍵ペア
| Test Assertion | TA-09.03.01.07 |
|---|---|
| Purpose | Verifies that the public key that exists in the Derived PIV Authentication certificate corresponds to the private key located in the Derived PIV Application. |
| DTR(s) | • DTR-07.03.01.13 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with |
| テストアサーション | TA-09.03.01.07 |
|---|---|
| 目的 | Derived PIV Authentication certificateに存在する公開鍵が、派生PIVアプリケーションに格納されている秘密鍵に対応することを検証します。 |
| DTR | • DTR-07.03.01.13 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 |
| • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object. 3. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 4. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07' or '11'. P2, key reference, is set to '9A' indicating the Derived PIV Authentication Key • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response 5. Verify the signature obtained in Step 4 using the subject public key from the certificate. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with status word '90 00'. 3. From Step 3, the command returns the status word '90 00'. 4. From Step 4, the command returns the signed challenge with the status word '90 00'. 5. From Step 5, the private key corresponds to the public key contained in the certificate as the signature verification succeeds. |
| • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含めます。 3. 次の内容でVERIFYコマンドを送信します。 • P2(鍵参照値)を'80'に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて'FF'でパディングして値の全長を8バイトにする 4. GENERAL AUTHENTICATEコマンドを送信します。 • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は'00'、コマンドチェーンを使用する場合は'10'。(コマンドの最後のチェーンではCLAを'00'に設定する) • P1(アルゴリズム参照)を'07'または'11'に設定します。P2(鍵参照)を、Derived PIV Authentication Keyを示す'9A'に設定する • コマンドのデータフィールドには、チャレンジを指定する'81'、続いてランダムに生成したチャレンジ、さらに応答を要求するための'82 00'を含める 5. 証明書のサブジェクト公開鍵を用いて、手順4で得た署名を検証します。 | |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、コマンドはステータスワード'90 00'を返します。 4. 手順4より、コマンドは署名されたチャレンジとステータスワード'90 00'を返します。 5. 手順5より、署名検証が成功するため、秘密鍵は証明書に含まれる公開鍵に対応しています。 |
9.3.1.8 UUID in the subjectAltName
9.3.1.8 subjectAltName内のUUID
| Test Assertion | TA-09.03.01.08 |
|---|---|
| Purpose | Verifies that a UUID is populated in the subjectAltName field of the Derived PIV Authentication certificate. |
| DTR(s) | • DTR-07.03.01.07 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
| テストアサーション | TA-09.03.01.08 |
|---|---|
| 目的 | Derived PIV Authentication certificateのsubjectAltNameフィールドにUUIDが設定されていることを検証します。 |
| DTR | • DTR-07.03.01.07 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Extract the value of the subjectAltName extension from the certificate. |
|---|---|
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, a name of type uniformResourceIdentifier containing a UUID is present. |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. 証明書からsubjectAltName拡張の値を抽出します。 |
|---|---|
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、UUIDを含むuniformResourceIdentifier型の名前が存在します。 |
9.3.1.9 piv-interim Extension
9.3.1.9 piv-interim拡張
| Test Assertion | TA-09.03.01.09 |
|---|---|
| Purpose | Verifies that the piv-interim extension is present in the Derived PIV Authentication certificate. |
| DTR(s) | • DTR-07.03.01.08 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Extract the piv-interim extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the non-critical piv-interim extension is present and contains the interim_indicator field, which is of type BOOLEAN. |
| テストアサーション | TA-09.03.01.09 |
|---|---|
| 目的 | Derived PIV Authentication certificateにpiv-interim拡張が存在することを検証します。 |
| DTR | • DTR-07.03.01.08 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. 証明書からpiv-interim拡張を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、非クリティカルなpiv-interim拡張が存在し、BOOLEAN型のinterim |
9.3.1.10 cRLDistributionPoints Extension
9.3.1.10 cRLDistributionPoints拡張
| Test Assertion | TA-09.03.01.10 |
|---|---|
| Purpose | Verifies that the cRLDistributionPoints extension in the Derived PIV Authentication certificate contains an HTTP URI. |
| DTR(s) | • DTR-07.03.01.10 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Extract the cRLDistributionPoints extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, a URI with the “HTTP” scheme that can be used to access CRL information is present. |
| テストアサーション | TA-09.03.01.10 |
|---|---|
| 目的 | Derived PIV Authentication certificateのcRLDistributionPoints拡張がHTTP URIを含むことを検証します。 |
| DTR | • DTR-07.03.01.10 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. 証明書からcRLDistributionPoints拡張を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、CRL情報へのアクセスに使用できる、スキームが“HTTP”のURIが存在します。 |
9.3.1.11 RSA Exponent
9.3.1.11 RSA公開指数
| Test Assertion | TA-09.03.01.11 |
|---|---|
| Purpose | Verifies that for RSA keys, the exponent of the asymmetric key for Derived PIV Authentication is equal to 65 537. |
| DTR(s) | • DTR-07.05.01.14 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Derived PIV Authentication certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with |
| テストアサーション | TA-09.03.01.11 |
|---|---|
| 目的 | RSA鍵の場合、Derived PIV Authentication用の非対称鍵の指数が65 537に等しいことを検証します。 |
| DTR | • DTR-07.05.01.14 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にDerived PIV Authentication certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 |
| • Data field of the command containing the tag ('5FC105') of the X.509 Certificate for Derived PIV Authentication data object 3. Extract the subjectPublicKeyInfo->subjectPublicKey from the certificate. 4. Parse the exponent from the extracted public key. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 4, the exponent of the RSA asymmetric key for PIV Authentication is equal to 65 537. |
| • コマンドのデータフィールドにX.509 Certificate for Derived PIV Authenticationデータオブジェクトのタグ('5FC105')を含める 3. 証明書からsubjectPublicKeyInfo->subjectPublicKeyを抽出します。 4. 抽出した公開鍵から指数を解析して取り出します。 | |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4より、PIV Authentication用のRSA非対称鍵の指数は65 537に等しい値です。 |
9.3.2 X.509 Certificate for Digital Signature19
9.3.2 電子署名用X.509証明書19
9.3.2.1 Signature Algorithm
9.3.2.1 署名アルゴリズム
| Test Assertion | TA-09.03.02.01 |
|---|---|
| Purpose | Verifies that the proper signature algorithm has been used to sign the digital signature certificate as specified in Table 3-3 of [SP800-78]. |
| DTR(s) | • DTR-07.03.02.01 • DTR-07.03.02.02 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A digital signature certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object 3. Extract signature->algorithm field value from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. |
| テストアサーション | TA-09.03.02.01 |
|---|---|
| 目的 | [SP800-78]のTable 3-3に規定されているとおり、digital signature certificateへの署名に適切な署名アルゴリズムが使用されていることを検証します。 |
| DTR | • DTR-07.03.02.01 • DTR-07.03.02.02 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にdigital signature certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める 3. 証明書からsignature->algorithmフィールドの値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 |
| 3. From Step 3, the algorithm value is in accordance with Table 3-3 of [SP800-78]. If the algorithm value is id-RSASSA-PSS, then the hashAlgorithm field in signature->parameters is populated with SHA-256 (OID = 2.16.840.1.101.3.4.2.1). For RSA with PKCS #1 v1.5 padding, the parameters field is populated with NULL. For ECDSA, the parameters field is absent. |
| 3. 手順3より、アルゴリズムの値は[SP800-78]のTable 3-3に従っています。アルゴリズムの値がid-RSASSA-PSSの場合、signature->parametersのhashAlgorithmフィールドにはSHA-256(OID = 2 |
9.3.2.2 Subject Public Key Algorithm
9.3.2.2 主体公開鍵アルゴリズム
| Test Assertion | TA-09.03.02.02 |
|---|---|
| Purpose | Verifies that the public key algorithm used for generating the keys is as specified in Table 3-4 of [SP800-78]. |
| DTR(s) | • DTR-07.03.02.03 • DTR-07.03.02.04 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A digital signature certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object 3. Extract subjectPublicKeyInfo->algorithm->algorithm field value. 4. Match the algorithm value to the Table 3-4 of [SP800-78]. 5. If the algorithm is elliptic curve, ensure that an OID from Table 3-5 of [SP800-78] is populated in the subjectPublicKeyInfo->algorithm->parameters->namedCurve field. Note: If the RSA algorithm is used, the subjectPublicKeyInfo->algorithm->parameters field will be NULL. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Steps 4 and 5, the digital signature key is generated using an allowed asymmetric key algorithm. |
| テストアサーション | TA-09.03.02.02 |
|---|---|
| 目的 | 鍵の生成に使用された公開鍵アルゴリズムが、[SP800-78]のTable 3-4に規定されたものであることを検証します。 |
| DTR | • DTR-07.03.02.03 • DTR-07.03.02.04 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にdigital signature certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める 3. subjectPublicKeyInfo->algorithm->algorithmフィールドの値を抽出します。 4. アルゴリズムの値を[SP800-78]のTable 3-4と照合します。 5. アルゴリズムが楕円曲線の場合、[SP800-78]のTable 3-5にあるOIDがsubjectPublicKeyInfo->algorithm->parameters->namedCurveフィールドに設定されていることを確認します。注:RSAアルゴリズムが使用される場合、subjectPublicKeyInfo->algorithm->parametersフィールドはNULLとなります。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4および5より、デジタル署名鍵が許可された非対称鍵アルゴリズムを用いて生成されています。 |
9.3.2.3 Public Key Size
9.3.2.3 公開鍵長
| Test Assertion | TA-09.03.02.03 |
|---|---|
| Purpose | Verifies that the key size requirements are in accordance with Table 3-1 of [SP800-78]. |
| DTR(s) | • DTR-07.03.02.09 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A digital signature certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT token command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object 3. Extract subjectPublicKeyInfo->algorithm->algorithm field value. 4. Extract the subjectPublicKeyInfo->subjectPublicKey from the certificate 5. Match the key size to Table 3-1 of [SP800-78]. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 5, the key size is in accordance with Table 3-1 of [SP800-78]. |
| テストアサーション | TA-09.03.02.03 |
|---|---|
| 目的 | 鍵サイズの要件が[SP800-78]のTable 3-1に従っていることを検証します。 |
| DTR | • DTR-07.03.02.09 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にdigital signature certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTトークンコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める 3. subjectPublicKeyInfo->algorithm->algorithmフィールドの値を抽出します。 4. 証明書からsubjectPublicKeyInfo->subjectPublicKeyを抽出する 5. 鍵サイズを[SP800-78]のTable 3-1と照合します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順5より、鍵サイズは[SP800-78]のTable 3-1に従っています。 |
9.3.2.4 Key Usage Extension
9.3.2.4 Key Usage拡張
| Test Assertion | TA-09.03.02.04 |
|---|---|
| Purpose | Verifies that the digital signature certificate asserts the appropriate purposes for the key. |
| DTR(s) | • DTR-07.03.02.05 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A digital signature certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' |
| テストアサーション | TA-09.03.02.04 |
|---|---|
| 目的 | digital signature certificateが鍵の適切な用途を表明していることを検証します。 |
| DTR | • DTR-07.03.02.05 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にdigital signature certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' |
| 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object 3. Extract the value of the keyUsage extension from the certificate. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the digitalSignature and nonRepudiation bits have been set. No other bits have been set. |
| 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める 3. 証明書からkeyUsage拡張の値を抽出します。 | |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、digitalSignatureビットおよびnonRepudiationビットが設定されています。他のビットは設定されていません。 |
9.3.2.5 Certificate Policy
9.3.2.5 証明書ポリシー
| Test Assertion | TA-09.03.02.05 |
|---|---|
| Purpose | Verifies that the digital signature certificate asserts the appropriate certificate policy OID. |
| DTR(s) | • DTR-07.03.02.06 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A digital signature certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object. 3. Extract the value of the certificatePolicies extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the certificatePolicies extension asserts one of the following: id-fpki-common-policy, id-fpki-common-hardware or id-fpki-common-High. |
| テストアサーション | TA-09.03.02.05 |
|---|---|
| 目的 | digital signature certificateが適切な証明書ポリシーOIDを表明していることを検証します。 |
| DTR | • DTR-07.03.02.06 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にdigital signature certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含めます。 3. 証明書からcertificatePolicies拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、certificatePolicies拡張は次のいずれかを表明している:id-fpki-common-policy、id-fpki-common-hardware、またはid-fpki-common-High。 |
9.3.2.6 Authority Information Access Extension
9.3.2.6 Authority Information Access拡張
| Test Assertion | TA-09.03.02.06 |
|---|---|
| Purpose | Verifies that the authority information access extension in the digital signature certificate is populated appropriately and contains |
| テストアサーション | TA-09.03.02.06 |
|---|---|
| 目的 | digital signature certificateのauthority information access拡張が適切に設定され、 |
| an id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod, which points to the location where the certificates issued to the issuer of this certificate can be found. | |
| DTR(s) | • DTR-07.03.02.07 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A digital signature certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object. 3. Extract the value of the authorityInfoAccess extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the authorityInfoAccess extension contains an id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod with an accessLocation of type uniformResourceIdentifier where the scheme is “http” or “ldap.” |
| この証明書の発行者に対して発行された証明書を入手できる場所を指すid-ad-caIssuers(1 | |
| DTR | • DTR-07.03.02.07 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にdigital signature certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含めます。 3. 証明書からauthorityInfoAccess拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、authorityInfoAccess拡張は、uniformResourceIdentifier型でスキームが“http”または“ldap”のaccessLocationを持つid-ad-caIssuers(1 |
9.3.2.7 Asymmetric Key Pair
9.3.2.7 非対称鍵ペア
| Test Assertion | TA-09.03.02.07 |
|---|---|
| Purpose | Verifies that the public key that exists in the digital signature certificate corresponds to the private key within the Derived PIV Application. |
| DTR(s) | • DTR-07.03.02.10 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A digital signature certificate is present within the Derived PIV Application. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| テストアサーション | TA-09.03.02.07 |
|---|---|
| 目的 | digital signature certificateに存在する公開鍵が、派生PIVアプリケーション内の秘密鍵に対応することを検証します。 |
| DTR | • DTR-07.03.02.10 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にdigital signature certificateが存在します。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object 3. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 4. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07', '11', or '14'. P2, key reference, is set to '9C' indicating the digital signature key • Data field in the command is to include '81' specifying a challenge, followed by a randomly generated challenge, and '82 00' in order to request a response 5. Verify the signature obtained in Step 4 using the subject public key from the certificate obtained in Step 2. |
|---|---|
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with status word '90 00'. 3. From Step 3, the command returns status word '90 00'. 4. From Step 4, the command returns the signed challenge with the status word '90 00' 5. From Step 5, the private key corresponds to the public key contained in the certificate as the signature verification succeeds. |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める 3. 次の内容でVERIFYコマンドを送信します。 • P2(鍵参照値)を'80'に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションパスワードを含め、必要に応じて'FF'でパディングして値の全長を8バイトにする 4. GENERAL AUTHENTICATEコマンドを送信します。 • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は'00'、コマンドチェーンを使用する場合は'10'。(コマンドの最後のチェーンではCLAを'00'に設定する) • P1(アルゴリズム参照)を'07'、'11'、または'14'に設定します。P2(鍵参照)を、デジタル署名鍵を示す'9C'に設定する • コマンドのデータフィールドには、チャレンジを指定する'81'、続いてランダムに生成したチャレンジ、さらに応答を要求するための'82 00'を含める 5. 手順2で得た証明書のサブジェクト公開鍵を用いて、手順4で得た署名を検証します。 |
|---|---|
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、コマンドはステータスワード'90 00'を返します。 4. 手順4より、コマンドは署名されたチャレンジとステータスワード'90 00'を返します。 5. 手順5より、署名検証が成功するため、秘密鍵は証明書に含まれる公開鍵に対応しています。 |
9.3.2.8 cRLDistributionPoints Extension
9.3.2.8 cRLDistributionPoints拡張
| Test Assertion | TA-09.03.02.08 |
|---|---|
| Purpose | Verifies that the cRLDistributionPoints extension in the digital signature certificate contains at least one URI, either LDAP or HTTP. |
| DTR(s) | • DTR-07.03.02.08 |
| Issuer Documentation | None. |
| テストアサーション | TA-09.03.02.08 |
|---|---|
| 目的 | digital signature certificateのcRLDistributionPoints拡張が、LDAPまたはHTTPのURIを少なくとも1つ含むことを検証します。 |
| DTR | • DTR-07.03.02.08 |
| 発行者文書 | なし。 |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A digital signature certificate is present within the Derived PIV Application. |
|---|---|
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object 3. Extract the cRLDistributionPoints extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, a URI with either the “LDAP” or “HTTP” scheme that can be used to access CRL information is present. |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にdigital signature certificateが存在します。 |
|---|---|
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める 3. 証明書からcRLDistributionPoints拡張を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、CRL情報へのアクセスに使用できる、スキームが“LDAP”または“HTTP”のURIが存在します。 |
9.3.2.9 RSA Exponent
9.3.2.9 RSA公開指数
| Test Assertion | TA-09.03.02.09 |
|---|---|
| Purpose | Verifies that for RSA keys, the exponent of the asymmetric key for digital signature is equal to 65 537. |
| DTR(s) | • DTR-07.03.02.11 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A digital signature certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10A') of the X.509 Certificate for Digital Signature data object 3. Extract the subjectPublicKeyInfo->subjectPublicKey from the certificate. 4. Parse the exponent from the extracted public key. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. |
| テストアサーション | TA-09.03.02.09 |
|---|---|
| 目的 | RSA鍵の場合、デジタル署名用の非対称鍵の指数が65 537に等しいことを検証します。 |
| DTR | • DTR-07.03.02.11 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にdigital signature certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Digital Signatureデータオブジェクトのタグ('5FC10A')を含める 3. 証明書からsubjectPublicKeyInfo->subjectPublicKeyを抽出します。 4. 抽出した公開鍵から指数を解析して取り出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 |
| 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 4, the exponent of the RSA asymmetric key for digital signature is equal to 65 537. |
| 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4より、デジタル署名用のRSA非対称鍵の指数は65 537に等しい値です。 |
9.3.3 X.509 Certificate for Key Management20
9.3.3 鍵管理用X.509証明書20
9.3.3.1 Signature Algorithm
9.3.3.1 署名アルゴリズム
| Test Assertion | TA-09.09.03.01 |
|---|---|
| Purpose | Verifies that the proper signature algorithm has been used to sign the key management certificate as specified in Table 3-3 of [SP800-78]. |
| DTR(s) | • DTR-07.03.03.01 • DTR-07.03.03.02 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A key management certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 3. Extract signature->algorithm field value from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the algorithm value is in accordance with Table 3-3 of [SP800-78]. If the algorithm value is id-RSASSA-PSS, then the hashAlgorithm field in signature->parameters field is populated with SHA-256 (OID = 2.16.840.1.101.3.4.2.1). For RSA with PKCS #1 v1.5 padding, the parameters field is populated with NULL. For ECDSA, the parameters field is absent. |
| テストアサーション | TA-09.09.03.01 |
|---|---|
| 目的 | [SP800-78]のTable 3-3に規定されているとおり、key management certificateへの署名に適切な署名アルゴリズムが使用されていることを検証します。 |
| DTR | • DTR-07.03.03.01 • DTR-07.03.03.02 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にkey management certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 3. 証明書からsignature->algorithmフィールドの値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、アルゴリズムの値は[SP800-78]のTable 3-3に従っています。アルゴリズムの値がid-RSASSA-PSSの場合、signature->parametersフィールドのhashAlgorithmフィールドにはSHA-256(OID = 2 |
9.3.3.2 Subject Public Key Algorithm
9.3.3.2 主体公開鍵アルゴリズム
| Test Assertion | TA-09.03.03.02 |
|---|---|
| Purpose | Verifies that the public key algorithm used for generating the keys is as specified in Table 3-4 of [SP800-78]. |
| DTR(s) | • DTR-07.03.03.03 • DTR-07.03.03.04 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A key management certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 3. Extract subjectPublicKeyInfo->algorithm->algorithm field value. 4. Match the algorithm value to the Table 3-4 of [SP800-78]. 5. If the algorithm is elliptic curve, ensure that an OID from Table 3-5 of [SP800-78] is populated in the subjectPublicKeyInfo->algorithm->parameters->namedCurve field. Note: If the RSA algorithm is used, the subjectPublicKeyInfo->algorithm->parameters field will be be NULL. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Steps 4 and 5, the key management key is generated using an allowed asymmetric key algorithm. |
| テストアサーション | TA-09.03.03.02 |
|---|---|
| 目的 | 鍵の生成に使用された公開鍵アルゴリズムが、[SP800-78]のTable 3-4に規定されたものであることを検証します。 |
| DTR | • DTR-07.03.03.03 • DTR-07.03.03.04 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にkey management certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 3. subjectPublicKeyInfo->algorithm->algorithmフィールドの値を抽出します。 4. アルゴリズムの値を[SP800-78]のTable 3-4と照合します。 5. アルゴリズムが楕円曲線の場合、[SP800-78]のTable 3-5にあるOIDがsubjectPublicKeyInfo->algorithm->parameters->namedCurveフィールドに設定されていることを確認します。注:RSAアルゴリズムが使用される場合、subjectPublicKeyInfo->algorithm->parametersフィールドはNULLとなります。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4および5より、鍵管理鍵が許可された非対称鍵アルゴリズムを用いて生成されています。 |
9.3.3.3 Public Key Size
9.3.3.3 公開鍵長
| Test Assertion | TA-09.09.03.03 |
|---|---|
| Purpose | Verifies that the key size requirements are in accordance with Table 3-1 of [SP800-78]. |
| DTR(s) | • DTR-07.03.03.09 |
| Issuer Documentation | None. |
| テストアサーション | TA-09.09.03.03 |
|---|---|
| 目的 | 鍵サイズの要件が[SP800-78]のTable 3-1に従っていることを検証します。 |
| DTR | • DTR-07.03.03.09 |
| 発行者文書 | なし。 |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A key management certificate is present within the Derived PIV Application. |
|---|---|
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 3. Extract subjectPublicKeyInfo->algorithm->algorithm field value. 4. Extract the subjectPublicKeyInfo->subjectPublicKey from the certificate. 5. Match the key size to Table 3-1 of [SP800-78]. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 5, the key size is in accordance with Table 3-1 of [SP800-78]. |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にkey management certificateが存在します。 |
|---|---|
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 3. subjectPublicKeyInfo->algorithm->algorithmフィールドの値を抽出します。 4. 証明書からsubjectPublicKeyInfo->subjectPublicKeyを抽出します。 5. 鍵サイズを[SP800-78]のTable 3-1と照合します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順5より、鍵サイズは[SP800-78]のTable 3-1に従っています。 |
9.3.3.4 Key Usage Extension
9.3.3.4 Key Usage拡張
| Test Assertion | TA-09.03.03.04 |
|---|---|
| Purpose | Verifies the key management certificate asserts the appropriate purposes for the key. |
| DTR(s) | • DTR-07.03.03.05 |
| Issuer Documentation | None. |
| Precondition(s) | • A Token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A key management certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 4. Extract subjectPublicKeyInfo->algorithm->algorithm field value. 5. Extract the value of the keyUsage extension from the certificate. |
| テストアサーション | TA-09.03.03.04 |
|---|---|
| 目的 | key management certificateが鍵の適切な用途を表明していることを検証します。 |
| DTR | • DTR-07.03.03.05 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にkey management certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 4. subjectPublicKeyInfo->algorithm->algorithmフィールドの値を抽出します。 5. 証明書からkeyUsage拡張の値を抽出します。 |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 5, if the public key algorithm is RSA, then the keyUsage extension only asserts the keyEncipherment bit. If the public key algorithm is elliptic curve, then the keyUsage extension only asserts the keyAgreement bit. |
|---|
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順5より、公開鍵アルゴリズムがRSAの場合、keyUsage拡張はkeyEnciphermentビットのみを表明しています。公開鍵アルゴリズムが楕円曲線の場合、keyUsage拡張はkeyAgreementビットのみを表明しています。 |
|---|
9.3.3.5 Certificate Policy
9.3.3.5 証明書ポリシー
| Test Assertion | TA-09.03.03.05 |
|---|---|
| Purpose | Verifies the key management certificate asserts the appropriate certificate policy OID. |
| DTR(s) | • DTR-07.03.03.06 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A key management certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 3. Extract the value of the certificatePolicies extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the certificatePolicies extension asserts one of the following: id-fpki-common-policy, id-fpki-common-hardware or id-fpki-common-High. |
| テストアサーション | TA-09.03.03.05 |
|---|---|
| 目的 | key management certificateが適切な証明書ポリシーOIDを表明していることを検証します。 |
| DTR | • DTR-07.03.03.06 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にkey management certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 3. 証明書からcertificatePolicies拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、certificatePolicies拡張は次のいずれかを表明している:id-fpki-common-policy、id-fpki-common-hardware、またはid-fpki-common-High。 |
9.3.3.6 Authority Information Access Extension
9.3.3.6 Authority Information Access拡張
| Test Assertion | TA-09.03.03.06 |
|---|---|
| Purpose | Verifies that the authority information access extension in the key management certificate is populated appropriately and contains an id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod, which points to the location where the certificates issued to the issuer of this certificate can be found. |
| テストアサーション | TA-09.03.03.06 |
|---|---|
| 目的 | key management certificateのauthority information access拡張が適切に設定され、この証明書の発行者に対して発行された証明書を入手できる場所を指すid-ad-caIssuers(1 |
| DTR(s) | • DTR-07.03.03.07 |
|---|---|
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A key management certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 3. Extract the value of the authorityInfoAccess extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the authorityInfoAccess extension contains an id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod with an accessLocation of type uniformResourceIdentifier where the scheme is “http” or “ldap.” |
| DTR | • DTR-07.03.03.07 |
|---|---|
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にkey management certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 3. 証明書からauthorityInfoAccess拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、authorityInfoAccess拡張は、uniformResourceIdentifier型でスキームが“http”または“ldap”のaccessLocationを持つid-ad-caIssuers(1 |
9.3.3.7 Asymmetric Key Pair
9.3.3.7 非対称鍵ペア
| Test Assertion | TA-09.03.03.07 |
|---|---|
| Purpose | Verifies that the public key that exists in the key management certificate corresponds to the private key within the Derived PIV Application. |
| DTR(s) | • DTR-07.03.03.10 |
| Issuer Documentation | None. |
| Precondition(s) | • A Token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A key management certificate is present within the Derived PIV Application. • The Derived PIV Application Password is recorded. • The Derived PIV Application Password’s retry counter is not 0. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object |
| テストアサーション | TA-09.03.03.07 |
|---|---|
| 目的 | key management certificateに存在する公開鍵が、派生PIVアプリケーション内の秘密鍵に対応することを検証します。 |
| DTR | • DTR-07.03.03.10 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にkey management certificateが存在します。 • 派生PIVアプリケーションのパスワードが記録されています。 • 派生PIVアプリケーションのパスワードのリトライカウンタが0ではありません。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める |
| 3. Send the VERIFY command with • P2, key reference value, is set to '80' • Data field of the command will contain the correct Derived PIV Application Password, padded with 'FF' (if necessary) to complete the total length of the value to 8 bytes 4. Send the GENERAL AUTHENTICATE command • CLA is set to: 1. '00' if command chaining is not needed or '10' if command chaining is used. (The last chain of the command sets CLA to '00') • P1, algorithm reference, is set to '07', '11', or '14'. P2, key reference, is set to '9D' indicating the key management key • Data field in the command is to include one of the following: 1. If P1 = '07', the template '81' contains an encrypted key 2. If P1 = '11' or '14', the template '85' contains the other party’s public key.21 5. Verify the response obtained in Step 4 using the subject public key from the certificate obtained in Step 2. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, the command returns status word '90 00' 4. From Step 4, for algorithm reference '07', the command returns the transported key with status word '90 00'. For algorithm reference '11' or '14', the command returns the shared secret Z22 with status word '90 00'. 5. From Step 5, the private key corresponds to the public key contained in the certificate. For algorithm reference '07', the test tool application’s copy of the plaintext key corresponds to the one received in the response to Step 4 from the token. For algorithm reference '11' or '14', the shared secret returned in Step 4 matches the shared secret computed off token. |
| 3. 次の内容でVERIFYコマンドを送信します。 • P2(鍵参照値)を'80'に設定する • コマンドのデータフィールドには、正しい派生PIVアプリケーションのパスワードを含め、必要に応じて'FF'でパディングして値の全長を8バイトにする 4. GENERAL AUTHENTICATEコマンドを送信します。 • CLAを次のように設定します。 1. コマンドチェーンが不要な場合は'00'、コマンドチェーンを使用する場合は'10'。(コマンドの最後のチェーンではCLAを'00'に設定する) • P1(アルゴリズム参照)を'07'、'11'、または'14'に設定します。P2(鍵参照)を、鍵管理鍵を示す'9D'に設定する • コマンドのデータフィールドには、次のいずれかを含めます。 1. P1 = '07'の場合、テンプレート'81'に暗号化された鍵を含める 2. P1 = '11'または'14'の場合、テンプレート'85'に相手方の公開鍵を含めます。21 5. 手順2で得た証明書のサブジェクト公開鍵を用いて、手順4で得た応答を検証します。 | |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、コマンドはステータスワード'90 00'を返す 4. 手順4より、アルゴリズム参照が'07'の場合、コマンドは転送された鍵とステータスワード'90 00'を返します。アルゴリズム参照が'11'または'14'の場合、コマンドは共有シークレットZ22とステータスワード'90 00'を返します。 5. 手順5より、秘密鍵は証明書に含まれる公開鍵に対応しています。アルゴリズム参照が'07'の場合、テストツールアプリケーションが保持する平文鍵のコピーは、手順4でトークンから受け取った応答の鍵に対応しています。アルゴリズム参照が'11'または'14'の場合、手順4で返された共有シークレットは、トークン外で計算した共有シークレットと一致します。 |
9.3.3.8 cRLDistributionPoints Extension
9.3.3.8 cRLDistributionPoints拡張
| Test Assertion | TA-09.03.03.08 |
|---|---|
| Purpose | Verifies that the cRLDistributionPoints extension in the key management certificate contains at least one URIs, either LDAP or HTTP. |
| DTR(s) | • DTR-07.03.03.08 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A key management certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 3. Extract the cRLDistributionPoints extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 3, a URI with either the “LDAP” or “HTTP” scheme that can be used to access CRL information is present. |
| テストアサーション | TA-09.03.03.08 |
|---|---|
| 目的 | key management certificateのcRLDistributionPoints拡張が、LDAPまたはHTTPのURIを少なくとも1つ含むことを検証します。 |
| DTR | • DTR-07.03.03.08 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にkey management certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにX.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 3. 証明書からcRLDistributionPoints拡張を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順3より、CRL情報へのアクセスに使用できる、スキームが“LDAP”または“HTTP”のURIが存在します。 |
9.3.3.9 RSA Exponent
9.3.3.9 RSA公開指数
| Test Assertion | TA-09.09.03.09 |
|---|---|
| Purpose | Verifies that for RSA keys, the exponent of the asymmetric key for key management is equal to 65 537. |
| DTR(s) | • DTR-07.03.03.11 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A key management certificate is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with |
| テストアサーション | TA-09.09.03.09 |
|---|---|
| 目的 | RSA鍵の場合、鍵管理用の非対称鍵の指数が65 537に等しいことを検証します。 |
| DTR | • DTR-07.03.03.11 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にkey management certificateが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 |
| • Data field of the command containing the tag ('5FC10B') of the X.509 Certificate for Key Management data object 3. Extract the subjectPublicKeyInfo->subjectPublicKey from the certificate. 4. Parse the exponent from the extracted public key. | |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 4, the exponent of the RSA asymmetric key for key management is equal to 65 537. |
| • コマンドのデータフィールドにX.509 Certificate for Key Managementデータオブジェクトのタグ('5FC10B')を含める 3. 証明書からsubjectPublicKeyInfo->subjectPublicKeyを抽出します。 4. 抽出した公開鍵から指数を解析して取り出します。 | |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4より、鍵管理用のRSA非対称鍵の指数は65 537に等しい値です。 |
9.3.4 X.509 Certificate of the Derived PIV Credential Issuer (Content Signing)
9.3.4 派生PIVクレデンシャル発行者のX.509証明書(コンテンツ署名)
9.3.4.1 Signature Algorithm
9.3.4.1 署名アルゴリズム
| Test Assertion | TA-09.03.04.01 |
|---|---|
| Purpose | Verifies that the signature field of the Derived PIV Credential Issuer's (content signing) certificate specifies one of the following algorithm OIDs: 1.2.840.113549.1.10 (id-RSASSA-PSS), 1.2.840.113549.1.11 (Sha256WithRSAEncryption), 1.2.840.10045.4.3.2 (edsa-with-Sha256), 1.2.840.10045.4.3.3 (edsa-with-Sha384). |
| DTR(s) | • DTR-07.03.04.01 • DTR-07.03.04.02 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the certificates field contents from the Security Object. 4. Extract signature->algorithm field value from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 4, the algorithm value is in accordance with Table 3-3 of [SP800-78]. If the algorithm value is id-RSASSA-PSS, |
| テストアサーション | TA-09.03.04.01 |
|---|---|
| 目的 | Derived PIV Credential Issuerの(コンテンツ署名)証明書のsignatureフィールドが、次のいずれかのアルゴリズムOIDを指定していることを検証する:1 |
| DTR | • DTR-07.03.04.01 • DTR-07.03.04.02 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectからcertificatesフィールドの内容を抽出して解析します。 4. 証明書からsignature->algorithmフィールドの値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4より、アルゴリズムの値は[SP800-78]のTable 3-3に従っています。アルゴリズムの値がid-RSASSA-PSSの場合、 |
| then the hashAlgorithm field in signature->parameters is populated with SHA-256 (OID = 2.16.840.1.101.3.4.2.1). For RSA with PKCS #1 v1.5 padding, the parameters field is populated with NULL. For ECDSA, the parameters field is absent. |
| signature->parametersのhashAlgorithmフィールドにはSHA-256(OID = 2 |
9.3.4.2 Subject Public Key Algorithm
9.3.4.2 主体公開鍵アルゴリズム
| Test Assertion | TA-09.03.04.02 |
|---|---|
| Purpose | Verifies that the public key algorithm used for generating the keys is one of the following OIDs: 1.2.840.113549.1.1.1 (RSA Encryption) or 1.2.840.10045.2.1 (elliptic curve key). |
| DTR(s) | • DTR-07.03.04.03 • DTR-07.03.04.04 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the certificates field contents from the Security Object. 4. Extract subjectPublicKeyInfo->algorithm->algorithm field value from the extracted certificate. 5. Match the algorithm value to the Table 3-4 of [SP800-78]. 6. If the algorithm is elliptic curve, ensure that an OID from Table 3-5 of [SP800-78] is populated in the subjectPublicKeyInfo->algorithm->parameters->namedCurve field. Note: If the RSA algorithm is used, the subjectPublicKeyInfo->algorithm->parameters field will be NULL. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 5, the Derived PIV Credential Issuer’s (content signing) key pair is generated using an allowed asymmetric key algorithm. |
| テストアサーション | TA-09.03.04.02 |
|---|---|
| 目的 | 鍵の生成に使用された公開鍵アルゴリズムが、次のOIDのいずれかであることを検証する:1 |
| DTR | • DTR-07.03.04.03 • DTR-07.03.04.04 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectからcertificatesフィールドの内容を抽出して解析します。 4. 抽出した証明書からsubjectPublicKeyInfo->algorithm->algorithmフィールドの値を抽出します。 5. アルゴリズムの値を[SP800-78]のTable 3-4と照合します。 6. アルゴリズムが楕円曲線の場合、[SP800-78]のTable 3-5にあるOIDがsubjectPublicKeyInfo->algorithm->parameters->namedCurveフィールドに設定されていることを確認します。注:RSAアルゴリズムが使用される場合、subjectPublicKeyInfo->algorithm->parametersフィールドはNULLとなります。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順5より、Derived PIV Credential Issuerの(コンテンツ署名)鍵ペアが、許可された非対称鍵アルゴリズムを用いて生成されています。 |
| 4. From Step 6, the Derived PIV Credential Issuer’s (content signing) key pair is generated using an allowed curve. |
| 4. 手順6より、Derived PIV Credential Issuerの(コンテンツ署名)鍵ペアが、許可された曲線を用いて生成されています。 |
9.3.4.3 Public Key Size23
9.3.4.3 公開鍵長23
| Test Assertion | TA-09.03.04.03 |
|---|---|
| Purpose | Verifies that size of the subject public key in the Derived PIV Credential Issuer’s (content signing) certificate conforms to Table 3-2 of [SP800-78]. |
| DTR(s) | • DTR-07.03.04.10 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the certificates field contents from the Security Object. 4. Extract subjectPublicKeyInfo->algorithm->algorithm field value. 5. Extract the subjectPublicKeyInfo->subjectPublicKey from the certificate 6. Match the key size to Table 3-2 of [SP800-78]. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 6, the key size is in accordance with Table 3-2 of [SP800-78]. |
| テストアサーション | TA-09.03.04.03 |
|---|---|
| 目的 | Derived PIV Credential Issuerの(コンテンツ署名)証明書のサブジェクト公開鍵のサイズが、[SP800-78]のTable 3-2に適合していることを検証します。 |
| DTR | • DTR-07.03.04.10 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectからcertificatesフィールドの内容を抽出して解析します。 4. subjectPublicKeyInfo->algorithm->algorithmフィールドの値を抽出します。 5. 証明書からsubjectPublicKeyInfo->subjectPublicKeyを抽出する 6. 鍵サイズを[SP800-78]のTable 3-2と照合します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順6より、鍵サイズは[SP800-78]のTable 3-2に従っています。 |
9.3.4.4 Key Usage Extension
9.3.4.4 Key Usage拡張
| Test Assertion | TA-09.03.04.04 |
|---|---|
| Purpose | Verifies the Derived PIV Credential Issuer’s (content signing) certificate asserts the appropriate purpose for the key. |
| DTR(s) | • DTR-07.03.04.05 |
| Issuer Documentation | None. |
| テストアサーション | TA-09.03.04.04 |
|---|---|
| 目的 | Derived PIV Credential Issuerの(コンテンツ署名)証明書が鍵の適切な用途を表明していることを検証します。 |
| DTR | • DTR-07.03.04.05 |
| 発行者文書 | なし。 |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
|---|---|
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the certificates field contents from the Security Object. 4. Extract the value of the keyUsage extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command the requested data object along with the returns status word '90 00'. 3. From Step 4, the digitalSignature bit has been set. No other bits have been set. |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
|---|---|
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectからcertificatesフィールドの内容を抽出して解析します。 4. 証明書からkeyUsage拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4より、digitalSignatureビットが設定されています。他のビットは設定されていません。 |
9.3.4.5 Certificate Policy
9.3.4.5 証明書ポリシー
| Test Assertion | TA-09.03.04.05 |
|---|---|
| Purpose | Verifies the Derived PIV Credential Issuer’s (content signing) certificate asserts the appropriate certificate policy OID. |
| DTR(s) | • DTR-07.03.04.06 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the certificates field contents from the Security Object. 4. Extract the value of the certificatePolicies extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command the requested data object along with the returns status word '90 00'. |
| テストアサーション | TA-09.03.04.05 |
|---|---|
| 目的 | Derived PIV Credential Issuerの(コンテンツ署名)証明書が適切な証明書ポリシーOIDを表明していることを検証します。 |
| DTR | • DTR-07.03.04.06 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectからcertificatesフィールドの内容を抽出して解析します。 4. 証明書からcertificatePolicies拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 |
| 3. From Step 4, the certificatePolicies extension asserts the id-fpki-common-piv-contentSigning policy. |
| 3. 手順4より、certificatePolicies拡張はid-fpki-common-piv-contentSigningポリシーを表明しています。 |
9.3.4.6 Extended Key Usage
9.3.4.6 Extended Key Usage
| Test Assertion | TA-09.03.04.06 |
|---|---|
| Purpose | Verifies the Derived PIV Credential Issuer’s (content signing) certificate asserts the appropriate OID in the extended key usage extension. |
| DTR(s) | • DTR-07.03.04.07 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the certificates field contents from the Security Object. 4. Extract the value of the extKeyUsage extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 4, the extended key usage extension asserts the id-PIV-content-signing OID, indicating that the certificate is authorized to sign PIV data objects. |
| テストアサーション | TA-09.03.04.06 |
|---|---|
| 目的 | Derived PIV Credential Issuerの(コンテンツ署名)証明書が、extended key usage拡張で適切なOIDを表明していることを検証します。 |
| DTR | • DTR-07.03.04.07 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectからcertificatesフィールドの内容を抽出して解析します。 4. 証明書からextKeyUsage拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4より、extended key usage拡張はid-PIV-content-signing OIDを表明しており、この証明書がPIVデータオブジェクトへの署名を許可されていることを示しています。 |
9.3.4.7 Authority Information Access Extension
9.3.4.7 Authority Information Access拡張
| Test Assertion | TA-09.03.04.07 |
|---|---|
| Purpose | Verifies the authority information access extension in the Derived PIV Credential Issuer’s (content signing) certificate is populated appropriately and contains the id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod, which points to the location where the certificates issued to the issuer of this certificate can be found. |
| DTR(s) | • DTR-07.03.04.08 |
| Issuer Documentation | None. |
| テストアサーション | TA-09.03.04.07 |
|---|---|
| 目的 | Derived PIV Credential Issuerの(コンテンツ署名)証明書のauthority information access拡張が適切に設定され、この証明書の発行者に対して発行された証明書を入手できる場所を指すid-ad-caIssuers(1 |
| DTR | • DTR-07.03.04.08 |
| 発行者文書 | なし。 |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
|---|---|
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the certificates field contents from the Security Object. 4. Extract the value of the authorityInfoAccess extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 4, the authorityInfoAccess extension contains an id-ad-caIssuers (1.3.6.1.5.5.7.48.2) accessMethod with an accessLocation of type uniformResourceIdentifier where the scheme is “http.” |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
|---|---|
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectからcertificatesフィールドの内容を抽出して解析します。 4. 証明書からauthorityInfoAccess拡張の値を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4より、authorityInfoAccess拡張は、uniformResourceIdentifier型でスキームが“http”のaccessLocationを持つid-ad-caIssuers(1 |
9.3.4.8 cRLDistributionPoints Extension
9.3.4.8 cRLDistributionPoints拡張
| Test Assertion | TA-09.03.04.08 |
|---|---|
| Purpose | Verifies that cRLDistributionPoints extension in the Derived PIV Credential Issuer’s (content signing) certificate contains at least one URI, either LDAP or HTTP. |
| DTR(s) | • DTR-07.03.04.09 |
| Issuer Documentation | None. |
| Precondition(s) | • A token with the Derived PIV Application is inserted into an appropriate token reader. • Suitable drivers have been loaded between the test system and an instance of the reader. • A Security Object is present within the Derived PIV Application. |
| Test Scenario | 1. Send the SELECT command with • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. Send the GET DATA command with • Data field of the command containing the tag ('5FC106') of the Security Object 3. Extract and parse the certificates field contents from the Security Object 4. Extract the cRLDistributionPoints extension from the certificate. |
| Expected Result(s) | 1. From Step 1, the command returns the application property template with the status word '90 00'. |
| テストアサーション | TA-09.03.04.08 |
|---|---|
| 目的 | Derived PIV Credential Issuerの(コンテンツ署名)証明書のcRLDistributionPoints拡張が、LDAPまたはHTTPのURIを少なくとも1つ含むことを検証します。 |
| DTR | • DTR-07.03.04.09 |
| 発行者文書 | なし。 |
| 前提条件 | • 派生PIVアプリケーションを搭載したトークンが、適切なトークンリーダーに挿入されています。 • テストシステムとリーダーの間に適切なドライバーが読み込まれています。 • 派生PIVアプリケーション内にSecurity Objectが存在します。 |
| テストシナリオ | 1. 次の内容でSELECTコマンドを送信します。 • AID == 'A0 00 00 03 08 00 00 20 00 01 00' 2. 次の内容でGET DATAコマンドを送信します。 • コマンドのデータフィールドにSecurity Objectのタグ('5FC106')を含める 3. Security Objectからcertificatesフィールドの内容を抽出して解析する 4. 証明書からcRLDistributionPoints拡張を抽出します。 |
| 期待結果 | 1. 手順1より、コマンドはapplication property templateとステータスワード'90 00'を返します。 |
| 2. From Step 2, the command returns the requested data object along with the status word '90 00'. 3. From Step 4, a URI with either the “LDAP” or “HTTP” scheme that can be used to access CRL information is present. |
| 2. 手順2より、コマンドは要求されたデータオブジェクトとステータスワード'90 00'を返します。 3. 手順4より、CRL情報へのアクセスに使用できる、スキームが“LDAP”または“HTTP”のURIが存在します。 |
Appendix A—Testing of Derived PIV Credentials on Embedded Tokens
付録A—組込みトークン上の派生PIVクレデンシャルのテスト
Embedded hardware tokens are not removable from the mobile device, but may be accessed by software using the underlying cryptographic interface of the mobile device. Since these tokens are built into the mobile device, they do not require an application interface definition to enable communication between the token and the mobile device native environment. Nevertheless, embedded tokens can be tested for the service they provide. Two types of testing are described below:
組込みハードウェアトークンはモバイル機器から取り外せませんが、モバイル機器の基盤となる暗号インターフェースを用いてソフトウェアからアクセスできます。これらのトークンはモバイル機器に内蔵されているため、トークンとモバイル機器のネイティブ環境との通信を可能にするアプリケーション・インターフェース定義は必要ありません。それでも、組込みトークンが提供するサービスを試験できます。以下では2種類の試験について説明します。
A.1 Functional Testing
A.1 機能テスト
In order to ensure that an embedded Derived PIV Credential follows the specification, test entities may develop test assertions to test these credentials within their operating environment. For example, in order to determine if a Derived PIV Authentication certificate and associated private key on the mobile device can be used for authentication, a test entity may set up an TLS-enabled test website and test whether a mobile device with an embedded Derived PIV Authentication certificate can successfully authenticate to the site. Similarly, for testing digital signature and encryption capabilities, a native email client on a mobile device may be setup to sign or decrypt Secure/Multipurpose Internet Mail Extensions (S/MIME) messages and the results reviewed to determine suitable functionality.
組込み型の派生PIVクレデンシャルが仕様に従っていることを確認するため、テスト主体は、自らの運用環境内でこれらのクレデンシャルをテストするテストアサーションを策定してもよいです。たとえば、モバイルデバイス上の派生PIV認証証明書と関連する秘密鍵を認証に使用できるかを判断するために、テスト主体はTLS対応のテスト用Webサイトを構築し、派生PIV認証証明書を組み込んだモバイルデバイスがそのサイトに対して正しく認証できるかをテストできます。同様に、デジタル署名と暗号化の機能をテストするには、モバイルデバイス上のネイティブの電子メールクライアントを設定してSecure/Multipurpose Internet Mail Extensions(S/MIME)メッセージの署名または復号を行わせ、その結果を確認して適切に機能するかを判断できます。
A.2 Data Model Testing
A.2 データモデルのテスト
In order to perform data model conformance testing, test entities need to obtain the certificates (i.e., Derived PIV Authentication, digital signature, and key management). Methods for obtaining the certificates include, but are not limited to, (i) performing a functional test and acquiring the certificate by means of that test, (ii) using vendor-specific interface commands to extract the certificates, or (iii) requesting the certificates from the issuer directly.
データモデルの適合性試験を行うには、試験実施機関は証明書(すなわち、派生PIV認証、電子署名、および鍵管理の各証明書)を取得する必要があります。証明書の取得方法には、(i) 機能試験を実施し、その試験を通じて証明書を取得する、(ii) ベンダー固有のインターフェースコマンドで証明書を抽出する、(iii) 発行者に証明書を直接請求する方法などがありますが、これらに限定されません。
Once the certificates have been obtain, test entities can follow (as appropriate) the test assertions from Section 9.3 to verify that the certificates conform to the appropriate profiles.
証明書を取得した後、試験実施機関は適宜、第9.3節の試験アサーションに従って、証明書が該当するプロファイルに準拠していることを検証できます。
Appendix B—Acronyms
付録B—略語
API — Application Programming Interface
API — アプリケーションプログラミングインタフェース
BER — Basic Encode Rules
BER — 基本符号化規則
CMS — Cryptographic Message Syntax
CMS — 暗号メッセージ構文
CRL — Certificate Revocation List
CRL — 証明書失効リスト
DTR — Derived Test Requirement
DTR — 派生テスト要件
ECDH — Elliptic Curve Diffie–Hellman
ECDH — 楕円曲線ディフィー・ヘルマン
ECDSA — Elliptic Curve Digital Signature Algorithm
ECDSA — 楕円曲線デジタル署名アルゴリズム
HSPD — Homeland Security Presidential Directive
HSPD — 国土安全保障大統領指令
HTTP — Hypertext Transfer Protocol
HTTP — ハイパーテキスト転送プロトコル
ICCD — Integrated Circuit(s) Card Devices
ICCD — 集積回路カードデバイス
IUT — Implementation Under Test
IUT — テスト対象の実装
NIST — National Institute of Standards and Technology
NIST — 米国国立標準技術研究所
OSCP — Online Certificate Status Protocol
OSCP — オンライン証明書状態プロトコル
OID — Object Identifier
OID — オブジェクト識別子
PC — Personal Computer
PC — パーソナルコンピュータ
PIV — Personal Identity Verification
PIV — 個人識別検証
PKI — Public Key Infrastructure
PKI — 公開鍵基盤
PSS — Probabilistic Signature Scheme
PSS — 確率的署名方式
PUK — Password Unblocking Key
PUK — パスワードブロック解除鍵
RSA — Rivest Shamir Adleman
RSA — Rivest Shamir Adleman
S/MIME — Secure/Multipurpose Internet Mail Extensions
S/MIME — Secure/Multipurpose Internet Mail Extensions
SD — Secure Digital
SD — Secure Digital
SHA — Secure Hash Algorithm
SHA — セキュアハッシュアルゴリズム
SIM — Subscriber Identity Module
SIM — 加入者識別モジュール
SSP — Shared Service Provider
SSP — 共有サービスプロバイダ
TA — Test Assertion
TA — テストアサーション
TLV — Tag-Length-Value
TLV — タグ・長さ・値
USB — Universal Serial Bus
USB — Universal Serial Bus
UICC — Universal Integrated Circuit Cards
UICC — Universal Integrated Circuit Cards
URI — Uniform Resource Identifier
URI — 統一資源識別子
URL — Uniform Resource Locator
URL — 統一資源位置指定子
Appendix C—Glossary of Terms
付録C—用語集
Application Protocol Data Unit — A part of the application layer in the Open Systems Interconnection Reference model that is used for communication between two separate device's applications. In the context of smart cards, an APDU is the communication unit between a smart card reader and a smart card. The structure of the APDU is defined by [ISO7816-4].
Application Protocol Data Unit — 開放型システム間相互接続(OSI)参照モデルのアプリケーション層の一部であり、別々のデバイスのアプリケーション間の通信に用いられます。スマートカードの文脈では、APDUはスマートカードリーダとスマートカードの間の通信単位です。APDUの構造は [ISO7816-4] で定義されています。
Derived PIV Application — A standardized application residing on a cryptographic token that hosts a Derived PIV Credential and associated mandatory and optional elements.
Derived PIV Application — 暗号トークン上に常駐する標準化されたアプリケーションであり、派生PIVクレデンシャルと、関連する必須要素およびオプション要素を保持します。
Derived PIV Credential — An X.509 Derived PIV Authentication certificate, which is issued in accordance with the requirements specified in [SP800-157], where the PIV Authentication certificate on the Applicant’s PIV Card serves as the original credential. The Derived PIV Credential is an additional common identity credential under [HSPD12] and [FIPS201] that is issued by a federal department or agency and that is used with mobile devices
Derived PIV Credential — [SP800-157] に規定された要件に従って発行されるX.509派生PIV認証証明書であり、申請者のPIVカード上のPIV認証証明書が元のクレデンシャルとなります。派生PIVクレデンシャルは、[HSPD12] および [FIPS201] の下での追加の共通識別クレデンシャルであり、連邦の省庁または機関が発行し、モバイルデバイスで使用される
All other significant technical terms used within this document are defined in other key documents including [FIPS201], [SP800-63], and [SP800-73].
本書で使用するその他の重要な技術用語は、[FIPS201]、[SP800-63]、[SP800-73]などの主要文書で定義されています。
Appendix D—References
付録D—参考文献
[FIPS140] National Institute of Standards and Technology, Security Requirements for Cryptographic Modules, Federal Information Processing Standards (FIPS) Publication 140-2, May 2001 (including change notices through 12/3/02). http://csrc.nist.gov/publications/fips/fips140-2/fips1402.pdf [accessed 6/3/16].
[FIPS140] National Institute of Standards and Technology, Security Requirements for Cryptographic Modules, Federal Information Processing Standards (FIPS) Publication 140-2, 2001年5月(2002年12月3日までの変更通知を含む). http://csrc.nist.gov/publications/fips/fips140-2/fips1402.pdf [2016年6月3日アクセス].
[FIPS201] National Institute of Standards and Technology, Personal Identity Verification (PIV) of Federal Employees and Contractors, Federal Information Processing Standards (FIPS) Publication 201-2, August 2013. http://dx.doi.org/10.6028/NIST.FIPS.201-2.
[FIPS201] National Institute of Standards and Technology, Personal Identity Verification (PIV) of Federal Employees and Contractors, Federal Information Processing Standards (FIPS) Publication 201-2, 2013年8月. http://dx.doi.org/10.6028/NIST.FIPS.201-2.
[GPSE] GlobalPlatform, GlobalPlatform Card Secure Element Configuration v1.0, October 2012. http://www.globalplatform.org/specificationscard.asp [accessed 6/3/16].
[GPSE] GlobalPlatform, GlobalPlatform Card Secure Element Configuration v1.0, 2012年10月. http://www.globalplatform.org/specificationscard.asp [2016年6月3日アクセス].
[HSPD12] Homeland Security Presidential Directive-12, Policies for a Common Identification Standard for Federal Employees and Contractors, August 27, 2004. http://www.dhs.gov/homeland-security-presidential-directive-12 [accessed 6/3/16].
[HSPD12] Homeland Security Presidential Directive-12, Policies for a Common Identification Standard for Federal Employees and Contractors, 2004年8月27日. http://www.dhs.gov/homeland-security-presidential-directive-12 [2016年6月3日アクセス].
[ICCDSPEC] Universal Serial Bus Device Class: Smart Card ICCD Specification for USB Integrated Circuit(s) Card Devices, Revision 1.0, April 22, 2005. http://www.usb.org/developers/docs/devclass_docs/DWG_Smart-Card_USB-ICC_ICCD_rev10.pdf [accessed 6/3/16].
[ICCDSPEC] Universal Serial Bus Device Class: Smart Card ICCD Specification for USB Integrated Circuit(s) Card Devices、Revision 1.0、2005年4月22日。http://www.usb.org/developers/docs/devclass_docs/DWG_Smart-Card_USB-ICC_ICCD_rev10.pdf[2016年6月3日アクセス]。
[ISO7816-4] International Organization for Standardization/International Electrotechnical Commission (ISO/IEC), Identification cards — Integrated circuit cards – Part 4: Organization, security and commands for interchange, ISO/IEC 7816-4:2013, 2013. http://www.iso.org/iso/home/store/catalogue_ics/catalogue_detail_ics.htm?csnumber=54550 [accessed 6/3/16].
[ISO7816-4] 国際標準化機構/国際電気標準会議(ISO/IEC)、Identification cards — Integrated circuit cards – Part 4: Organization, security and commands for interchange, ISO/IEC 7816-4:2013、2013年。http://www.iso.org/iso/home/store/catalogue_ics/catalogue_detail_ics.htm?csnumber=54550[2016年6月3日アクセス]。
[PROF] Federal PKI Policy Authority Shared Service Provider Working Group, X.509 Certificate and Certificate Revocation List (CRL) Extensions Profile for the Shared Service Providers (SSP) Program, Version 1.7, May 5, 2015. https://www.idmanagement.gov/IDM/s/document_detail?Id=kA0t00000008ObeCAE [accessed 6/3/16].
[PROF] Federal PKI Policy Authority Shared Service Provider Working Group, X.509 Certificate and Certificate Revocation List (CRL) Extensions Profile for the Shared Service Providers (SSP) Program, Version 1.7, 2015年5月5日. https://www.idmanagement.gov/IDM/s/document_detail?Id=kA0t00000008ObeCAE [2016年6月3日アクセス].
[RFC2585] R. Housley and P. Hoffman, Internet X.509 Public Key Infrastructure Operational Protocols: FTP and HTTP, Internet Engineering Task Force (IETF) Network Working Group Request for Comments (RFC) 2585, May 1999. http://dx.doi.org/10.17487/RFC2585.
[RFC2585] R. Housley and P. Hoffman, Internet X.509 Public Key Infrastructure Operational Protocols: FTP and HTTP, Internet Engineering Task Force (IETF) Network Working Group Request for Comments (RFC) 2585, 1999年5月. http://dx.doi.org/10.17487/RFC2585.
[RFC3370]
[RFC3370]
R. Housley, Cryptographic Message Syntax (CMS) Algorithms, Internet Engineering Task Force (IETF) Network Working Group Request for Comments (RFC) 3370, August 2002. http://dx.doi.org/10.17487/RFC3370.
R. Housley, Cryptographic Message Syntax (CMS) Algorithms, Internet Engineering Task Force (IETF) Network Working Group Request for Comments (RFC) 3370, 2002年8月. http://dx.doi.org/10.17487/RFC3370.
[RFC4122]
[RFC4122]
P. Leach, M. Mealling, and R. Salz, A Universally Unique IDentifier (UUID) URN Namespace, Internet Engineering Task Force (IETF) Network Working Group Request for Comments (RFC) 4122, July 2005. http://dx.doi.org/10.17487/RFC4122.
P. Leach、M. Mealling、R. Salz, A Universally Unique IDentifier (UUID) URN Namespace, Internet Engineering Task Force (IETF) Network Working Group Request for Comments (RFC) 4122, 2005年7月. http://dx.doi.org/10.17487/RFC4122.
[RFC5652]
[RFC5652]
R. Housley, Cryptographic Message Syntax (CMS), Internet Engineering Task Force (IETF) Network Working Group Request for Comments (RFC) 5652, September 2009. http://dx.doi.org/10.17487/RFC5652.
R. Housley, Cryptographic Message Syntax (CMS), Internet Engineering Task Force (IETF) Network Working Group Request for Comments (RFC) 5652, 2009年9月. http://dx.doi.org/10.17487/RFC5652.
[RFC5751]
[RFC5751]
B. Ramsdell and S. Turner, Secure/Multipurpose Internet Mail Extensions (S/MIME) Version 3.2 Message Specification, Internet Engineering Task Force (IETF) Request for Comments (RFC) 5751, January 2010. http://dx.doi.org/10.17487/RFC5751.
B. RamsdellおよびS. Turner, Secure/Multipurpose Internet Mail Extensions (S/MIME) Version 3.2 Message Specification, Internet Engineering Task Force (IETF) Request for Comments (RFC) 5751, 2010年1月. http://dx.doi.org/10.17487/RFC5751.
[SEC1]
[SEC1]
Certicom Research, SEC 1: Elliptic Curve Cryptography, Version 1.0, Standards for Efficient Cryptography, September 2000. http://www.secg.org/SEC1-Ver-1.0.pdf [accessed 6/3/16].
Certicom Research, SEC 1: Elliptic Curve Cryptography, Version 1.0, Standards for Efficient Cryptography, 2000年9月. http://www.secg.org/SEC1-Ver-1.0.pdf [2016年6月3日アクセス].
[SP800-56A] National Institute of Standards and Technology, Recommendation for Pair-Wise Key Establishment Schemes Using Discrete Logarithm Cryptography, NIST Special Publication (SP) 800-56A Revision 2, May 2013. http://dx.doi.org/10.6028/NIST.SP.800-56Ar2.
[SP800-56A] 米国国立標準技術研究所、Recommendation for Pair-Wise Key Establishment Schemes Using Discrete Logarithm Cryptography、NIST特別刊行物(SP)800-56A改訂2、2013年5月。http://dx.doi.org/10.6028/NIST.SP.800-56Ar2.
[SP800-63]
[SP800-63]
National Institute of Standards and Technology, Electronic Authentication Guideline, NIST Special Publication (SP) 800-63-2, August 2013. http://dx.doi.org/10.6028/NIST.SP.800-63-2.
National Institute of Standards and Technology, Electronic Authentication Guideline, NIST Special Publication (SP) 800-63-2, 2013年8月. http://dx.doi.org/10.6028/NIST.SP.800-63-2.
[SP800-73]
[SP800-73]
National Institute of Standards and Technology, Interfaces for Personal Identity Verification, NIST Special Publication (SP) 800-73-4, May 2015 (includes updates as of 2/8/16). http://dx.doi.org/10.6028/NIST.SP.800-73-4.
National Institute of Standards and Technology, Interfaces for Personal Identity Verification, NIST Special Publication (SP) 800-73-4, 2015年5月(2016年2月8日現在の更新を含む). http://dx.doi.org/10.6028/NIST.SP.800-73-4.
[SP800-78]
[SP800-78]
National Institute of Standards and Technology, Cryptographic Algorithms and Key Sizes for Personal Identity Verification, NIST Special Publication (SP) 800-78-4, May 2015. http://dx.doi.org/10.6028/NIST.SP.800-78-4.
National Institute of Standards and Technology, Cryptographic Algorithms and Key Sizes for Personal Identity Verification, NIST Special Publication (SP) 800-78-4, 2015年5月. http://dx.doi.org/10.6028/NIST.SP.800-78-4.
[SP800-79]
[SP800-79]
National Institute of Standards and Technology, Guidelines for the Authorization of Personal Identity Verification Card Issuers (PCI) and Derived PIV Credential Issuers (DPCI), NIST Special Publication (SP) 800-79-2, July 2015. http://dx.doi.org/10.6028/NIST.SP.800-79-2.
National Institute of Standards and Technology, Guidelines for the Authorization of Personal Identity Verification Card Issuers (PCI) and Derived PIV Credential Issuers (DPCI), NIST Special Publication (SP) 800-79-2, 2015年7月. http://dx.doi.org/10.6028/NIST.SP.800-79-2.
[SP800-96]
[SP800-96]
National Institute of Standards and Technology, PIV Card to Reader Interoperability Guidelines, NIST Special Publication (SP) 800-96, September 2006. http://dx.doi.org/10.6028/NIST.SP.800-96.
National Institute of Standards and Technology, PIV Card to Reader Interoperability Guidelines, NIST Special Publication (SP) 800-96, 2006年9月. http://dx.doi.org/10.6028/NIST.SP.800-96.
[SP800-157] National Institute of Standards and Technology, Guidelines for Derived Personal Identity Verification (PIV) Credentials, NIST Special Publication (SP) 800-157, December 2014. http://dx.doi.org/10.6028/NIST.SP.800-157.
[SP800-157] 米国国立標準技術研究所、Guidelines for Derived Personal Identity Verification (PIV) Credentials, NIST特別刊行物(SP)800-157、2014年12月。http://dx.doi.org/10.6028/NIST.SP.800-157.